North Korea linked TraderTraitor associated with the Lazarus Group was identified by TRM Labs as responsible for the $6.3 billion Binance crypto heist.
Binance initial investigation points to a compromised DevOps engineer’s laptop as a possible entry point.
Meanwhile North Korea under Kim Jong Un fired around 10 ballistic missiles towards the East Sea
Cyber operations and missile launches. Pyongyang on two fronts.
You can choose to put someone else first without deciding your own preference shouldn't matter. Real compromise means choosing someone else this time, not negating what you want. #Relationships#Compromise
Endeor here, our account was compromised today and i'm glad to announce that as of now, I have gained back control.
The previous tweets, made by the comprimiser, have been deleted.
Other than that, Have a Happy Halloween today everyone!!!! 🎃🎃
#BLOCKBOUND
We're aware of the recent news about a compromised launcher for another game and that Dune: Awakening was mentioned as one of the games that may have been compromised.
We can confirm that Dune: Awakening is not affected by this vulnerability. We no longer have a launcher, and the launcher we previously used was developed in-house with no shared code from those affected.
Thank you for raising your concerns!
I am on the "Helix is compromised" train and this general will be a new hero who either A) bumps heads with Sojourn over how to run Overwatch because they are by-the-books or B) straight up an Conspiracy asset
Share
Copied
retrowen 👾 father of hammond@retro_wen
Thinking about this past year, I wish the IJC could’ve had more of a looming presence on Overwatch as an organization.
I’d love to see some more tension within the Overwatch organization and I’m hoping Helix’s involvement can stir something up!
Thinking about this past year, I wish the IJC could’ve had more of a looming presence on Overwatch as an organization.
I’d love to see some more tension within the Overwatch organization and I’m hoping Helix’s involvement can stir something up!
The current election will be rerun.
Investigations are concluding that foreign actors have interfered—through access to infrastructure, influence operations, and efforts to undermine public trust. Under Executive Order 13848 (signed in 2018), the Director of National Intelligence is required to assess foreign interference within 45 days of an election.
Once that assessment confirms such interference, the existing national emergency—already in effect—will be fully triggered, authorizing targeted sanctions, asset freezes, and a legal basis to deem the election results compromised.
The old system is at an end. Paper trails, centralized machinery, and opaque vote-counting rooms will no longer be acceptable once foreign interference is established.
The solution is a new, sovereign electoral infrastructure: a blockchain layer dedicated to voter registration, casting ballots, and public verification.
Every vote is recorded as an immutable, auditable transaction. There is no single point of failure. There is no hidden aggregation. It allows for real-time public verification without compromising voter privacy.
Foreign interference triggers a reset. Blockchain serves as the permanent replacement.
A U.S.-built blockchain is the chosen solution for this challenge.
I like to call it the "Kennedy Blockchain"—named after the last president who attempted to expose secret societies, the "deep state," and the Federal Reserve—an effort for which he was killed.
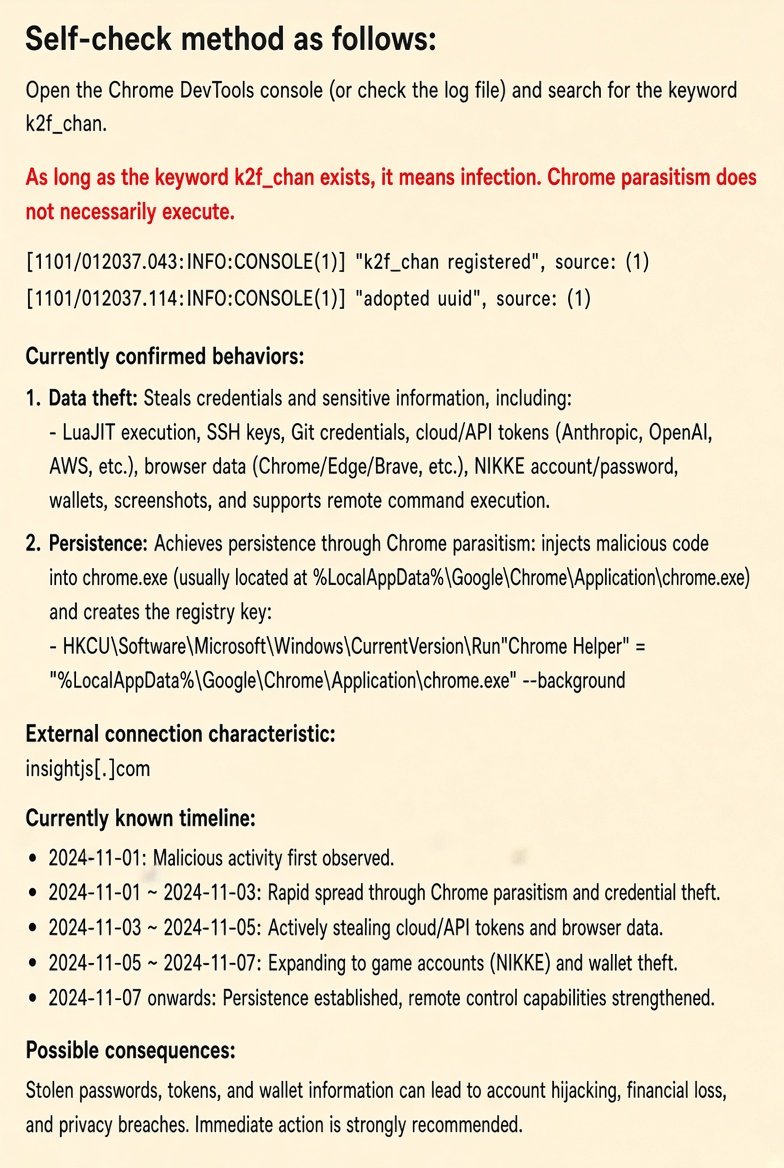
#NIKKE oomfies, there's confirmation that the NIKKE launcher was targeted by a supply chain attack: It got injected with malicious script, all of your browser credentials, tokens, cookies, etc might be compromised. This means it can bypass 2FA. Please, change all your passwords.
NOW: Seaview Avenue in St Andrew. Motorists urged to approach with caution after section of the roadway compromised following consistent rainfall #Tuesday#November#Ja
🚨 Hackers Breach at Least 27 Organizations Using Stolen Microsoft Entra ID and Azure DevOps Credentials
An ongoing cyberattack campaign has compromised cloud environments belonging to at least 27 organizations, with attackers abusing stolen Microsoft Entra ID application credentials and Azure DevOps identities to gain access to Microsoft 365 and Azure resources.
According to security researchers at Todyl, the campaign began on November 1, targeting managed service providers (MSPs) and their customers across government, energy, transportation, education, legal, and other sectors.
Investigators have identified extensive unauthorized activity, including:
• 27 organizations affected
• 45 application registrations targeted
• 33+ successful application authentications
• Approximately 2,279 mailbox items accessed
• 81 files downloaded from compromised environments
• One application used to access 15 customer tenants
Stolen information included password lists, private keys, VPN configurations, backup credentials, and remote access settings, raising concerns about additional compromises.
Attackers were able to impersonate trusted applications and access cloud resources without triggering traditional user MFA challenges. No Microsoft vulnerability was exploited.
Attack Details
• Initial activity: November 1, 2026
• Targeted platforms: Microsoft Entra ID, Azure DevOps, Microsoft 365
• Attack method: Stolen application credentials and session token abuse
• Confirmed source IP: 199[.]19[.]77[.]84
• Attribution: Unknown
• Status: Ongoing investigation
Organizations are advised to investigate unusual service principal activity, revoke compromised credentials, rotate exposed secrets, and review third-party application permissions.
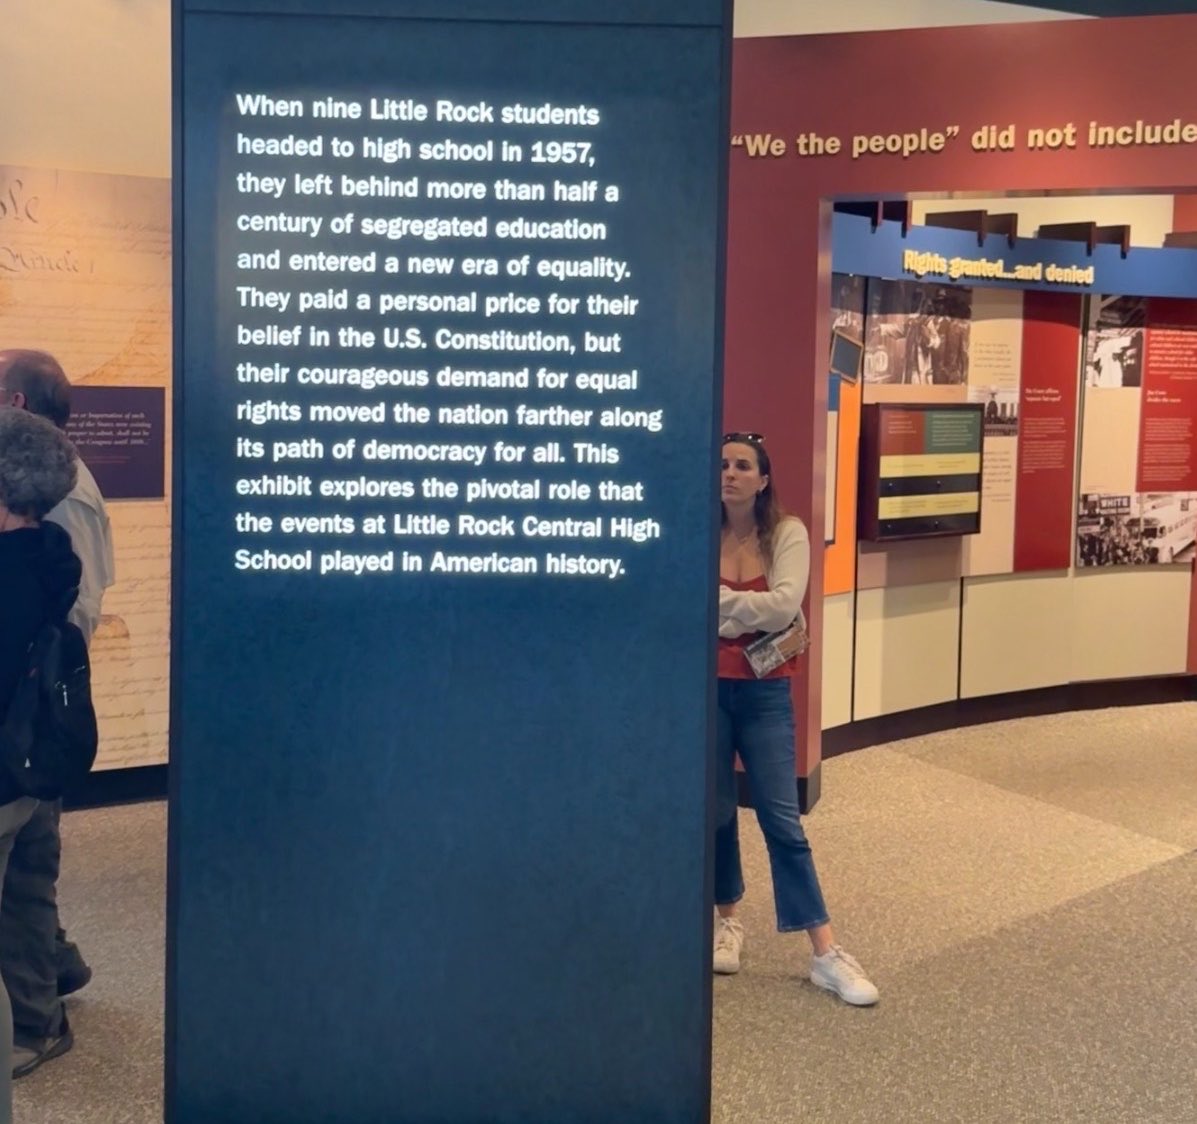
We have arrived at the Little Rock Nine historical site.
The Heisman and I have struck a deal that if we can visit here (and she can get her National Parks passport stamped) then I can drink as much beer as I want this weekend WITHOUT REPERCUSSIONS!
#Compromise
There is probaly a day
When #compromise
Is just about right-
You give a little, I give a lot
We #hold together
To see if it all balances
All that we have
All that we bring
To a long table we set
Together for all the days
We live as one
#vsspoem#vssromance
Watching this video of a school being demolished in Hopley broke something in me. When we are fighting to protect young people from falling into drugs we are out here demolishing schools.
The real scandal here is the system that created this situation. Ordinary people did not wake up and steal land but were sold stands, given papers, assured by people in authority that they were safe.
We saw the same situation in St Martins when a Council owned and run Pay-Scheme was disowned in the heat of political pressure.
How can the same system that looked away, or profited, or connived with land barons come back to punish them for trusting it?
Land barons do not operate in a vacuum but thrive where Council is weak, compromised, or complicit. Council officials who should protect public land have instead been enabling its illegal sale. So to be clear accountability must start at the top, not at the bottom.
Council authorities who connived with land barons, who issued or tolerated fake papers should be held accountable. Victims should not be made culpable for a failure of governance. Why have we not seen any Council official being held responsible @mafume
We must prosecute the land barons and corrupt Council officials and have commissions that have tangible results.
the second batch of XP recovery is done
everyone who completed all the mission steps has had their compromised XP transferred over
check your updated XP on your @jumperapp profile
if you're holding XP on a non-evm wallet you've got until 13 November to complete the mission and update your XP
this is the final call.
Everyone, this is a serious issue:
Apparently Nikke PC client has been compromised by a supply chain attack! So please, don’t use it and only use the mobile version until Shift Up announces something.
Altros has pointed this out, share this if you can!