Hi everyone!
Here it's my write-up for a postMessage vuln I found in a BBP:
- why postMessage() and how can lead to a vuln.
- when is jQuery really vulnerable and exploitable.
- chain this issue with CORS to get a 5X bounty.
#bugbountytips#xss#domxss
when i start learning web application attack vectors, the only thing disturbed me is "DOM XSS".
didn't find any detailed video tutorial of DOM XSS, so now i made a one with really simple explanation.
Click the link below to watch
#domxss#xss
DOM based XSS
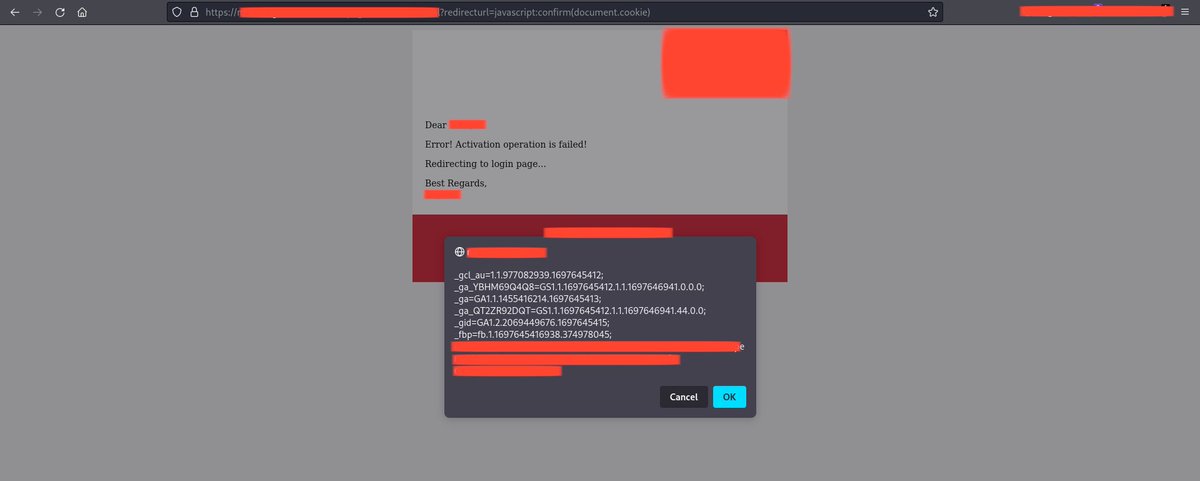
Recently I was able to find a DOM based XSS, This vulnerability usually arise when JavaScript takes data from an attacker-controllable source.
Thread 🧵
#bugbountytips#domxss#xss
Dom XSS Tip:
Once you've found where the source is being read, you can use the JavaScript debugger to add a break point and follow how the source's value is used. You might find that the source gets assigned to other variables.
#domxss#sourcecodereview
A new video for post message attacks. Why it happened, syntax, we wrote vulnerable code and see how to read and bypass regex for origin
Next video we will solve labs and special case and how to find it with Dom Invader
#bugbounty#infosec#domxss