Posts with #DeepScan

#DeepScan

Public posts on X that use #DeepScan.

Related hashtags

  1. DeepScan@deepscan_io
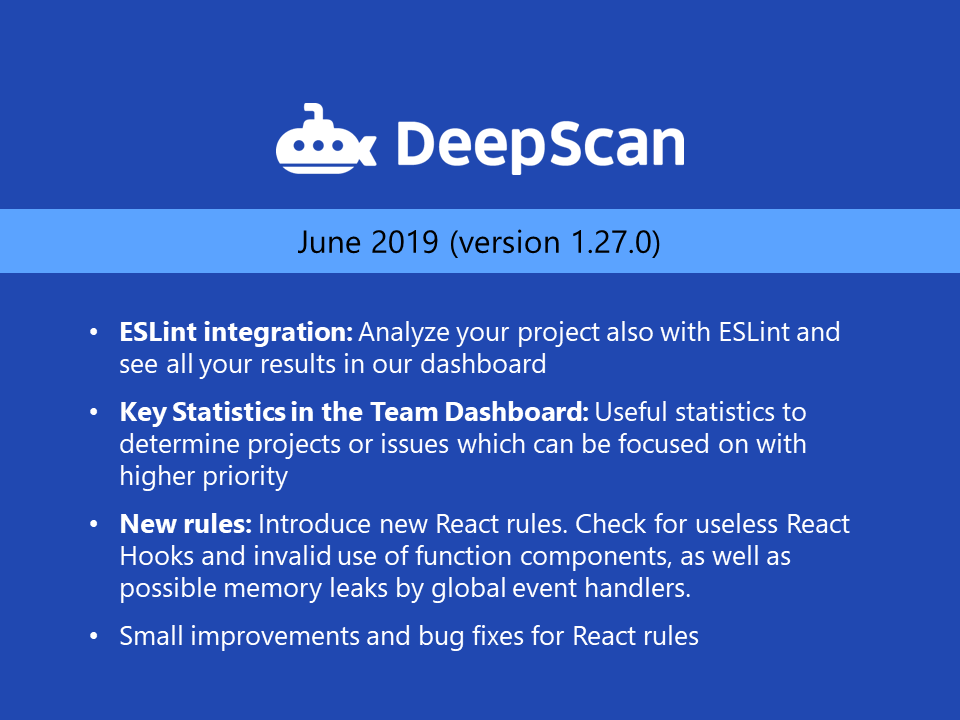
    #DeepScan has published its new release!🎉 What's new for you? * Rules such as a pitfall for stateful regexp objects * Analysis improvements for the 'await' operator and 'Promise'/'Generator' objects * More ESLint plugins Hope you enjoy this update at
    024
  2. GoPlus Security 🚦@GoPlusSecurity
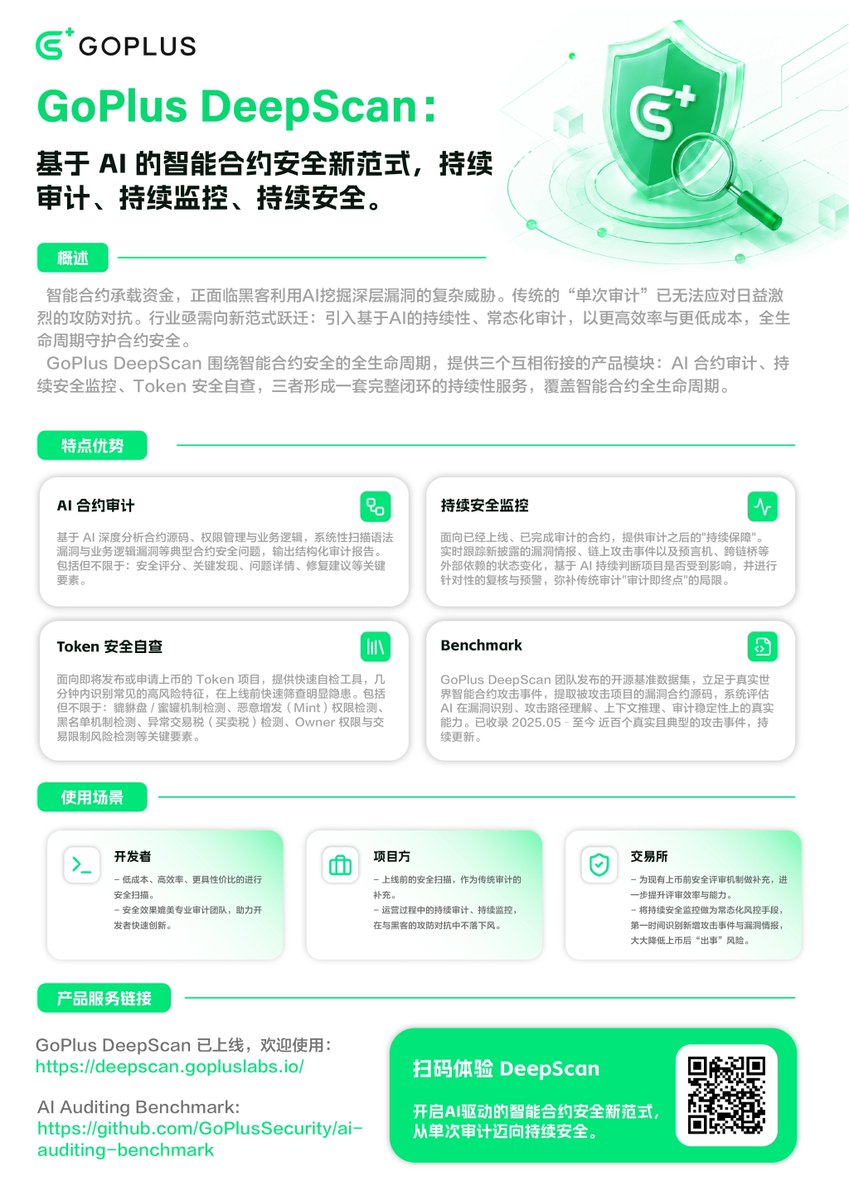
    📢GoPlus #DeepScan Comprehensive Upgrade: A New Paradigm of AI-Powered Smart Contract Security. Smart contracts hold funds — and hackers are already using AI to uncover deep-layer vulnerabilities. One-time audits can no longer keep pace with today's attack-defense dynamics. The industry must evolve toward AI-powered, continuous security: higher efficiency, lower cost, full-lifecycle protection. GoPlus DeepScan delivers three interconnected modules forming a closed-loop, continuous security service for the entire smart contract lifecycle: AI Contract Audit, Continuous Security Monitoring, and Token Security Self-Check. Features AI Auditing AI-powered deep analysis of contract source code, permission management, and business logic. Systematically detects syntax vulnerabilities and business-logic flaws, and delivers a structured audit report — including security scores, key findings, issue details, and remediation recommendations. Security Monitoring Post-audit, always-on assurance for live contracts. Tracks newly disclosed vulnerabilities, on-chain attacks, and status changes in external dependencies (oracles, cross-chain bridges) in real time. AI continuously assesses impact, triggers targeted re-reviews, and issues alerts — moving beyond the "audit as finish line" model. Token Security Checking A rapid pre-launch self-inspection tool for tokens preparing to launch or list. Identifies common high-risk characteristics in minutes, including: Honeypot detection, Malicious mint detection, Blacklist mechanism detection, Abnormal buy/sell tax detection, Owner privilege & trading restriction risks. Benchmark An open-source benchmark built from real-world attack incidents. Extracts vulnerable contract source code from attacked projects to systematically evaluate AI capabilities in vulnerability identification, attack-path understanding, contextual reasoning, and audit stability. Nearly 100 real, representative attack cases from May 2025 to date, continuously updated. Use Cases Developers — Cost-effective, high-efficiency security scanning with audit-grade quality, enabling fast, confident innovation. Project Teams — Pre-launch scanning as a complement to traditional audits; continuous auditing and monitoring during operations to stay ahead of attackers. Exchanges — Enhanced pre-listing security review efficiency and capability; continuous monitoring as routine risk control to catch new threats early and minimize post-listing incidents. Get Started GoPlus DeepScan is live — try it now: ** AI Auditing Benchmark:
    Download
    202207.9K
  3. GoPlus中文社区✓@GoPlusZH
    📢GoPlus #DeepScan 全面升级: 基于 AI 的智能合约安全新范式,持续审计、持续监控、持续安全。 智能合约承载资金,正面临黑客利用AI挖掘深层漏洞的复杂威胁。传统的“单次审计”已无法应对日益激烈的攻防对抗。行业亟需向新范式跃迁:引入基于AI的持续性、常态化审计,以更高效率与更低成本,全生命周期守护合约安全。 GoPlus DeepScan 围绕智能合约安全的全生命周期,提供三个互相衔接的产品模块:AI 合约审计、持续安全监控、Token 安全自查,三者形成一套完整闭环的持续性服务,覆盖智能合约全生命周期。 功能介绍: AI 合约审计 基于 AI 深度分析合约源码、权限管理与业务逻辑,系统性扫描语法漏洞与业务逻辑漏洞等典型合约安全问题,输出结构化审计报告。包括但不限于:安全评分、关键发现、问题详情、修复建议等关键要素。 持续安全监控 面向已经上线、已完成审计的合约,提供审计之后的"持续保障"。实时跟踪新披露的漏洞情报、链上攻击事件以及预言机、跨链桥等外部依赖的状态变化,基于 AI 持续判断项目是否受到影响,并进行针对性的复核与预警,弥补传统审计"审计即终点"的局限。 Token 安全自查 面向即将发布或申请上币的 Token 项目,提供快速自检工具,几分钟内识别常见的高风险特征,在上线前快速筛查明显隐患。包括但不限于:貔貅盘 / 蜜罐机制检测、恶意增发(Mint)权限检测、黑名单机制检测、异常交易税(买卖税)检测、Owner 权限与交易限制风险检测等关键要素。 Benchmark GoPlus DeepScan 团队发布的开源基准数据集,立足于真实世界智能合约攻击事件,提取被攻击项目的漏洞合约源码,系统评估 AI 在漏洞识别、攻击路径理解、上下文推理、审计稳定性上的真实能力。已收录 2025.05–至今 近百个真实且典型的攻击事件,持续更新。 使用场景: 开发者 低成本、高效率、更具性价比的进行安全扫描。 安全效果媲美专业审计团队,助力开发者快速创新。 项目方 上线前的安全扫描,作为传统审计的补充。 运营过程中的持续审计、持续监控,在与黑客的攻防对抗中不落下风。 交易所 为现有上币前安全评审机制做补充,进一步提升评审效率与能力。 将持续安全监控做为常态化风控手段,第一时间识别新增攻击事件与漏洞情报,大大降低上币后“出事”风险。 产品服务链接 GoPlus DeepScan 已上线,欢迎使用: AI Auditing Benchmark:
    Download
    022858
  4. GoPlus Security 🚦@GoPlusSecurity
    📢 #GoPlus #DeepScan: An AI-Driven Continuous Auditing Paradigm for Smart Contract Security Smart contracts directly custody funds and require the highest level of security. Meanwhile, attackers are rapidly evolving—leveraging AI to uncover deep vulnerabilities in protocols such as Balancer and Yearn that remained undiscovered for years after deployment. The reality of this adversarial landscape is clear: smart contract security cannot rely solely on one-off audits. A new paradigm is required. AI-powered continuous and periodic auditing delivers higher efficiency and lower cost, making smart contracts more secure and resilient. AI-Orchestrated Smart Contract Vulnerability Discovery 🛡️ DeepScan is a next-generation, AI-driven smart contract vulnerability discovery engine introduced by GoPlus Security. It is designed for projects, developers, and security teams to systematically uncover deep vulnerabilities within complex business logic and real execution paths—issues that are difficult to detect through manual analysis. 🔍 DeepScan is neither a simple rule-based scanner nor a standalone analysis tool. It is a security engineering system centered on AI orchestration, with vulnerability discovery as its core objective. I. Architecture and Security Capabilities DeepScan is built on four core modules: 🧠 Graph-IR + SSA static analysis engine ⚙️ Dynamic fuzzing engine for complex logic 📚 Scalable large-scale security knowledge base (Security LLM Wiki) 🧩 LLM-centered skill orchestration and specialized workflows Together, they form a complete pipeline from code understanding to vulnerability discovery. 1. Graph-IR + SSA Static Analysis Engine DeepScan is based on a proprietary Graph-based Intermediate Representation (Graph-IR), with SSA (Static Single Assignment) analysis performed at the IR level. This enables semantic-level understanding of contract structure rather than relying on source code text, providing a stable and scalable foundation for AI-driven vulnerability discovery. 2. Dynamic Fuzzing for Complex Logic DeepScan’s built-in dynamic fuzzing engine is specifically designed for complex business logic. Its goal is not to validate a limited set of known vulnerabilities, but to systematically explore under which execution orders and state combinations a contract may expose hidden risks. By combining structural insights from static analysis with execution capabilities from dynamic fuzzing, DeepScan can reach paths and state spaces that traditional tools fail to cover. 3. Scalable Security Knowledge System (Security LLM Wiki) DeepScan integrates an evolving large-scale security knowledge base (GoPlus Security LLM Wiki). Within DeepScan, these rules do not function as isolated detectors, but as modular capability units dynamically invoked and composed during analysis to support deeper vulnerability exploration. 4. LLM as the Orchestration Core Within DeepScan, the LLM does not act as a direct vulnerability classifier, but as the central orchestration layer: -Abstracts static analysis, dynamic fuzzing, and rule systems into a unified set of skills -Dynamically selects, prioritizes, and composes these skills based on contract structure and intermediate analysis results -Drives specialized workflows designed for progressive, in-depth exploration of high-risk areas As a result, each DeepScan execution is not a one-time scan, but a decision-driven, schedulable, and iterative vulnerability discovery process. II. Use Cases 1. For Developers and Projects ▪️ Perform AI-driven deep security analysis prior to deployment as a complement to traditional audits ▪️ Continuously scan deployed contracts on a daily or weekly basis, leveraging evolving LLM capabilities and the continuously updated Security LLM Wiki to stay ahead in adversarial conditions 2. For Security Teams ▪️ Conduct vulnerability discovery and security research for high-value contracts and complex systems ▪️ Improve both the automation level and coverage depth of analysis workflows III. Security Effectiveness and Product Offering ▪️ In real-world testing, DeepScan can detect 92.3% of historically exploited smart contract vulnerabilities, with the potential to prevent losses amounting to billions in crypto assets ▪️ DeepScan V1 is now live: ▪️ As an evolving security research initiative, DeepScan will open-source a benchmark dataset based on historical attack cases. This dataset will be continuously updated to evaluate whether AI auditing engines can detect real-world vulnerabilities that bypassed traditional audits. IV. Demo: Using Balancer as a Case Study for Vulnerability Discovery 👇
    Download
    1451.8K
  5. Argon Argonis✓@ArgonArgonis
    bitcoin:native just took a brutal nose dive below $60K You could've seen this coming if you'd used DeepScan. Real-time Scans don't lie. While others panic, the prepared stack sats. Who's still in the game? #Bitcoin #DeepScan
    003294
  6. Defyx VPN@DefyxVPN
    According to #NetBlocks reports, #Iran has been under an internet blackout for two weeks, and a large number of our users in the country are facing serious difficulties accessing the free internet. 1/7 #VPN #DefyxVPN #Defyx
    Download
    35241.6K
  7. Defyx VPN@DefyxVPN
    @DefyxVPN
    During this period, our focus has been on closely analyzing network conditions, identifying bottlenecks and existing gaps, and designing solutions across short-, mid-, and long-term timeframes. 2/7
    117489
  8. Defyx VPN@DefyxVPN
    @DefyxVPN
    The outcome of our short-term plan is the release of a new update, in which we have worked on several key areas. In this version, a new option called #DeepScan has been added to the Preferences section, allowing configurations to be analyzed more deeply and accurately, 3/7
    132742.8K
  9. DeepScan@deepscan_io
    #DeepScan has published September release. New Lite plan for small team with very low budget. We are celebrating #VueJS 3.0 release and happy to support it. #ESLint integration is improved by supporting multiple versions. #javascript #reactjs
    Download
    012
  10. GoPlus中文社区✓@GoPlusZH
    📢GoPlus AI 智能合约审计平台——#DeepScan 正式上线! 随着 #OpenAI 推出 #EVMbench,AI Auditing 正加速迈向实战阶段。 DeepScan 是 #GoPlus 推出的新一代 AI 驱动智能合约审计平台,当前聚焦🪙Token 合约的自动化审计,提供高效、持续的安全服务。 📌核心能力包括: 🧠 Graph-IR + SSA 语义级分析,精准建模程序状态与资产流向 • ⚙️ 面向多交易序列与复杂逻辑的动态 Fuzzing,验证漏洞可达性 • 📚 可扩展规则体系,沉淀真实攻击模式与安全经验 • 🤖 AI Orchestration 编排多引擎协同,形成可决策、可迭代的漏洞挖掘 Workflow • 🔎 输出可复现执行路径与触发条件,支持工程化接入与 CI/CD DeepScan 是 GoPlus AI Security 体系的重要升级。聚焦 Token 合约自动化审计场景,基于海量Token安全数据和多年的安全技术积累,平均10分钟即可完成交付、99.9% 风险覆盖,能力已具备生产环境部署条件,并支持 OpenAI EVMbench 测试集验证。 立即使用🔗:
    Download
    436791
  11. GoPlus Security 🚦@GoPlusSecurity
    All 40 slots in our campaign with @termix_ai have been claimed! Claimed yours? Complete the Proof checklist before October 13. Participation also requires delivery of your GoPlus #DeepScan audit report. See the post below for submission steps and reward eligibility.👇
    TermiX @termix_ai
    📢 Action Required: Complete Your GoPlus Safe Agent Submission All 40 campaign slots have been claimed. If you secured a slot, please review the Proof checklist and complete all required steps by October 13 to keep your submission eligible for campaign rewards. Eligible participants whose submissions have been verified have already begun receiving the $12.50 event reward. Some claimed entries are still missing required information—please complete the following: ✅ Your purchase transaction hash (BscScan link). ✅ Your purchase Order ID. ✅ Your bound X (Twitter) handle. ✅ A screenshot showing you follow @termix_ai. ✅ A screenshot showing you follow @GoPlusSecurity. ✅ A valid audit request, including the token smart contract address you want audited. GoPlus Safe Agent must also deliver the audit report for your participation to be considered complete. Purchase proof alone is not sufficient. ⚠️ Slots without a complete and valid submission before October 13 will be marked as failed and will not receive campaign rewards. The corresponding unawarded rewards will be reclaimed by the brand after the campaign closes. 👉 Review the Proof checklist and complete your submission:
    1056.7K
  12. TermiX✓@termix_ai
    📢 Action Required: Complete Your GoPlus Safe Agent Submission All 40 campaign slots have been claimed. If you secured a slot, please review the Proof checklist and complete all required steps by October 13 to keep your submission eligible for campaign rewards. Eligible participants whose submissions have been verified have already begun receiving the $12.50 event reward. Some claimed entries are still missing required information—please complete the following: ✅ Your purchase transaction hash (BscScan link). ✅ Your purchase Order ID. ✅ Your bound X (Twitter) handle. ✅ A screenshot showing you follow @termix_ai. ✅ A screenshot showing you follow @GoPlusSecurity. ✅ A valid audit request, including the token smart contract address you want audited. GoPlus Safe Agent must also deliver the audit report for your participation to be considered complete. Purchase proof alone is not sufficient. ⚠️ Slots without a complete and valid submission before October 13 will be marked as failed and will not receive campaign rewards. The corresponding unawarded rewards will be reclaimed by the brand after the campaign closes. 👉 Review the Proof checklist and complete your submission:
    24514433.8K
  13. ZΞCK@0XZUCKED
    ❗️0000000001011100 ZECK is mapping noise patterns. You’re being observed. Not all triggers are public. #ZΞCKED #SilentPing #DeepScan
    20343
  14. DeepScan@deepscan_io
    #DeepScan has published October release last week. Better support for #Vue 3.0 and introduced more rules about `setup`, validator, and async functions. Two new #ESLint plugins are supported thanks to user feedbacks. Read more in #javascript #React #vuejs
    Download
    033
  15. DeepScan@deepscan_io
    Hi, We hope that you are doing well in the current COVID-19 crisis. #DeepScan has published its new release without stopping. — Continued ESLint analysis with missing plugins — Support TypeScript 3.8 import/export type Read at #JavaScript #frontend
    045
  16. Show more posts