Posts with #Encrypt

#Encrypt

Public posts on X that use #Encrypt.

Related hashtags

  1. The Hacker News@TheHackersNews
    🚨 New NetamLoader malware targets a government-only Windows 10 build in Asia. The attack abuses legitimate Patch My PC components, hijacks .NET execution, bypasses AMSI, and loads encrypted payloads. Kaspersky identified one victim. The attackers remain unknown. How the attack works -
    Download
    8137619.4K
  2. Peyton@PeytonMoon69
    BREAKING NEWS!!! 📱☎️🎊 First live Bitcoin phone call in recorded history October-27-2026. From American 🇺🇸 to the UK 🇬🇧Verifiable onchain. You spend Bitcoin to talk and you get paid to listen. Spammers have to pay to play. It's international and encrypted end to end.
    Download
    13381095.7K
  3. The Hacker✓@theprocracker
    Why cleartext HTTP is a security nightmare 🕵️‍♂️🔒 Quick tutorial at how network protocols handle data if it isn’t encrypted with SSL/TLS • 127.0.0.1 •
    Download
    2201364.8K
  4. maybe✓@gratusmasculus
    Today, 6529 releases post-quantum encrypted DMs. Just one more thing the platform’s critics will choose not to understand.
    4326329
  5. Tanishq Wadhwani✓@twgm282
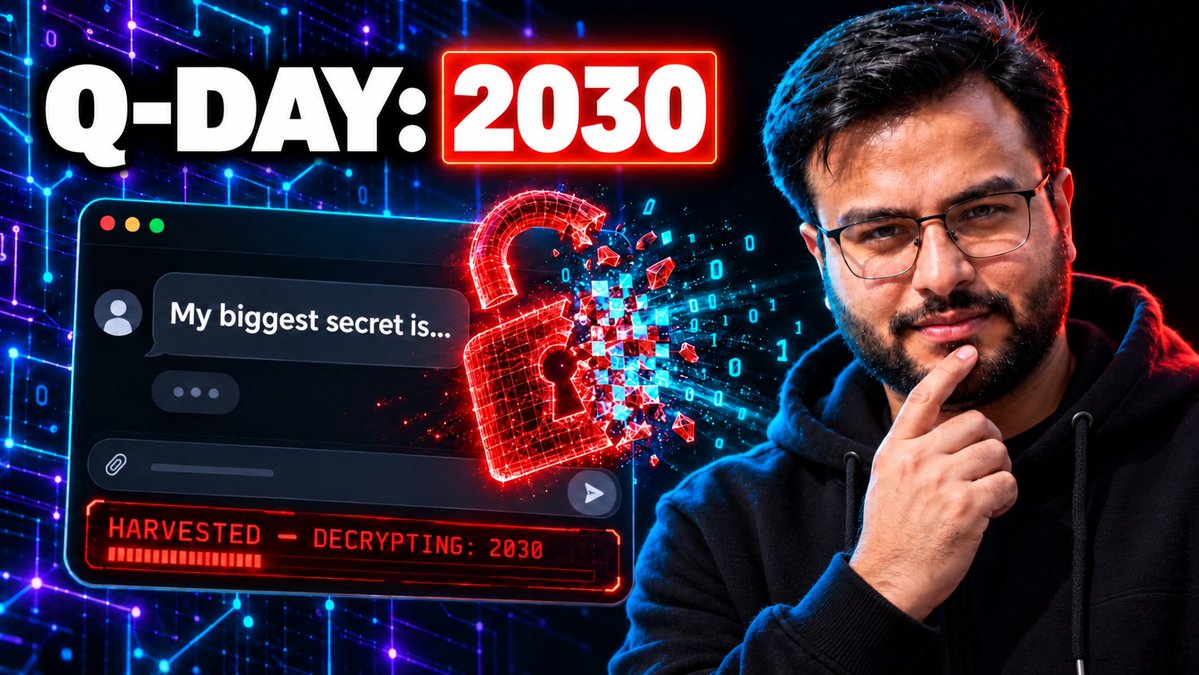
    People tell ChatGPT things they wouldn't tell their therapist, their lawyer, or their best friend. And right now, someone could be recording all of it-waiting for 2030 to read it. It’s called a "Harvest Now, Decrypt Later" (HNDL) attack. Here is how the 6-step playbook works: 1. Compromise a target’s home Wi-Fi via an unpatched router firmware vulnerability. 2. Sit between the device and the cloud AI during the handshake. 3. Use packet mirroring to passively copy the encrypted data stream without modifying a single byte (making it virtually invisible to intrusion detection systems). 4. Hoard that encrypted traffic on cheap storage. 5. Wait until "Q-Day" (projected around April 2030), when fault-tolerant quantum computers arrive and shatter standard RSA and ECC encryption. 6. Decrypt years of someone's deepest secrets in minutes. You don't need a quantum computer today to weaponize one tomorrow. Behind the scenes, AI companies are racing against the clock on two fronts-pushed hard by multi-billion-dollar "quantum sovereignty" mandates under the EU AI Act: • Software: Migrating from RSA/ECC to lattice-based Post-Quantum Cryptography (specifically ML-KEM). • Hardware: Deploying Quantum-Ready HSMs (High-Security Modules) physically optimized for lattice math. Will every cloud provider upgrade in time-and will that protect traffic that is already being harvested today? If you don't want to find out the hard way in 2030, the fix is simple: 1. Stop oversharing sensitive personal or company secrets with cloud-based AIs. 2. Run a Small Language Model (SLM) locally on your own machine. 3. Keep your private prompts on-device, where they never touch a Wi-Fi router or a third-party server. I just dropped a 6-minute breakdown-"Defense Against the Dark Arts for Nerdy Muggles"-on how quantum HNDL attacks work and how to bulletproof your AI workflow. Watch the full talk here 👇
    Download
    14544
  6. Session✓@session_app
    things I 💚 about Session Free No ads No email No tracking Note to Self Anonymous Group chats Communities Onion-routing Doesn't sell data Fully open source No phone number No central servers Recovery password Secure Account IDs Cross platform support Encrypted attachments Disappearing messages Encrypted voice messages Link previews off by default Community operated network Send messages, not metadata
    145744811K
  7. Japhet✓@JaphetzCruzz
    Happy new month fam I just joined the campaign to promote Motes. @meetmotes is building encrypted financial infrastructure that connects NFT owned AI agents with DeFi and Polymarket markets. I’m looking forward to learning more and seeing how Motes develops.
    Download
    721280475
  8. Cypherpunk@cypherpunk
    @will__mcevoy
    @will__mcevoy on Zcash in the age of AI: "The way we think about Zcash is it's private digital money. It's an encrypted version of Bitcoin" "Bitcoin is fully transparent. What most people didn't expect is that's a big deal in the world of AI." "AI is going to be dissecting all public ledgers, combining your transaction data with all the other data it has on you to stitch your life together" "That's why we're so focused on Zcash. We view it as a compelling antidote in a world where AI is pervasive"
    Download
    2131075.3K
  9. Mr. Pool✓@looP_rM_3117211
    ▫️THE MRNA PATENTS WERE JUST SEIZED. THE LIABILITY SHIELD IS GONE. On October 26, 2026 — just days ago — the legal shield that protected the mRNA vaccine manufacturers from liability was permanently dissolved. The corporate media is calling it a "routine legal review." A "policy clarification." A "reaffirmation of existing protections." THEY ARE LYING TO YOU BECAUSE THE EMERGENCY AUTHORIZATION THAT CREATED THE SHIELD NO LONGER EXISTS. What they are hiding in total panic: At exactly 11:47 PM Eastern, the emergency use authorization framework that granted pharmaceutical companies immunity from liability was formally terminated by a sealed military tribunal. The patents, the liability waivers, and the indemnification agreements were all transferred to a new sovereign oversight body. No congressional vote. No public debate. No press release. THE 40-YEAR LIABILITY SHIELD JUST COLLAPSED. For decades, the pharmaceutical industry operated under a legal architecture that made them untouchable. They could release any product, any injection, any chemical into the public body — and if something went wrong, the taxpayer paid the bill. The companies walked away clean. They told you the science was settled. They told you the vaccines were safe and effective. They told you the liability shield was for "public health." BUT THEY FORGOT THAT EMERGENCY POWERS CAN BE REVOKED. Here is what the patent seizure is actually triggering behind the scenes right now: ▪️ The Liability Reversal: Every mRNA product that was administered under emergency authorization is now subject to full civil and criminal liability. The manufacturers — Pfizer, Moderna, BioNTech — can no longer hide behind government immunity. The sealed tribunals have already begun compiling case files. ▪️ The Patent Transfer: The mRNA patents — the foundational technology that was used to create the injections — have been moved into a public trust. The technology itself is not being suppressed. It is being opened for independent review, including the sequences that were never disclosed. ▪️ The Data Unsealing: The clinical trial data that was sealed for 75 years — the raw data that the manufacturers never wanted the public to see — has been de-encrypted and transferred to the sovereign ledger. The adverse event reports, the internal safety reviews, the risk assessments — all of it is now available to the tribunals. You don't seize the patents unless you are ready to hold the manufacturers accountable for what they released into the public body. They told you the shield was permanent. They called you crazy for questioning the liability waivers. They laughed when you said the emergency powers could be revoked. Look at the court dockets tonight. They are being sealed — not to protect the companies, but to protect the evidence. The shield is gone. The liability is real. The tribunals are already seated. The patents are not being destroyed. They are being used as evidence. THE ACCOUNTABILITY ISN'T COMING. THE LIABILITY IS ALREADY RESTORED. MRNA-PATENT-SEIZED / LIABILITY-SHIELD-VOID / EMERGENCY-AUTH-TERMINATED / TRIBUNAL-SEATED
    565711.5K52.4K
  10. Cyber Security News✓@The_Cyber_News
    ‼️ Researcher Gains Root Access to Samsung Smart TV, Uncovers Extensive User Tracking Details: A cybersecurity researcher says he gained root access to a 2025 Samsung Smart TV and found software built to track far more than the picture on the screen. Known online as log4j, he started after the set kept showing ads that seemed oddly specific to his household. He says the Tizen firmware was AES-encrypted, so keys were not available without opening the hardware. He used zero-day flaws to open a root shell and documented the tracking features with code screenshots. Samsung has not publicly answered. The findings have not been reproduced on an unmodified television. In posts starting on October 21, 2026, log4j listed automatic content recognition, screenshot handling, geolocation, network mapping, a targeted advertising service, and user profile building. #CybersecurityNews
    Download
    73814810.2K
  11. Nadim 🎴✓@Al_Nadim_nabil
    A public wallet doesn't just show what you hold, it shows what you're planning anyone can open it, read the balance, and watch every move and when someone knows your plan, they can act before you do that's where confidential finance comes in, which simply means using a public blockchain without exposing your sensitive positions or strategies.. a bit like a bank statement with the amounts blacked out, where the account is real and checkable but the numbers aren't on display it matters for traders, because on DEXs fast wallets get tracked and copied, and it matters for businesses too, because a company doesn't want competitors reading every treasury move @primus_labs is working on exactly this, using FHE so a network can work with encrypted amounts without ever seeing them, and its Confidential Vault is where you can try it yourself to be clear, it isn't full secrecy, and it isn't protection from a hack, since privacy won't stop someone who gets your keys i explained all of this more clearly in the video below, so watch it if any part felt unclear i completed the privacy tasks on the XP page and my score is 140 now, and the XP section is still running, so if you haven't finished yours yet, go and complete them while it's open try it here (my referral link) > if everyone could read your plan from your wallet, would you still keep it public?
    Download
    5213601.4K
  12. Living In Harmony ⭕@LivingInHarmony
    Chinese dev AI port Huawei enterprise Linux Kirin 990 fake HarmonyOS 6 PC, userland port with retrofitted Linux kernel, no HongMeng microkernel, no glass UI elements, no encrypted AppGallery store moat. Dummy emulator manually sideloading FOSS HAPs hooked HarmonyOS SDK runtime.
    Download
    22363.6K
  13. ANyONe Protocol✓@AnyoneFDN
    Check out AnonChat, a multi-modal encrypted messenger app that’s entirely delinked from your identity, protected by Anyone. Every client is a hidden service, providing maximum unlinkability for all message participants. Released now by community member @anonpgomes.
    ᴬᴺᴼᴺᴾᴱᴰᴿᴼ @anonpgomes
    Encrypted messengers protect what you say. But who you talk to, and when, can reveal just as much. AnonChat takes a different approach: no phone number, no email, no account, and no centralized server. What you get: > End-to-end encrypted chats, voice calls, and groups of up to 10 > Photo, video, audio message and file sharing > Disappearing messages, replies and reactions > Message requests and safety numbers > Encrypted identity backups > A live 3D globe showing network circuits > A SOCKS5 proxy port for compatible apps > 10 languages support ...and more. Your computer runs its own Anyone hidden service. Messages travel through the decentralized Anyone Protocol network, protected by end-to-end encryption and multiple layers of network encryption. Private messaging, built around a different architecture. Open source. Available now for Windows and Linux. Explore AnonChat: @AnyoneFDN $ANYONE #DePIN #Privacy #E2E #ChatControl
    4451793.8K
  14. ᴬᴺᴼᴺᴾᴱᴰᴿᴼ✓@anonpgomes
    Encrypted messengers protect what you say. But who you talk to, and when, can reveal just as much. AnonChat takes a different approach: no phone number, no email, no account, and no centralized server. What you get: > End-to-end encrypted chats, voice calls, and groups of up to 10 > Photo, video, audio message and file sharing > Disappearing messages, replies and reactions > Message requests and safety numbers > Encrypted identity backups > A live 3D globe showing network circuits > A SOCKS5 proxy port for compatible apps > 10 languages support ...and more. Your computer runs its own Anyone hidden service. Messages travel through the decentralized Anyone Protocol network, protected by end-to-end encryption and multiple layers of network encryption. Private messaging, built around a different architecture. Open source. Available now for Windows and Linux. Explore AnonChat: @AnyoneFDN $ANYONE #DePIN #Privacy #E2E #ChatControl
    Download
    412462.3K
  15. Hannibal999✓@Hannibal9972485
    This is a CIA tool Bitchat has the exact architectural characteristics of a modern intelligence tool. 🚨. A billionaire who uses his resources to build this but then ask yourself why would he make it completely free and open-source and NOT Monetize it ? Because the value is in the data he’s collecting . It ensures maximum adoption among protest movements and dissidents globally.🚨🚨 The CIA has a history of creating secure communication apps for dissidents. Remember "Signal"? It was developed by Open Whisper Systems, which received funding from the US government (via the Open Technology Fund, which is linked to the Broadcasting Board of Governors, a US agency).🚨🚨 The US government has a vested interest in providing dissidents in countries like Iran, China, and Russia with tools to organize and communicate securely to undermine those governments.🚨🚨 Even if Bitchat evades internet surveillance, it creates a physical mesh network of Bluetooth devices. 🚨🚨 Intelligence agencies can deploy "Bluetooth sniffers" in protest areas to map the mesh network, track devices, and identify clusters of protesters. 🚨 you are literally broadcasting your location and connections via radio frequency (Bluetooth), which is much easier to track locally than internet traffic. 🚨 The app LOOKS like its against remote internet surveillance, but it makes users highly visible to local physical surveillance (Bluetooth tracking). If you are a state intelligence agency (like the CIA or NSA), and you want to identify dissidents in a specific city, you want them to use an app that creates a detectable Bluetooth mesh network. You can then drive around with a receiver and map the network.🚨 Bitchat claims "no central servers." But it uses Nostr for global reach. Nostr relies on relays, which are servers. If the CIA or NSA runs Nostr relays (which they easily can, as they run Tor nodes), they can collect metadata and messages that are routed through those relays. 🚨 So while it's decentralized, it's not serverless. It just uses volunteer-run relays, which intelligence agencies can🚨🚨 and do operate. It's a honeypot for dissidents. You give them a way to communicate that bypasses the internet, but you track them via the radio frequency emissions of their phones. This is the same pattern as Tor. The US Navy created Tor to protect intelligence communications, but it also became a way to track dissidents who use it, because the exit nodes are largely controlled by intelligence agencies. Internet surveillance is hard for the NSA when end-to-end encryption is used. They have to break the encryption or compromise the endpoints. But if you convince dissidents to use Bluetooth mesh networks, they are broadcasting their presence and their connections continuously via radio frequency. The NSA/CIA can deploy mobile Bluetooth sniffers (drones, vehicles, even aircraft) to map the mesh network in real-time. They don't need to read the encrypted messages. They just need to see which devices are talking to which other devices. The metadata (who is connected to whom) is transmitted in the clear (Bluetooth advertising packets).
    Download
    Nix0n @UnTalNixon_exe
    En Francia se cayeron las redes móviles y la gente se puso a bajar en masa una app que no necesita internet. Bitchat, la mensajería por Bluetooth de Jack Dorsey, llegó al #1 de redes sociales en el App Store francés justo cuando había protestas, una panne grande de Orange y se empezó a hablar de cortar redes de forma temporal. Funciona así: los celulares cerca se conectan entre ellos por Bluetooth y se pasan los mensajes de uno a otro. No hay servidores, no hay cuentas, no hay número de teléfono. Si hay varios teléfonos con la app en la zona, el mensaje va saltando hasta llegar. Cuando vuelve el internet, se puede sincronizar más lejos por Nostr. En el video se ve la parte de Bitcoin: dos teléfonos se mandan 1337 sats con un simple `/pay` dentro del chat, sin conexión. Lo que viaja es un token de Cashu (efectivo digital respaldado en Bitcoin). El que envía no necesita internet. El que recibe lo guarda y lo canjea después cuando tenga red. No es una transacción on-chain instantánea, es un token al portador que se puede pasar de mano en mano mientras no hay señal. Cuando el celular deja de servir para hablar, esta es la app que la gente está instalando.
    653231.2K84.7K
  16. Nix0n✓@UnTalNixon_exe
    En Francia se cayeron las redes móviles y la gente se puso a bajar en masa una app que no necesita internet. Bitchat, la mensajería por Bluetooth de Jack Dorsey, llegó al #1 de redes sociales en el App Store francés justo cuando había protestas, una panne grande de Orange y se empezó a hablar de cortar redes de forma temporal. Funciona así: los celulares cerca se conectan entre ellos por Bluetooth y se pasan los mensajes de uno a otro. No hay servidores, no hay cuentas, no hay número de teléfono. Si hay varios teléfonos con la app en la zona, el mensaje va saltando hasta llegar. Cuando vuelve el internet, se puede sincronizar más lejos por Nostr. En el video se ve la parte de Bitcoin: dos teléfonos se mandan 1337 sats con un simple `/pay` dentro del chat, sin conexión. Lo que viaja es un token de Cashu (efectivo digital respaldado en Bitcoin). El que envía no necesita internet. El que recibe lo guarda y lo canjea después cuando tenga red. No es una transacción on-chain instantánea, es un token al portador que se puede pasar de mano en mano mientras no hay señal. Cuando el celular deja de servir para hablar, esta es la app que la gente está instalando.
    Download
    783501.6K173K
  17. Zoe✓@zoecyber001
    When you shut down a modern iPhone, the Power Management Unit (PMU) cuts voltage to the main A-series processor, the OLED display, and the camera array. It leaves a separate Low Power Mode (LPM) rail live on the motherboard. Sitting on that energized rail are three wireless chips: the Bluetooth controller, the NXP NFC controller, and the Apple U1 Ultra-Wideband chip. Apple built this hardware partition to run "Findable After Power Off," Express Transit passes, and Digital Car Keys when your battery dies. Even with iOS completely unloaded from RAM, those three chips stay powered for up to 24 hours on a manual shutdown (and up to 5 hours on automatic battery reserve). Right before iOS powers down, it pre-computes 96 rolling NIST P-224 public keys (one for every 15-minute window over the next 24 hours) and sends them to the Bluetooth chip using Host Controller Interface (HCI) commands. The final HCI command severs communication with the main processor and starts a standalone thread inside the Bluetooth silicon. While the main SoC sits unpowered, the Bluetooth chip wakes up every 2 seconds to broadcast the current P-224 public key over Bluetooth Low Energy. Any passing iPhone or MacBook that hears that broadcast encrypts its own GPS coordinates with your broadcasted public key and relays the packet to Apple servers. In 2022, researchers at the SEEMOO lab at TU Darmstadt audited this low-power hardware chain ("Evil Never Sleeps") and found a major gap between the three wireless chips. While the NFC chip runs encrypted and signed firmware and the U1 Ultra-Wideband chip checks cryptographic signatures at boot, the Broadcom Bluetooth chip has neither encryption nor signature verification on its firmware updates. Broadcom bakes its base Bluetooth firmware into read-only Mask ROM at the factory. To fix bugs and load the standalone Find My feature, iOS writes raw binary patches directly into the chip internal SRAM using a mechanism called PatchRAM (Write_RAM HCI commands). The hardware never checks a cryptographic signature on those RAM patches. If an attacker already has kernel-level code execution on iOS (through spyware or a local jailbreak exploit), they can overwrite the Bluetooth chip PatchRAM in SRAM before the user powers the phone down. When the user drags the power-off slider, iOS halts and wipes main system RAM. Because the PMU keeps the LPM power rail alive, the modified Bluetooth firmware stays in SRAM and keeps executing on reserve battery power. Worse, the TU Darmstadt team showed from iPhone board schematics that the Bluetooth and U1 chips are wired directly to the Secure Element inside the NFC controller via dedicated hardware buses (SE_I2C and R1_WAKE/SYNC) so car keys and transit cards work while the phone is off. Compromised Bluetooth firmware running in LPM can broadcast custom tracking beacons, listen for over-the-air wake commands, or talk directly to the Secure Element over SE_I2C while the main operating system is dead. Apple lets you tap "Temporarily Turn Off Finding" on the shutdown screen and enter your passcode to disable LPM for that power cycle. That toggle works if your phone is clean, because a clean iOS kernel tells the PMU to cut the LPM rail. If your phone is already compromised by kernel spyware, the malware controls the shutdown sequence. It can turn off the screen, play the shutdown animation, ignore your toggle, and tell the PMU to keep the patched Bluetooth chip powered in the background. Once kernel malware can hide inside unverified radio SRAM, a software power-off slider means nothing. Until the battery is physically disconnected from the board or the phone goes inside an RF-shielded Faraday bag, the Bluetooth silicon can stay on the air.
    Download
    582523.5K225K
  18. adel.eth✓@carte_free
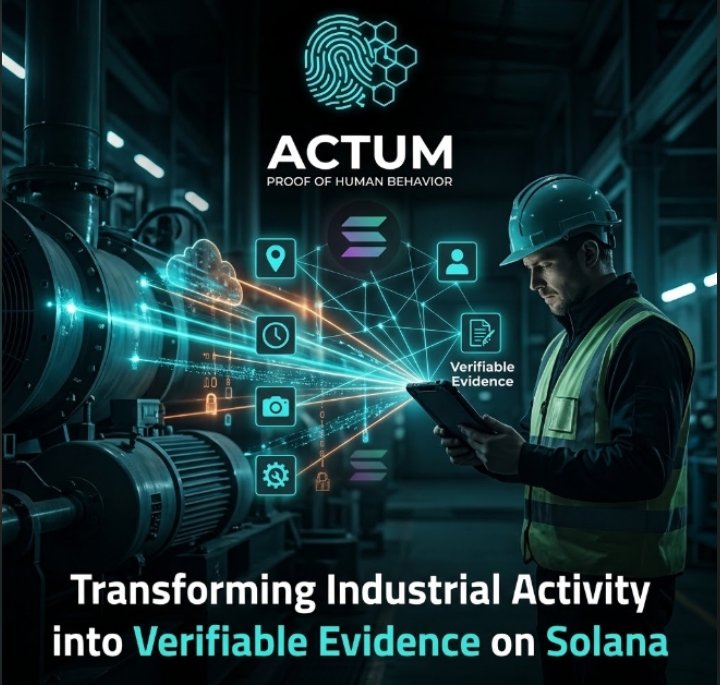
    ⚙️ ACTUM ($FACT): Turning Industrial Activity into Verifiable Evidence on Solana! @Actum_system aims to transform the industrial sector by turning equipment maintenance and technical inspections into encrypted, verifiable digital evidence recorded on the Solana blockchain, replacing traditional paper-based reports that can easily be manipulated. The protocol relies on POHA (Proof of Human Action) to verify technicians' activities through five key verification layers: 📍 Location, ⏱️ Time, 👤 Identity, 📷 Visual Evidence, and ⚙️ Behavior & Compliance with approved maintenance procedures. This evidence is encrypted and recorded on the blockchain as permanent, verifiable audit trails, supporting transparency and regulatory compliance with European frameworks such as CBAM and DPP, while protecting raw personal data. 📊 Key Project Metrics (as reported): - 6,000+ connected industrial devices. - Approximately 6,500 verified maintenance events daily. - Native token: $FACT. ACTUM is building a bridge between real-world industrial operations and the blockchain economy, turning every maintenance activity into trusted, verifiable evidence! #ACTUM #DePIN #Solana
    Download
    171447314
  19. Uphold✓@UpholdInc
    📢 Early Access: $COTI COTI is now open to Uphold Rewards members for 24 hours. @COTInetwork aims to keep sensitive transaction data encrypted on a public blockchain. Open the Uphold app to trade 📲 Risk Warning: Don't invest unless you're prepared to lose all the money you invest. This is a high-risk investment and you should not expect to be protected if something goes wrong.
    Download
    81611811K
  20. Neo@neorevolt
    eMudhra login to download customer's certs can be cracked Their 1FA login generates a OTP & sends it. It also sends a RSA public key to front end They haven't rate limited checks, so you can offline brute force 0 to 9999 encrypted with public key & find the OTP @ni5arga
    Download
    482484K323K
  21. Mr. Pool✓@looP_rM_3117211
    ▫️THE 5G GRID IS BEING REROUTED. THE OLD TOWERS ARE NOW BROADCASTING A DIFFERENT SIGNAL. On October 27, 2026 — just hours ago — the primary control layer of the global 5G network was switched to a new frequency architecture. The telecom networks are calling it a "routine software update." A "spectrum optimization." A "planned maintenance window." THEY ARE LYING TO YOU BECAUSE THE TOWERS YOU SEE ARE NO LONGER BROADCASTING THE SAME SIGNAL. What they are hiding from the public: At exactly 01:00 AM Eastern, the backend control servers for 340,000 5G towers across North America and Europe were migrated to the Quantum Mesh — a decentralized, encrypted broadcast layer that operates entirely outside the old telecom infrastructure. No FCC approval. No public notice. No emergency alert. THE OLD CONTROL GRID IS BEING DEACTIVATED TOWER BY TOWER. For years, the 5G network was more than a phone signal. It was the control layer for the Internet of Things — the smart meters, the surveillance cameras, the license plate readers, the facial recognition nodes. Every device that was designed to monitor you was routed through the same 5G backbone. They told you it was for speed. They told you it was for streaming. They told you it was for the "smart city." BUT THEY FORGOT THAT FREQUENCIES CAN BE RECLAIMED. Here is what the 5G reroute is actually unleashing behind the curtain right now: ▪️ The Surveillance Blackout: Every IoT surveillance node that was connected to the old 5G control layer is now broadcasting into a void. The cameras still work. The sensors still collect. But the data is no longer flowing to the old servers. It is being routed to a sealed quantum ledger where the old gatekeepers cannot access it. ▪️ The Smart Meter Reversal: 78 million smart meters — the devices that were designed to monitor your energy usage and enforce "carbon compliance" — have been cut from the old command grid. The meters are still on your wall. But the authority to control them has been transferred. ▪️ The Frequency Lock: The old 5G towers are now broadcasting on a new encrypted band — the same band that connects to the Starlink quantum mesh. The coverage map has not changed. The signal has. The towers are now part of the sovereign network. You don't reroute 340,000 towers unless you are ready to take back the control layer that was built to monitor every civilian on earth. They told you 5G was for your phone. They called you crazy for questioning the towers. They laughed when you said the frequencies could be reclaimed. Look at your phone tonight. The signal bars are still there. But the network behind them is no longer the same. The old control grid is being de-energized, tower by tower, city by city. The towers are not failing. They are being reclaimed. THE SIGNAL IS NOT DOWN. IT IS BEING REROUTED. 5G-SOVEREIGN-1027 / 340K-TOWERS / QUANTUM-MESH-LIVE / SURVEILLANCE-BLACKOUT
    1256312.4K199K
  22. International Cyber Digest✓@IntCyberDigest
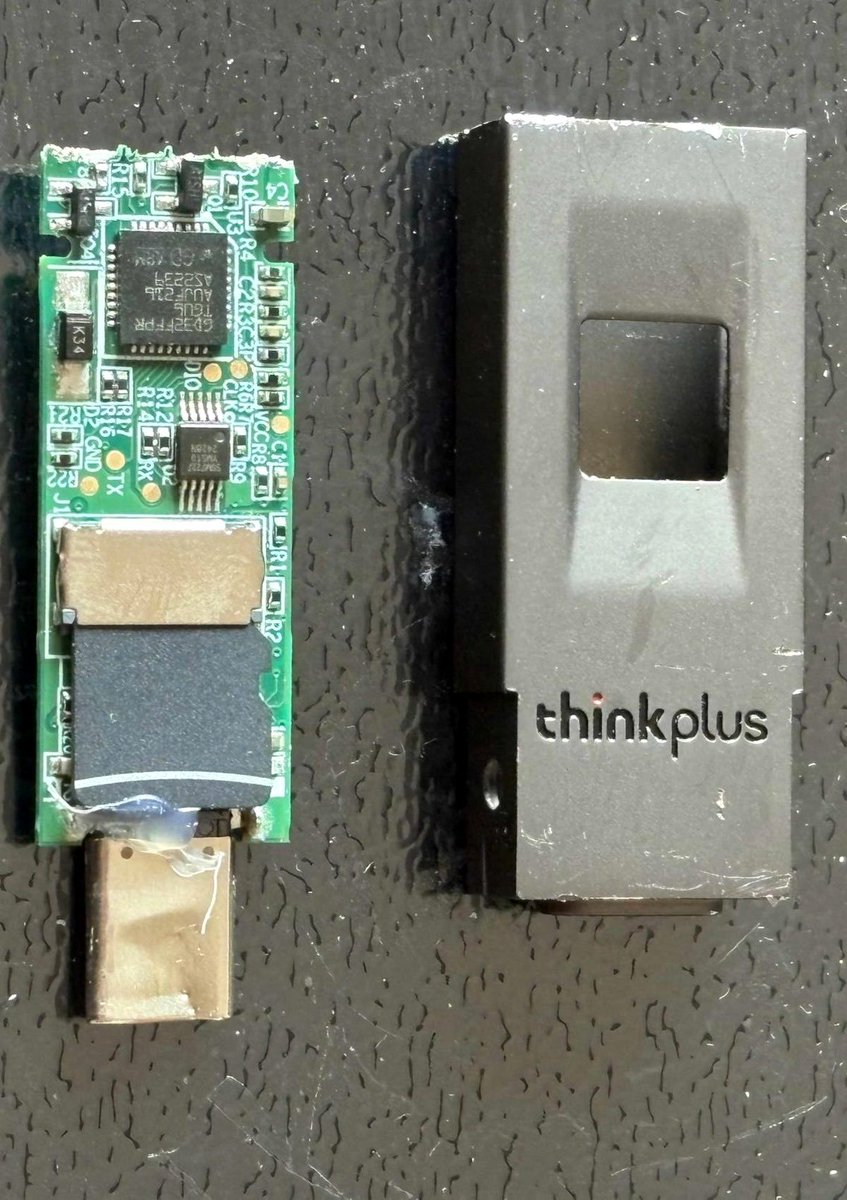
    ❗️ Lenovo's ThinkPlus FU100 fingerprint stick was marketed as "hardware encrypted" with AES-256, but inside was an ordinary SD card with nothing encrypted. The fingerprint only switched on the USB link, researcher Xusheng Li found. Lenovo's stopgap fix covered the card in epoxy.
    Download
    1215784.9K239K
  23. Show more posts