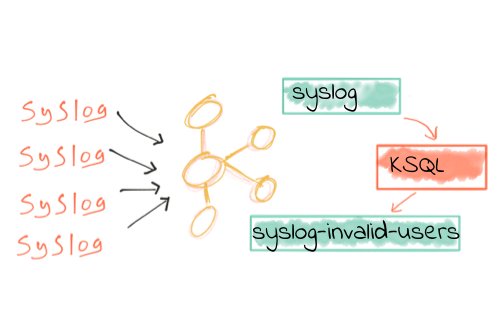
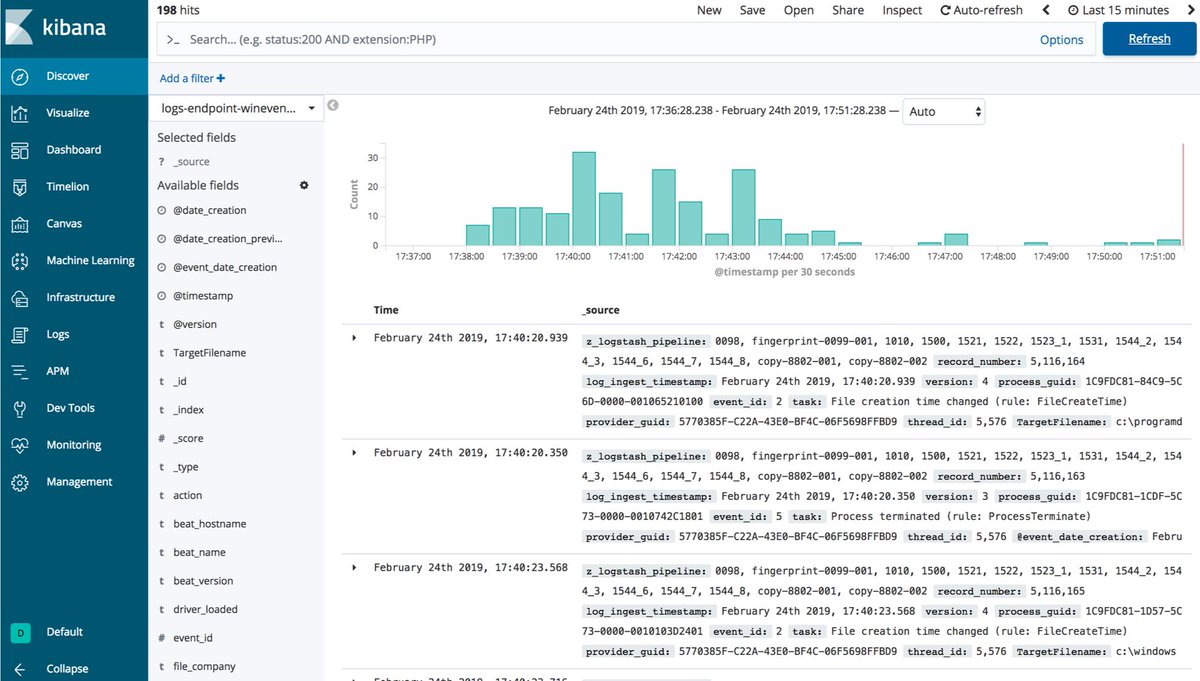
Ever wonder how to use #KSQL for threat hunting? By taking data from Sysmon and streaming it into @apachekafka for processing in KSQL, you can rapidly detect suspicious behavior. @Cyb3rWard0g blogs about joining Sysmon events 1 and 3 in real time:
13063