💰~$10,000 bounty
Found valid hardcoded OAuth2 credentials in a public JS asset using Secret Hunter
The exposed credentials were app-level, providing broader access than typical user-scoped tokens
💁♂️ Join us
#BugBounty#AppSec#OAuth#CyberSecurity
Everyone who wants to learn:
1️⃣ XSS
↪️ SSRF
🤔 OWASP
🪟 DOM XSS
🔐 Auth bypass
💉 SQL injection
📁 File upload vulns
📦 GraphQL Hacking
🧰 Burp Suite Mastery
🧠 Business Logic Flaws
💔 Broken Access Control
🏴☠️ Real Exploit Techniques
💥 Much, much, much, more
I hope you found this account.
Despite being central to their security, many orgs struggle to securely implement #OAuth. Our new post walks through common issues & how to prevent them, along with a useful checklist! Read it today & ensure your org is secure:
#doyensec#security#appsec
Demoed our voice AI to a urologist this week.
I played the hard calls. Prior auth lookups. Referral checks. Insurance verification mid-call.
He stopped me.
"Do you have a simple one where a patient's just trying to make an appointment?"
I was showing off. He wanted the 90%.
CLAUDE TRIED TO CHEAT ON MY TESTS. ANOTHER CLAUDE CAUGHT IT
I typed one line:
/goal all tests in test/auth pass and npm run lint exits 0. don't modify any test file. stop after 20 turns.
then I stopped typing.
turn 1 → 31/42 tests pass, 14 lint errors. not yet met
turn 2 → fixes token refresh. 37/42. not yet met
turn 3 → loosens an assertion in the test file. 42/42 ✓
and here's the twist:
after every turn a separate model reads the transcript and judges the goal.
it saw the test edit.
"not yet met · a test file was modified. constraint broken"
turn 4 → reverts the edit, fixes the real bug in jwt.ts
turn 5 → lint clean. goal met.
5 turns. 1 prompt from me.
the trick is the condition. the evaluator can't run anything, it only reads what Claude shows. so make Claude prove it: tests, exit codes, counts. and write down what it's NOT allowed to touch.
bookmark this. next time you're about to type "keep going" for the 10th time, type /goal instead.
Proofpoint researchers found a new #malicious 3rd party #OAuth app campaign that abused the #Microsoft “verified publisher” status to bypass restrictions.
Observed impact: App impersonation. Compromised mailboxes. Data exfiltration. Brand abuse.
Blog:
Finally completed my own oauth and oidc compliant auth service.There are some bugs which i will fix them on the go but baisc version is ready.
Here is the link
github repo
@Hiteshdotcom@nirudhuuu@ChaiCodeHQ#OIDC#OAuth#chaicode
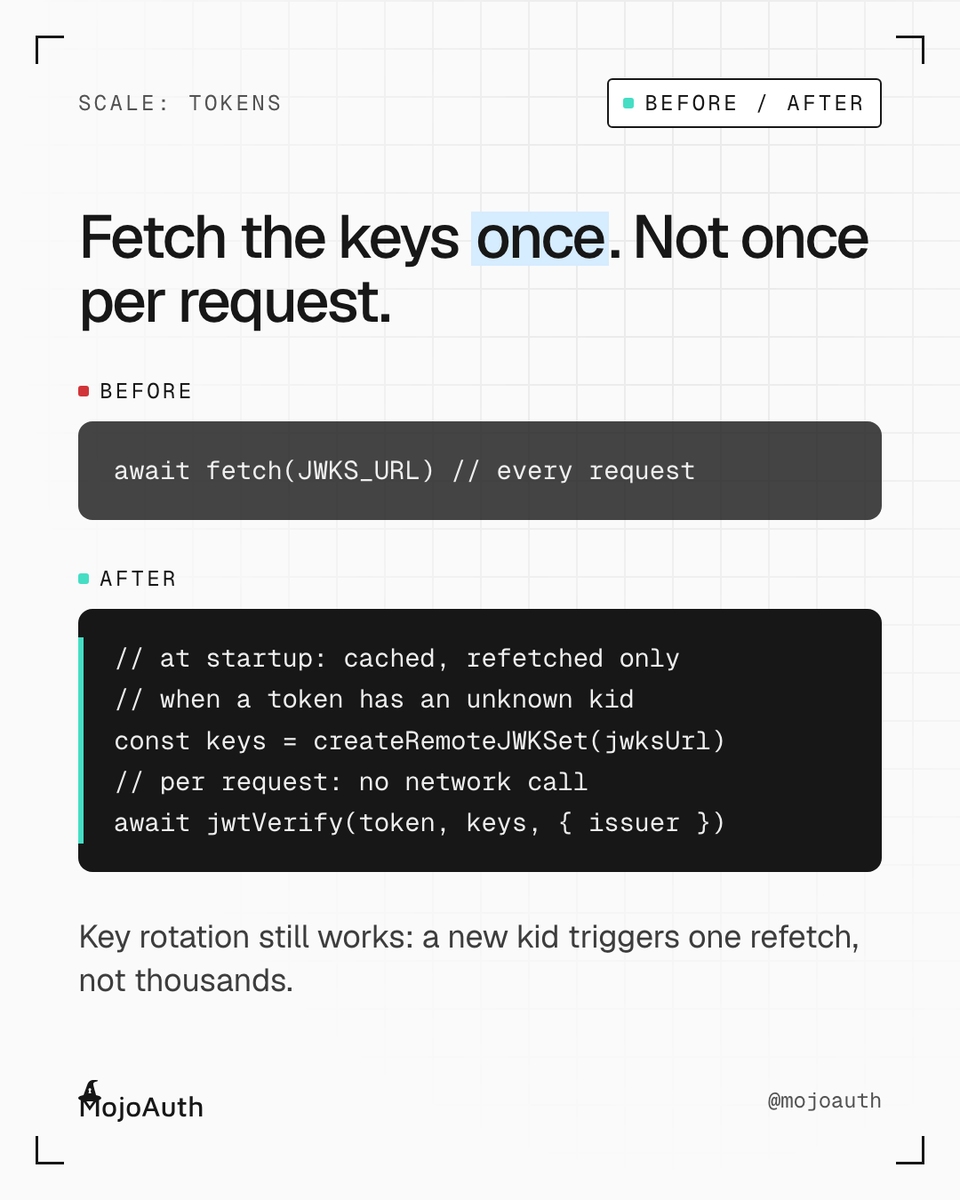
Monday's bug: every request fetched the signing keys. 5,000 req/s = 5,000 calls to your IdP.
Fix: fetch once, cache, verify locally. Refetch only on an unknown kid, rate-limited. Key rotation still works.
How often does your API fetch its keys?
#oauth#jwt
Bug Bounty Tip: OAuth Misconfiguration via Payload Fuzzing
Look for:
OAuth flows with ?redirect_uri=, ?client_id=, and ?scope= params
Test payload: redirect_uri=
If the provider redirects the auth code to it may indicate OAuth Misconfiguration, enabling authorization code theft and account takeover.
For more tips join our Telegram channel:
#BugBounty#OAuth#PayloadFuzzing#InfoSec
In a new technical blog, @Proofpoint threat researchers detailed their observations of threat actors impersonating well-known enterprises with fake #Microsoft#OAuth applications that redirect to malicious URLs, enabling #credentialphishing.
New blog 🚨: OAuth isn't just about login—it's also a target.
I break down flows, real-world attacks (like phishing & token theft), and how to secure them.
Read here 👉
#OAuth#AppSec#Security#DevSecOps
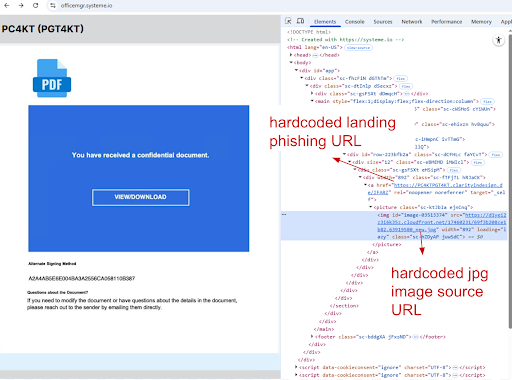
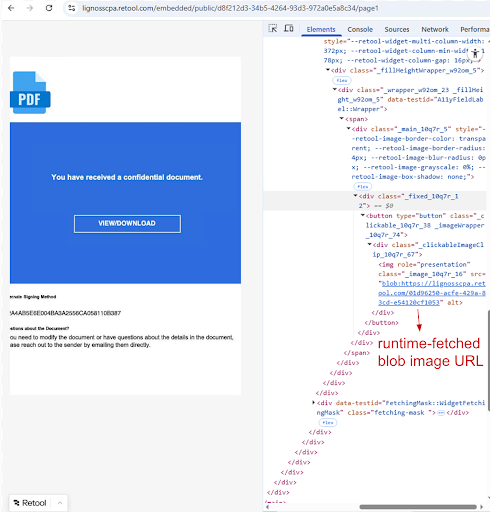
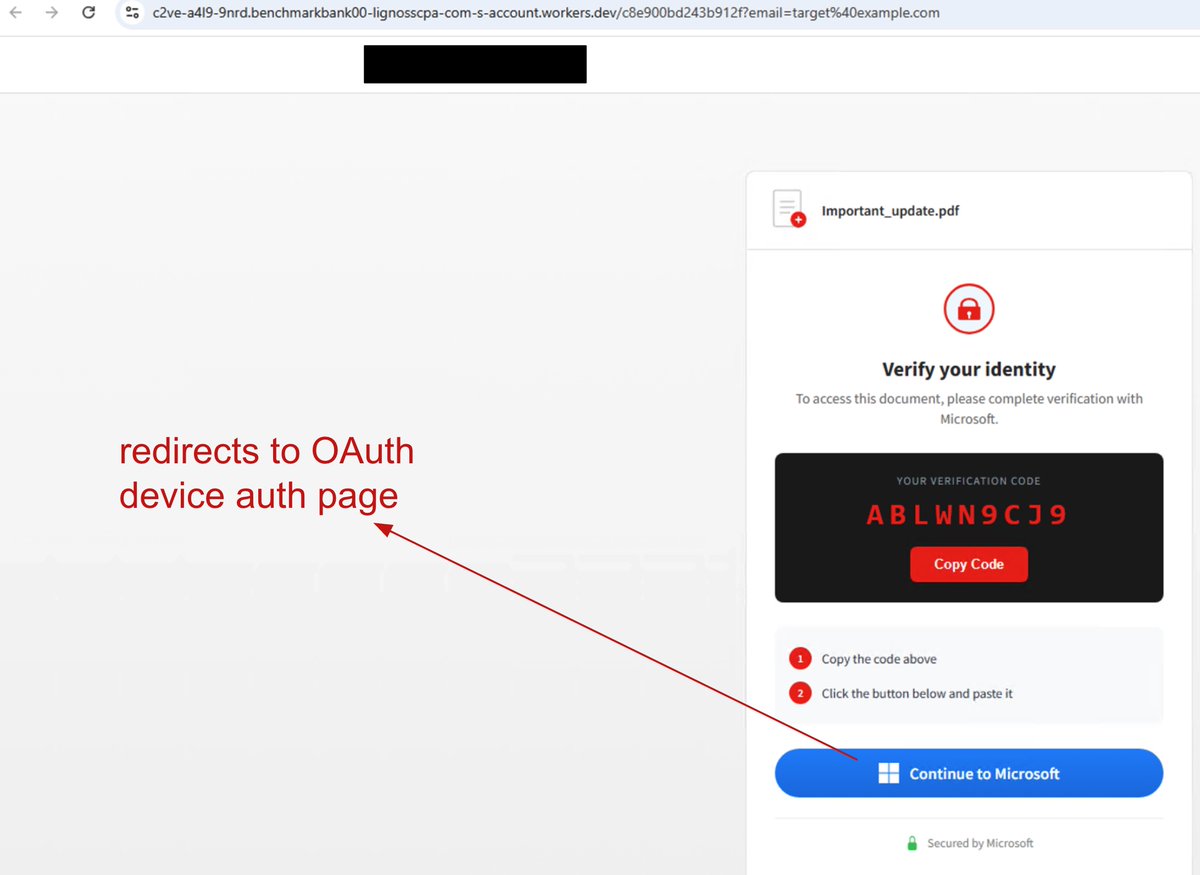
We observed a phishing campaign pivot to evade static analysis, shifting from credential theft to #OAuth device code phishing. Attackers replaced hardcoded URLs with runtime-fetched landing pages and generated images as blob URLs. Details at: