#Trickbot has compromised over a million devices around the world since 2016 and ESET has been tracking its activities since the beginning. When the opportunity to join an international #takedown of their operation presented itself, we did not hesitate.
2020-12-20:📺[Course] #Zero2Automated: Learn
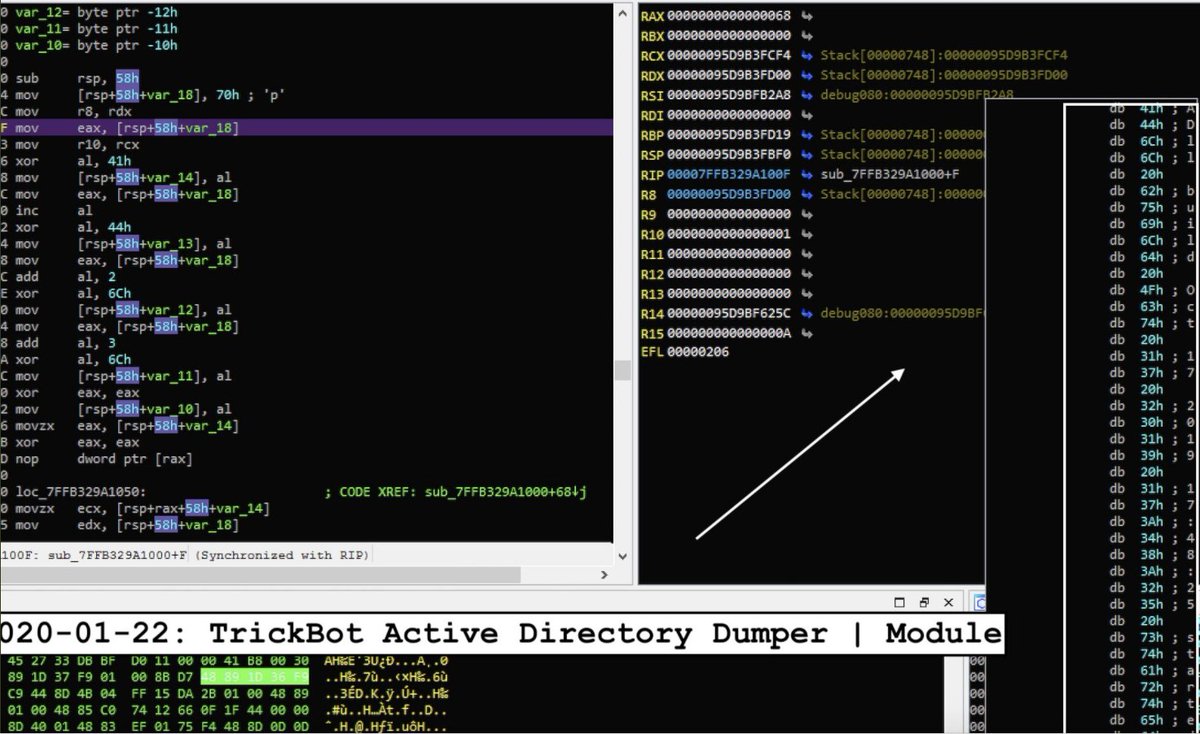
Automation & Malware Reversing Engineering: Capabilities of Rootkits & Bootkits - #TrickBoot Case Study
📚Overview of Boot Process, SPI Controller & UEFI Firmware
only via | #TrickBot
cc @0verflow | @sysopfb
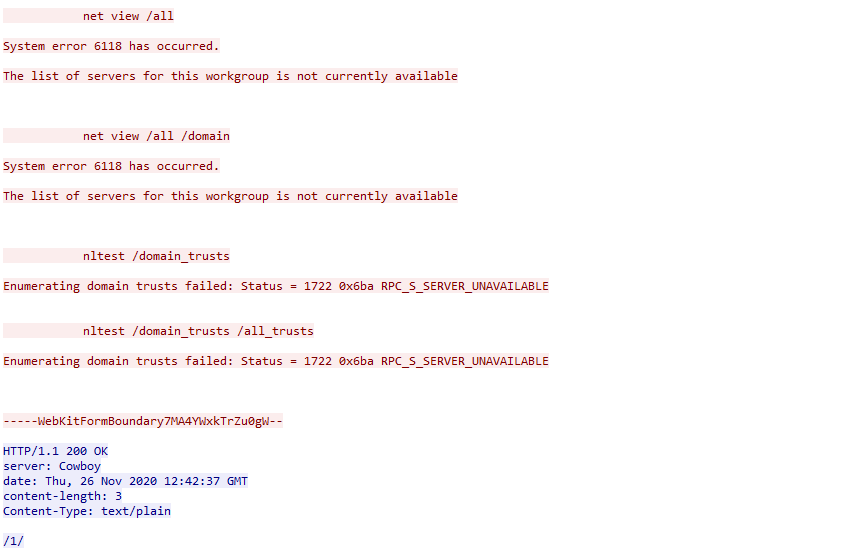
Due to the recent UpT(r)ick of #Trickbot activity we share 2 @Suricata_IDS rules which detect observed Trickbot exfiltration and communication activity
The infamous #Emotet botnet has returned with the help of the #TrickBot malware, nearly 10 months after a coordinated law enforcement operation dismantled its C&C infrastructure in late January 2021.
Read details:
#infosec#cybersecurity#hacking
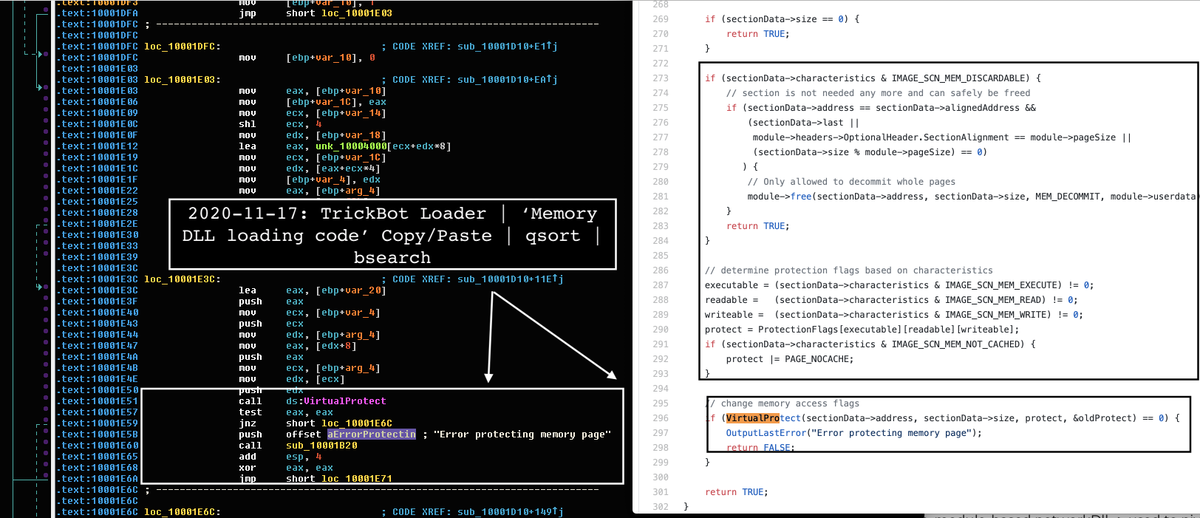
11-18-2017: Let's Learn: #Trickbot banking #Trojan
Checks for various loaded DLL's via GetModuleHandle API after decryption
TL; DR the #malware retrieves a handle for the specified modules associated
with various anti-virus products and sandbox engines to prevent analysis 😉