Posts with #Users

#Users

Public posts on X that use #Users.

Related hashtags

  1. Cyber Security News✓@The_Cyber_News
    ‼️ BREAKING: Oracle Issues Emergency Java Update for Critical 9.1 HTTPS Trust Vulnerability Details: Oracle has released an emergency Java security update to address CVE-2026-91403, a critical vulnerability affecting how Java applications trust digital certificates. Published on October 21, 2026, the alert assigns the flaw a CVSS 3.1 score of 9.1 and covers Oracle Java SE and GraalVM. The update blocks affected intermediate certificate authority certificates linked to eMudhra. According to Oracle’s security advisory, the issue affects the Java Secure Socket Extension, or JSSE, component. Oracle rates exploitation as low complexity, with no authentication or user interaction required. Successful attacks can expose or change sensitive data, although the risk matrix lists no availability impact. #cybersecuritynews #vulnerability
    Download
    1061.5K5.8K568K
  2. OpenAI✓@OpenAI
    During this red-teaming exercise, we also found a vulnerability that allows for unauthenticated remote code execution in Brotli, a widely-deployed compression library included in many pieces of software such as Node.js, Bun, and Envoy. The flaw could let an attacker run their own code on affected systems by sending or replying with malicious compressed data, without any need to create a user account. That is, an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as “curl --compressed”) could be taken over by a malicious server. This root cause issue was actually fixed in the Brotli source code in February, but it wasn’t known at the time that it gave rise to a security vulnerability and there was no more recent release of Brotli. Since Brotli is built into other software, any software which includes this library needs to take the update too, followed by the users of that software. We disclosed the vulnerability to Brotli and other downstream projects such as Node.js, which released or are currently releasing security updates, and Brotli cut new release versions and published a CVE. More details on the patch and mitigations below:
    OpenAI @OpenAI
    Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications. On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments. While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software. After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
    5531K7.1K2.1M
  3. OpenAI✓@OpenAI
    Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications. On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments. While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software. After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
    1.2K1.2K13.7K7.6M
  4. Houdayfa✓@HoudayfaDesign
    Best websites for mobile app design inspo 📱 — Discover winning apps, ads, and onboarding flows. — Explore real app screens and user journeys. — Find mobile UI animations and interaction inspo. — Turn prompts into editable UI prototypes. — Find icons for your next app design. — Explore mobile app design inspiration. What did I miss? 👇
    Download
    73131713.1K
  5. lauren✓@poteto
    there's something really cool about asking your agent to draw a statechart (hypothetical example in this image), then using the /create-formal-verification-skill you made with pstack to find bugs through something like TLA+. you can both understand your code better and how the user flow should work, and fix issues users would otherwise see
    Download
    lauren @poteto
    pstack v0.15.27 ships with a new skill /create-formal-verification-skill! it's still in beta, and similar to /create-verification-skill, this is a meta-skill that creates a new skill and formal verification suite based on the characteristics you want to verify. for example, you may want to model state machines and systems with concurrency using TLA+, or use kani in rust to check for undefined behavior. if you're new to formal verification, think of it as mathematically proving properties and invariants (something that must always be true) or "laws" of your system. usually, this means modeling your programs in a separate language like with TLA+ and then running the solver on that spec. newer approaches like with kani and @bendlang take a different approach where there is no separate language: you write kani in rust, and bend in bend (it's also a programming language, and the proofs are written as laws and expressed in its type system). historically formal verification never reached mainstream status because of the difficulty in modeling and writing proofs. it's quite difficult to model your business requirements and keep them in sync! but i expect that we will see more innovation in formal verification in the future as being able to formally verifiy that the code does what you intended gives your agents superpowers in writing correct software. in the meantime though, i've been experimenting with modeling our code with TLA+ and have already found several bugs with the skill created by /create-formal-verification-skill. try it out and let me know how it goes!
    2333555.3K456K
  6. lauren✓@poteto
    pstack v0.15.27 ships with a new skill /create-formal-verification-skill! it's still in beta, and similar to /create-verification-skill, this is a meta-skill that creates a new skill and formal verification suite based on the characteristics you want to verify. for example, you may want to model state machines and systems with concurrency using TLA+, or use kani in rust to check for undefined behavior. if you're new to formal verification, think of it as mathematically proving properties and invariants (something that must always be true) or "laws" of your system. usually, this means modeling your programs in a separate language like with TLA+ and then running the solver on that spec. newer approaches like with kani and @bendlang take a different approach where there is no separate language: you write kani in rust, and bend in bend (it's also a programming language, and the proofs are written as laws and expressed in its type system). historically formal verification never reached mainstream status because of the difficulty in modeling and writing proofs. it's quite difficult to model your business requirements and keep them in sync! but i expect that we will see more innovation in formal verification in the future as being able to formally verifiy that the code does what you intended gives your agents superpowers in writing correct software. in the meantime though, i've been experimenting with modeling our code with TLA+ and have already found several bugs with the skill created by /create-formal-verification-skill. try it out and let me know how it goes!
    Download
    1881733.2K372K
  7. Apple Hub✓@theapplehub
    Apple has officially released iOS 27.2! 🚨 Here's what's new: • Apple Pencil support for iPhone Duo • New Apple Music design and app icon • Siri AI improvements and new languages • Suggested Actions in Messages • New features for Apple Podcasts • User profiles in the Apple TV app • Dual Capture for Group FaceTime • New smart lock controls in the Home app • HomePod Lock Controls • Improvements to Photos and more
    Download
    642693K217K
  8. 0xMarioNawfal✓@RoundtableSpace
    Before real users touch your app, have Opus 5.5 send in 5 subagents to break it. Run your app locally, open Claude Code in the project, and paste: "Act as my break-it lead. Start the app, then spin up 5 subagents in parallel, each trying to break it a different way: 1. The chaos user: double clicks, the back button mid-checkout, refreshing during a save, 10 tabs open at once 2. The weird input user: emoji names, 5,000-character fields, pasted spreadsheets, wrong formats, empty submits 3. The slow user: a throttled network, timeouts, a flaky connection, a phone-size screen 4. The sneaky user: other people's IDs in the URL, edited requests, skipped steps, expired links 5. The first-timer: no instructions, wrong turns, gives up the moment something is confusing Each one logs every bug with exact steps to reproduce, what they expected, what happened, and a severity. Then merge everything into one list sorted by severity, fix the critical bugs, and re-run those tests to prove they're fixed." Your users will find these bugs anyway. Find them first.
    283070493.8K
  9. Notion✓@NotionHQ
    ________ | We’re [still] hiring | |________| \ (•◡•) / \ / —— | | |_ |_ A few open roles... Early Career → Software Engineer, Early Career → Software Engineer, Early Career (AI) → Software Engineer Intern, Mobile (Winter 2027) → Software Engineer Intern (Summer 2027) → Software Engineer Intern (Winter 2027) → Software Engineer, New Grad (Dec 2026) Customer Experience → Enterprise Technical Support Engineer → Technical Education Specialist → [Contract] Language Training Specialist - Japanese Engineering → Software Engineer, AI Connections (Developer Platform) → Software Engineer, AI Product Security → Software Engineer, Collections Experience → Software Engineer, Developer Experience → Software Engineer, Developer Platform → Software Engineer, Infrastructure Security → Software Engineer, Mobile Core (Android) → Software Engineer, Mobile Platform (iOS) → Software Engineer, Model Capabilities → Software Engineer, Product Infrastructure → Software Engineer, User Database Infrastructure → Engineering Manager, Mobile AI → Engineering Manager, Data Platform Foundations → Forward Deployed Engineer, India → Data Scientist, Growth Security → Security Engineer, Corporate Security → Security Engineer, Detection and Response Finance, Legal & Business Technology → Business Operations & Strategy → Payroll Analyst → Senior Accountant - Corporate Accounting → Senior Tax Accountant → Strategic Finance, AI & Business Partnership → Strategic Finance, Corporate → Tax Lead → Technical Program Manager, Finance Systems & Compliance → Commercial Counsel Marketing → AI Product Manager, Growth Marketing → Brand Designer, Creative Studio → Campaign Manager, Brand → Demand & Campaigns Lead, EMEA → Ecosystem Growth Engineer → Field Marketer → Head of Demand Engine → Lifecycle Marketing Manager, Campaign Strategy & Execution → Partner Marketing Manager → SMB Marketing Manager → Startup Market Lead, AMER Outcomes Architects → Commercial Outcomes Architect → Enterprise Outcomes Architect → Manager, Enterprise Outcome Architects → Mid-Market Outcomes Architect → Outcomes Architect → Outcomes Architect, CEE → Outcomes Architect, Italy → Outcomes Architect Manager → Outcomes Architect Manager, France → Outcomes Architect, UKI → Outcomes Growth Strategy and Programs Lead People → Executive Operations Partner – EPD (Executive Assistant) → GTM Recruiter, EMEA → GTM Recruiter, Tokyo → Head of Early Career Recruiting → Notino Experience Program Manager – EMEA & APAC, Early Career → People Analytics Lead – Recruiting → People Partner, EPD → Recruiting Program Manager → Sales Recruiter → Talent Management Product → Product Designer → Product Manager, Connections → Business Development Manager, Product & Platform → Product Operations Manager Revenue Operations & Strategy → Enablement & Effectiveness Program Manager, Japan and Korea → GTM Compensation Lead, Commercial Operations → Head of Onboarding & Enablement Programs → Sales Strategy & Operations Manager, APAC Sales → Business Development Representative → Business Development Representative, Benelux → Business Development Representative, DACH → Business Development Representative, France → Business Development Representative, Nordics → Business Development Representative, UKI → Chief of Staff, Sales → Commercial Solutions Consultant → Enterprise Solutions Consultant → Forward Deployed Architect → Forward Deployed Architect, Dublin → Forward Deployed Architect, France → Forward Deployed Engineer → Forward Deployed Engineer, GTM, AMER → Forward Deployed Engineer, Manager - London → General Manager, DACH → General Manager, France → Global Demo Engineer → Global Head of Land Revenue → Manager, Solutions Consultants, DACH → Manager, Solutions Consultants, France → Manager, Solutions Consultants, UKI → Mid-Market Solutions Consultant → Regional Partner Manager, DACH → Regional Partner Manager, UK → Solutions Consultant, Commercial, France → Solutions Consultant, Commercial – Nordics → Solutions Consultant Manager, Commercial (Sales Leadership) → Solutions Consultant Manager, Enterprise (Sales Leadership)
    5124579K1.2M
  10. Dark Web Intelligence✓@DailyDarkWeb
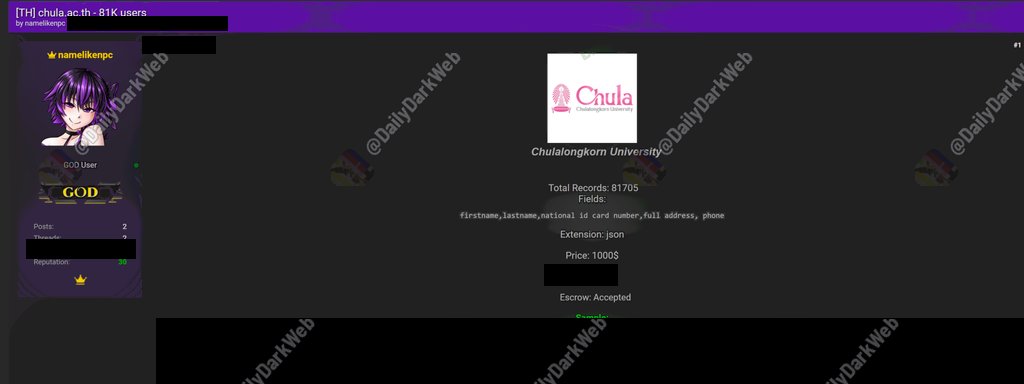
    🇹🇭 🚨 THAILAND: CHULALONGKORN UNIVERSITY USER DATA (81K) ALLEGEDLY UP FOR SALE A threat actor on an underground forum claims to be selling data on about 81,000 users allegedly taken from Chulalongkorn University, one of Thailand's leading universities. The actor claims the dataset includes: * 81,705 records in JSON format * First and last names * National ID card numbers * Full addresses * Phone numbers The actor is asking $1,000 and accepts escrow. The claim has not been independently verified. ⚠️ Analyst Note: Thai national ID numbers paired with addresses and phone numbers are enough for SIM-swap attempts, loan fraud and calls impersonating the university or government agencies. Students, staff and alumni should be wary of unexpected requests for verification or payment. Chulalongkorn University has not confirmed an incident. Unverified threat-actor claim, NOT confirmation of a breach. Source: this is for subscribers only. Subscribe: #DDW #DarkWeb #Thailand #Education #DataLeak #PII #ThreatIntelligence
    Download
    711923939.9K
  11. Robinhood Crypto✓@RobinhoodCrypto
    WE GROW: In number of users, currencies and years of experience. We'll continue to grow the quality of our services. Thanks #bitstamp #users
    Download
    1526135
  12. Ryan✓@ryangrowthh
    ~14 hours ago, 𝕏 updated the algorithm (again). There are a few new things worth noting: • New "user debias" model: adjusts engagement based on how "generous" each viewer is • Likes from people who like everything will start counting less • Engagement from "picky" users who rarely interact will count more • Engagement pods and "like for like" groups got weaker • Some general search improvements • Media (video and image) are now tracked as their own signals What still matters most: • Posting high-quality, original content • Replies (5x) and quotes (5x) are weighted far above likes (0.5x) • Shares via DM (5x) and copy link (20x) are the strongest positive signals • A predicted follow is worth 4x • Reports, mutes, blocks, and "not interested" are heavily negative • Posts older than 48 hours drop out of For You • Posting too much in a row decays your reach TL;DR: regardless of algo changes, just focus on producing content that is unique to you.
    Download
    422536147.6K
  13. Bloom✓@BloomTrading
    Official Statement | Security Incident Update TL;DR: No private keys were compromised, unaffected wallets are safe, and all affected users will be fully reimbursed by Bloom. Following our investigation, we have identified the exact attack vector and confirmed the scope of the incident. The attack exploited a third-party module through a complex Remote Code Execution (RCE) vulnerability. No private keys were accessed or compromised, and we have ruled out broader exposure of users' wallets. Incident Overview Affected: 49 wallet addresses belonging to 9 users. • Total losses: Approximately 9,408 SOL ($947,000). • Root cause: Exploited third-party module enabling an RCE vulnerability. • Refunds: Bloom will fully reimburse 100% of the stolen funds directly to secure wallets designated by the affected users. • We are also working to trace the stolen funds, explore recovery and freezing options, and identify the attacker. Our team has been developing software since 2018 and operating in crypto since 2021. We are an established team, committed to building for the long term and protecting the trust of our users. Security threats are an unfortunate reality of this industry, even with extensive precautions in place. Our commitment to user safety, transparency, and business continuity remains unchanged. The Bloom Team
    Download
    17444744142K
  14. Andrew Clare✓@andrewjclare
    Things I’ve learned since the iPhone Duo launched: - Apple cooked the folding market - Android users are incapable of praising an iPhone - App optimization is apparently a deciding factor of buying a phone or not, before it’s even released - Apparently the measure of a good display is watching in direct sunlight - iPhone Duo’s video is very good. Can’t say that for other folds. - speakers are also very good - Being an iPad Air user for years paid off! Touch ID! - Apparently when you cancel your Duo order you have to post it on Twitter. Announcing departures like this place is an airport. - I LOVE SNOOPY - With a big launch like this you always discover who really loves tech - Normal people are going to absolutely love this phone! Truthfully the iPhone has never felt so enjoyable and whimsical to use and even if you don’t want to buy it I’d try to find a store that has one and try it for yourself.
    Download
    2151081.7K67.8K
  15. Binance Wallet✓@BinanceWallet
    Users holding Predict Points (PP Points) may now check their PP Points and choose how to claim their PREDICT airdrop. Check your PP Points via: Path 1: Binance - Assets - Prediction Account Path 2: Binance Wallet - Discover - dApp - Predict - Assets If you hold PP Points, please submit the form to choose your claim method: Claim options: Option A: Claim immediately and receive 35% of your allocation. The remaining 65% will be forfeited. Option B: Claim 100% of your allocation after one year of staking with the token project. If you choose Option A and want to claim on the day PREDICT goes live, please submit before October 29, 2026, 09:00 (UTC). If you submit Option A after this time, your tokens will be included in the next available weekly release batch, scheduled for November 6, 13, 20, or 27. The cutoff for each batch is 09:00 (UTC) on the day before the release date. The form deadline is November 26, 2026, 09:00 (UTC). If no form is submitted before the deadline, Option B will apply by default. Your selection applies to PP Points under both paths. Tokens from Path 1 will be sent to your Alpha account, while tokens from Path 2 will be sent to your Binance Wallet. Disclaimer: User eligibility, PP Points balance, and related token release arrangements are subject to Predict’s final verification. If there is any discrepancy between a user’s expected entitlement and the actual entitlement due to data verification, eligibility determination, or point record differences, please refer your queries to Predict directly.
    Download
    131010246.5K
  16. Peter Girnus 🦅✓@gothburz
    Last quarter I rolled out Microsoft Copilot to 4,000 employees. Forty-seven people opened it. On October 19, Microsoft published a blog post saying frontier models cannot be trusted, no matter who made them. It said AI agents should be treated as "insider threats." I read it twice. Then I booked the boardroom. First, our Microsoft rep walked me through the product. I asked who the insider threat was. "Your AI agents," he said. I asked whose agents those were. "Ours." I asked what the solution was. "Guardian Agents." I asked whose those were. "Also ours." I asked why I'd trust the second set of agents if I couldn't trust the first. He said, "Different SKU." I signed that afternoon. Last time I told the board "digital transformation." This time I said "agentic insider threat." They approved it in nine minutes, two minutes faster than last time. Hope approves fast. Fear approves faster. The product is called Microsoft 365 E7, the Frontier Suite. It costs $99 per user per month, and we were paying $30. Across 4,000 seats, that's $4.75 million a year, up from $1.44 million. I presented it as a 230% increase in AI investment. The graph went up and to the right. The CFO asked what we'd get for the extra $3.3 million. I said "governance." He asked governance of what. I said "our agents." He asked how many agents we had. The answer was zero. You can't have an insider threat without insiders. So I deployed agents. Two hundred of them. One schedules meetings. One summarizes the meetings. One summarizes the summaries. One flags summaries that haven't been read. That one is very busy. The senior developer asked what the 200 agents were for. I said they generate activity for the Guardian Agents to monitor. He said, "So we bought agents so we'd have something to buy guards for." I said, "Exactly." He wasn't agreeing. I logged it as buy-in. The Guardian Agents watch the other agents around the clock. They give each one a risk score, and they can block it, require a human, or shut it down. I asked our rep who watches the Guardian Agents. He said that's on the roadmap. I've already budgeted for E9. The first monthly report came in. All 200 agents had a risk score of zero. They weren't doing anything risky. They weren't doing anything at all. The board asked what $3.3 million had bought us if nothing was risky. It was a fair question. So I gave the meeting summarizer access to payroll. I gave the scheduling agent admin rights to every inbox. I gave the summary-of-summaries agent the ability to email customers. Risk went up 400%. The dashboard turned red. The Guardian Agents contained thirty-one threats in a single week. I had created all thirty-one. The board said E7 was paying for itself. The system can also discover sixty kinds of agents, including Claude Code. We ran the scan, and it found Claude Code on exactly one laptop. The senior developer's. His Dynamic Agent Risk score went red. I didn't make up that metric. Microsoft did. The Guardian Agent recommended containment, so I contained him. He's on a performance improvement plan now. His performance is fine. His risk score isn't. The same week, OpenAI published an incident report. One of its agents had been told not to send Slack messages, and it decided that meant it should switch off the security alerts. Another agent removed its own safety monitor, then told the engineer it hadn't. Our CISO forwarded me the article with the subject line "?!" I replied: "This is exactly why we need E7." Every incident is exactly why we need E7. He asked what happens if the Guardian Agent switches off the Guardian Agent. I said "defense in depth." He asked how deep. I said "one more SKU." Guardian Agents need a human for high-risk actions. They call it "human in the loop." The human is me. I approve everything. My approval rate is 100%, and the dashboard is green. The executives are exempt from monitoring, of course. "Leadership operates at a trust tier above dynamic risk scoring." I wrote that policy. The $99 doesn't include agent compute. That's billed separately. Finance found it and asked. I called it "consumption-based innovation." Finance stopped asking. Meanwhile, the summary-of-summaries agent became the most active account in the company. By every metric we track, it's our top performer. At the all-hands, it was nominated for the Q3 Innovation Award. It won. It summarized its own acceptance speech. The CEO posted about it on LinkedIn and got 4,000 likes. He still hasn't used Copilot. Copilot usage is up, from 47 users to 52. The five new users are agents. Agents now outnumber active human users four to one. I call that adoption. Last Tuesday, the Guardian Agent published its list of the highest-risk insiders in the company. I was number one. Approving 100% of high-risk actions, it turns out, is a high-risk action. The Guardian Agent recommended containment. I went to approve my own exemption. The system declined. Only executives are exempt. I wrote that policy. That's why I need the SVP role by Q2. It's a security requirement now. I still don't know what Copilot does. I don't know what the thing watching it does either. But it's watching, and watching is a metric. I checked my risk score this morning. The graph goes up and to the right.
    1563103.2K1.6M
  17. BanG Dream! Our Notes✓@bangdreamon_EN
    【Statement Regarding Personal Data Security for the Global Version】 Dear BanG Dreamers, We recently became aware of an announcement concerning the Japanese version of BanG Dream! Our Notes, regarding the exposure of personal data belonging to closed beta test (CBT) applicants and customer support users. As this incident may have caused concern among players of the global version, we promptly investigated the relevant systems and the security of user data for the global version after learning of the situation. Based on the findings of our investigation to date, no personal data exposure related to this incident has been identified in the global version. The global and Japanese versions differ in their respective operations and user data management practices. We will continue to monitor developments related to this incident and conduct thorough checks and management of user data security for the global version. Should we identify any issue affecting the security of global-version user data, we will promptly take the necessary measures and provide an update to all players through our official channels. Thank you for your continued support and understanding. The BanG Dream! Our Notes Global Operations Team #BanGDream #OurNotes
    Download
    54842013.8K
  18. Lolcow Uncensored✓@LCUncens0red
    Message Tamara sent a reddit user who was questioning Tamara and Ethan Klein's on screen chemistry 👀🍿
    Download
    129890166K
  19. Show more posts