Found an authenticated Server-Side Request Forgery (SSRF) vulnerability that allows bypassing the internal-host validation logic by using alternative IPv4 representations such as octal notation
#webhacking#bugcrowd#web2#web3#BugBounty
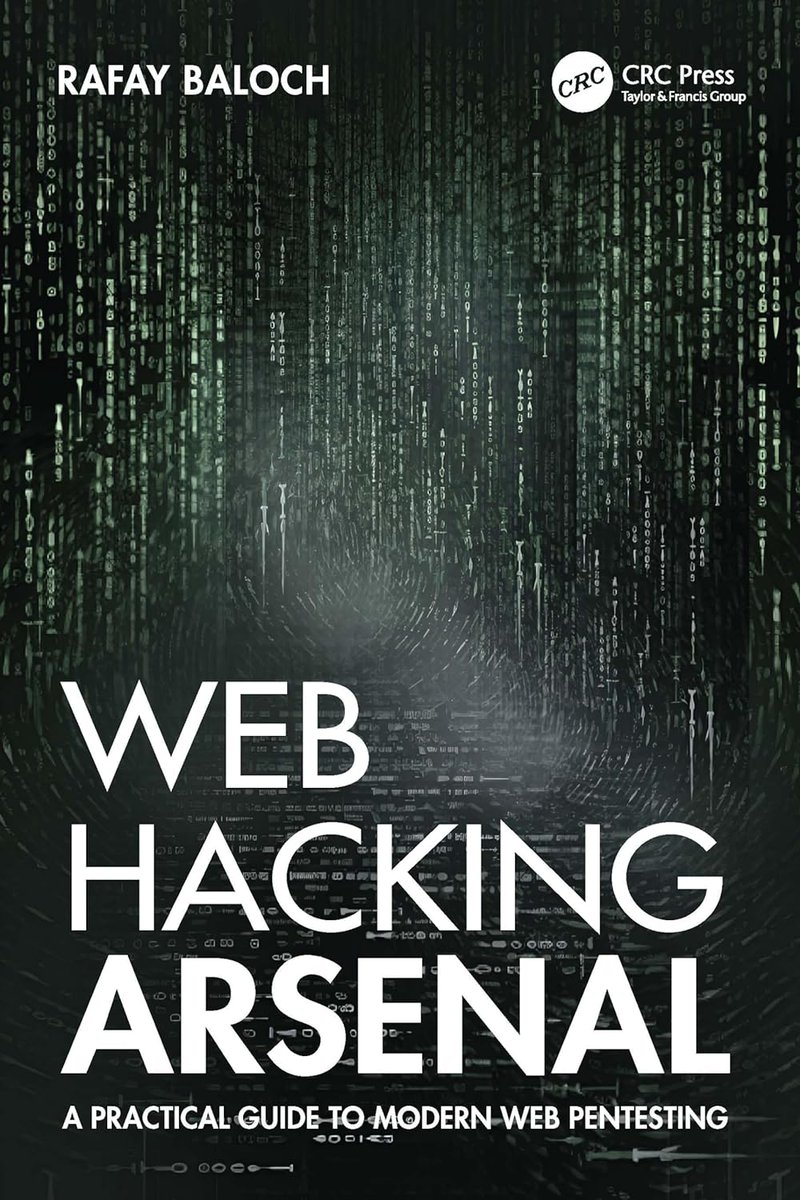
My book, "Web Hacking Arsenal: A Practical Guide to Modern Web Pentesting" is now available on Amazon for Pre-Order. Order your copy today and stay ahead of the game! #CyberSecurity#Webhacking#bugbountytip
Link:
Just completed the Web Fundamentals path on @tryhackme!
Learnt how the web works (DNS, HTTP), manual web app testing, OWASP Top 10, IDOR, XSS, SQLi, Burp Suite basics & more.
Practiced everything through hands-on labs, Juice Shop & the Pickle Rick CTF.
#WebHacking
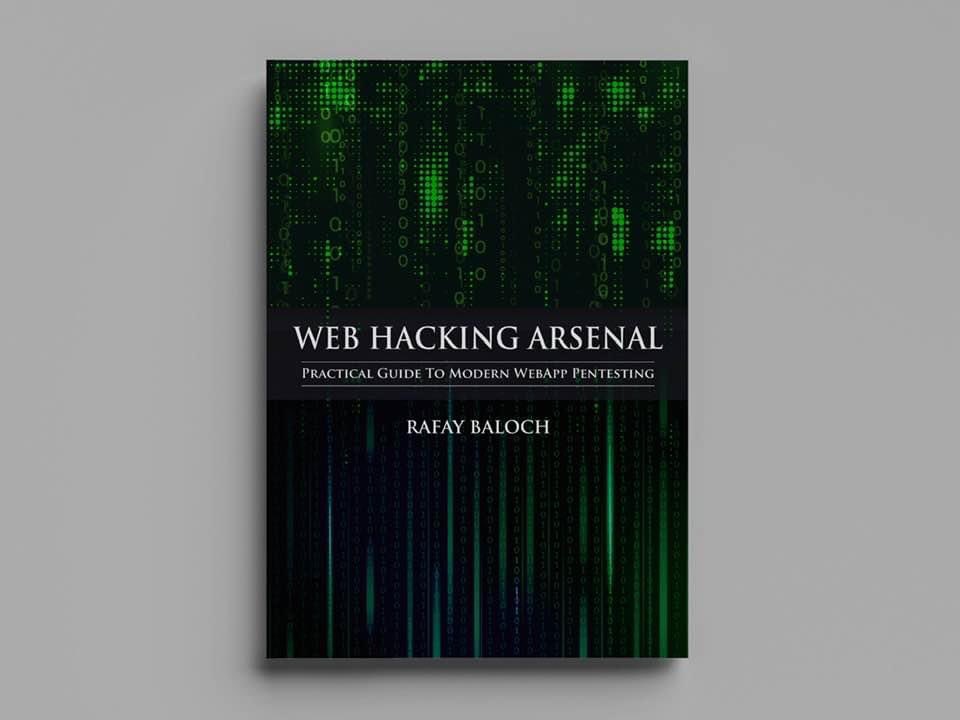
Help me finalize the cover for my upcoming book, "Web Hacking Arsenal" to be released in first quarter of 2024. Suggessions are welcomed along with suggessions for new cover designs. #webhacking#cybersecurity
Day 29: Walking an Application 💻
Finished Common Linux Privesc and completed this room as well today! Started the Jr Pentester path to try and earn tickets for prizes (and of course learn new skills) 🎟️
#100DaysOfHacking#TryHackMe
Day 30: Intro to Web Hacking Module
Completed the following @tryhackme rooms today:
• Content Discovery 🔎
• Subdomain Enumeration 🕵🏾♀️
• Authentication Bypass 🔓
• IDOR 📂
• SSRF 🌐
AND I managed to get the Pentester title 😈
#100DaysOfHacking#THM#WebHacking