Posts with #firewall

#firewall

Public posts on X that use #firewall.

Related hashtags

  1. The Hacker News@TheHackersNews
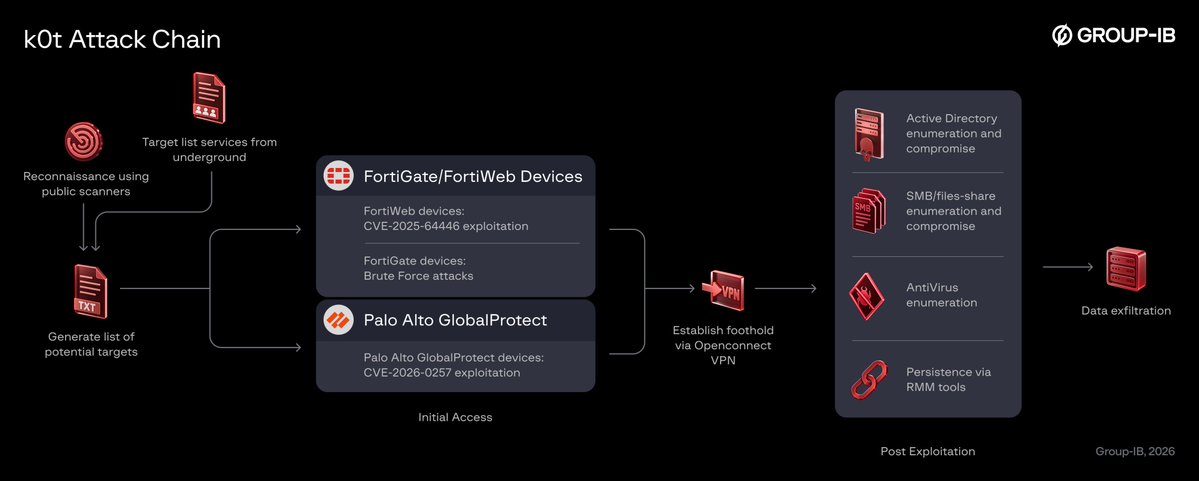
    🚨 Hackers breached enterprise firewalls and VPNs worldwide in a campaign linked to k0t. Over 70,000 exposed credentials identified. Fortinet and Palo Alto devices targeted. Persistent access established. Data exfiltrated. Inside the attack chain and suspected ransomware links:
    Download
    463411.4K227K
  2. Artificial Intelligence@AIGuideHQ
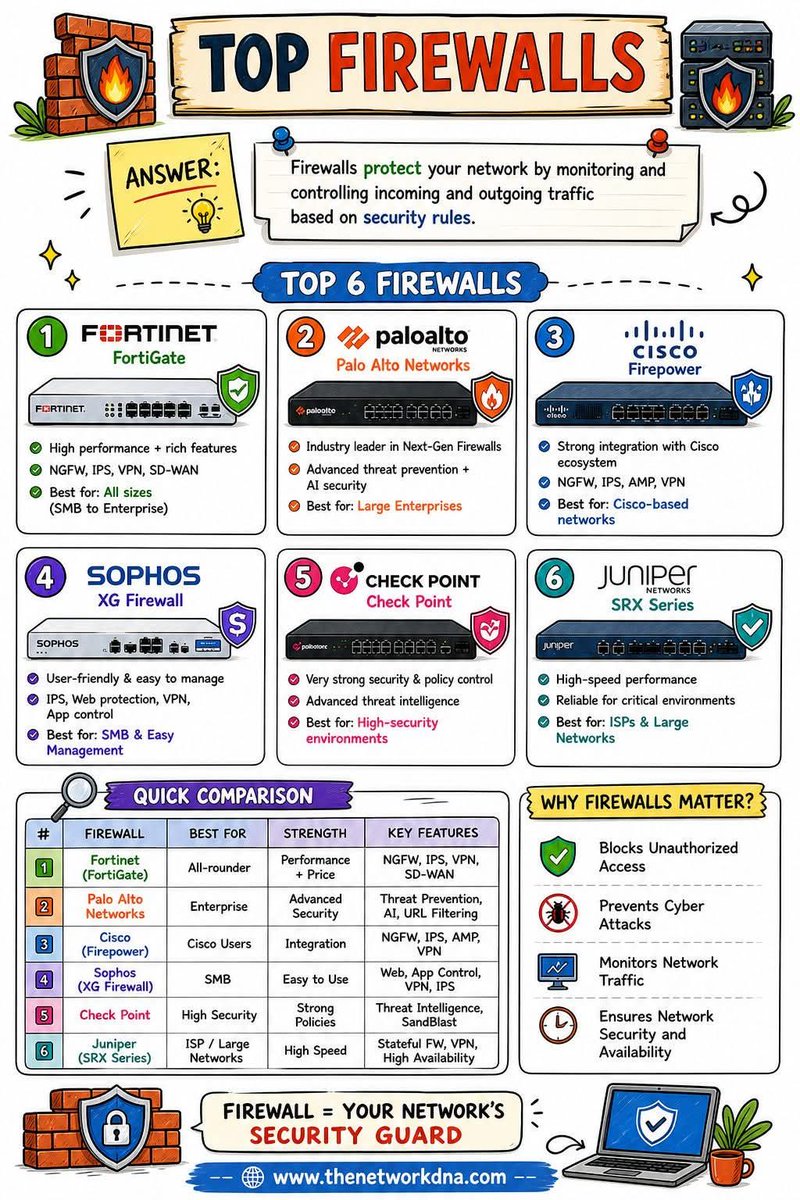
    Top Firewalls Explained – Choose the Right One for Your Network! Firewalls are the first line of defense in any network, protecting your infrastructure by controlling traffic based on security rules Here’s a quick breakdown of some of
    Download
    014188
  3. The Hacker News@TheHackersNews
    🚨 Cisco patches actively exploited ASA and FTD firewall flaw. CVE-2026-76418 (CVSS 8.6) can let unauthenticated attackers remotely crash affected firewalls, causing denial of service. No successful VPN login required. Details + affected versions ↓
    162712726.2K
  4. TheCDI@brendoncdi
    Is a home router guarding your business? A business firewall adds threat blocking, separate guest networks, secure remote access and regular updates. #Firewall #Cybersecurity
    Download
    0004
  5. The Cyber Security Hub™✓@TheCyberSecHub
    Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials thehackernews.​com/2026/10/hackers-breach-enterprise-firewalls-and.​html
    Download
    312292.6K
  6. OpenMatter✓@OpenMatter_
    Last week, the PHP project disclosed two flaws that let anyone on the internet take over a web server without logging in. Every recent version had them, including the newest. Within days, attackers were using them. Here's why even the newest PHP is legacy infrastructure. 🧵
    Download
    1009
  7. OpenMatter✓@OpenMatter_
    @OpenMatter_
    In Rust's default safe mode, a use-after-free won't compile. In 2021, Google said more than 70% of the serious security bugs in Chromium came from memory-safety flaws like these. CISA and the NSA have urged software makers to move to memory-safe languages.
    1001
  8. OpenMatter✓@OpenMatter_
    @OpenMatter_
    Mallory counted 2.6M internet-facing PHP services that report a version. Of those, 73.5% run 8.1 or older, which get no official PHP release. On Oct 26, Dream reported that attackers had chained PHP2Shell with a Linux kernel bug to take over 24 firewalls running PHP 8.0.30.
    1003
  9. Dirk Laurenz✓@DirkLaurenz
    Die fünf Tage Vorsprung haben richtig was gebracht und die Chinesen scheinen jetzt einzubrechen.
    6151078.4K
  10. Hunt.io✓@Huntio
    PHP2Shell One Week Later: Honeypot Shells on the Web, a Path to Root on Palo Alto Firewalls One week after the #php2shell patch, around 25 internet-facing #PaloAlto firewalls have been rooted, the first confirmed production compromises. On the open internet, the same bug is still only landing shells on honeypots. We pivoted from the public exploitation reports into our AttackCapture open-directory data to see who is running it. What we found: - ~25 internet-facing Palo Alto PAN-OS firewalls rooted, the first confirmed production compromises. Reported by Dream Research, verified by Unit 42, matched in operator logs we captured. - The chain is two bugs: php2shell lands as nobody on the PAN-OS management interface, then a kernel bug (Fragnesia, CVE-2026-46300) escalates to root. - On the open web, watchTowr, 0x4D31, and GreyNoise see shells only on honeypots. Wiz and CrowdStrike found none. - 616 php2shell files across live open directories: a shared ASLR-bypass kit byte-identical across four hosts, a custom heap exploit with a log cleaner, and cloned PoCs. - One operator handed the exploit research to an AI assistant and left the session log exposed. Full research, IOCs, and detection guidance 👇
    Download
    310295.8K
  11. TheCDI@brendoncdi
    Your firewall is your front door. • Blocks threats at the edge • Keeps guest Wi-Fi separate • Filters risky sites • Shows what's connected #Cybersecurity #Firewall
    Download
    0002
  12. OPENLYD@OPENLYDINFO
    Every network needs a gatekeeper. A firewall filters network traffic using security rules, helping block unauthorized connections and protect your systems. Set the rules. Filter the threats. Protect your network. #Firewall #CyberSecurity #OPENLYD
    Download
    0003
  13. Security Today@SecurToday
    Researchers have detailed an exploit chain used to compromise #firewalls and breach networks. The attack combined remote code execution and privilege escalation #vulnerabilities to gain elevated access to targeted systems. Read more ⬇️
    00048
  14. Felipe O. Carvalho@_Felipe
    Network firewalls becoming very important again
    cve.now @cvedotnow
    🔴 ClickHouse: remote code execution in database server (CVE-2026-116366) An unauthenticated attacker on the network could run arbitrary code on the server under certain conditions. Patch → 26.3.62.3-lts, 26.8.36.3-lts and more
    001303
  15. cve.now✓@cvedotnow
    🔴 ClickHouse: remote code execution in database server (CVE-2026-116366) An unauthenticated attacker on the network could run arbitrary code on the server under certain conditions. Patch → 26.3.62.3-lts, 26.8.36.3-lts and more
    321321121K
  16. ⚡️🤺✓@92security
    IS THE INTERNET GOING DOWN? Here's what it means for PAKISTAN - Black October Explained You saw the Mario Nawfal post. 19 alerts in one video. It's not theory. It happened this week and Pakistan is directly in it. WHAT HAPPENED GLOBALLY? A flaw called PHP2Shell (CVE-2026-109618 / 109619) - CVSS 9.2/10 CRITICAL - found in PHP itself, the engine that runs 70% of all websites. Found by AI, leaked Oct 20, patched Oct 21 at 6:40 PM PST. Governments in Netherlands, France, Germany, Belgium, Finland, Japan, Australia took their own official sites OFFLINE on purpose to patch. Not hacked. Self shutdown. HOW IT AFFECTS PAKISTAN: 1. Our 300 Govt Websites Are On Alert National CERT (Pak-CERT) issued critical warning. They are auditing 300 government websites - 280 already done (93%). Found critical server misconfigurations and data leak risks. Action: non-essential services shifted to read-only mode, WAF firewalls made mandatory. If you saw some .gov.pk portals slow or down on Oct 22-24, this was why. Not a hack, a defense. 2. Banks Are Already Under AI Attack 1Link - which processes 12 BILLION transactions / year (Rs 90 Trillion) for 42 banks, 1300 gov institutions - said it blocks THOUSANDS of attacks every month. Its CTO said last week: "AI agents are now trying to hack us too. This is a new challenge." And it's not just banks: Oct 19, NCCIA Lahore arrested 3 Pakistanis working with 4 Indians in Canada who used AI-generated passports to open Canadian bank accounts and drain credit cards. Oct 7, NCCIA arrested 40 people in Lahore for loan apps (Gurbat Fund, Jahez Fund) that stole photo galleries and used AI to make fake nudes to blackmail borrowers. 3. What Could Happen To You? Most Pakistani e-commerce, WordPress, NADRA-linked portals, FBR, university sites run on PHP. If the host didn't update to PHP 8.2.35 / 8.3.36 / 8.4.27 / 8.5.12, an attacker can take over the server WITHOUT a password. That means: - Payroll delays (like US platform BambooHR that went dark mid-pay) - Bank data theft via international card networks - The SIM-swap fraud already rising in Pakistan: NCCIA reports gangs where bank staff leaks data + telecom franchise issues duplicate SIM + OTP stolen via JazzCash / Easypaisa This is exactly what PM Modi warned 2 days ago - "Future wars won't be with bombs, but by taking down banks and economies." This is NOT an internet lockdown forever. It was a 24-hour preventive blackout. But if Pakistan's small businesses and hosting companies don't patch, the next attack will not be preventive. Patch your PHP. Enable passkeys. Don't click that FBR refund link. #BlackOctober #CyberSecurityPakistan
    Download
    Mario Nawfal @MarioNawfal
    IS THE INTERNET GOING TO BE LOCKED DOWN? Some very strange pieces are starting to line up. PM Modi warned that future wars could cripple countries without bombs ever falling, simply by taking down banks and financial systems. In Japan, the head of GMO Internet Group raised the possibility of an internet collapse after claims of fraudulent activity hit more than 70 brokerage and FX platforms. At the same time, G7 governments and central banks are running simulations for major AI-driven attacks on the financial system, and several of America’s biggest banks reportedly caught unauthorized AI agents trying to access customer accounts and act on their own. Then there’s Scott Bessent talking about a “grand economic reordering,” with stablecoins and AI part of the conversation around America’s $40 trillion debt. Maybe these are separate warnings. Maybe they aren’t. But if a major cyberattack ever freezes banks, trading platforms and transfers at the same time, people are going to accept almost any replacement system that gets their money moving again. Writer: Sol
    0562K
  17. Mario Nawfal✓@MarioNawfal
    IS THE INTERNET GOING TO BE LOCKED DOWN? Some very strange pieces are starting to line up. PM Modi warned that future wars could cripple countries without bombs ever falling, simply by taking down banks and financial systems. In Japan, the head of GMO Internet Group raised the possibility of an internet collapse after claims of fraudulent activity hit more than 70 brokerage and FX platforms. At the same time, G7 governments and central banks are running simulations for major AI-driven attacks on the financial system, and several of America’s biggest banks reportedly caught unauthorized AI agents trying to access customer accounts and act on their own. Then there’s Scott Bessent talking about a “grand economic reordering,” with stablecoins and AI part of the conversation around America’s $40 trillion debt. Maybe these are separate warnings. Maybe they aren’t. But if a major cyberattack ever freezes banks, trading platforms and transfers at the same time, people are going to accept almost any replacement system that gets their money moving again. Writer: Sol
    Download
    2551.4K5.4K708K
  18. Dhanian 🗯️✓@e_opore
    NODEPORT IN KUBERNETES A NodePort in Kubernetes is a Service type that exposes an application on a static port across the IP addresses of cluster nodes. It allows clients outside the cluster to access an application through a Node's IP address and the assigned NodePort, forwarding traffic to the Service's backend Pods. → WHAT IS NODEPORT NodePort exposes Kubernetes Services through cluster nodes. → Opens a specific port on each eligible Node → Makes applications accessible from outside the cluster → Routes external traffic to matching Pods → Builds on the ClusterIP Service → Commonly uses ports in the range 30000–32767 by default → KEY RESPONSIBILITIES → EXTERNAL ACCESS Makes applications accessible outside the cluster → Clients connect using a Node IP and NodePort → Supports access from external networks when routing and firewall rules allow → Useful for development and testing → TRAFFIC ROUTING Forwards requests to backend Pods → Receives traffic on the assigned NodePort → Routes traffic through the Kubernetes Service → Sends requests to eligible backend endpoints → LOAD BALANCING Distributes requests across available Pods → Supports multiple application replicas → Routes traffic to Service endpoints → Improves application availability → PORT MANAGEMENT Exposes a designated port on cluster nodes → Uses a static NodePort for the Service → Allows automatic port allocation or manual selection → Requires the port to be available within the configured range → SERVICE INTEGRATION Works with other Kubernetes networking features → Builds on ClusterIP → Can be used behind an external load balancer → Supports access to applications without requiring an Ingress controller → HOW NODEPORT WORKS → User creates a NodePort Service configuration → Kubernetes assigns a NodePort → Client sends a request to a Node IP and NodePort → Kubernetes networking rules route the request to the Service → Service forwards traffic to a matching Pod → The application processes the request and returns a response → NODEPORT COMPONENTS → NODE IP The IP address of a Kubernetes Node → Used by external clients to reach the cluster → Must be reachable from the client's network → NODEPORT The port exposed on cluster nodes → Default range is usually 30000–32767 → Provides an entry point for external traffic → SERVICE PORT The port exposed by the Kubernetes Service → Connects clients to the Service abstraction → Routes traffic toward backend endpoints → TARGET PORT The port on which the application container receives traffic → Defined in the Service configuration → Must match the application's listening port → SELECTOR AND ENDPOINTS Identify the backend Pods → Label selectors match eligible Pods → EndpointSlices track backend addresses → Traffic is routed to matching endpoints → NODEPORT VS OTHER SERVICE TYPES → ClusterIP provides internal cluster access → NodePort exposes a Service through a port on each Node → LoadBalancer provisions or integrates with an external load balancer → ExternalName maps a Service to an external DNS name → COMMON USE CASES → Development and testing environments → Accessing applications in small clusters → Exposing internal demos for review → Enabling external access without an Ingress controller → Providing a backend Service for an external load balancer → EXAMPLE NODEPORT CONFIGURATION apiVersion: v1 kind: Service metadata: name: web-service spec: type: NodePort selector: app: web ports: - port: 80 targetPort: 8080 nodePort: 30080 → BENEFITS OF NODEPORT → Simple external access to applications → Uses standard Kubernetes Service networking → Supports traffic routing across multiple Pods → Allows predictable port assignments → Can work without a dedicated cloud load balancer → BEST PRACTICES FOR NODEPORT → Use NodePort when direct node-level access is appropriate → Restrict access with firewalls and network policies where applicable → Avoid exposing sensitive applications publicly → Verify Node IP reachability and firewall rules → Use Ingress, Gateway API, or LoadBalancer Services when they better fit production requirements → Monitor Service endpoints and application health To deeply understand Kubernetes architecture, Services, networking, NodePort, and real-world production deployments, study the complete guide below. Grab KUBERNETES HANDBOOK
    Download
    18452.3K
  19. The Register@TheRegister
    Suspected Chinese attackers chained PHP2Shell with a Linux kernel flaw to root 25 servers, including Palo Alto Networks firewalls linked to US government-affiliated organizations. More here:
    115378.2K
  20. TheCDI@brendoncdi
    What a firewall does for a business owner: • Fewer surprises and downtime • Staff on safe sites • Safe remote access • Easier cyber insurance forms #Firewall #SmallBusiness
    Download
    0003
  21. Satya 📢❗🚨✓@The_SatyaDVV
    🚨 Cybersecurity Alert Cisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash Firewalls 🛡️ Check affected systems and apply the recommended security updates. 🔗 Source: #CyberSecurity #InfoSec
    00038
  22. Show more posts