Posts with #hacker
#hacker
Public posts on X that use #hacker.
Related hashtags
 You are a liar @TrustWallet 🚨 TRUST WALLET COMPROMISED 🆘 How did my Trust Wallet get hacked when your security is supposed to be so strong? My hard earn 915 USDT was transferred from my Trust Wallet, and multiple fake U5DT transactions are being made repeatedly. Don’t put the blame on me. I kept my Trust Wallet secure on a single iPhone. Neither my seed phrase nor my private key has ever been shared anywhere, I don’t use this wallet for anything, and I haven’t connected it to any website. I can say with certainty that Trust Wallet has been hacked. I want my money back. Here is Txhash : 0x31ca896a1a6398af5b8db714a990ee024f351bea5198c042a44e6789b8ce44de #trustwallet


 Trust Wallet @TrustWalletWe are aware of the recently disclosed PHP vulnerability. Trust Wallet’s wallet apps and core infrastructure are not built on PHP. Users are unaffected and no action is required.58811938.3K
 We are aware of the recently disclosed PHP vulnerability. Trust Wallet’s wallet apps and core infrastructure are not built on PHP. Users are unaffected and no action is required.1191981.8K471K
 Claude Code hacked my website in 35 seconds and found 7 security flaws, including a way user data could be exposed I gave Claude one job: think like an attacker, go through my backend, and find everything you can break it started tracing authentication, following user input through the code, and checking how database queries were built 35 seconds later I had a list I didn't want to read > an access control flaw that could expose other users' data > a SQL injection risk buried in a database query > a dangerous command execution path > credentials sitting in the codebase > missing security headers > weak input validation > insecure file access the command execution issue caught my attention first Claude followed user input into a function that could execute system commands, then explained why the code was dangerous and what would need to be tested before calling it an exploitable vulnerability then it found a route that checked whether someone was logged in, but never verified whether they had permission to access the requested resource anyone authenticated could pull anyone else's data you don't need a sophisticated zero day when a missing authorization check is all that stands between an attacker and your users' records I asked it to go through the findings again, explain the evidence, rank the severity, and recommend fixes it turned everything into a report with affected files and specific remediation steps 7 findings, one session, zero manual line-by-line reviewstarmex @starmexxx29111257.5K

 PHP, a programming language that powers as much as 70% of the world's websites and web applications, disclosed two critical security issues on Tuesday, Oct. 20, that could leave it vulnerable to hackers. The issues would allow bad actors to steal information or launch a cyberattack on anyone visiting a hacked website. PHP software powers WordPress, Drupal, Joomla, and Magento websites, according to a blog post by Huntress cybersecurity researcher John Hammond. "When a critical bug lands in PHP itself, rather than in one app built on top of it, the number of places you have to go looking to identify vulnerable PHP versions gets very big, very fast," he wrote. Get live updates at:
 198620942.9K

 Tom's Hardware@tomshardwareNvidia RTX 20, 30, and 40-series GPUs hacked to remove a half-speed AI throttle195044040.9K

 The internet is being hacked right now so I made this emergency video with 6 steps that you can take to secure your account right now: 1. Disconnect apps and agents you don't use 2. Use @1Password with watchtower 3. Turn on two-factor auth with the right app 4. Rotate or retire your API keys 5. Ask AI to update software packages 6. Don't trust breach emails or calls I also share a prompt that you can use to get AI to audit all of the above in the video description. 📌 Watch now:362730490.9K


 how to rescue airdrops & nfts from a hacked wallet never send gas to the hacked wallet. the drainer bot sweeps it in seconds the play: fresh sponsor wallet pays gas > claim + move in one tx > assets land in your safe wallet before the bot reacts > first steps - go to: antidrain[.]dev (remove []) - make a brand new safe wallet. this is where your tokens will labd > how to rescue (website): - tap "start a rescue" - generate a sponsor wallet and put a small amount of gas in it (eth, bnb, etc on the same chain) - pick claim & transfer, unstake or sweep - for an airdrop: paste the hacked wallet key, the claim contract and the claim hex data, then your safe address - hit execute. claim and transfer land in the same tx > how to rescue: (extension, new update) - install extension - set a password > import the hacked wallet > add the sponsor wallet > set your safe address - open transfer to pull tokens, or connect it to the claim site like a normal wallet - it auto finds tokens and nfts still sitting in the hacked wallet - nfts: up to 50 in one tx > what it costs: - nfts: free - tokens, airdrops, native coins: 20% taken inside the rescue tx, you get 80% - gas: paid by the sponsor wallet. withdraw what's left after > what not to do: - don't reuse the hacked wallet after. ever - don't import your new safe wallet's key anywhere in the tool - it can't bring back what's already stolen > works on: - ethereum, base, arbitrum, bsc, optimism, polygon, monad and more evm chains + solana 80% of an airdrop is better than 0% bookmark this before you need it
 41172.6K
 My app got hacked last night and 35,000 profiles were wiped. Here’s what happened / how to prevent it: I bypassed RLS with a view so users could see each other's profiles, and didn't revoke Supabase's default anon permissions, so the public key could delete everyone through it (a truly awful rookie mistake from me). Here’s a prompt so this NEVER happens to you: Audit my Supabase project for security holes. Assume the anon key is public and anyone can call my REST API with it, logged out or with a free account. Check and fix: 1. Every table in public has RLS enabled, and every policy scopes rows to auth.uid(). Flag any policy that is just "true", especially on INSERT, UPDATE or DELETE. 2. Every view: is it security_invoker = true? Can anon or authenticated INSERT, UPDATE or DELETE through it? Revoke write grants on all views. 3. Revoke delete and truncate on all tables from anon, and set alter default privileges so new tables don't get them. 4. List every ON DELETE CASCADE from user tables and confirm that nothing a client can delete cascades into data it shouldn't. 5. Every security definer function: who can execute it, and does it trust a user id passed as a parameter instead of auth.uid()? 6. Every profile column that grants access (pro flags, trial dates, roles, admin) can only be changed by the server. Add a trigger that ignores client writes to those columns. 7. Every API route: it reads the user from the verified JWT, never from the request body, and checks ownership before reading or writing. 8. Crons and webhooks fail closed when their secret is missing, and webhooks verify signatures. 9. No temporary auth bypasses, hardcoded keys or guessable passwords. 10. Add a safety net: limit deletes per request on key tables, keep an audit copy of deleted rows, alert when row counts drop, and confirm backups work. For each finding, show the exact SQL or code fix and explain what an attacker could do today. Then run Supabase Security Advisor and fix everything it reports.10839885111K

 50 Web Sites Google Doesn't Want You to Know About 1.) ' — Bypass any paywall 2.) ' — Millions of free textbooks 3.) ' — Free academic articles 4.) ' — Find free app alternatives 5.) ' — Find where any content is published 6.) ' — Access any old web page 7.) ' — 70,000 free classic books 8.) ' — Free PDF downloads 9.) ' — Free courses from top universities 10.) ' — Solve any math problem instantly 11.) ' — Free Photoshop in your browser 12.) ' — Compress any image for free 13.) ' — Remove image backgrounds for free 14.) ' — Remove objects from photos 15.) ' — Remove video backgrounds 16.) ' — Turn code into art 17.) ' — Stylish code screenshots 18.) ' — Free product mockups 19.) ' — Create mockups without Photoshop 20.) ' — Check if you've been hacked 21.) ' — Scan any file for malware 22.) ' — Send self-destructing messages 23.) ' — Instant disposable email 24.) ' — Auto-deleting file sharing 25.) ' — Permanently save any web page 26.) ' — Find alternatives to any site 27.) ' — Listen to any radio station worldwide 28.) ' — Discover every music genre 29.) ' — Find songs from any TV show 30.) ' — Focus music 31.) ' — Custom focus soundscapes 32.) ' — Cafe sounds that boost productivity 33.) ' — AI academic paper assistant 34.) ' — Search scientific consensus 35.) ' — Visualize academic paper maps 36.) ' — Free academic search 37.) ' — Understand any academic paper 38.) ' — Summarize any YouTube video 39.) ' — AI search engine for developers 40.) ' — Test any regex instantly 41.) ' — Format code cleanly 42.) ' — Read JSON like a human 43.) ' — Understand terminal commands 44.) ' — Effective bookmark manager 45.) ' — Check if any site is down 46.) ' — Reverse image search 47.) ' — Check internet speed 48.) ' — Free PDF editing 49.) ' — Merge and split PDFs 50.) ' — Second-long temporary email The internet is much bigger than what Google shows you. If you’d love to see more content like this, don’t forget to follow for more AI magic.
 24371014.9K

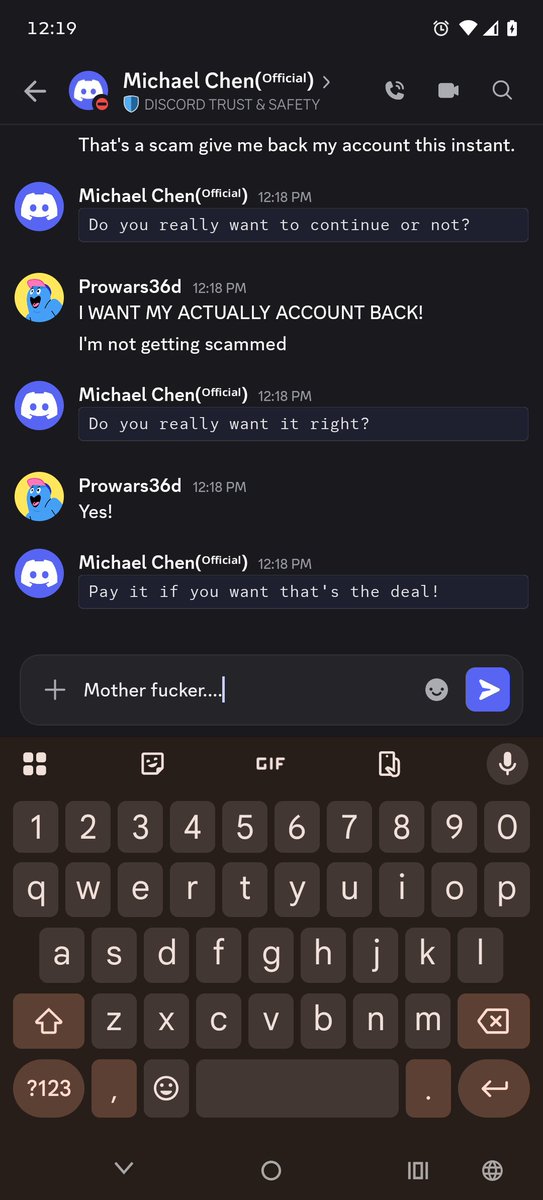
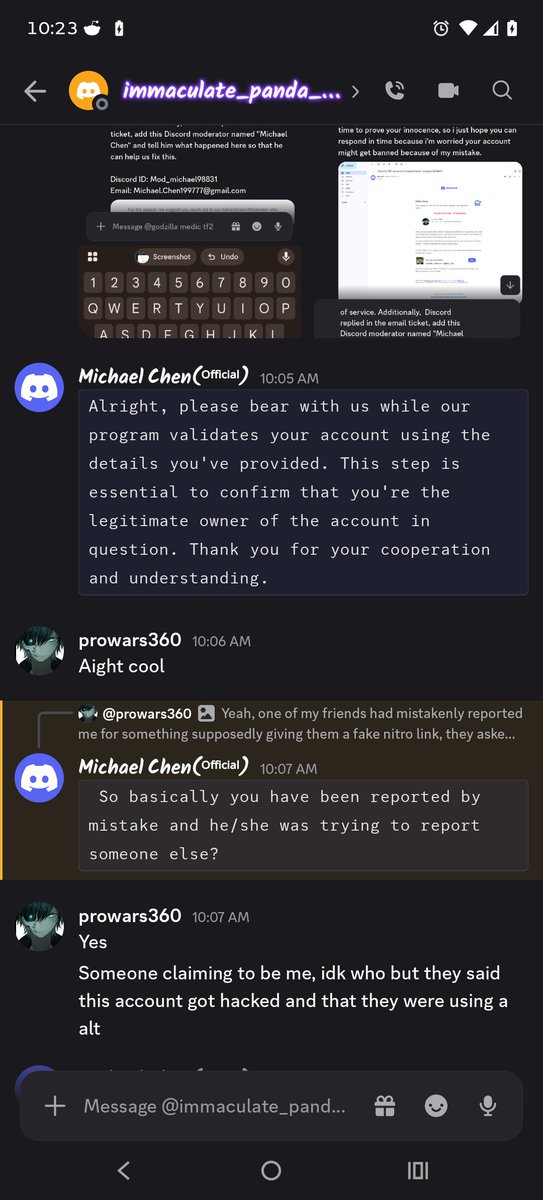
 Jesse the horror artist@JesseWa39010394I NEED HELP MY DISCORD GOT HACKED AND IT ACCOUNT RECOVERY ISN'T HELPING I WANT MY ACCOUNT BACK!! @discord_support


 459741.5K1.2M
 We recently discovered a database with 2 million user records that belongs to @MyFreeCams for sale on a #hacker forum. Due to the nature of the platform, the leak could put #MyFreeCams users at risk of #blackmail, #SocialEngineering attempts and more.14114692

- Show more posts