Posts with #networksecuritymonitoring

#networksecuritymonitoring

Public posts on X that use #networksecuritymonitoring.

Related hashtags

  1. Richard Bejtlich 💾 🇺🇦@taosecurity
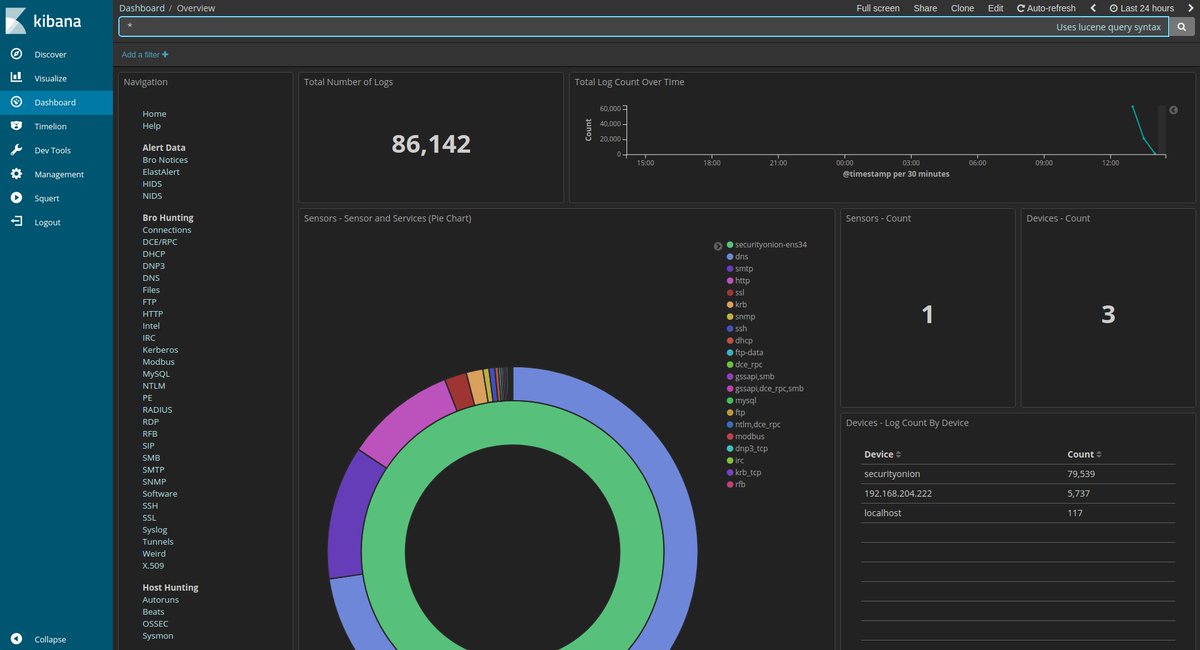
    Collection is 1/2 of detection, but only 1/4 of the entire detection & response process. Detection only matters if you can escalate to a party with will & skill to act, and they indeed resolve the incident. From and my #networksecuritymonitoring 101 class.
    Download
    Florian Roth ⚡️ @cyb3rops
    Log collection is only one half of the story named Security Monitoring The other half is about threat detection—“what should I look for in the log data?” Our Sigma project has 600+ answers to that question & a converter to generate queries for your SIEM
    350198
  2. Florian Roth ⚡️✓@cyb3rops
    Log collection is only one half of the story named Security Monitoring The other half is about threat detection—“what should I look for in the log data?” Our Sigma project has 600+ answers to that question & a converter to generate queries for your SIEM
    4137486
  3. Richard Bejtlich 💾 🇺🇦@taosecurity
    IDS alerts are nice, but we evolved #networksecuritymonitoring ~25 yrs ago because you need more than alerts to validate them. That’s why NSM integrates alerts, transactions, extracted content, & PCAP. Alerts can start an investigation, but they’re usually not enough to solve it.
    0225
  4. Richard Bejtlich 💾 🇺🇦@taosecurity
    This is one of the many advantages of running real open source @Zeekurity on your #networksecuritymonitoring platform, not something that just looks like Zeek: add your own code, or leverage contributed code as happened here with @amazon. We at @corelight_inc will check this out!
    the real blake @voteblake
    Excited to announce I've received open source and legal approval to contribute Ethernet/IP, S7, BACNet, Profinet, and MS-TDS parsers to the @Zeekurity open source #NSM tool, increasing its #ICS coverage
    0517
  5. the real blake@voteblake
    Excited to announce I've received open source and legal approval to contribute Ethernet/IP, S7, BACNet, Profinet, and MS-TDS parsers to the @Zeekurity open source #NSM tool, increasing its #ICS coverage
    741154
  6. Richard Bejtlich 💾 🇺🇦@taosecurity
    To all the academic security teachers: please stop giving your students assignments to run "Bro" to generate alerts and find "bad traffic." @Zeekurity is inherently policy-neutral. Vern built it to generate transaction logs for network traffic, not decide what is good or bad.
    12274
  7. Richard Bejtlich 💾 🇺🇦@taosecurity
    @taosecurity
    Instead, ask students to compare the data generated by open source network tools that create records in various formats, eg Zeek using @Zeekurity, NetFlow v5/v9 (maybe via Softflowd), IPFIX (perhaps via Yaf), etc. Or, compare costs and benefits of alerts, transactions, pcap, etc.
    1622
  8. Richard Bejtlich 💾 🇺🇦@taosecurity
    @taosecurity
    @Zeekurity To be more specific regarding #networksecuritymonitoring: download ch 1 (free) from my last book and ask students to create, then compare and contrast, various NSM data types, from a given pcap. They'll get experience running tools and interpreting output.
    0722
  9. Richard Bejtlich 💾 🇺🇦@taosecurity
    This Memorial Day sale applies to my Practice of #networksecuritymonitoring book, I hear that chapter 9 is still popular among SOC and CIRT managers, but everything except the detailed @securityonion setup material in part II is still pretty useful!
    Download
    No Starch Press @nostarch
    Our Memorial Day sale begins Friday May 22. 30% off everything with free US shipping on orders $50+ at Use code REMEMBER30. Ends 5/25.
    2636
  10. No Starch Press✓@nostarch
    Our Memorial Day sale begins Friday May 22. 30% off everything with free US shipping on orders $50+ at Use code REMEMBER30. Ends 5/25.
    Download
    05775
  11. Richard Bejtlich 💾 🇺🇦@taosecurity
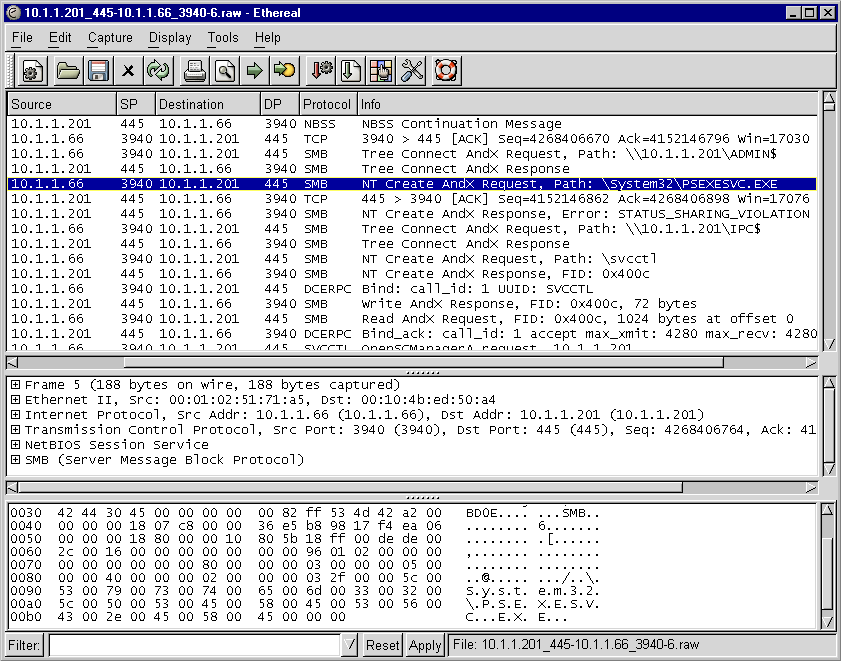
    Amazing, happy birthday #wireshark! I remember when we added Ethereal to our Solaris systems at the #AFCERT. This must have been late 1998 or early 1999? It was so helpful to analysts of all skill levels. #networksecuritymonitoring
    Gerald Combs @geraldcombs
    Reminder: The next remote Wireshark Developer Den is tomorrow. Also, the project is 22 years old today.
    2744
  12. Gerald Combs@geraldcombs
    Reminder: The next remote Wireshark Developer Den is tomorrow. Also, the project is 22 years old today.
    3638
  13. The Aviationist✓@TheAviationist
    The F-22 Is Finally Getting Some Much Needed Upgrades:
    12173
  14. Richard Bejtlich 💾 🇺🇦@taosecurity
    Ethereal was a game-changer IMHO. Previously I used Snoop and Tcpdump on Solaris, or did manual protocol analysis. Ethereal and later Wireshark made it a lot easier to understand traffic. We integrated it into our #afcert workflow and I loved it. #networksecuritymonitoring
    Today In Infosec @todayininfosec
    1998: Ethereal was first released publicly as version 0.2.0. Its creator, Gerald Combs, thought it was cool that Bob Metcalfe named Ethernet after luminiferous ether so he picked a name beginning with ether. Since 2006 the network protocol analyzer has been known as Wireshark.
    628104
  15. Today In Infosec@todayininfosec
    1998: Ethereal was first released publicly as version 0.2.0. Its creator, Gerald Combs, thought it was cool that Bob Metcalfe named Ethernet after luminiferous ether so he picked a name beginning with ether. Since 2006 the network protocol analyzer has been known as Wireshark.
    Download
    5143364
  16. Show more posts