Posts with #toolshell

#toolshell

Public posts on X that use #toolshell.

Related hashtags

  1. CISA Cyber@CISACyber
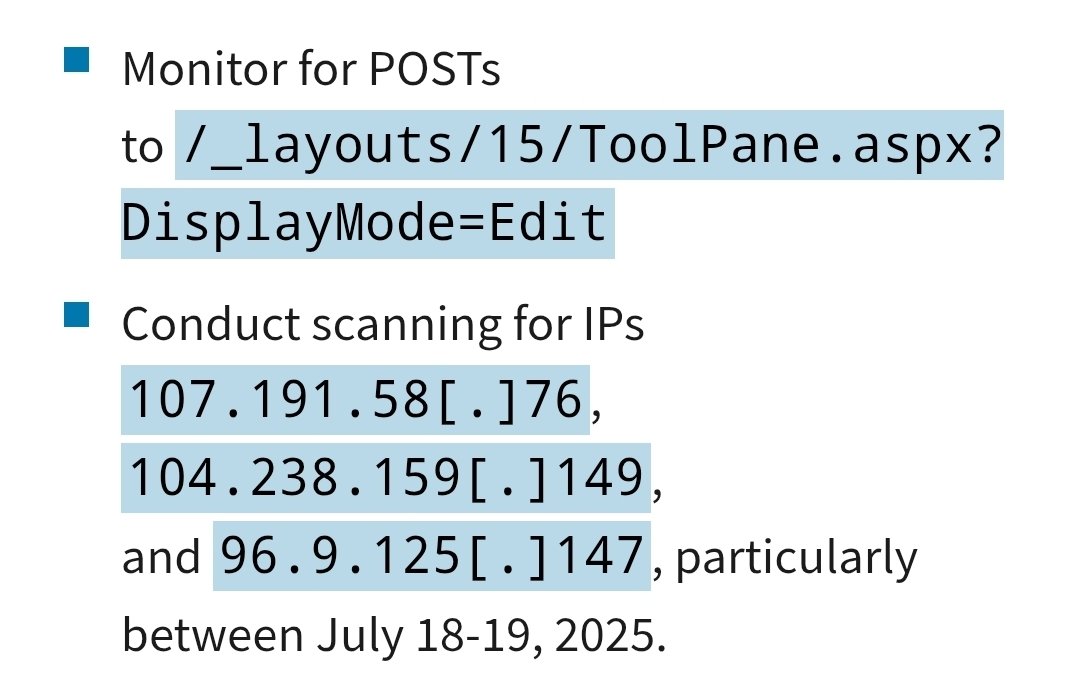
    We’ve released a Malware Analysis Report with analysis & detection signatures on files related to Microsoft SharePoint vulnerabilities known as #ToolShell. Review IOCs and detection signatures in our 🆕report 👉
    Download
    19423829.9K
  2. Gi7w0rm✓@Gi7w0rm
    Quck analysis of new #ToolShell payload observed by @leak_ix: Paylaod is a .dll executed in memory. Sha-256: 3461da3a2ddcced4a00f87dcd7650af48f97998a3ac9ca649d7ef3b7332bd997 It collects System Info and the sensitive machine key. Sends back in response. Single Request takeover.
    Download
    Gi7w0rm @Gi7w0rm
    ⚠️ New payload in the relation to #ToolShell . Attackers now don't need the static file anymore, leaking keys from memory without leaving the file. This means the existence of a file is not a reliable IoC anymore.
    44714825.3K
  3. Gi7w0rm✓@Gi7w0rm
    ⚠️ New payload in the relation to #ToolShell . Attackers now don't need the static file anymore, leaking keys from memory without leaving the file. This means the existence of a file is not a reliable IoC anymore.
    LeakIX @leak_ix
    Just a heads-up, attackers found a way to leak information, including keys entirely from memory. Checking for "the file" is not enough to assess compromise and warrant key rotation anymore. Just rotate your keys if you were exposed, period.
    1175128.7K
  4. CISA Cyber@CISACyber
    Update: See newly added info to our #ToolShell Alert. We’ve included info on ransomware deployment, new webshells involved in exploitation, & detection guidance 👉
    Download
    2327010.3K
  5. Kai Nazarkardeh 🇨🇦✓@kainazarkardeh
    Patched #SharePoint after #ToolShell? You may still be exposed. The suspected China-nexus actor behind #Warlock ransomware (Longlegs / Storm-2603) is still breaking into on-prem SharePoint more than a year later. Recent victims include a water utility, a telecom provider, a regional government body, and a university across Portuguese- and Spanish-speaking countries. How they operate: → Exploit SharePoint, then drop web shells
→ Steal ASP. NET machine keys and forge signed payloads for RCE
→ Kill EDR via BYOVD (K7RKScan.sys, CVE-2025-1055)
→ Hide remote access inside VS Code tunnels
→ Stage ransomware in SYSVOL and let domain replication deploy it In one intrusion, #EDR was disabled on 40+ hosts in about 2 hours, and ransomware hit 33+. What to do now: 1Patch, then rotate ASP. NET machine keys and restart IIS. Stolen keys survive patching. 2Hunt for web shells in SharePoint LAYOUTS directories. 3Enforce the vulnerable driver blocklist / HVCI. 4Block VS Code tunnels on servers. 5Alert on executables written to SYSVOL. Your detection window is hours, not days. Source: #Symantec Threat Hunter Team #ThreatIntel #Ransomware #SharePoint #CyberSecurity
    002140
  6. Wiz✓@wiz_io
    🚨 Research update: #ToolShell is back, and it just leveled up. Two new vulnerabilities in Microsoft SharePoint Server, CVE-2025-53770 (RCE) and CVE-2025-53771 (auth bypass), are being actively exploited in the wild. 🔓 Attackers are chaining them to >> • Bypass authentication with a forged header • Drop a stealthy web shell • Steal server keys • Achieve full unauthenticated RCE These are bypasses of bugs hashtag#Microsoft patched just days ago. SharePoint Online is safe, but self-managed SharePoint in cloud or on-prem is not. 📊 According to Wiz data, 9% of cloud environments are still running vulnerable versions. Full technical breakdown & timeline 👇
    Download
    06242.6K
  7. CISA Cyber@CISACyber
    Malicious actors are exploiting RCE vulnerability CVE-2025-53770 to compromise on-prem SharePoint servers. See our Alert for info & mitigations on exploitation activity, known as #ToolShell. 👉
    Download
    45714444.7K
  8. @onyphe.io@onyphe
    [WRITE-UP] Identifying #Sharepoint boxes vulnerable to #ToolShell, at scale 👉 Last weekend we watched a wave of realization hit Sharepoint admins around the world as they were confronted with a set a vulnerabilities... Read more:
    035370
  9. Alexandre@Alexpinsard
    Une faille #SharePoint a touché l’Agence nucléaire 🇺🇸, exploitée via un zero-day par des hackers d’État 🇨🇳. Microsoft a patché, mais l’alerte est orange : environnements on-prem = risque +. Passez le patch #ToolShell dès maintenant. v/@nextinpact
    Download
    00298
  10. Telefónica Tech EN✓@TefTech_EN
    📰 Our weekly cybersecurity newsletter is here! 🔵#Microsoft patches two new 0-day exploits in #ToolShell attacks against SharePoint 🔵#APT35 launches AI phishing campaigns against Western researchers And much more! 👇
    012255
  11. LeakIX✓@leak_ix
    Just a heads-up, attackers found a way to leak information, including keys entirely from memory. Checking for "the file" is not enough to assess compromise and warrant key rotation anymore. Just rotate your keys if you were exposed, period.
    05715631.6K
  12. CISA Cyber@CISACyber
    Update: As we continue to monitor the scope & impact of #ToolShell, we’ll update our related Alert with new info. Today, we’ve added info on new CVEs & additional mitigations on exploitation activity. 👉
    Download
    223559.5K
  13. Kryptomania@kryptomania84
    "Verwundbar sind Organisationen, die Sharepoint auf eigenen Servern laufen haben – wer Microsoft 365 nutzt, ist nicht betroffen." #Microsoft #toolshell
    00286
  14. @onyphe.io@onyphe
    💥 [UPDATE] We now have a reliable vulnerable detection method (check-based) for CVE-2025-35770. 📌 Nearly 500 unique IP addresses are vulnerable, counting numerous governmental organizations. #SharePoint #ToolShell
    @onyphe.io @onyphe
    [BLOG] Massive Exploitation of SharePoint Following Disclosure of CVE-2025-53770 📣 "On 11,000 IPs, we count 139 already compromised. Among the victims, a few banks, and a fair number of government organizations" 👉 Read: Cc @BleepinComputer
    148753
  15. @onyphe.io@onyphe
    [BLOG] Massive Exploitation of SharePoint Following Disclosure of CVE-2025-53770 📣 "On 11,000 IPs, we count 139 already compromised. Among the victims, a few banks, and a fair number of government organizations" 👉 Read: Cc @BleepinComputer
    0111K
  16. Steven Lim✓@0x534c
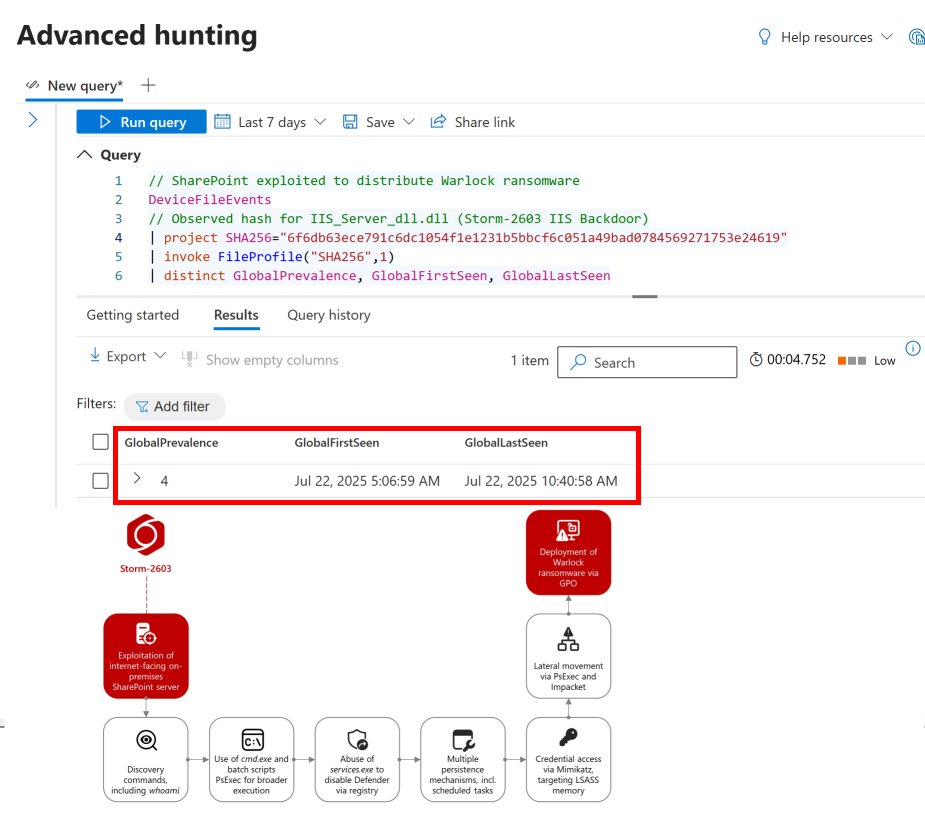
    #ToolShell #Warlock 🚨 KQLWizard intel update: Storm-2603 exploited CVE-2025-53770 on 4 internet-facing SharePoint servers on 22 July, deploying Warlock ransomware via ToolShell. Initial access confirmed via observed hash for IIS_Server_dll.dll (Storm-2603 IIS Backdoor). #Cybersecurity #Sharepoint #RCE
    Download
    2291199.3K
  17. @onyphe.io@onyphe
    💥 [NOUVELLES] Nous avons maintenant une méthode fiable de détection de la vulnérabilité CVE-2025-53770. 📌 Près de 500 adresses IP uniques sont vulnérables, comptant de nombreuses organisations gouvernementales. #SharePoint #Toolshell Cc @MondeInformatiq
    @onyphe.io @onyphe
    [BLOG] Exploitation large échelle de la CVE-2025-53770 sur Microsoft SharePoint Server 📣 "Sur 11 000 IP, 139 sont compromises. Parmi les victimes, des universités, quelques banques, et des organisations gouvernementales …" Cc @MondeInformatiq
    0482K
  18. @onyphe.io@onyphe
    [BLOG] Exploitation large échelle de la CVE-2025-53770 sur Microsoft SharePoint Server 📣 "Sur 11 000 IP, 139 sont compromises. Parmi les victimes, des universités, quelques banques, et des organisations gouvernementales …" Cc @MondeInformatiq
    0241K
  19. Show more posts