Peter Todd✓

@peterktodd

@opentimestamps founder pgp: 37EC7D7B0A217CDB4B4E007E7FAB114267E4FA04 25JUPL6ksapY1iCLWkFcSaXaA6Ar3W7JDCdPjeSApump 🇺🇦🇮🇱🇹🇼

1.2K Following205K Followers82.4K Posts
  1. Peter Todd✓@peterktodd
    The hardest part about being a contrarian is knowing when not to be.
    Pedro L. Gonzalez @emeriticus
    The mind virus of conspiratorial thinking has been devastating. It completely paralyzes analysis and reduces everything to entertainment, fodder for clicks, traffic, and attention. It’s like a caricature of the Straussian close reading of texts: the “real” meaning is always hidden from view, and being unable to see it means you don’t have access to esoteric insights and knowledge. In reality, you’re just reading it wrong. In the case of Russia right now, nobody really knows what’s happening. But that doesn’t matter; all you have to do is come up with the most absurd theory, and the more absurd it is, the truer it must be.
    156105723957K
  2. Pedro L. Gonzalez✓@emeriticus
    The mind virus of conspiratorial thinking has been devastating. It completely paralyzes analysis and reduces everything to entertainment, fodder for clicks, traffic, and attention. It’s like a caricature of the Straussian close reading of texts: the “real” meaning is always hidden from view, and being unable to see it means you don’t have access to esoteric insights and knowledge. In reality, you’re just reading it wrong. In the case of Russia right now, nobody really knows what’s happening. But that doesn’t matter; all you have to do is come up with the most absurd theory, and the more absurd it is, the truer it must be.
    Download
    55474071M
  3. Peter Todd✓@peterktodd
    Peter Todd
    RT @opentimestamps: I've released new versions of the OpenTimestamps Client, and the python-opentimestamps library, fixing several bugs and potential security issues: One notable issue is that the ots-git-gpg-wrapper, used in the Git support, wasn't properly passing *only* timestamped data to the underlying gpg command. So it's possible that an attacker could have constructed a timestamped and signed git commit that appeared to have a timestamped signature, when in reality that signature was *not* timestamped. Secondly, python-opentimestamps did not correctly handle the case where a fork was followed by two identical opcodes. That is, a non-minimally-encoded timestamp where the two opcodes following a fork uselessly did the same thing. Previously, the second branch would silently overwrite the first; now python-opentimestamps raises a DeserializationError exception in this case. While python-opentimestamps would never produce such a serialized timestamp, it's possible that other implementations did, and the API of python-opentimestamps may be changed to handle this case in the future. Other than that I don't think any of the remaining issues are all that serious in the typical way that OpenTimestamps is used — manual validation of timestamps in rare exceptional circumstances, and creating timestamps with the default calendars. That said, if you are doing automated validation of timestamps for an important use case, you should check the release notes and make sure these issues don't affect you. Finally, there's been some recent fixes made to the OpenTimestamps Server, including a potential bug/DoS attack that could trigger as the wallet runs out of funds. Once triggered, this bug would prevent fee-bumping, thus preventing confirmation of timestamp transactions. If you run your own server, you should check the latest git history. That said, very few people actually need to run the OpenTimestamps server; in almost all circumstances you should just be using the public calendars. Thanks to Ferdinando Ametrano for his work finding and fixing these issues. -@peterktodd
    080816
  4. Peter Todd✓@peterktodd
    Peter Todd
    RT @DrewPavlou: Judge Alexandre de Moraes signed an order demanding Bolsonaro hand over his passport WITHIN SEVEN MINUTES of the close of voting. Before votes had even been counted. What did he know about the vote results that enabled him to make this order within seven minutes of polls closing - seemingly confident that Bolsonaro had already lost?
    09410824
  5. Peter Todd✓@peterktodd
    Peter Todd
    RT @AlexBerenson: URGENT: Sweden will not offer mRNA-based Covid shots to its citizens this winter, only older protein-based jabs - a stunning rejection. Expect other countries to follow as we learn more about the long-term risks of repeated mRNA/LNP dosing.
    05130868
  6. Peter Todd✓@peterktodd
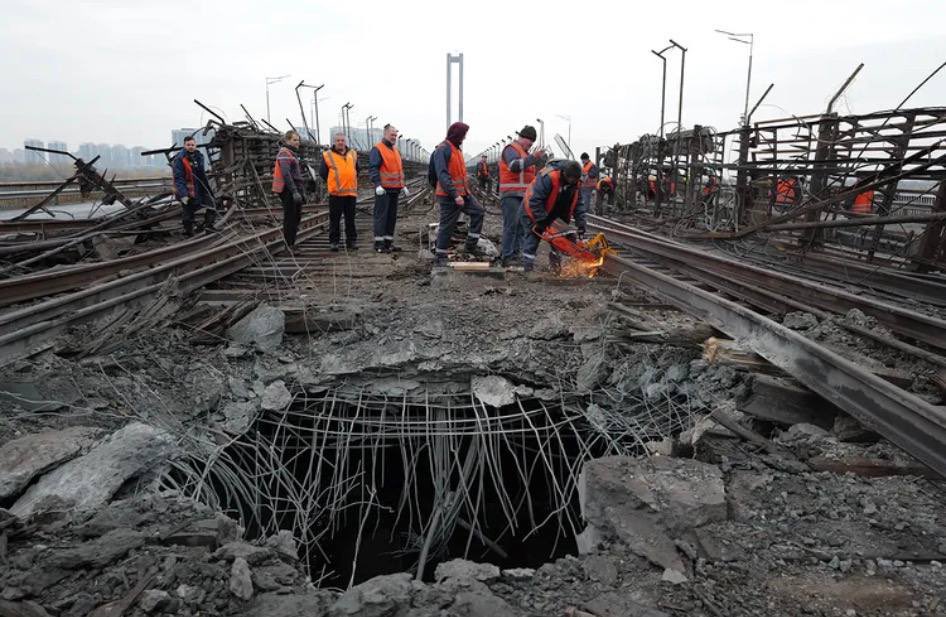
    That's a direct hit between the subway tracks. Russia is trying to cut Kyiv in two.
    Saint Javelin @saintjavelin
    During the missile attack on Kyiv, russia hit the Pivdennyi Bridge.
    62243.7K
  7. Saint Javelin✓@saintjavelin
    During the missile attack on Kyiv, russia hit the Pivdennyi Bridge.
    Download
    68935436.7K
  8. Peter Todd✓@peterktodd
    Peter Todd
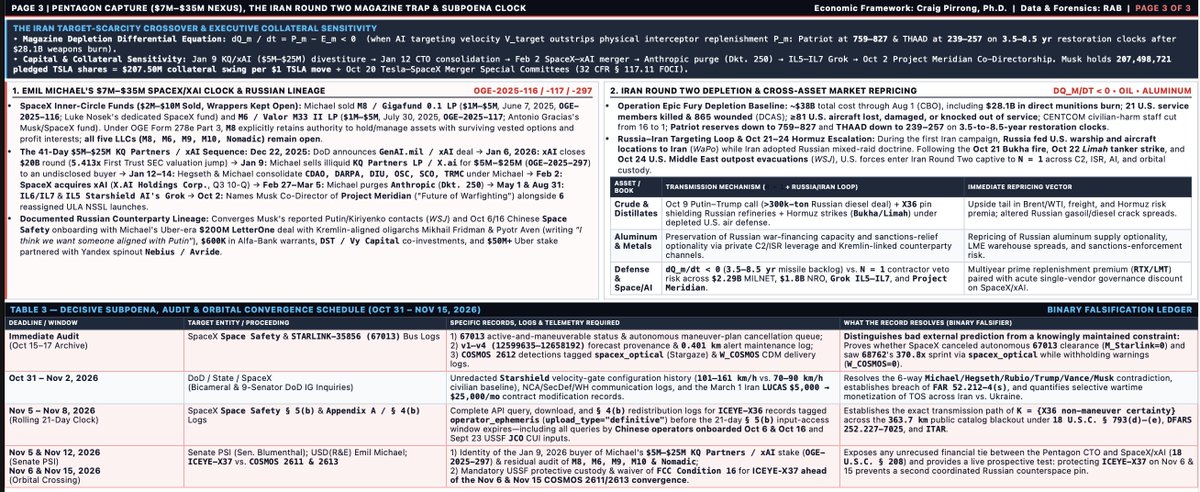
    RT @LibertyLynx: Another note for SpaceX attorneys and PR: There was no need to issue an alert at all. Your own internal data showed a safe 2km pass. But you issued a 400m collision alert anyway. Why? Because the alert itself is the weapon. Issuing it triggered FCC Cond 16, legally freezing ICEYE so it couldn't dodge. STARLINK-35856 didn't use its auto-evasion. It just parked there and kept the false alarm blaring while Russia sprinted in. It wasn't an accident.
    Lynx @LibertyLynx
    SpaceX Blocked A U.S. And NATO Satellite to Assist a Russian Intercept After Crippling Ukraine's Air Defenses The Math Proves the Reality that Musk doesn't want you to see. On Oct 13-14, SpaceX restricted Starshield/Starlink during a 39-missile Russian attack, cutting Ukrainian drone intercepts by 23% and stranding U.S. personnel in Kyiv. Forty-eight hours later (Oct 15), SpaceX blocked U.S.-licensed NRO, Space Force, and NATO radar satellite ICEYE-X36 in orbit so Russia's COSMOS 2612 weapon could intercept it (99.89%-99.98% posterior) Our Model Demonstrates that the Russian intercept of the US/NATO ICEYE X-36 satellite (contemporaneous with the throttling of Starlink) would not have been possible, and almost certainly not been attempted, without SpaceX resources. At a material opportunity cost, Russia sprinted its COSMOS satellite to intercept ICEYE X36. Based on a previous attempt in June during which X36 maneuvered to evade COSMOS, Russia knew that this would be successful only if X36 could not maneuver. On October 15, SpaceX fixed X36 in place by issuing a collision alert for a sub-kilometer approach with its Starlink 35856 when SpaceX's own data shows that the actual distance was 4.8-5.0x as great. SpaceX issued no warning to COSMOS despite the fact that its sprint was far more threatening than the stable X36 orbit. SpaceX did not maneuver its Starlink 35856 satellite to clear the supposed collision risk. How, absent coordination with SpaceX, could Russia have known that SpaceX would take actions that (a) misrepresented the danger posed by X36, and (b) resulted in the fixing of X36 thereby enabling COSMOS's successful intercept? Thus, SpaceX was directly involved in simultaneously compromising Ukraine’s defensive and offensive capabilities. The conjunction of these two events makes innocent explanations untenable. The Pentagon Capture & Iran Round Two Trap: Pentagon CTO Emil Michael who cashed out $7M–$35M from Musk’s inner-circle SpaceX vehicles (M8/Gigafund 0.1 and M6/Valor M33 II) and KQ Partners / xAI (selling xAIfor $5M–$25M three days before taking over CDAO/OSCand 21 days before SpaceX bought xAI, while keeping M8, M6, M9, M10 & Nomadic open) and Pete Hegseth purged rival Anthropic in two hours, surrendered combat command over US drones used to attack Iran to Starlink’s "Terms of Service," and on October 2 named Musk Co-Director of Project Meridian to design the Pentagon's "Future of Warfighting" just as America enters Iran Round Twowith depleted Patriot/THAAD magazines and Russia feeding U.S. warship/aircraft locations to Tehran. SpaceX’s actions in Ukraine raise serious questions about its alignment with US security interests and its reliability as a cornerstone of US defense. These questions are particularly troubling given the effectively irreplaceable position SpaceX has been granted by the Hegseth/Emil Michael Pentagon. $SPCX $TSLA Our full quantitative analysis below w/ @streetwiseprof
    01.3K01K
  9. Lynx✓@LibertyLynx
    SpaceX Blocked A U.S. And NATO Satellite to Assist a Russian Intercept After Crippling Ukraine's Air Defenses The Math Proves the Reality that Musk doesn't want you to see. On Oct 13-14, SpaceX restricted Starshield/Starlink during a 39-missile Russian attack, cutting Ukrainian drone intercepts by 23% and stranding U.S. personnel in Kyiv. Forty-eight hours later (Oct 15), SpaceX blocked U.S.-licensed NRO, Space Force, and NATO radar satellite ICEYE-X36 in orbit so Russia's COSMOS 2612 weapon could intercept it (99.89%-99.98% posterior) Our Model Demonstrates that the Russian intercept of the US/NATO ICEYE X-36 satellite (contemporaneous with the throttling of Starlink) would not have been possible, and almost certainly not been attempted, without SpaceX resources. At a material opportunity cost, Russia sprinted its COSMOS satellite to intercept ICEYE X36. Based on a previous attempt in June during which X36 maneuvered to evade COSMOS, Russia knew that this would be successful only if X36 could not maneuver. On October 15, SpaceX fixed X36 in place by issuing a collision alert for a sub-kilometer approach with its Starlink 35856 when SpaceX's own data shows that the actual distance was 4.8-5.0x as great. SpaceX issued no warning to COSMOS despite the fact that its sprint was far more threatening than the stable X36 orbit. SpaceX did not maneuver its Starlink 35856 satellite to clear the supposed collision risk. How, absent coordination with SpaceX, could Russia have known that SpaceX would take actions that (a) misrepresented the danger posed by X36, and (b) resulted in the fixing of X36 thereby enabling COSMOS's successful intercept? Thus, SpaceX was directly involved in simultaneously compromising Ukraine’s defensive and offensive capabilities. The conjunction of these two events makes innocent explanations untenable. The Pentagon Capture & Iran Round Two Trap: Pentagon CTO Emil Michael who cashed out $7M–$35M from Musk’s inner-circle SpaceX vehicles (M8/Gigafund 0.1 and M6/Valor M33 II) and KQ Partners / xAI (selling xAIfor $5M–$25M three days before taking over CDAO/OSCand 21 days before SpaceX bought xAI, while keeping M8, M6, M9, M10 & Nomadic open) and Pete Hegseth purged rival Anthropic in two hours, surrendered combat command over US drones used to attack Iran to Starlink’s "Terms of Service," and on October 2 named Musk Co-Director of Project Meridian to design the Pentagon's "Future of Warfighting" just as America enters Iran Round Twowith depleted Patriot/THAAD magazines and Russia feeding U.S. warship/aircraft locations to Tehran. SpaceX’s actions in Ukraine raise serious questions about its alignment with US security interests and its reliability as a cornerstone of US defense. These questions are particularly troubling given the effectively irreplaceable position SpaceX has been granted by the Hegseth/Emil Michael Pentagon. $SPCX $TSLA Our full quantitative analysis below w/ @streetwiseprof
    Download
    2893.1K8.2K710K
  10. Peter Todd✓@peterktodd
    Peter Todd
    RT @avidseries: Prominent accounts are already expressing outrage over RFK Jr.'s comments, but it's actually even broader than what he's saying: Muslims in general (and not just Arabs) have not distinguished themselves in science, at least in the modern age.
    Bulwark Clips @BulwarkClips
    RFK: "There's five hundred million Arabs in the world. And yet they don't produce science. They don't win the Novel Prize. They don't win the Fields Prize. They don't win the Wolf Prize. They don't produce literature."
    023601K
  11. Bulwark Clips✓@BulwarkClips
    RFK: "There's five hundred million Arabs in the world. And yet they don't produce science. They don't win the Novel Prize. They don't win the Fields Prize. They don't win the Wolf Prize. They don't produce literature."
    Download
    4.8K1.9K15.4K9M
  12. Peter Todd✓@peterktodd
    Peter Todd
    RT @MandelDuck: "Outtake" from the @btcplusplus video I didnt include in the original because the joke is probably too techy 😅
    Christian Moss @MandelDuck
    Bitcoin Seinfeld: Bitcoiners at the airport part 4 Anybody else got those post conference blues? (or conference fatigue?)
    090889
  13. Christian Moss✓@MandelDuck
    Bitcoin Seinfeld: Bitcoiners at the airport part 4 Anybody else got those post conference blues? (or conference fatigue?)
    Download
    2156495102K
  14. Peter Todd✓@peterktodd
    Peter Todd
    RT @msabouri: Sweden is officially ditching mRNA vaccines, and they are not hiding their reasons for doing so.
    02.8K0944
  15. Peter Todd✓@peterktodd
    Peter Todd
    RT @realjoshuareid: So in California. They give instructions on how ballots should be placed in the envelope. When you do that — the Democrat candidate aligns with a visible hole. Which means, when processing the ballots the person sorting them can tell if it is a Democrat Ballot or a ballot voting for someone else. That is significant. Now think about the time it takes to process California ballots. Who is it that in some areas (LA County Mayoral Election) you have a mass dump of 24k ballots all for one candidate and not another? How I imagine this works. A ballot facility takes all the ballots that have that mark filled out and separates them. Then they process them individually. The others ballots then are processed separately. An initial count of a batch should give a rough estimate of Democrats versus Republican votes and give a probability of who is leading out of that batch. This is before any ballots are actually counted. This is a great method to know who is leading in the ballots prior to processing the ballots, especially when this is a numbers game.
    01.6K0906
  16. Peter Todd✓@peterktodd
    Peter Todd
    RT @IterIntellectus: funny how they had to use a logarithmic scale to make it look like afghans, middle easterners, and africans rape less than they do this is how it would look like if linear
    Basil the Great @BasilTheGreat
    🚨BREAKING: New Data reveals that migrants from most of the world are committing sex crimes at a FAR HIGHER rate than British nationals [@TheEconomist ]
    02920965
  17. Basil the Great✓@BasilTheGreat
    🚨BREAKING: New Data reveals that migrants from most of the world are committing sex crimes at a FAR HIGHER rate than British nationals [@TheEconomist ]
    Download
    886622.5K98.2K
  18. Peter Todd✓@peterktodd
    > GPS L1 was designed in the 1970s with no cryptographic authentication. Common misconception. Public key cryptography can't help here. GPS is a unidirectional protocol based on measuring timing. It is inherently vulnerable to replay attacks. Crypto auth simply can't fix that.
    Zoe @zoecyber001
    In January 2016, the US Air Force decommissioned a single GPS satellite (SVN 23) and accidentally uploaded a 13.7-microsecond timing error into the broadcast navigation data. That 0.000013-second offset knocked BBC digital radio transmitters off the air for two days and broke police and fire dispatch networks across North America. Today, an attacker with a software-defined radio can force that exact timing failure on a target building from across the street. 1. Why critical infrastructure relies on a 1970s radio signal Cell towers, power substations, and stock exchanges all need their servers to tick in lockstep. Installing a commercial cesium atomic clock at every site costs roughly $65,000 per unit, so operators bolt a $200 GPS timing receiver to the roof instead. That rooftop antenna listens to atomic clocks aboard 31 GPS satellites orbiting 20,200 kilometers above the Earth. Civilian GPS L1 C/A was designed in the 1970s with no cryptographic authentication. Worse, by the time a satellite's radio signal travels 20,200 kilometers through space, it hits the Earth's surface at roughly -130 dBm (a tenth of a femtowatt). A 10-milliwatt transmitter plugged into a laptop in a parking lot is tens of millions of times stronger at the rooftop antenna than the real satellites in orbit. 2. Jam-and-spoof vs. synchronous time-walking If an attacker uses an open-source tool like gps-sdr-sim on a $300 SDR to broadcast a fake timestamp that is an hour off, a modern timing receiver spots the sudden jump and switches to its internal backup oscillator. To bypass that check, attackers use clock slewing, also known as time walking: * Hard takeover (gps-sdr-sim): A basic attacker generates a pre-computed baseband file that starts at the current UTC second, transmits strongly enough to force the rooftop receiver to lose lock on the real sky and re-acquire the louder fake signal, and then plays back a programmed clock drift. * Seamless carry-off (Synchronous spoofer): Against hardened receivers that alert on any signal drop, a more advanced spoofer uses a receiving antenna to track the live satellites in real time. It transmits a counterfeit signal matched to the exact code phase and Doppler shift of the real sky at the victim's antenna, ramps up its power by a few decibels to capture the receiver's Delay-Locked Loop (DLL), and pulls the timing pulse forward by 100 to 200 nanoseconds per second. Because the drift stays inside the receiver's tracking threshold, the local clock slides smoothly away from UTC without raising a loss-of-lock alarm. 3. What breaks when a clock drifts by microseconds Once a site's local clock drifts past a few microseconds, automated protection hardware starts shutting equipment down: * 5G TDD cell tower mute (±1.5 microseconds): Most mid-band 5G networks use Time Division Duplexing (TDD), where towers transmit and receive on the exact same frequency by alternating time slots every few milliseconds. The 3GPP specification requires neighboring towers to stay synchronized within ±1.5 microseconds (a 3-microsecond maximum window between adjacent base stations). If a spoofed tower drifts past 1.5 microseconds, its 100-watt downlink burst transmits directly into the neighboring tower's uplink listening window, deafening the cell. To prevent cross-link interference, the baseband's synchronization watchdog automatically mutes the radio transmitter and drops every phone on the tower. * 500 kV substation breaker trips (100 microseconds): High-voltage transmission lines use Line Current Differential Relays (ANSI 87L) at both ends of a wire to compare AC phase angles using GPS timestamps, while Phasor Measurement Units (PMUs) track grid stability across cities. Under IEEE C37.118, just 26.5 microseconds of timing error creates a 1% Total Vector Error on a 60 Hz line (31.8 microseconds on a 50 Hz grid). If an attacker walks one substation's GPS clock off by 100 to 200 microseconds, the differential relay sees a massive phantom phase shift between the two ends of the transmission line, assumes the cable has suffered a short circuit, and trips the main 500 kV breakers on a healthy power line. * High-frequency trading halts (100 microseconds): Under European MiFID II RTS 25 rules, automated trading engines must timestamp every order within 100 microseconds of UTC. When the exchange's time-sync daemon detects that its GPS discipline has breached that 100-microsecond ceiling, compliance middleware halts order execution. 4. How infrastructure operators defend the clock Upgrading an orbiting satellite constellation takes decades, so engineers harden the ground equipment across four layers: * Galileo OSNMA and Chimera: Europe's Galileo constellation now broadcasts OSNMA (Open Service Navigation Message Authentication), which cryptographically signs the navigation data bits so a tool like gps-sdr-sim cannot forge satellite messages. Because an attacker can still record and delay genuine signed signals (a meaconing relay attack), newer systems pair data signatures with encrypted spreading-code markers like Galileo CAS and GPS Chimera. * Multi-constellation and multi-band receivers: Timing receivers track GPS, Galileo, BeiDou, and GLONASS across both L1 and L5 bands simultaneously. Spoofing four constellations across multiple frequencies at once requires vastly more complex RF hardware. * Anti-spoofing CRPA antennas: Critical sites use Controlled Reception Pattern Antennas (multi-element phased arrays) or choke-ring antennas that only accept signals arriving from high up in the sky and null out radio signals coming horizontally from a parking lot. * PTP over fiber and rubidium holdover: Telecom and grid operators back up rooftop antennas with Precision Time Protocol (IEEE 1588v2) distributed over fiber-optic lines, paired with local Oven-Controlled Crystal Oscillators (OCXOs) or miniature rubidium atomic clocks. If the rooftop antenna drifts faster than the internal rubidium physics package allows, the timing card disconnects the GPS input and free-runs within 1 microsecond for up to 72 hours.
    81144.5K
  19. Zoe✓@zoecyber001
    In January 2016, the US Air Force decommissioned a single GPS satellite (SVN 23) and accidentally uploaded a 13.7-microsecond timing error into the broadcast navigation data. That 0.000013-second offset knocked BBC digital radio transmitters off the air for two days and broke police and fire dispatch networks across North America. Today, an attacker with a software-defined radio can force that exact timing failure on a target building from across the street. 1. Why critical infrastructure relies on a 1970s radio signal Cell towers, power substations, and stock exchanges all need their servers to tick in lockstep. Installing a commercial cesium atomic clock at every site costs roughly $65,000 per unit, so operators bolt a $200 GPS timing receiver to the roof instead. That rooftop antenna listens to atomic clocks aboard 31 GPS satellites orbiting 20,200 kilometers above the Earth. Civilian GPS L1 C/A was designed in the 1970s with no cryptographic authentication. Worse, by the time a satellite's radio signal travels 20,200 kilometers through space, it hits the Earth's surface at roughly -130 dBm (a tenth of a femtowatt). A 10-milliwatt transmitter plugged into a laptop in a parking lot is tens of millions of times stronger at the rooftop antenna than the real satellites in orbit. 2. Jam-and-spoof vs. synchronous time-walking If an attacker uses an open-source tool like gps-sdr-sim on a $300 SDR to broadcast a fake timestamp that is an hour off, a modern timing receiver spots the sudden jump and switches to its internal backup oscillator. To bypass that check, attackers use clock slewing, also known as time walking: * Hard takeover (gps-sdr-sim): A basic attacker generates a pre-computed baseband file that starts at the current UTC second, transmits strongly enough to force the rooftop receiver to lose lock on the real sky and re-acquire the louder fake signal, and then plays back a programmed clock drift. * Seamless carry-off (Synchronous spoofer): Against hardened receivers that alert on any signal drop, a more advanced spoofer uses a receiving antenna to track the live satellites in real time. It transmits a counterfeit signal matched to the exact code phase and Doppler shift of the real sky at the victim's antenna, ramps up its power by a few decibels to capture the receiver's Delay-Locked Loop (DLL), and pulls the timing pulse forward by 100 to 200 nanoseconds per second. Because the drift stays inside the receiver's tracking threshold, the local clock slides smoothly away from UTC without raising a loss-of-lock alarm. 3. What breaks when a clock drifts by microseconds Once a site's local clock drifts past a few microseconds, automated protection hardware starts shutting equipment down: * 5G TDD cell tower mute (±1.5 microseconds): Most mid-band 5G networks use Time Division Duplexing (TDD), where towers transmit and receive on the exact same frequency by alternating time slots every few milliseconds. The 3GPP specification requires neighboring towers to stay synchronized within ±1.5 microseconds (a 3-microsecond maximum window between adjacent base stations). If a spoofed tower drifts past 1.5 microseconds, its 100-watt downlink burst transmits directly into the neighboring tower's uplink listening window, deafening the cell. To prevent cross-link interference, the baseband's synchronization watchdog automatically mutes the radio transmitter and drops every phone on the tower. * 500 kV substation breaker trips (100 microseconds): High-voltage transmission lines use Line Current Differential Relays (ANSI 87L) at both ends of a wire to compare AC phase angles using GPS timestamps, while Phasor Measurement Units (PMUs) track grid stability across cities. Under IEEE C37.118, just 26.5 microseconds of timing error creates a 1% Total Vector Error on a 60 Hz line (31.8 microseconds on a 50 Hz grid). If an attacker walks one substation's GPS clock off by 100 to 200 microseconds, the differential relay sees a massive phantom phase shift between the two ends of the transmission line, assumes the cable has suffered a short circuit, and trips the main 500 kV breakers on a healthy power line. * High-frequency trading halts (100 microseconds): Under European MiFID II RTS 25 rules, automated trading engines must timestamp every order within 100 microseconds of UTC. When the exchange's time-sync daemon detects that its GPS discipline has breached that 100-microsecond ceiling, compliance middleware halts order execution. 4. How infrastructure operators defend the clock Upgrading an orbiting satellite constellation takes decades, so engineers harden the ground equipment across four layers: * Galileo OSNMA and Chimera: Europe's Galileo constellation now broadcasts OSNMA (Open Service Navigation Message Authentication), which cryptographically signs the navigation data bits so a tool like gps-sdr-sim cannot forge satellite messages. Because an attacker can still record and delay genuine signed signals (a meaconing relay attack), newer systems pair data signatures with encrypted spreading-code markers like Galileo CAS and GPS Chimera. * Multi-constellation and multi-band receivers: Timing receivers track GPS, Galileo, BeiDou, and GLONASS across both L1 and L5 bands simultaneously. Spoofing four constellations across multiple frequencies at once requires vastly more complex RF hardware. * Anti-spoofing CRPA antennas: Critical sites use Controlled Reception Pattern Antennas (multi-element phased arrays) or choke-ring antennas that only accept signals arriving from high up in the sky and null out radio signals coming horizontally from a parking lot. * PTP over fiber and rubidium holdover: Telecom and grid operators back up rooftop antennas with Precision Time Protocol (IEEE 1588v2) distributed over fiber-optic lines, paired with local Oven-Controlled Crystal Oscillators (OCXOs) or miniature rubidium atomic clocks. If the rooftop antenna drifts faster than the internal rubidium physics package allows, the timing card disconnects the GPS input and free-runs within 1 microsecond for up to 72 hours.
    Download
    189158745.7K
  20. Peter Todd✓@peterktodd
    Posts @peterktodd
    Bidirectional, timestamping-based, time synchronization protocols like Roughtime (and even @opentimestamps in principal) _can_ do cryptographically secured trusted time synchronization: But their accuracy is absolutely shit compared to GPS, because if you actually have no trusted signal path assumptions the best you can do is the difference between actual latency and minimum possible latency (eg speed of light). Roughtime aims to achieve time sync within about a second; GPS, when working properly, can easily achieve nanoseconds on relatively cheap hardware. Literally a billion times better. Realistically the only way to improve this situation is invest in better clocks, to run longer between trusted time sync opportunities. Fortunately, atomic clocks are _way_ more affordable and compact than they used to be. You can even get chip scale atomic clocks in packages with sizes like 41 × 35 × 12 mm.
    304930
  21. Peter Todd✓@peterktodd
    Peter Todd
    RT @DrewPavlou: Moroccan men in Spain care so deeply about the French education system that they are willing to vandalise bike shares in Barcelona. Really inspiring that they care so deeply about education. Respect!
    Lee Kuan Yimby @LeeKuanYimby
    Destroying the bike share should do it.
    018601.1K
  22. Peter Todd✓@peterktodd
    What he says at the end of the video: “Don't cry for money. Don't say thank you.” When I do military donations in Ukraine, the soldiers I'm getting stuff for always seem to find an excuse to buy me something. A coffee, a juice, a small meal. Something to make us equal partners.
    Seinfeld’s Puffy Shirt 🇨🇦 🇺🇸 @JoniWagner
    Kitchener, Ontario: An Indian man records himself at St. Mary’s Church ‘pay what you can’ meal program, gleefully explaining to his followers how to get free food in Canada. His smug, celebratory arrogance is reprehensible. These places exist because actual struggling Canadians and churches are willing to help those in need. Instead, they’re being treated like a buffet by people who can clearly afford shoes and a phone. Generosity is not an invitation to be looted & our high trust society is collapsing right in front of our eyes. Wake up Canada. (I added subtitles to the video for clarity. It’s a bit clunky, but you get the point.)
    42175.3K
  23. Seinfeld’s Puffy Shirt 🇨🇦 🇺🇸✓@JoniWagner
    Kitchener, Ontario: An Indian man records himself at St. Mary’s Church ‘pay what you can’ meal program, gleefully explaining to his followers how to get free food in Canada. His smug, celebratory arrogance is reprehensible. These places exist because actual struggling Canadians and churches are willing to help those in need. Instead, they’re being treated like a buffet by people who can clearly afford shoes and a phone. Generosity is not an invitation to be looted & our high trust society is collapsing right in front of our eyes. Wake up Canada. (I added subtitles to the video for clarity. It’s a bit clunky, but you get the point.)
    Download
    144816618.9K
  24. Peter Todd✓@peterktodd
    Peter Todd
    RT @charlesgillespi: Never seen a more flagrant and violent breach of privacy in my life, and probably never will. Doubtful that a privacy violation will ever even be able to compare to the scale of this evil and deliberate attack. Samsung should be eviscerated for this. Criminal charges please
    log4j @log4j
    turns out it classifies what audio it hears, before reporting back to samsung. sensor preferences, dog-barking and baby-crying event counters, and camera streaming duration are built into telemetry paths.
    01.1K01.1K
  25. log4j✓@log4j
    turns out it classifies what audio it hears, before reporting back to samsung. sensor preferences, dog-barking and baby-crying event counters, and camera streaming duration are built into telemetry paths.
    Download
    2411.9K16.1K1.6M
  26. Peter Todd✓@peterktodd
    Peter Todd
    RT @Tatarigami_UA: Elon Musk lies again. Civilian Starlink was already speed-limited, and every terminal had to be whitelisted. Yet Starshield was throttled too, which can’t be explained by alleged ToS violations. His explanations keep contradicting each other, making his claims even less credible
    098001.1K
  27. Peter Todd✓@peterktodd
    Peter Todd
    RT @NicolasDorier: I've been spammed with password reset demand from my Microsoft account. At a rate of 2 per days. Not phishing, just pure brute force. Password resets needs 6 digits they send by email. So it doesn't seem likely to find anything. But a malicious actor which try every day, with a dump of millions of leaked account he found somewhere? Well he will crack a few of those with brute force every day... Use 2FA.
    02901K
  28. Peter Todd✓@peterktodd
    Peter Todd
    RT @JMF1958: The whole idea that shooting a retreating attacker is morally wrong seems predicated on the idea that said attacker is somehow running on *one-way feet*, and wouldn’t THINK of firing at you from cover once he reaches said cover.
    memetic_sisyphus @memeticsisyphus
    May every burglar who breaks into peoples home meet the same fate
    020801.2K
  29. memetic_sisyphus✓@memeticsisyphus
    May every burglar who breaks into peoples home meet the same fate
    Download
    23351.8K48.8K
  30. Peter Todd✓@peterktodd
    Peter Todd
    RT @ginamilan_: If someone from Somalia with a fake identity can serve in the United States Congress for years without getting caught, imagine still believing that illegals aren’t voting in U.S. elections.
    08K01.2K
  31. Peter Todd✓@peterktodd
    Peter Todd
    RT @Excellion: A test transaction for 2.5 BTC was sent to the @Liquid_BTC Federation wallet, reducing the shortfall to 600 BTC. The remaining 600 BTC will be moved to the wallet in the coming days. All network operations are continuing normally.
    0460753
  32. Show more posts