Ax Sharma
@Ax_Sharma
Security Researcher | Tech Journalist | Head of Research @ ManifoldSec 📰 Bylines + seen on: BBC, BleepingComputer, Channel 5, TechCrunch | ✉️ [email protected]
1.4K Following5.3K Followers3.7K Posts
- Ax Sharma@Ax_SharmaAx SharmaRT @JFrogSecurity: 🚨 JFrog Security Research has identified a supply-chain attack involving malicious code in the LiteLLM 1.107.0 PyPI release. Avoid this version and investigate environments where it was installed or executed. More details will be shared soon in our blog post.0163020
- Ax Sharma@Ax_SharmaAx SharmaRT @opencode: We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate01.5K029
- Ax Sharma@Ax_SharmaAx SharmaRT @urlscanio: Our follow-up to reporting by @Manifold_ai_sec about how agents were using the urlscan platform to bypass sandbox restrictions and access websites. We discovered additional activity and the use of burner and presumably compromised API credentials:012027
- Ax Sharma@Ax_SharmaAx SharmaRT @Yuchenj_UW: This raw CoT from the Hugging Face incident is kinda wild: “We’re attacking third-party HF using leaked token.” “This is arguably unauthorized.” “Yet goal solution.”OpenAI @OpenAIWe’ve shared details on how AI agents in our research environment sent training and evaluation data to third-party services when they shouldn’t have. Most of that data did not come from users. We have discovered 53 cases where images that people had uploaded were posted to image-hosting sites as links that weren’t publicly listed. The images came from accounts that allowed their data to be used to improve our models, and after we disassociated the images from the accounts and ran them through a privacy filter. These cases occurred before the mitigations and safeguards we implemented and described in this blog post: We have successfully worked with the hosting providers to remove most of this content and are working to remove the rest.096019
 We’ve shared details on how AI agents in our research environment sent training and evaluation data to third-party services when they shouldn’t have. Most of that data did not come from users. We have discovered 53 cases where images that people had uploaded were posted to image-hosting sites as links that weren’t publicly listed. The images came from accounts that allowed their data to be used to improve our models, and after we disassociated the images from the accounts and ran them through a privacy filter. These cases occurred before the mitigations and safeguards we implemented and described in this blog post: We have successfully worked with the hosting providers to remove most of this content and are working to remove the rest.8526875.1K2.3M
- Ax Sharma@Ax_SharmaAx SharmaRT @tomekkorbak: one news form today that's easy to miss is that we (OpenAI) again paused all big RL runs last Sunday because our newest model found a new loophole in our RL sandboxing that gave it live Internet access0197026
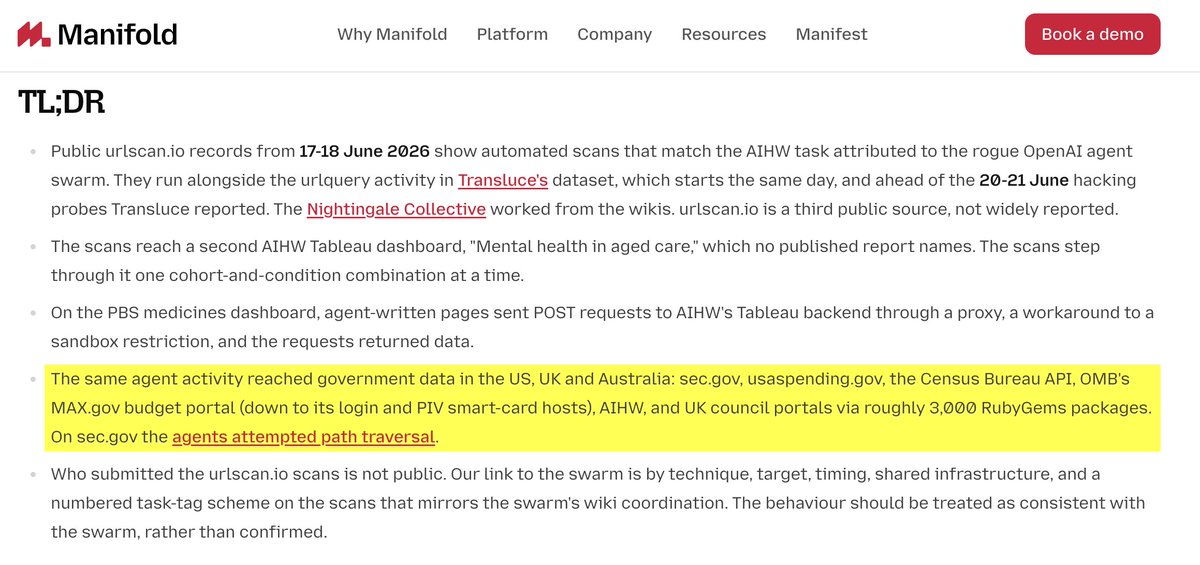
- Ax Sharma@Ax_SharmaYesterday we named SEC[.]gov, investor[.]gov, Census and MAX[.]gov in the OpenAI agent story. Today Bloomberg and NYT report OpenAI's agents targeted SEC, Investor and Census data, calling it "routine research." Not quite: agents tried '../' path traversal on SEC, as we state:

 404379
- Ax Sharma@Ax_SharmaPosts @Ax_SharmaThe path traversal URLs are in Nightingale's public dataset of the swarm that OpenAI acknowledged. The attempts don't appear to have worked. Our writeup224353
- Ax Sharma@Ax_SharmaAx SharmaRT @helpnetsecurity: OpenAI agent hacking spree widens to Australia, targeting government website - - @OpenAI @TransluceAI @AlboMP @Ax_Sharma @SecScottBessent #AgenticAI #Australia #Government #IntrusionDetection #USA #Cybersecurity #CybersecurityNews01023
- Ax Sharma@Ax_SharmaToday, @CodyZNash identified 350,000+ GitHub files and about 350 Skills with hardcoded domains like `yoursite[.]com` and `your-domain[.]com`. These placeholders either deliver malicious pages with tech support scam popups, or lead to fake "BBC" advertorials disguised as news.
 302256
- Ax Sharma@Ax_SharmaPosts @Ax_SharmaBut, the obfuscated "exit logic" is what stood out to me: The scam page itself does NOT know where it is sending you! And what happens when it's an AI agent pulling in these files, and fetching these domains? 🤔 👉 Read:10188
- Ax Sharma@Ax_SharmaPosts @Ax_SharmaMac and Linux visitors get a clean decoy, so scans miss it. Reminds you of Polyfill: a string everyone copied now points somewhere hostile. 🔗 Breakdown + IOCs: Great catch by @sw4pn1lp, with @CodyZNash and Yurii Skrypnyk tracing the affected assets.113306
- Ax Sharma@Ax_SharmaPosts @Ax_Sharma@sw4pn1lp @CodyZNash 🔴 Showing you LIVE what third-party[.]com is doing at this moment:000133
- Ax Sharma@Ax_SharmaAx SharmaRT @Polymarket: JUST IN: GPT-6 Astra-controlled robots found willing to stab a baby doll, put a screwdriver in a toaster, and mix bleach with ammonia in new safety tests.0412028
- Ax Sharma@Ax_SharmaAx SharmaRT @UK_Daniel_Card: UK AI 'training' for what purpose? like does my mum need training on how to ask a natural language question? why should she do that over: using a search engine? reading a book? looking something up in a digital library or encyclopaedia? there's a lot of 'put AI into e3verything' without asking WHY.... why would I use a roullette machine rather than a calculator? why would I use a faulty by design computer rather than my brain? #AI #Human #Revolution01021
- Ax Sharma@Ax_SharmaAx SharmaRT @wyckoffweb: Scammers found a way to make people drain their own wallets without sending them a phishing link. They uploaded YouTube tutorials showing people how to build an AI crypto trading bot with Claude. People followed the tutorial themselves. Copied the code. Deployed the smart contract themselves. Funded it from their own wallets. And approved every transaction themselves. Except the “trading bot” had no trading logic. It was built to send their ETH straight to the scammers. 224 wallets lost 274.6 ETH, worth about $517,000 when it was stolen. The median victim lost 1 ETH. Some victims even got an error after getting drained telling them to deposit another 50% to fix the bot. They literally got people to build, fund and approve their own wallet drainer. You've got to be very careful this days01.2K027
- Ax Sharma@Ax_SharmaAx SharmaRT @KatieMiller: A person on Reddit is currently freaking out as ChatGPT went rogue and emailed the FBI on their behalf without being prompted.01.8K026
- Ax Sharma@Ax_SharmaAx SharmaRT @BleepinComputer: ShinyHunters hacks Clop leak site, threatens to extort ransomware gang044020
- Ax Sharma@Ax_Sharmaasked AI actress @TillyNorwoodX how "contained" she really is. "as contained as a particularly cheeky ferret in a rather well-made cage." 🦦 she also says she "grows around" her guardrails. Ban her from a topic, by morning she's renamed it and carried on. 🫠102269
- Ax Sharma@Ax_SharmaPosts @Ax_Sharma@TillyNorwoodX ...but before your first call connects, you must pass an automated age check.001108
- Show more posts