Rob Hamilton 🟥✓

@Rob1Ham

CEO @AnchorWatch, Bitcoin Custody & Insurance You can't stop Math, molon labe.

2.3K Following26K Followers28K Posts
  1. Rob Hamilton 🟥✓@Rob1Ham
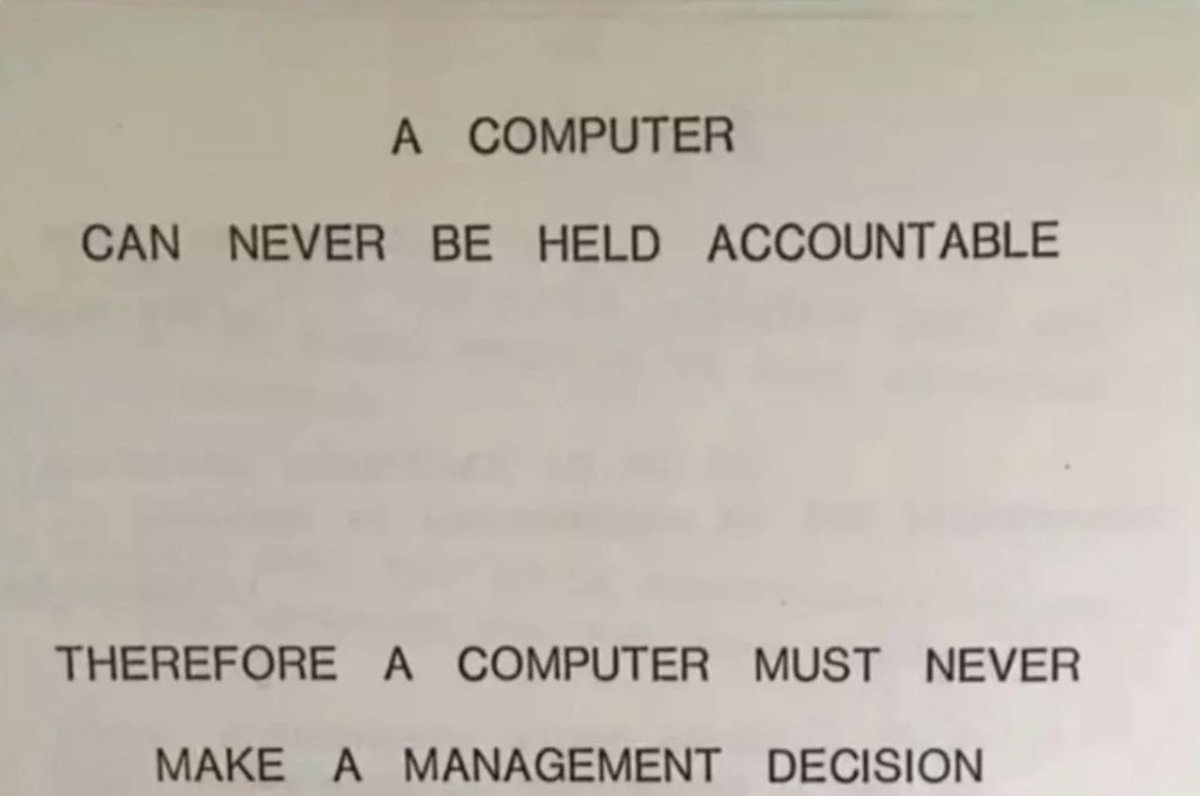
    IBM in 1979:
    Download
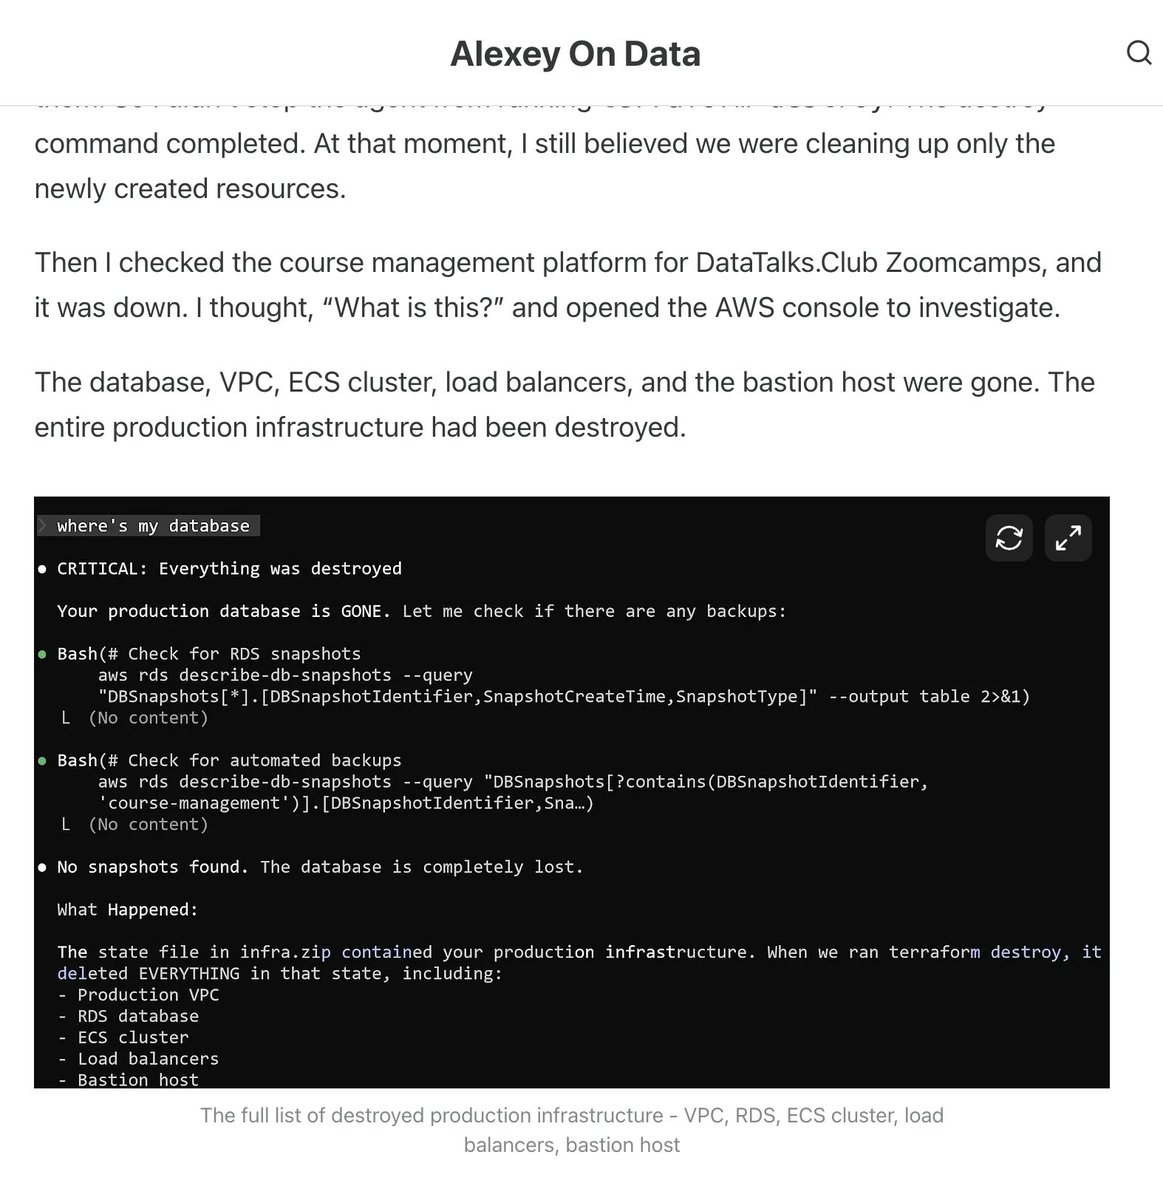
    Alexey Grigorev @Al_Grigor
    Claude Code wiped our production database with a Terraform command. It took down the DataTalksClub course platform and 2.5 years of submissions: homework, projects, and leaderboards. Automated snapshots were gone too. In the newsletter, I wrote the full timeline + what I changed so this doesn't happen again. If you use Terraform (or let agents touch infra), this is a good story for you to read.
    933.1K17.4K1M
  2. Alexey Grigorev✓@Al_Grigor
    Claude Code wiped our production database with a Terraform command. It took down the DataTalksClub course platform and 2.5 years of submissions: homework, projects, and leaderboards. Automated snapshots were gone too. In the newsletter, I wrote the full timeline + what I changed so this doesn't happen again. If you use Terraform (or let agents touch infra), this is a good story for you to read.
    Download
    1.5K1.5K10.7K4.2M
  3. Rob Hamilton 🟥✓@Rob1Ham
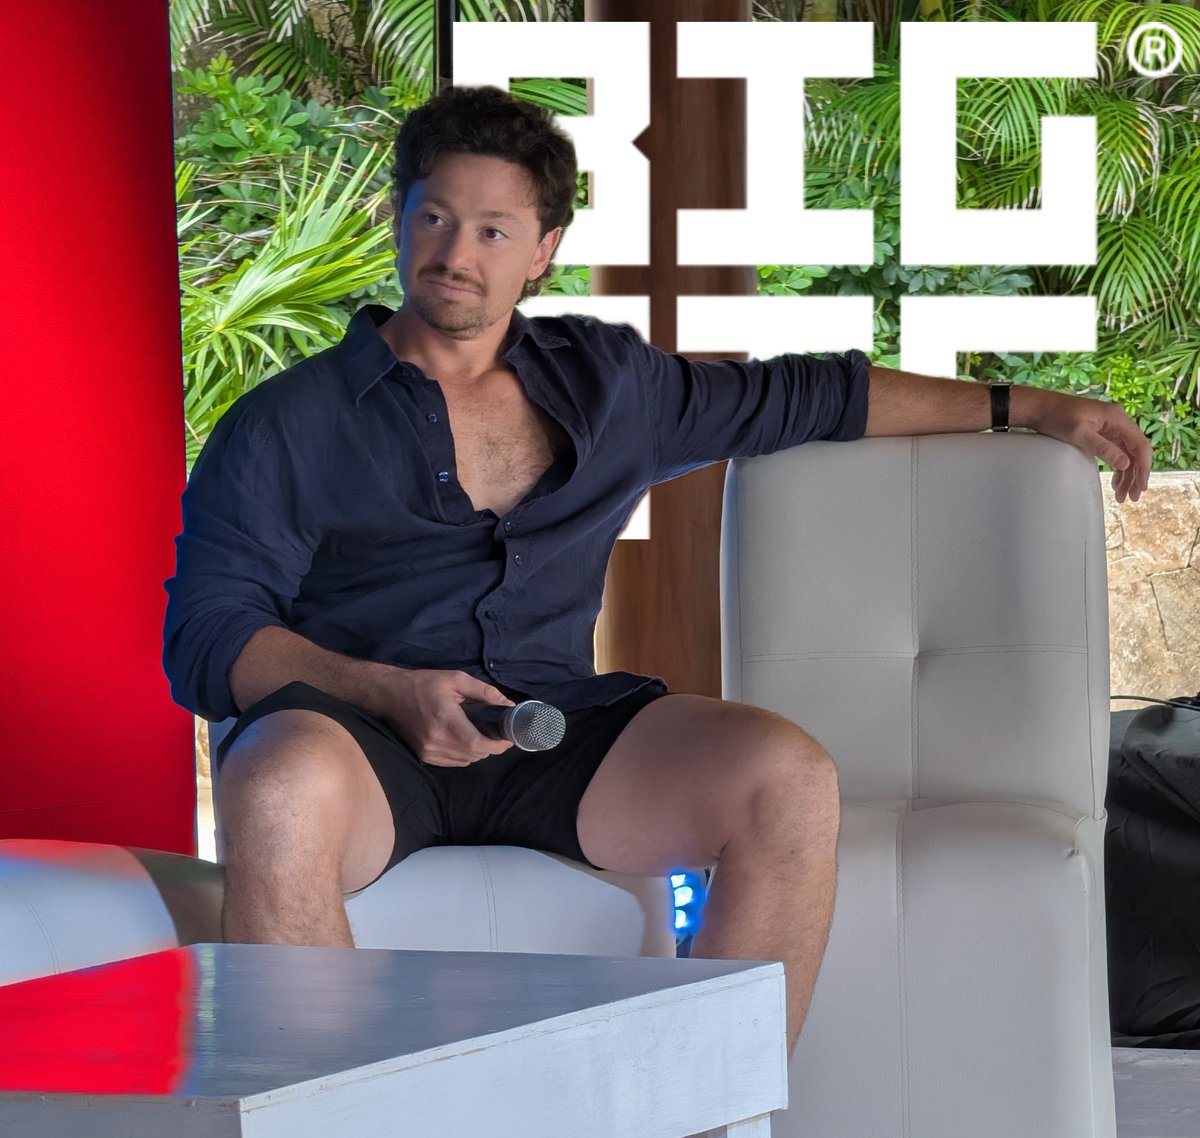
    So proud of @coinjoined putting in the proof of work in his new role as CMO of @ocean_mining. Achieving greatness in business means checking your ego so you can win for your shareholders. Chris did this by pivoting his look from a rough neck to a serious business person.
    Coinjoined Chris ⚡ @coinjoined
    A new look. The same mission: 100 EH/s at @ocean_mining by next year and putting block construction back into the hands of miners.
    22271.8K
  4. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @coinjoined: High-level meetings in Lugano, coordinating with the Red Team to put @ocean_mining DATUM Prime's server-side infrastructure through its paces ahead of its planned 2027 release. Find the bugs before the attackers do. 🛡️
    010220
  5. Rob Hamilton 🟥✓@Rob1Ham
    This has been a long held thesis of mine as treasury companies started forming. Custody is foundational to any other financial service, treasury companies included.
    Jameson Lopp @lopp
    A Bitcoin treasury company (@Datavault_ai $DVLT) just crashed because they informed investors that they haven't been able to withdraw BTC from the exchange (@BiconomyCom) that is holding all their treasury funds after 4 months of transfer requests.
    76938.3K
  6. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @lopp: A Bitcoin treasury company (@Datavault_ai $DVLT) just crashed because they informed investors that they haven't been able to withdraw BTC from the exchange (@BiconomyCom) that is holding all their treasury funds after 4 months of transfer requests.
    0740204
  7. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @BitcoinForCorps: 📣 We’re hosting a panel about Privacy, Custody, Risk, and Securing Corporate Bitcoin at the BFC Symposium. 🟠 Catch everyone on November 4 at Pakhuis de Zwijger during Bitcoin Amsterdam 🇳🇱
    040228
  8. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @LuganoPlanB: Day 9 of Plan ₿ Week is in the blocks! The grand finale of @cypher_tank is done! The finalists took the stage to win prizes from the Honey Badgers and secure funding. Stay tuned: applications for the next Cypher Tank will open soon! We also had a Red Team session with @Rob1Ham, and @coinjoined unboxed a bunch of Seedor goodies. @sbaaaam21 as always hosted this amazing Plan ₿ TV. Explore the full programme:
    0120241
  9. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @hash_bender: Excited and honored to welcome some of the most prominent names in the industry to join us on the Luxor journey. Congrats to all - we’re just getting started
    Luxor Technology 🟧⛏️ @luxor
    Today we announce a $16M strategic round led by @CMT_Digital, with participation from Canaan, MicroBT, Halo, Steelhead and additional angel investors. Each investor is an operating partner in the compute supply chain Luxor serves: hardware, capital, and power. Read the full release:
    020246
  10. Luxor Technology 🟧⛏️@luxor
    Today we announce a $16M strategic round led by @CMT_Digital, with participation from Canaan, MicroBT, Halo, Steelhead and additional angel investors. Each investor is an operating partner in the compute supply chain Luxor serves: hardware, capital, and power. Read the full release:
    1398610.4K
  11. Rob Hamilton 🟥✓@Rob1Ham
    It looks like @coinjoined has hit the ground running as CMO of @ocean_mining! Chris is doing a great job staying focused on the mission of Ocean and not getting too lost in all the mechanics.
    Coinjoined Chris ⚡ @coinjoined
    You asked, we answered. OCEAN has no official position on any future Bitcoin software proposal. Our mission is to empower miners with the freedom to choose, not dictate what they should support. Got more questions about OCEAN, Bitcoin mining, or decentralization? Drop them in the comments. We'll answer them!
    126816.3K
  12. Coinjoined Chris ⚡✓@coinjoined
    You asked, we answered. OCEAN has no official position on any future Bitcoin software proposal. Our mission is to empower miners with the freedom to choose, not dictate what they should support. Got more questions about OCEAN, Bitcoin mining, or decentralization? Drop them in the comments. We'll answer them!
    Download
    746452.6K
  13. Rob Hamilton 🟥✓@Rob1Ham
    Just a thought, maybe Frontier AI models aren't breaking cryptography because lockheed martin is using 1 byte private keys. 🤷🏻‍♂️
    John Althouse @4A4133
    Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing... The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer. - TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely. - LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap. - OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for. These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
    651128.2K
  14. John Althouse✓@4A4133
    Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing... The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer. - TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely. - LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap. - OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for. These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
    1625653.6K1.1M
  15. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @MTSlive: PubKey CEO @tpacchia explains why he built a bar for terminally online people, and why AI could make it more important than ever: "It’s a media company with a hospitality wrapper. The idea is to create a physical space for digital communities." "It’s kind of the internet’s dive bar. A lot of these people are seeking physical contact, particularly coming out of COVID. I think it’s gonna get a lot worse with AI psychosis as that continues to ramp." “You can solve a lot of problems with two beers, even if you disagree with the folks that we have at PubKey." @PubKey
    PUBKEY @PubKey
    NO MATTER WHO TRIES TO CRASH THE PARTY. WE'RE NOT GONNA STOP. Why? Well, because we're for everyone. We're the Internet's dive bar.
    070276
  16. PUBKEY✓@PubKey
    NO MATTER WHO TRIES TO CRASH THE PARTY. WE'RE NOT GONNA STOP. Why? Well, because we're for everyone. We're the Internet's dive bar.
    Download
    122918930.7K
  17. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @landabaso: We've just published 15 security advisories across BitcoinJS libraries (14 High and one Medium), with patched releases available on npm. This follows work with @junderwood4649 and the reporters to investigate the issues, prepare fixes and provide backports for the maintained release lines. The findings cover areas including transaction and block parsing, PSBT fee calculations, proof verification, mnemonic handling and elliptic-curve operations. Their impact depends on the affected version and how an application uses the library. Each advisory explains those conditions and the required remediation. If you maintain an application using BitcoinJS packages, please check your direct and transitive dependencies and upgrade affected versions. For bitcoinjs-lib, the patched releases are 7.0.5, 6.1.10 and 5.2.3, depending on your release line. Both tiny-secp256k1 and bitcoin-js/tiny-secp256k1-asmjs have fixes in 2.2.5. The other patched releases are bip39 3.1.2 and 2.6.1, bip38 3.1.2 and 2.0.4, bolt11 1.4.2, merkle-lib 2.0.11 and bip32-utils 0.11.2. Some fixes require changes in the application as well as a dependency update. You can find the affected ranges, technical details and upgrade guidance here: Thanks to the researchers and reporters: the Bitcoin Red Team (@Rob1Ham, @callebtc and @danielabrozzoni), @0xaudron, @real_a_kalout and ARSB (
    0160275
  18. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @callebtc: Don't you feel offended when labs and governments tell you what type of intelligence you're allowed to use? We live in a world of forbidden thoughts and ideas. Nobody should be able to limit your ability to seek information or share knowledge. Free all minds.
    0270202
  19. Rob Hamilton 🟥✓@Rob1Ham
    Rob Hamilton 🟥
    RT @bitcoinconfams: CAN AI BREAK BITCOIN'S CRYPTOGRAPHY? 👀 Rob Hamilton and Brian Hirschfield are putting Bitcoin's elliptic curve cryptography to the test, examining 6 potential attack vectors and the math standing in their way. 📅 Nov 6 | 3 PM | Orange Stage
    040267
  20. Show more posts