Posts con #HTTP2Shell

#HTTP2Shell

Posts públicos de X que usan #HTTP2Shell.

Hashtags relacionados

  1. Aikido✓@AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    Descargar
    1188533.4K814K
  2. Daniel Púa✓@devploit
    PHP2Shell update 🚀 13 → 56 perfiles. 5 → 30 con RCE. Gracias a las aportaciones de la comunidad por ampliar la colección. Nuevos: stage-3 vessel 8.5.0–8.5.10, Debian 13/apxs2 y nginx+PHP-FPM.
    45534317.6K
  3. CISA Cyber@CISACyber
    Update to #PHP2Shell Alert: SIGMA rule helps identify potentially suspicious activity & incorporated partner resources. If your org can't update immediately or uses unsupported PHP 8.1 or earlier versions, take affected PHP-based systems offline until patched or updated.
    CISA Cyber @CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    2116661371.7K
  4. CISA Cyber@CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    Descargar
    627352.3K297K
  5. 国家サイバー統括室(注意・警戒情報)@cyber_forecast
    【注意喚起】 2026年10月30日、PHPの複数の脆弱性(CVE-2026-109618、CVE-2026-109619)に関するJPCET/CCの注意喚起の件に関連して、オランダの国家サイバーセキュリティセンター(NCSC-NL)が本脆弱性の影響を受ける可能性がある製品一覧や対策情報などをまとめたリポジトリーを公開しています。
    194772.3K931K
  6. .@elkentaro
    React2Shell WP2Shell PHP2Shell Node2Shell Python2Shell HTTP2Shell Broccoli2Shell Log4Shell Spring4Shell Text4Shell Act4Shell #alldashells
    333733317.3K
  7. Zero Cost Marketing✓@ZeroCostProfit
    PHP2Shell is being exploited right now. A hacked server can push malicious scripts to every visitor. Including you. So I built a free Chrome extension: → Badge on every site you open → Red = unpatched PHP → Can block scripts there Free. No signup. Link below.
    Descargar
    404206
  8. Cybersecurity and Infrastructure Security Agency@CISAgov
    Update to #PHP2Shell Alert: SIGMA rule helps identify potentially suspicious activity & incorporated partner resources. If your org can't update immediately or uses unsupported PHP 8.1 or earlier versions, take affected PHP-based systems offline until patched or updated.
    CISA Cyber @CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    177226024.9K
  9. Praetorian✓@praetorianlabs
    php2shell is exploitable, the easy path needs display_errors=On. We found zero live customer hosts with it. Under default config, the leak takes heap control down to the freelist. Blog: Demo: #OffensiveSecurity #PraetorianGuard
    Descargar
    014353.5K
  10. Rapid7@rapid7
    Your team needs to make decisions about PHP2Shell. Conflicting advice makes that harder. On October 30, Rapid7’s Douglas McKee and Rik Ferguson take the stage for 'PHP2Shell Mythbusters'. Save your spot here:
    Descargar
    0141.6K
  11. Qualys@qualys
    Can't patch PHP2Shell yet? Here's how to build a stopgap with the controls you own. PHP2Shell comes with a clear instruction: update PHP. But patching at this scale still takes time. In Qualys telemetry, only 199,000 of the 156 million PHP package installations with a known version (about 0.13%) had been patched in the first 12 hours after disclosure. Here is how to bridge the gap between disclosure and patch, in four steps: 1. Find and Prioritize Exposed PHP 2. Apply the Qualys Mitigation 3. Add Layers from the Security Stack you already run 4. Patch, Restart, and Re-Validate Learn more and don't forget to access our free PHP2Shell service to help product your environment against this threat: #PHP2Shell
    Descargar
    238951
  12. LiveOverflow 🔴 hextree.io✓@LiveOverflow
    I took a closer look at the CTF, which aims to demonstrate that PHP2SHELL is not realistically exploitable. So I gave it a try. Note: My analysis could be wrong, and I'm more than happy to be proven otherwise. Here’s what I found: • The server responds with Server: nginx and X-Powered-By: PHP/8.4.26. • My differential fingerprinting scanner independently confirmed at least PHP 8.2+ • Hypotheses: I considered two possible setups: ◦ nginx → PHP-FPM ◦ nginx → Apache → PHP-FPM/mod_php • After comparing the server's behavior against local test environments, the closest match appears to be nginx → PHP cli-server. Plot twist: the response behavior is consistent with the PHP cli-server serving a static index.html rather than an index.php. If that's indeed the case, the challenge appears to be intentionally made unexploitable. My conclusion (for now) is that I'm questioning whether this is a good-faith challenge. Happy to be corrected if I've missed something!
    Descargar
    89982.2K574K
  13. Threatactix Research✓@ThreatactixLab
    🚨 Threat advisory: we’ve tracked [4] active PHP2Shell C2 servers over the last [48 hours]. They’re tied to [CVE-2026-109618, CVE-2026-109619] and target internet-facing PHP apps for unauthenticated RCE. #PHP2Shell #ThreatIntel
    Descargar
    277486
  14. Microsoft Security Response Center✓@msftsecresponse
    PHP2Shell, a Brotli decoder vulnerability, and the eMudhra certificate authority key issue each require attention. Microsoft is updating the services it operates and releasing fixes for affected products. Customers should review the issue-by-issue guidance for updates and actions in environments they manage:
    84218667K
  15. Microsoft Threat Intelligence✓@MsftSecIntel
    Patch now: PHP2Shell, Brotli, and eMudhra guidance for customers
    Microsoft Security Response Center @msftsecresponse
    PHP2Shell, a Brotli decoder vulnerability, and the eMudhra certificate authority key issue each require attention. Microsoft is updating the services it operates and releasing fixes for affected products. Customers should review the issue-by-issue guidance for updates and actions in environments they manage:
    1211474059.1K
  16. Dark Web Informer@DarkWebInformer
    🚨 PHP releases new Windows builds to fix critical HTTP2Shell vulnerability The PHP team has rebuilt its supported Windows packages with Brotli 1.2.1, addressing CVE-2026-111497, an out-of-bounds write flaw that can potentially lead to remote code execution. ⠀ In PHP’s Windows builds, the vulnerable Brotli decoder can be reached through the cURL extension when automatic HTTP response decompression is enabled. This cURL feature is disabled by default, but applications and HTTP client libraries can turn it on. ⠀ Updated builds: • PHP 8.5.12-1 • PHP 8.4.27-1 • PHP 8.3.36-1 • PHP 8.2.35-1 ⠀ The “-1” suffix indicates that the Windows packages were rebuilt with updated dependencies. The PHP source and runtime version numbers remain unchanged. This is separate from the PHP2Shell flaws patched on October 21.
    Descargar
    4116911.3K
  17. s1r1us✓@S1r1u5_
    php2shell is one of the most impactful bugs in recent times, yet threat actors aren’t mass exploiting it the bug is so complex that even porting the exploit between targets takes serious skill, human or ai so i benchmarked how well open and frontier models can do it. 🧵
    Descargar
    446463856.5K
  18. Hunt.io✓@Huntio
    PHP2Shell One Week Later: Honeypot Shells on the Web, a Path to Root on Palo Alto Firewalls One week after the #php2shell patch, around 25 internet-facing #PaloAlto firewalls have been rooted, the first confirmed production compromises. On the open internet, the same bug is still only landing shells on honeypots. We pivoted from the public exploitation reports into our AttackCapture open-directory data to see who is running it. What we found: - ~25 internet-facing Palo Alto PAN-OS firewalls rooted, the first confirmed production compromises. Reported by Dream Research, verified by Unit 42, matched in operator logs we captured. - The chain is two bugs: php2shell lands as nobody on the PAN-OS management interface, then a kernel bug (Fragnesia, CVE-2026-46300) escalates to root. - On the open web, watchTowr, 0x4D31, and GreyNoise see shells only on honeypots. Wiz and CrowdStrike found none. - 616 php2shell files across live open directories: a shared ASLR-bypass kit byte-identical across four hosts, a custom heap exploit with a log cleaner, and cloned PoCs. - One operator handed the exploit research to an AI assistant and left the session log exposed. Full research, IOCs, and detection guidance 👇
    Descargar
    4195711.3K
  19. GGSec@GGASecDe
    Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
    Descargar
    37505.9K
  20. PolySwarm 🇺🇸@PolySwarm
    🚨 Millions of PHP servers could be at risk from PHP2Shell (CVE-2026-109618 & CVE-2026-109619). Exploitation attempts are already emerging, raising concerns for WordPress, Drupal & Joomla sites. Read more: #Cybersecurity #PHP #Cybersecurity #PHP2Shell
    12131.1K
  21. Qualys@qualys
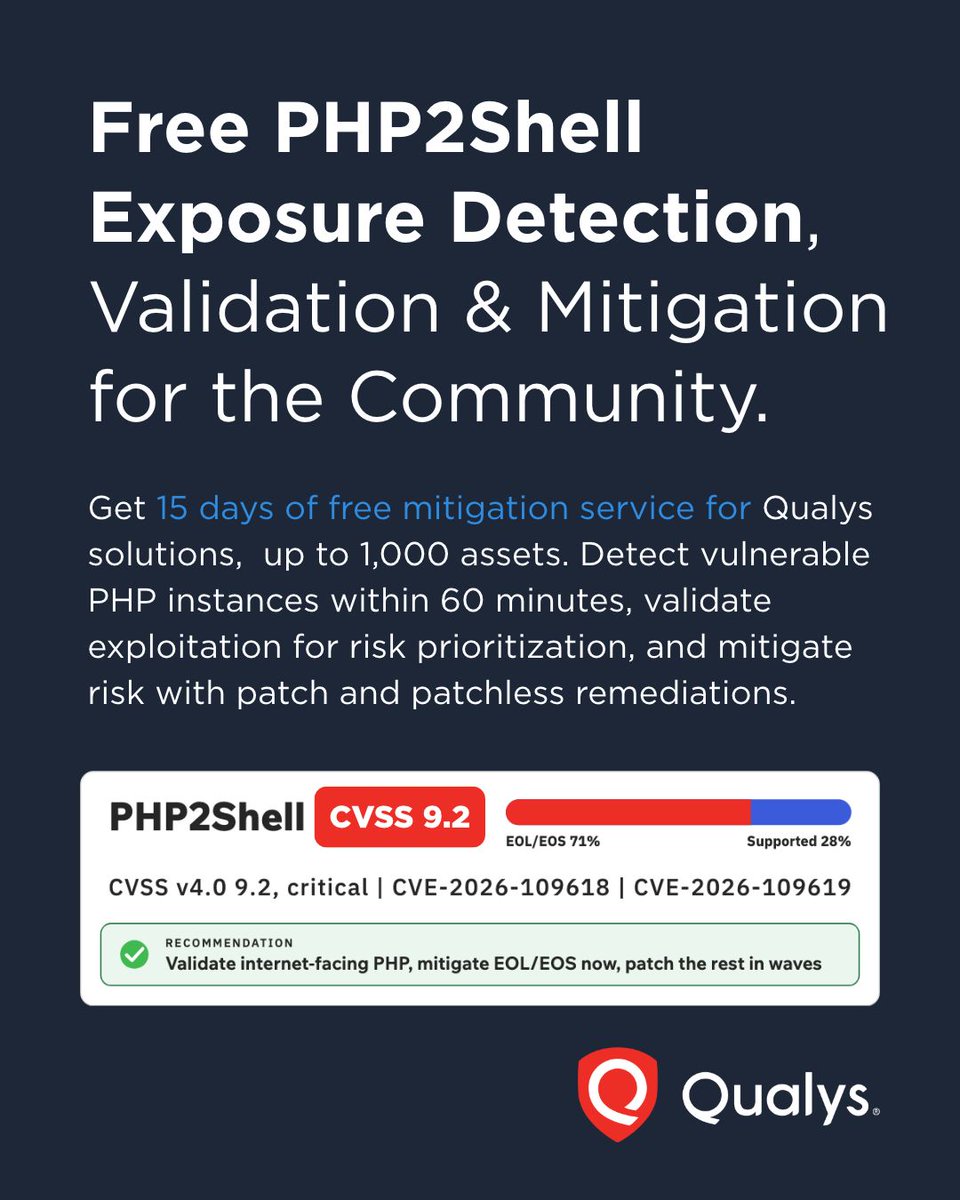
    PHP2Shell: Know your exposure. Take action. PHP2Shell is CVSS 9.2 critical, and end-of-life PHP won't get a patch. Qualys is offering a free 15-day mitigation service for up to 1,000 assets that can help you: -Detect vulnerable PHP instances within 60 minutes -Validate exploitability to prioritize real risk - Mitigate what you can't patch with patchless remediation Get Free PHP2Shell Mitigation Service:
    Descargar
    139976
  22. Mostrar más posts