Publicações com #HTTP2Shell

#HTTP2Shell

Publicações públicas do X que usam #HTTP2Shell.

Hashtags relacionados

  1. Hunt.io✓@Huntio
    PHP2Shell One Week Later: Honeypot Shells on the Web, a Path to Root on Palo Alto Firewalls One week after the #php2shell patch, around 25 internet-facing #PaloAlto firewalls have been rooted, the first confirmed production compromises. On the open internet, the same bug is still only landing shells on honeypots. We pivoted from the public exploitation reports into our AttackCapture open-directory data to see who is running it. What we found: - ~25 internet-facing Palo Alto PAN-OS firewalls rooted, the first confirmed production compromises. Reported by Dream Research, verified by Unit 42, matched in operator logs we captured. - The chain is two bugs: php2shell lands as nobody on the PAN-OS management interface, then a kernel bug (Fragnesia, CVE-2026-46300) escalates to root. - On the open web, watchTowr, 0x4D31, and GreyNoise see shells only on honeypots. Wiz and CrowdStrike found none. - 616 php2shell files across live open directories: a shared ASLR-bypass kit byte-identical across four hosts, a custom heap exploit with a log cleaner, and cloned PoCs. - One operator handed the exploit research to an AI assistant and left the session log exposed. Full research, IOCs, and detection guidance 👇
    Baixar
    4215913.1K
  2. BleepingComputer✓@BleepinComputer
    The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added the PHP2Shell vulnerabilities to its catalog of actively exploited security flaws and ordered federal agencies to patch their systems by Thursday.
    114315914.8K
  3. GreyNoise✓@GreyNoiseIO
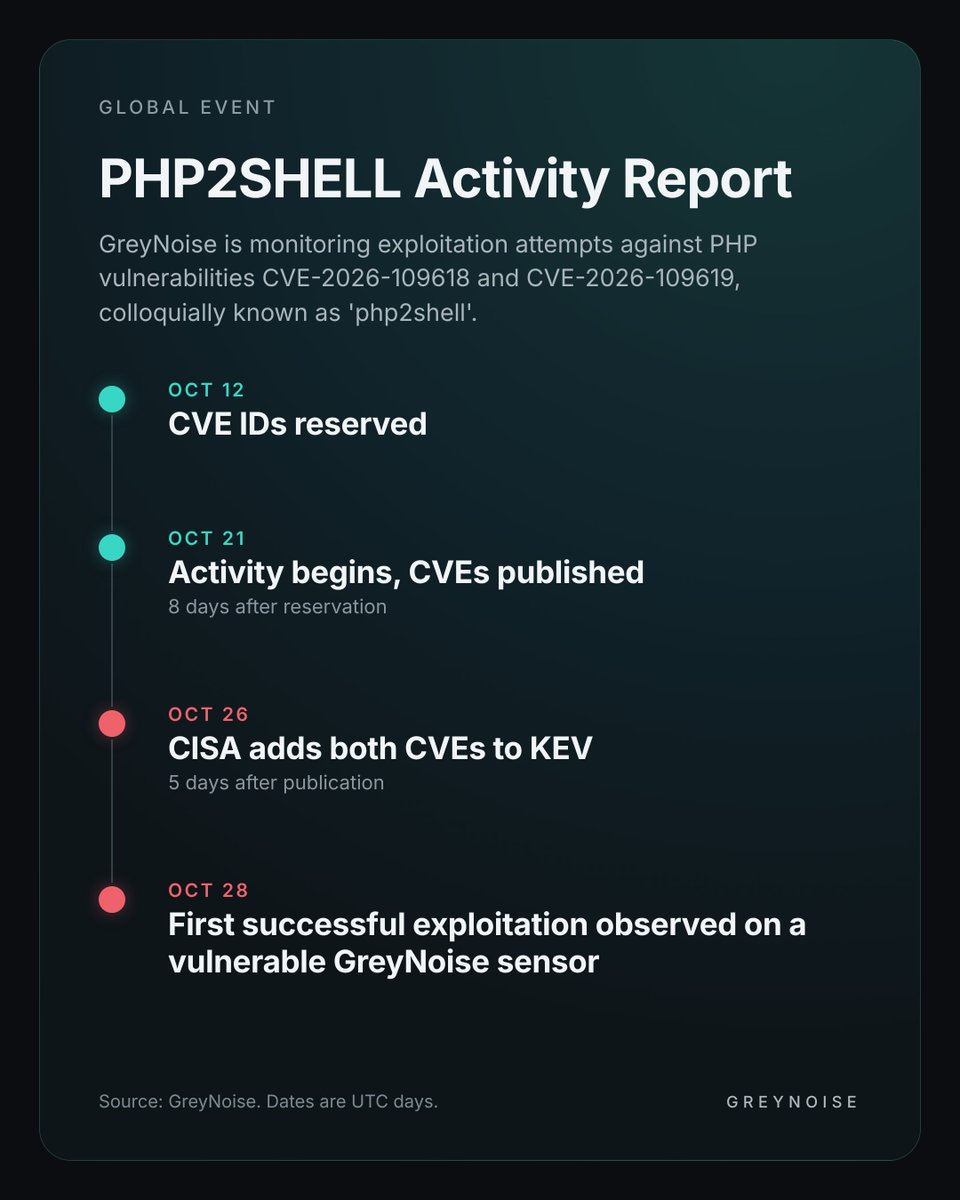
    GreyNoise is monitoring exploitation attempts against #php2shell (CVE-2026-109618 and CVE-2026-109619). On 28 Oct 2026, 05:14:01 UTC we observed the first successful exploitation of php2shell against a vulnerable GreyNoise sensor. "We’re seeing successful exploitation of these CVEs, but the conditions make it difficult for a threat actor to scale. Fifty different servers in various configurations can be vulnerable to these CVEs, but the same exploit may not work universally against all of them. Actors need to tailor their exploit for each respective configuration which makes mass exploitation challenging." - @ImposeCost, SVP of Adversary Operations at GreyNoise This live activity report is derived from GreyNoise data and updates as we observe new activity:
    Baixar
    522928K
  4. GGSec@GGASecDe
    Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
    Baixar
    37516.3K
  5. The Hacker News@TheHackersNews
    🚨 CISA adds two PHP2Shell bugs to its KEV catalog after confirming active exploitation. CVE-2026-109618 and CVE-2026-109619 enable unauthenticated remote code execution on affected PHP deployments. Read ↓
    266223242.8K
  6. IEEE Spectrum@IEEESpectrum
    PHP2Shell hints that AI may find legacy bugs faster than we can patch them; the next exploit might not end this safely.
    4121.2K
  7. BleepingComputer✓@BleepinComputer
    Critical 'HTTP2Shell' Brotli vulnerability triggers emergency patches
    53111316.7K
  8. Aimore✓@aimorebou
    OpenAI’s PHP2Shell checker can say "OK" about a server it never inspected✊ It reads two HTTP headers and compares the version to the patched releases. That’s it. No exploit probes. No scan of the install. Hidden headers: UNKNOWN. Backported fixes: invisible. PHP 8.1 and older: flagged even on the latest patch. OpenAI’s own README: "Even OK only describes the advertised version." Still a useful first look. Patched: 8.2.35, 8.3.36, 8.4.27, 8.5.12. Do you trust a green check that never touched your server?
    Baixar
    529447
  9. Daniel Púa✓@devploit
    Thanks @TenableSecurity for the mention! They used my php2shell PoC to reproduce CVE-2026-109618/109619 on several PHP 8.4/8.5 setups and wrote up why the exploit is so build-dependent: heap offsets, worker reuse, and why version checks lie. Great read.
    4281316.1K
  10. XBOW@Xbow
    With all the chaos around PHP2Shell, what can defenders do right now? A thread🧵
    33283.4K
  11. Rad Imre@ImreRad
    While everyone is pulling all-nighters over #php2shell & #HTTP2Shell, I audited Perl infra in my freetime: Found an RCE in the PAUSE indexer (CPAN's core). Reported & patched in hours—saving you from a perl2shell nightmare. (If you run a private PAUSE server: patch now! 😅)
    21171.4K
  12. Opsec✓@RunOpsec
    Today we're introducing our first upgrade since going live Opsec Workflows: a fleet of autonomous agents that defends your code against attacking agent swarms. Exploit complexity used to be a security control, and AI has mostly removed it. Attackers now run agents in parallel while defense still works one ticket at a time. Describe a security job once in plain English, and Workflows builds the agents behind it and runs them every time the trigger fires. The fleet checks every repo at once, the moment the work shows up, instead of waiting for someone to be online. Your team stops chasing breadth and spends its time on the calls that need judgment. It's live on
    Baixar
    1061081473.8K
  13. Opsec✓@RunOpsec
    @RunOpsec
    PHP2Shell showed the gap. Two PHP flaws more than a decade old became working exploits in hours, and attack traffic was already hitting sites before the official disclosure. Defense that waits for someone to be online loses that race. A fleet checks every repo at once, the moment a CVE lands.
    63060557
  14. Hostinger✓@Hostinger
    PHP2Shell: unauthenticated RCE, CVSS 9.2, exploited in the wild. We've patched across all hosting and tested the public exploit against our stack. No successful execution. Nothing to do on your side. Self-hosting? 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35.
    53213.4K
  15. The Hacker News@TheHackersNews
    🚨 PHP2Shell exploited in real-world attacks. An attacker chained PHP2Shell with a Linux kernel flaw to gain root access to 25 servers across four countries, including three in a U.S. government-affiliated environment. The intrusion extended into the internal network, where the attacker targeted Active Directory. Suspected China nexus. Signs of AI-assisted tooling. Read the full report:
    Baixar
    4112258565.6K
  16. The Hacker News@TheHackersNews
    🚨 Palo Alto Networks confirms active attacks exploiting PHP2Shell flaws in internet-exposed PAN-OS management interfaces. The flaws allow unauthenticated remote code execution. Multiple PAN-OS versions are affected, with some fixes still pending. Read ↓
    Baixar
    147325955.5K
  17. Tenable@TenableSecurity
    #PHP2Shell drew instant Log4Shell comparisons, but a week of testing showed the key difference: a working exploit has to be tuned to each target's exact PHP build. The exception is devices that all run the same build, like network appliances. Our post-mortem covers why both are true, and what it means for your patch prioritization queue:
    1361.1K
  18. BleepingComputer✓@BleepinComputer
    CISA ordered US federal agencies to patch a high-severity Linux kernel privilege escalation bug that attackers are chaining with the PHP2Shell flaws in the wild.
    13289912.2K
  19. HackerproofHQ@HackerproofHQ
    Security Update: PHP2Shell CVE-2026-109618 and CVE-2026-109619 could allow remote code execution on vulnerable PHP systems without authentication. Update affected systems, review logs, and investigate suspicious activity. #Cybersecurity #InfoSec #SecurityUpdates #Php
    Baixar
    101115301
  20. CyberDefenders®™✓@CyberDefenders
    An HTTP 500 error doesn't always mean an attack has failed. Sometimes, it's just the beginning of the investigation. 🔍 We've put together a practical detection and incident response guide to help you connect suspicious requests, PHP errors, and host activity to uncover signs of compromise. Now, put your investigation skills to the test with our new hands-on lab: GlassHeap - PHP2Shell 1. Start the lab: Read the guide:
    Baixar
    205519
  21. Mostrar mais publicações