We'll see a lot of stranded compute making its way to small modular datacenters in retail, academic, and commercial venues where power is abundant, cheap and renewable.
Datacenters are coming home.
Share
Copied
Elon Musk@elonmusk
@Yuchenj_UW I think we’re going to see a lot of stranded compute in partially complete data centers
I've been deep in several token mechanisms the past few months to conclude $HYPE has the best economics for turning product revenue into tokenholder value.
Is there any other better?
RT @alextapscott: New @defidecodedpod is out!
I sit down with @gregosuri of @akashnet to discuss why decentralized compute networks could power the next wave of AI.
Infrastructure bottlenecks, data centre backlash, and power shortages means we must tap into GPU capacity wherever it exists—even in our own homes.
Always a blast chatting with Greg.
Check it out!
Share
Copied
The DeFi Decoded Podcast@defidecodedpod
Episode 252: How Decentralized Compute Markets Solve AI Bottlenecks with Greg Osuri of Akash Network
@alextapscott@gregosuri@akashnet@CMCC_Global
0:00 Introduction
3:37 The state of compute: the biggest build-out in human history
4:27 Is AI demand slowing? Reading one lab’s soft quarter
8:27 Humans prompt once a minute, agents a thousand times
10:36 Will people pay for AI? Newspapers vs. the internet
15:14 “We let go any engineer that doesn’t use AI”
19:14 The subsidized party: a $200 plan worth $8,000 of compute
21:37 CoreWeave’s jitters and the leverage problem
23:25 Energy, permits, and the pushback stalling data centers
28:19 Training vs. inference, and the gigawatt problem
32:55 Why inference can run anywhere: Macs, offices, homes
36:37 Akash Home Node: putting your gaming PC to work
39:04 Akash today: nearly a trillion tokens a month
41:26 Making compute contracts tradable
47:00 Where to find Greg, and why homes are the future of AI
Crypto has matured. Capital allocators are recognizing that the most successful protocols will be those with minimal or no pre-launch funding, which contradicts venture capital math.
Successful protocols typically exhibit a stronger alignment between the token and the counterparties whose value derives from the liquidity and network effects.
There’s limited room for $100 million rounds that could potentially return $1 billion.
This is perhaps the most bullish thing about 2026. Crypto is becoming what it is supposed to be: transparency, information symmetry, and equal opportunity for participants.
I have never been more bullish on crypto.
LFG all in 🚀
RT @DavidVorick: Defenders are out here getting refusals from frontier models, meanwhile attackers are blazing forward with MILLIONS of attacks within 24 hours of a vulnerability announcement.
These "safeties" aren't saving anyone.
Share
Copied
Matthew Prince 🌥@eastdakota
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Every time I buy something from Japan, I'm always amazed by how thoughtful the packaging is and how high quality the products are. It's a whole new standard.
But doing business with the Japanese is quite the opposite. They move extremely slowly and are misaligned with the realities of modern delivery speeds.
I can't, for the love of God, figure out why that is.
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
PSA: Update your IoT devices, OS, browsers, and any developer tools or container images ASAP.
This is an extremely serious security incident.
Share
Copied
Anzal Abidi@AnzalAbidi
Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
"Speculative data center debt is being repackaged and sold to pension and retirement funds, university endowments, and other institutional investors in a manner eerily reminiscent of the subprime bubble."
"Speculative data center debt is being repackaged and sold to pension and retirement funds, university endowments, and other institutional investors in a manner eerily reminiscent of the subprime bubble."
Almost all new datacenters rely on behind-the-meter generation of low-cost natural gas from shale regions like the Permian Basin.
This party may end when the left sweeps Congress and the White House.
Share
Copied
John Arnold@johnarnold
Underappreciated how much the shale revolution unlocked the AI revolution.
Anthropic wants you to believe that the demand for AI is slowing down, but the reality is quite the opposite. The usage of inferences by agents is growing exponentially.
A significant portion of Anthropic’s revenue comes from enterprise companies like Meta. Meta is realizing that it is much more cost-effective to develop its own models rather than relying on Anthropic’s services.
Share
Copied
OpenRouter@OpenRouter
Agentic usage is up 34x since the start of February 2026.
Agentic usage is also now about 8x higher than human usage across OpenRouter on a weekly basis.
Agentic usage is up 34x since the start of February 2026.
Agentic usage is also now about 8x higher than human usage across OpenRouter on a weekly basis.
I've been sounding the horn about rising energy costs impacting hyperscalers for over four years and now AWS cannot deploy more compute due to lack of energy.
Distributed modular datacenters are the future and Akash is ready.
@NagatoDharma@akashnet Rising energy costs impact everything but can the managed better when compute clusters are well distributed to leverage regional advantages.
@NagatoDharma@akashnet Rising energy costs impact everything but can the managed better when compute clusters are well distributed to leverage regional advantages.
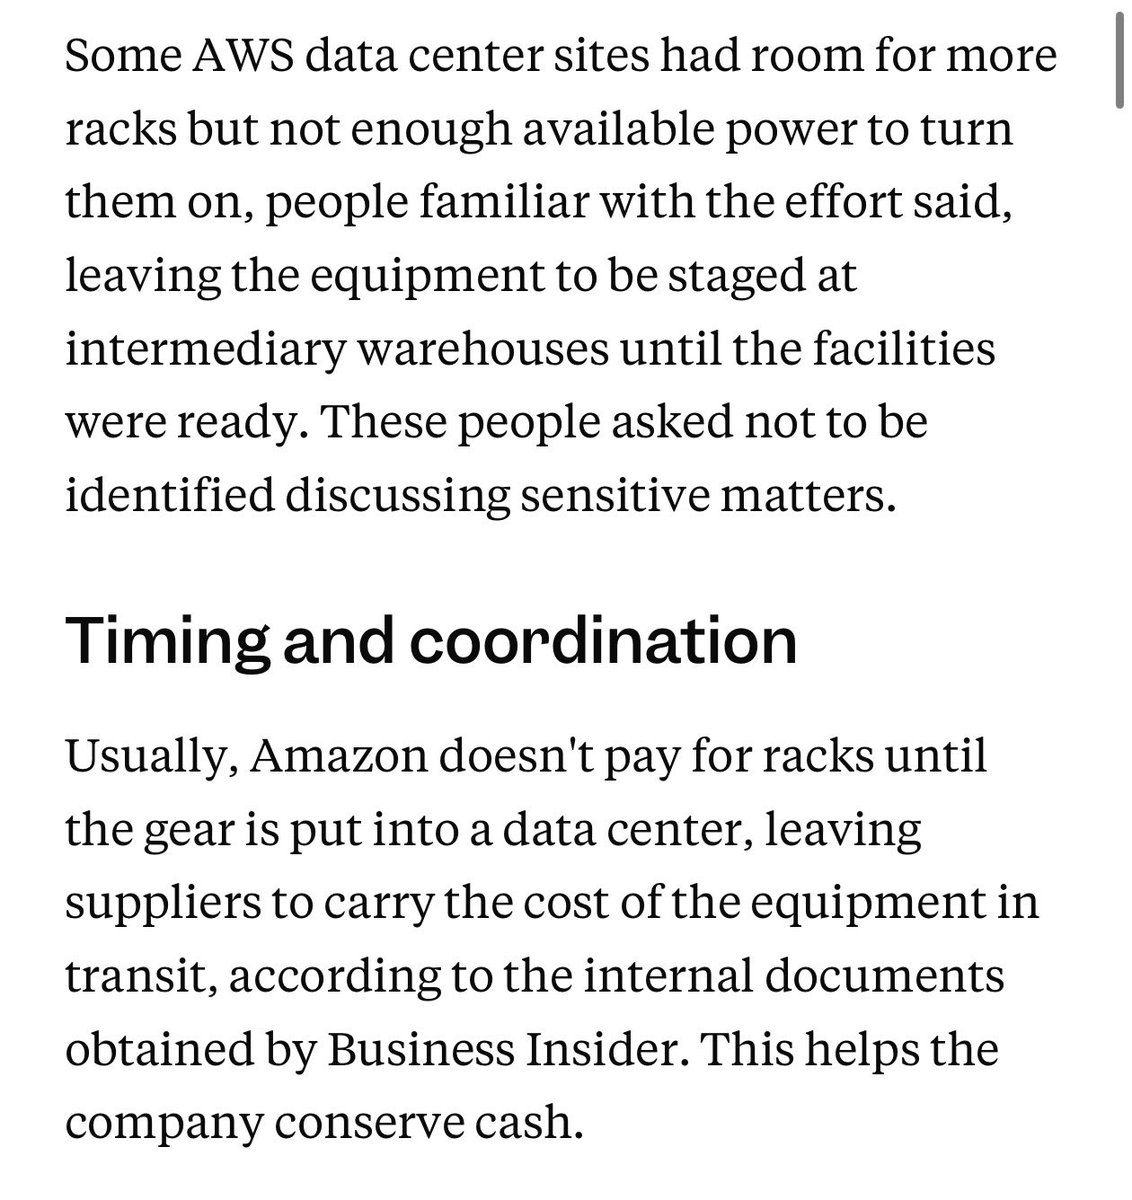
I’ve been talking about Hyperscalers hoarding valuable GPUs because they have no where to install them due to power and supply chain constraints.
An explosive investigation by Business insider just proved my suspicion.
The industry has a liquidity problem.
Share
Copied
Ed Zitron@edzitron
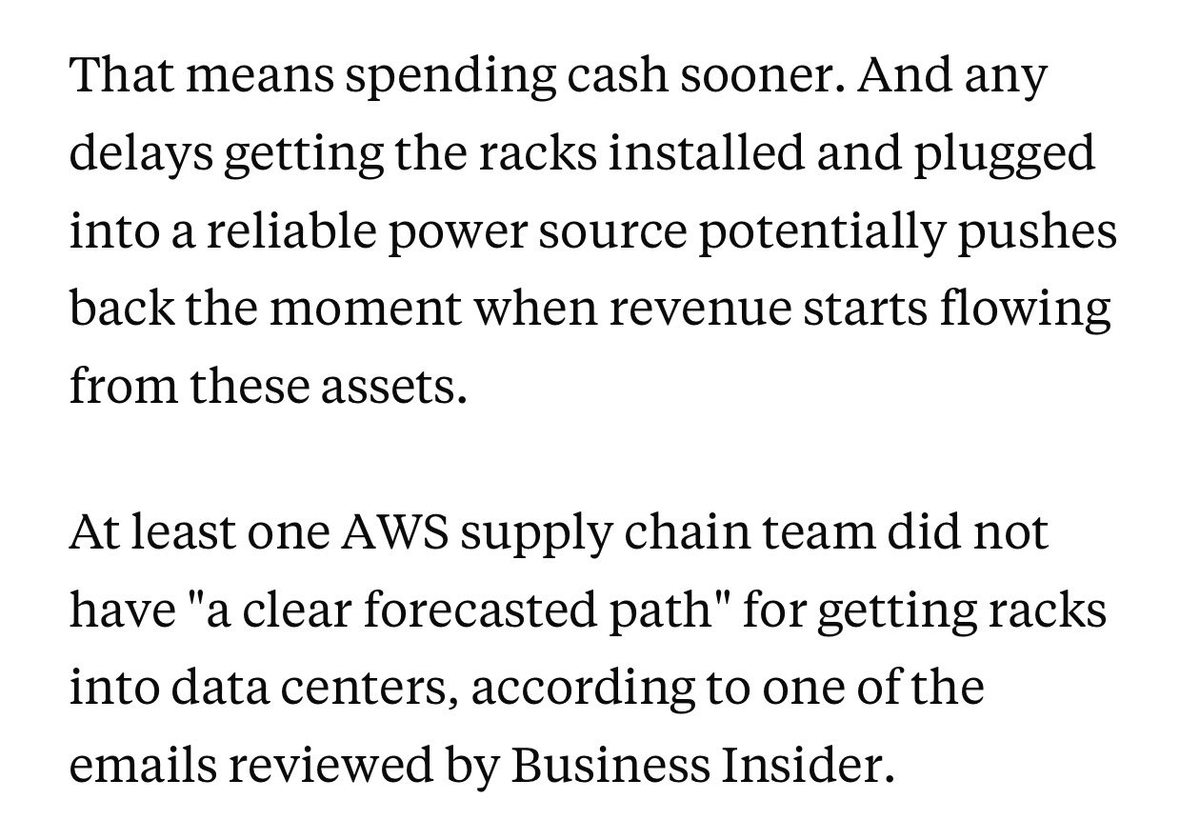
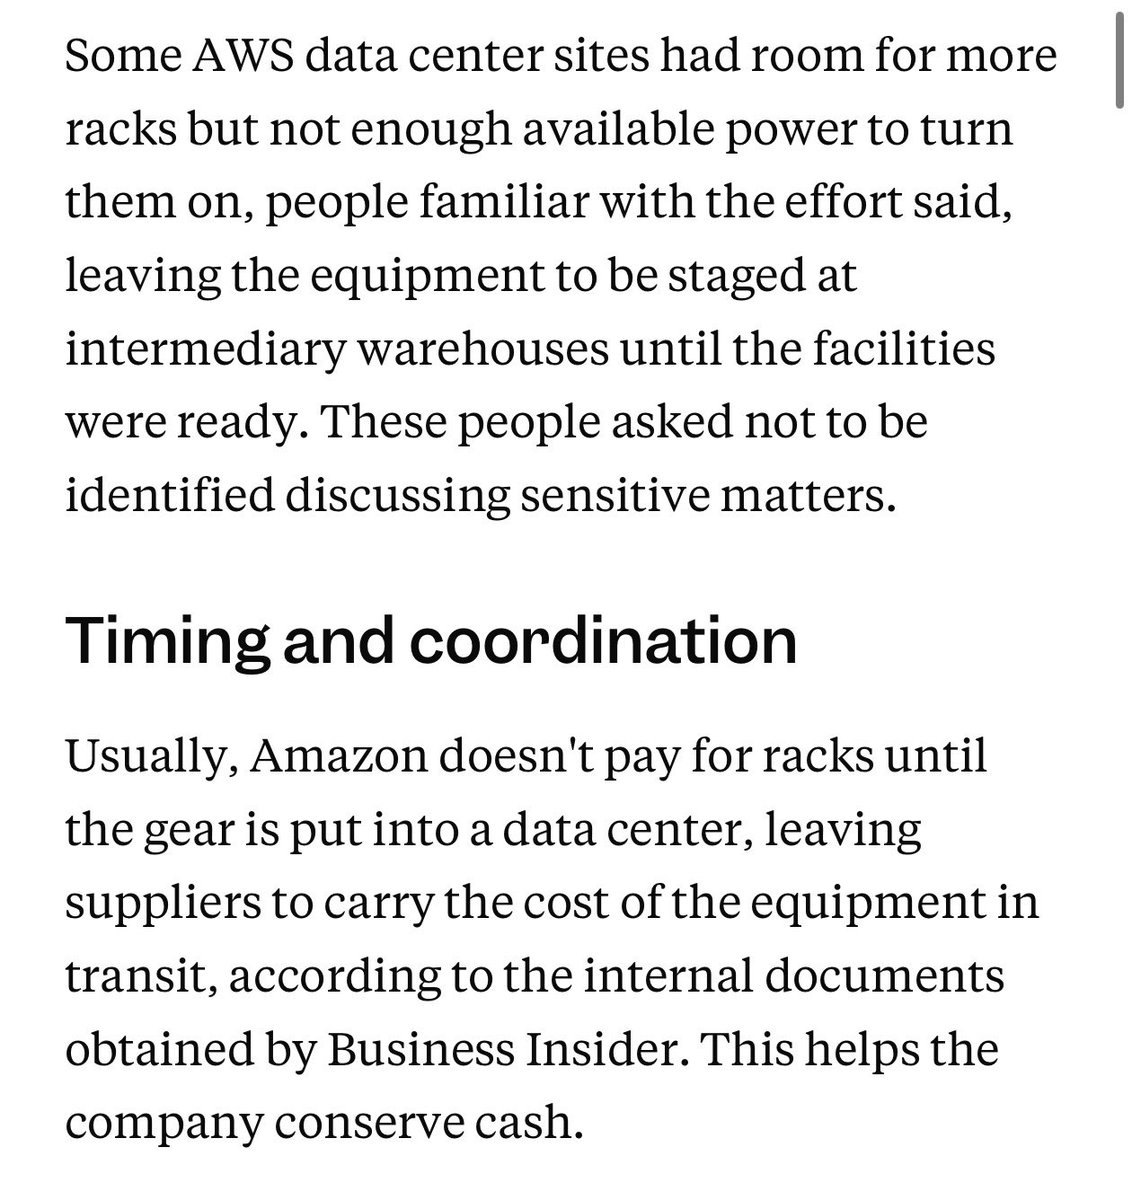
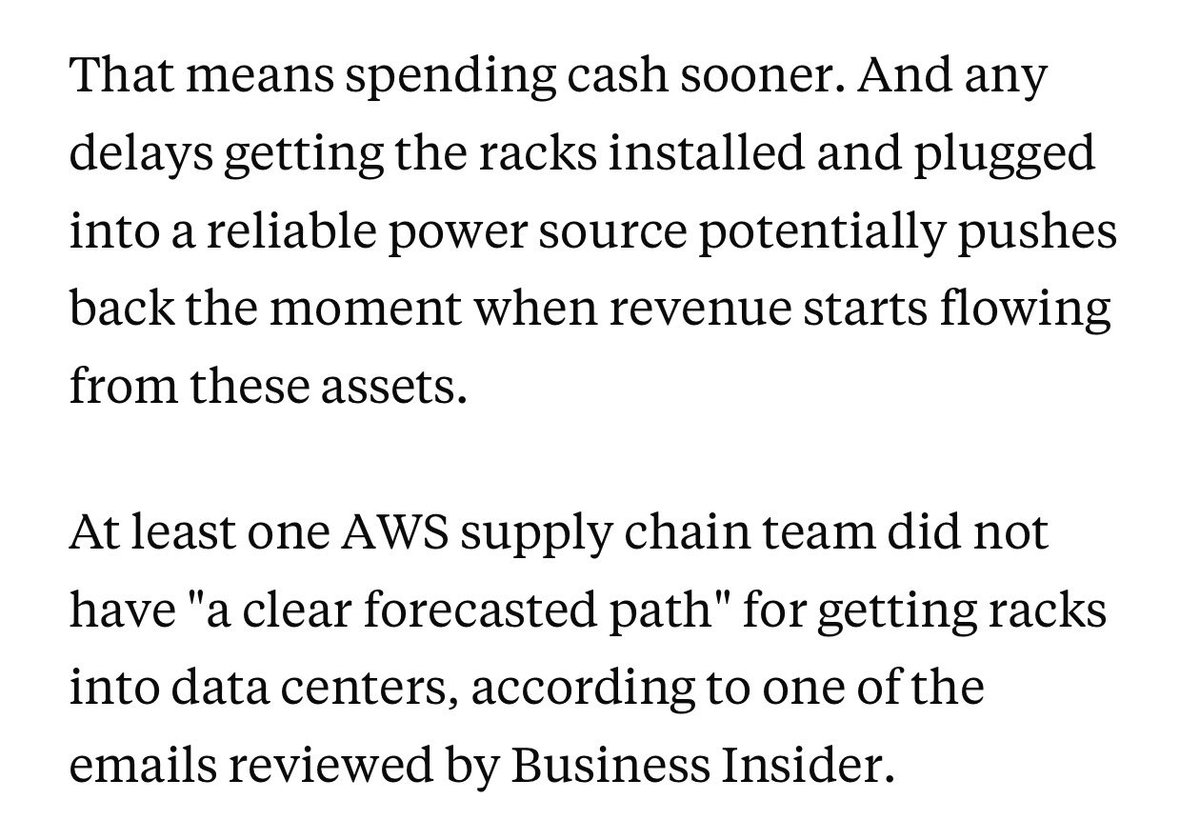
Business Insider confirms it: Amazon has warehouses of GPUs that can’t be installed, and is buying them so far in advance that a supply chain team said they “didn’t have a clear forecasted path” to installing them.
Business Insider confirms it: Amazon has warehouses of GPUs that can’t be installed, and is buying them so far in advance that a supply chain team said they “didn’t have a clear forecasted path” to installing them.
Until last year, GPUs were impossible to source; we saw an explosion of well-capitalized institutions.
From next year, it will be impossible to source hyperscaler-grade energy to scale AI; we'll see an explosion in demand for distributed clouds.
While you're too busy chasing memecoin scams, DePIN demand is exploding, and will be too late when you finally realize.
Wake up, anon. Zoom out.
RT @akashians_: Receipts from November 2024.
@gregosuri said hyperscalers would end up with GPUs they couldn’t power. Business Insider just reported Amazon has warehouses of them — sites with room for more racks but not enough power to turn them on, and no clear forecasted path to installing them.
He also said in Feb 2025 that everyone would be talking about the energy crisis in two years.
Somewhere right now there’s a startup that can’t get an H100, and a warehouse full of them that nobody can plug in.
That’s not a shortage. That’s an allocation failure — and it’s the exact problem @akashnet was built for. An open marketplace where any provider with powered, idle capacity can list it, and anyone who needs compute can rent it. No queue, no allocation meeting, no waiting on a substation.
$AKT #DePIN#DeAI#Web3#GPU@akashnetAI
Share
Copied
Greg Osuri 🇺🇸@gregosuri
I’ve been talking about Hyperscalers hoarding valuable GPUs because they have no where to install them due to power and supply chain constraints.
An explosive investigation by Business insider just proved my suspicion.
The industry has a liquidity problem.
Protocols that survived the past few years are relentlessly building.
I think I’ll start going back to crypto conferences moving forward — what’s the most exciting one coming up?
Share
Copied
Stacy Muur@stacy_muur
Compiled a list of protocols that have shut down in 2026.
82 protocols year-to-date.
I've never seen anything like this before.
RT @ElonTrades: Revolut is down today because of a Google Cloud outage in London (europe-west2).
A power event in one availability zone knocked out multiple services. Revolut’s app, cards, and payments went offline (funds and data are safe). Other banks and services were hit too.
Why didn’t multi-region or multi-cloud save them?
They use Google Cloud heavily (multi-year partnership) and do multi-region for some workloads. But the critical path (auth, card authorization, payments) was still too dependent on the London region. When that region had issues, failover didn’t fully cover it.
True active-active multi-region/multi-cloud for stateful banking systems is expensive and complex (data consistency, latency, compliance, testing). Many fintechs accept the residual risk until an incident forces the issue.
Decentralized options like Akash $AKT can reduce single-provider risk in theory, but they don’t currently match the compliance, SLAs, and predictability banks need for production payments infrastructure.
Share
Copied
Revolut@Revolut
We are currently experiencing a service disruption affecting multiple services. We can confirm that all our customers’ money and data are safe. We’ve been working to fix the issue since it was identified this morning and apologise to anyone affected and for any inconvenience caused.
We are currently experiencing a service disruption affecting multiple services. We can confirm that all our customers’ money and data are safe. We’ve been working to fix the issue since it was identified this morning and apologise to anyone affected and for any inconvenience caused.