Posts with #Disassembler

#Disassembler

Public posts on X that use #Disassembler.

Related hashtags

  1. ringzerø.training && @[email protected]@_ringzer0
    What are the limitations of an online sandbox? Here’s what expert @jstrosch has to say: Online sandboxes are a great first step for #malware analysis, as they allow you to: ID the malware family, see hosts it connects to & pull config info. BUT....👇
    143
  2. ringzerø.training && @[email protected]@_ringzer0
    @_ringzer0
    Here are the downsides: >Many require a paid subscription for premium features like choosing different OS (#Windows 7, 10, #Linux) or network routes (to defeat #geofencing) >May restrict access to all the raw data, like #API calls >Limit how much you can use it, so may not scale
    112
  3. ringzerø.training && @[email protected]@_ringzer0
    @_ringzer0
    A custom malware lab fixes these problems & lets you go deeper. W/ a home lab, you can do: automated analysis such as a sandbox, & more in-depth static/dynamic analysis thru tools like a #debugger & #disassembler. Learn how to build your own lab @
    012
  4. Howard Price@howprice
    Aira Force #Amiga #Emulator #Disassembler #Debugger 0.9.1 released Highlights: - Audio DMA emulation - First pass sync-to-video audio out (use at your own risk) - Emulator optimisations - macOS Universal Binaries More details here: Video with sound!
    Download
    014174
  5. Juan Fumero@snatverk
    New blogpost: Learn how to build JDK 21 and JDK 25 with the HotSpot Disassembler (HSDIS) plugin enabled for Linux. `hsdis` is a tool to inspect the JVM’s JIT-compiled assembly code, and this post explains how to configure it: 🔗 #java #disassembler
    016261.4K
  6. Gerred is in SF! ➡️ 10/31-11/7✓@sloppenheimer
    Opus 5.5 isn't blocking me on this for everyone paranoid about reverse engineering and game remakes. We're in a slow bytecode and register equal reverse engineering. Funnily enough, it wants 1 C++ file per disassembled function. I think everyone's fears were unfounded.
    Gerred is in SF! ➡️ 10/31-11/7 @sloppenheimer
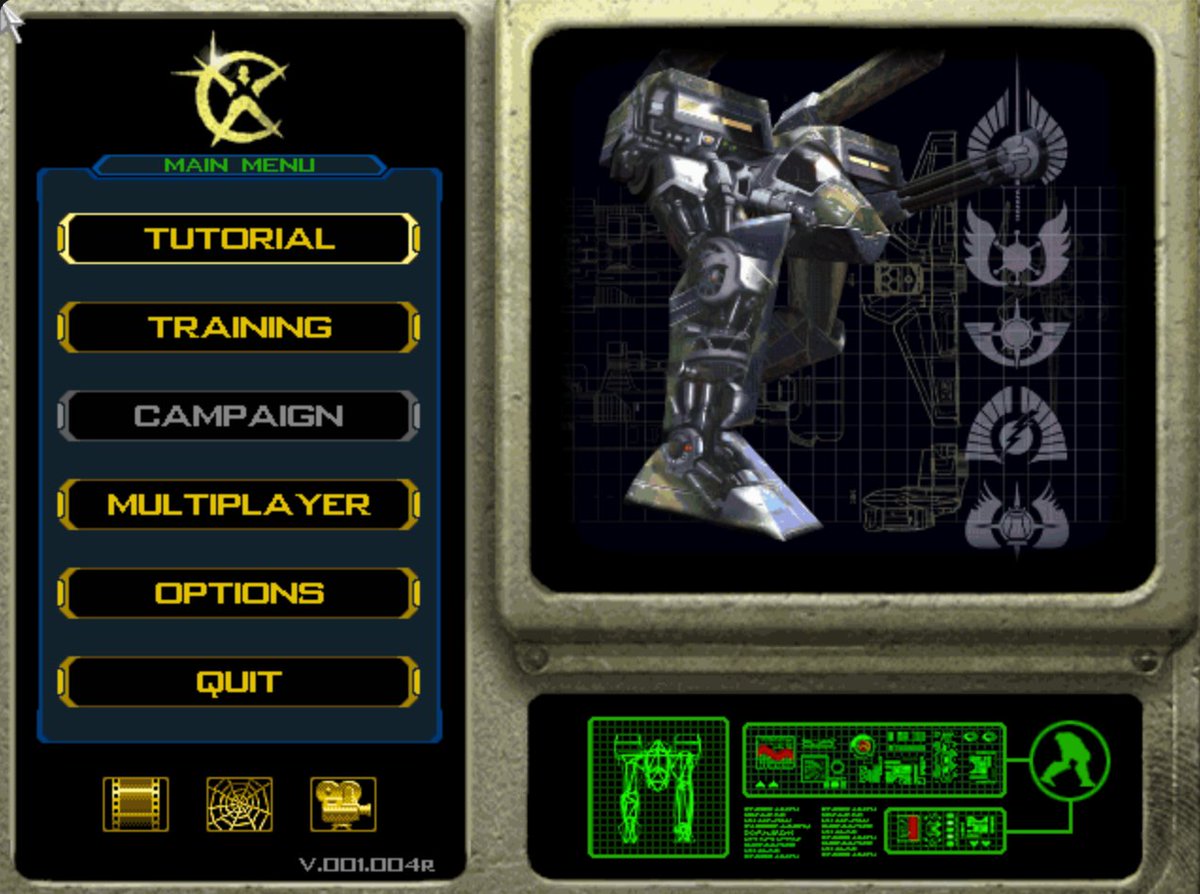
    decompilation and reverse engineering is fun, as it turns out. mac -> colima vm -> qemu -> borland c++ compiler + decompilation of starsiege from machine code, byte and register identical.
    208468
  7. Gerred is in SF! ➡️ 10/31-11/7✓@sloppenheimer
    decompilation and reverse engineering is fun, as it turns out. mac -> colima vm -> qemu -> borland c++ compiler + decompilation of starsiege from machine code, byte and register identical.
    Download
    10101.1K
  8. Hack with GitHub@HackwithGithub
    Plasma: Interactive #disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax
    02031
  9. rvaniaaa✓@rvaniaaaa
    5165359.4K
  10. Show more posts