Posts with #ProxyShell

#ProxyShell

Public posts on X that use #ProxyShell.

Related hashtags

  1. Donny Maasland@donnymaasland
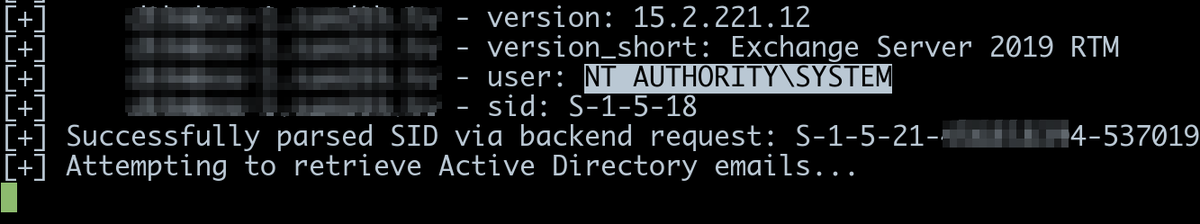
    I wanted to write detection rules for #ProxyShell, but as usual I couldn't find a PoC (although every vulnerable server has probably been compromised). Anyway, here is a PoC that gives you a PowerShell shell: So not full RCE, but enough for detection.
    Download
    597215
  2. Kyle Hanslovan@KyleHanslovan
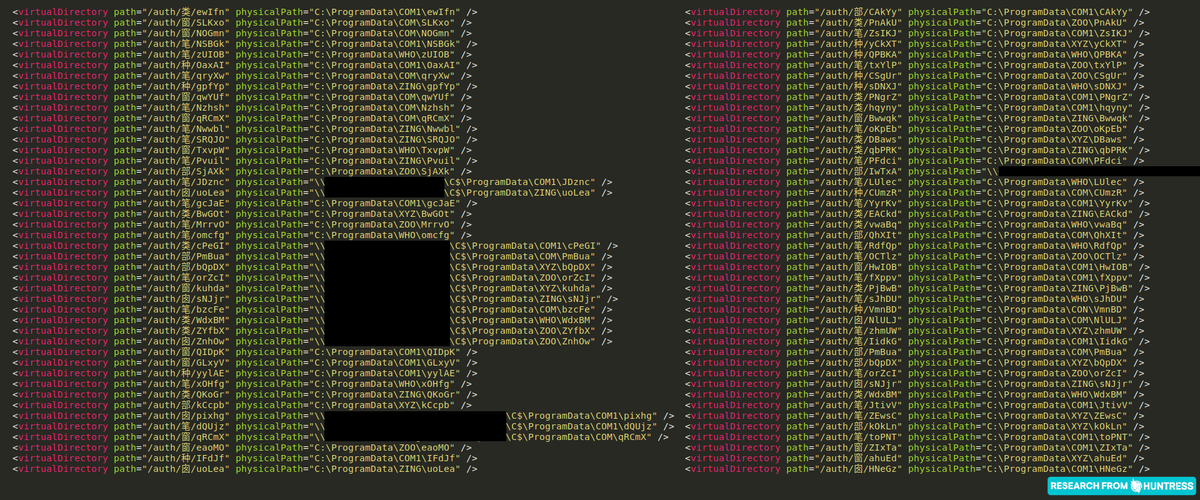
    While digging into a partner who was hit with #ProxyShell -> LockFile ransomware activity, @DaveKleinatland found a webshell relocation TTP we’ve never seen discussed before. Works like a symlink and allows actors to store webshells outside of typically monitored ASP directories.
    Dave Kleinatland @DaveKleinatland
    Alternate tactic being used in #ProxyShell: attacker modified IIS "MSExchangeOWAAppPool" app pool by adding additional virtual directory to "/owa" with path "/auth/类/hxxxy". Webshell located in C:\ProgramData\COM1\hxxxy. Check your configs when hunting!
    241133
  3. Dave Kleinatland@DaveKleinatland
    Alternate tactic being used in #ProxyShell: attacker modified IIS "MSExchangeOWAAppPool" app pool by adding additional virtual directory to "/owa" with path "/auth/类/hxxxy". Webshell located in C:\ProgramData\COM1\hxxxy. Check your configs when hunting!
    Download
    361192
  4. Sophos@Sophos
    NEW: The Squirrelwaffle (no, that's not a typo) malware loader was used in conjunction with the #ProxyLogon and #ProxyShell exploits to target an unpatched Microsoft Exchange server. 🎯 Learn more from the Sophos Rapid Response team investigation:
    Download
    0109
  5. Huntress@HuntressLabs
    Psst! Gentle reminder: #ProxyShell is NOT ProxyLogon, and just patching in March isn't good enough. Please, please, patch! (Also, LockFile ransomware is not the same as LockBit ransomware. 😬)
    01532
  6. Johnk3r@johnk3r
    I have written an @pdnuclei rule to detect the compromise of the Proxyshell vulnerability. I'll test a little more before committing. Very happy with the result 🚀 #proxyshell #CVE-2021-34473 #CTI
    Download
    41567
  7. TG Soft@VirITeXplorer
    @VirITeXplorer
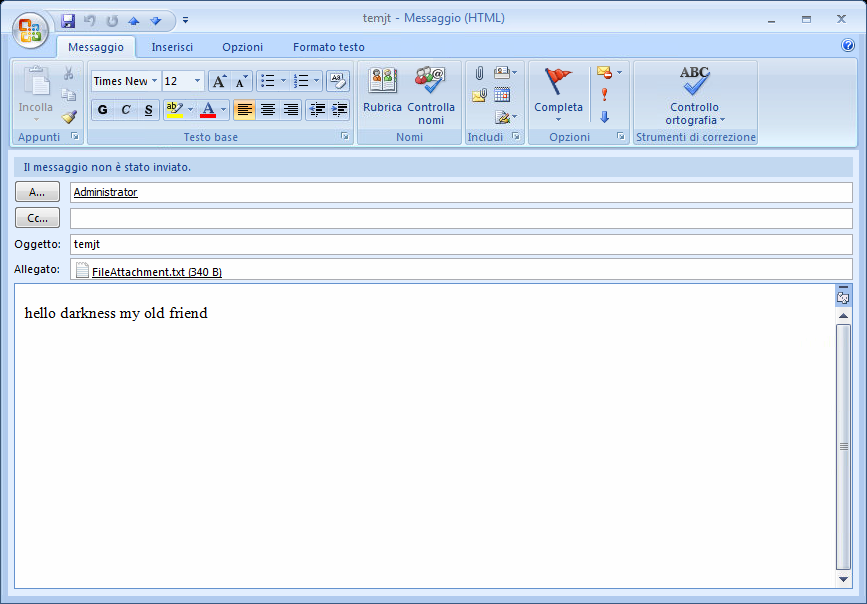
    Attacker exploited MS Exchange server with the #proxyshell discovered by Orange Tsai @orange_8361 ( Inside the attachment FileAttachment.txt there is the webshell. (1/n)
    Download
    315
  8. berming@ber_m1ng
    Just reproducing #ProxyShell RCE, great work from @orange_8361 ! Here's some tips if you're also trying to exploit 1. if you use python PYPSRP module, there's little bug and you might get error "... failed because the shell was not found on the server"
    3324
  9. John Hammond✓@_JohnHammond
    Still digging in to this, but we've seen ~90 occurrences of this over ~60 endpoints, some with multiple. Not all a "COM", or "COM1" subdirectory. Some with a \\ UNC path referring to a #ProxyShell webshell path even on separate machine (cc @HuntressLabs)
    Download
    Kyle Hanslovan @KyleHanslovan
    While digging into a partner who was hit with #ProxyShell -> LockFile ransomware activity, @DaveKleinatland found a webshell relocation TTP we’ve never seen discussed before. Works like a symlink and allows actors to store webshells outside of typically monitored ASP directories.
    11660
  10. The DFIR Report✓@TheDFIRReport
    APT35 Automates Initial Access Using ProxyShell ➡️Initial Access: #ProxyShell ➡️Discovery: net, ipconfig, PowerShell, quser, etc. ➡️PrivEsc: Scheduled Task ➡️Defense Evasion: Real-time Monitoring & WDigest enablement ➡️Credential Access: Comsvcs.dll
    2115271
  11. Andy Rector@DetectorRector
    Don't miss #ProxyShell 🐚 📫process name: MSExchangeMailboxReplication.exe 📁extension: asp(x) This is evidence of the last stage of the attack in which the Mailbox Export function is used to create a PST (!BDN magic bytes) containing an embedded web shell.
    Download
    0928
  12. John Hammond✓@_JohnHammond
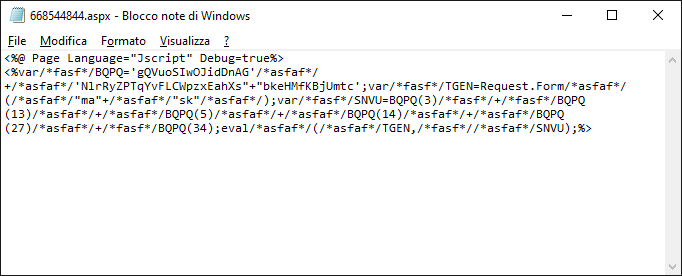
    Some cheeky #ProxyShell shenanigans in a discovered webshell -- the BQPQ variable looks like enough gibberish to be consider Base64 at first glance, but it's just a pool of characters to pull from and index the letters to build out the "unsafe" keyword for the eval function.
    Download
    325175
  13. Donny Maasland@donnymaasland
    Here is a list of PowerShell cmdlets you can use with #ProxyShell: Don't focus exclusively on "New-ManagementRoleAssignment" or "New-MailExportRequest".
    02884
  14. ESET Research✓@ESETresearch
    #ESETresearch uncovered previously unknown group #Worok, targeting high-profile users mostly in Asia. The group uses steganography to hide malicious payloads in PNG files and a custom PowerShell backdoor doing C&C via ICMP or HTTP protocols. @passil_t 1/5
    359109
  15. ESET Research✓@ESETresearch
    @ESETresearch
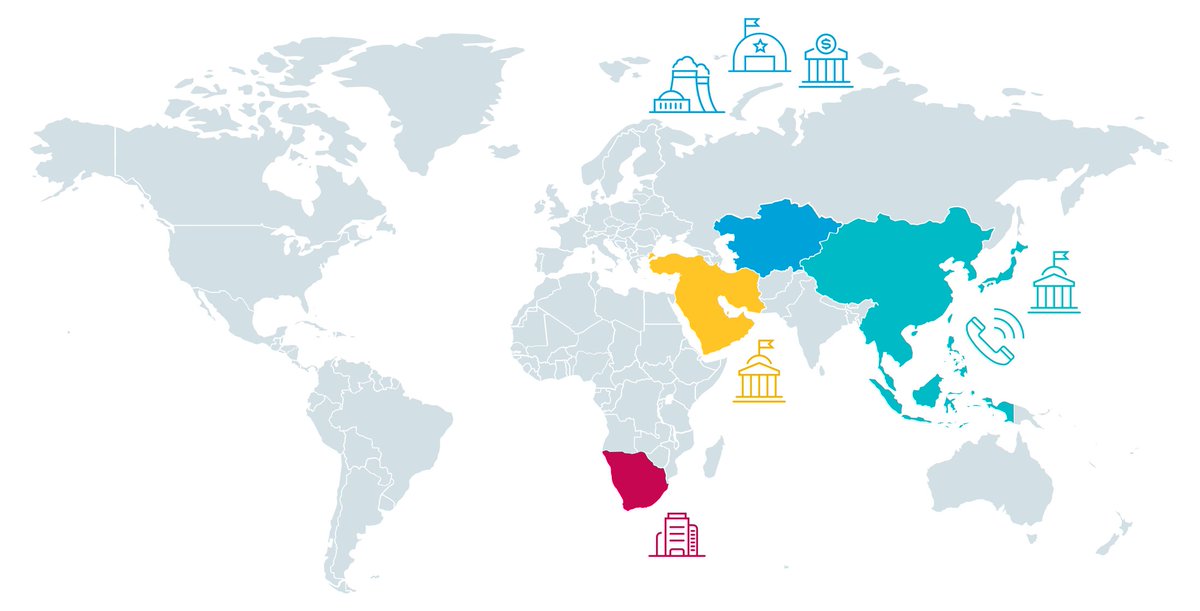
    Worok has used the #ProxyShell vulnerability as first access. According to ESET telemetry, the group has been active since late 2020 and continues to be active in 2022, targeting various sectors such as military and governmental entities, banks and telecommunications. 2/5
    Download
    237
  16. Show more posts