Posts with #LogAnalysis

#LogAnalysis

Public posts on X that use #LogAnalysis.

Related hashtags

  1. Phidlorah@Iam_Mcharo
    So this took me a while... However, as a SOC analyst, I must emphasize the importance of event log analysis. I gained a great deal of knowledge analyzing logs with event viewer@LetsDefendIO #CyberSecurity #loganalysis
    1111470
  2. SANS DFIR@sansforensics
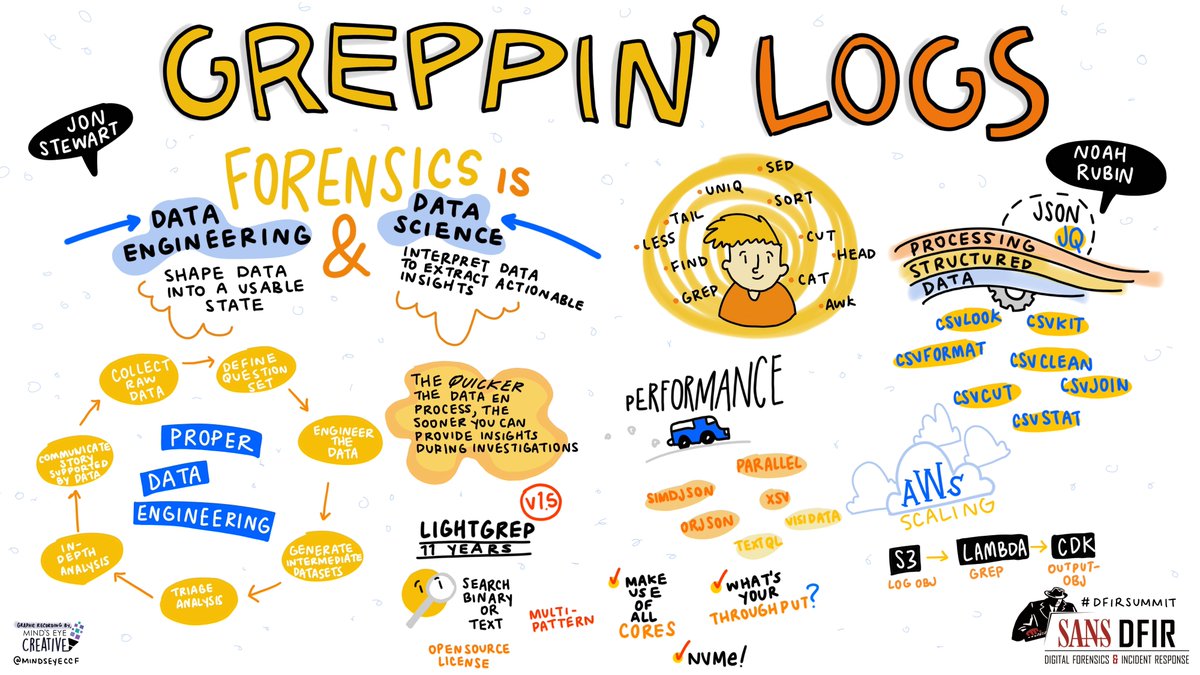
    🚨NEW VIDEO🚨 In their #DFIRSummit talk Jon Stewart and Noah Rubin discuss how to optimize systems for log searching, and cover a variety of command-line tools, including Stroz Friedberg's open source multipattern grep tool, Lightgrep. #DFIR #LogAnalysis
    Download
    037
  3. SANS DFIR@sansforensics
    In their #DFIRSummit talk Jon Stewart and Noah Rubin discuss how to optimize systems for log searching, and cover a variety of command-line tools, including Stroz Friedberg's open source multipattern grep tool, Lightgrep. #DFIR #LogAnalysis
    Download
    0515
  4. Mezmo@mezmodata
    The #LogDNA team has been hard at work creating new features to help you identify and resolve performance issues faster than ever before. Learn about Agent v2, Hourly Archiving, Extract and Aggregate Fields, and Custom Webhooks #logging #loganalysis
    Download
    035
  5. ta_rasul@_Bintuuu
    Week 4 as an intern @HSC_Consult.
This week, we dived into log analysis. Understanding the different log sources (firewall, webserver logs etc), how to interpret entries, and how they help detect suspicious activity in real environments.
#CyberSecurity #SOCAnalyst #LogAnalysis
    Download
    117355
  6. Graylog@graylog2
    TOMORROW 8/24: Join #Graylog #SIEM Engineer David Elgut LIVE at 1pm EST / 6pm BST on David's experience focuses on SIEM tools, SIEM pipeline creation, #loganalysis, log categorization, and in network + systems security. Join here:
    Download
    012
  7. Emerald Udoeyop@emeraald
    Day 39/100; Log Analysis Logs are the silent witnesses of cybersecurity. Today I dug into Windows Event Logs/Apache access logs, tracing suspicious activity from failed logins to POST requests. @ireteeh @segoslavia @comp_guyy #Cybersecurity #LogAnalysis #100DaysOfCyberSecurity
    Download
    Emerald Udoeyop @emeraald
    Day 38/100 #100DaysOfCybersecurity Today I learned how events become incidents, how to prioritize them, and how frameworks like SANS & NIST guide response. Also explored IR tools in a hands-on lab. @ireteeh @segoslavia @comp_guyy #CyberSecurity #IncidentResponse
    017222
  8. elizabeth@elizabe3435891
    Need a parser for your own log format? Drop a .dos file into logParser/projects. Want a custom report or tailored alert email? Same pattern. DDBLogAnalyser is modular—batch, stream, custom logic—all in DolphinDB script, no external pipeline. #DolphinDB #LogAnalysis #Automation
    0001
  9. Emiliano@Emilian40659768
    Log investigations are tedious: manually hunting through files, guessing time ranges, cross-referencing nodes. #DolphinDB's DDBLogAnalyser module automates the whole loop—batch processing, precise time filtering, and report generation. #Observability #LogAnalysis
    0004
  10. haksec.io✓@haksecio
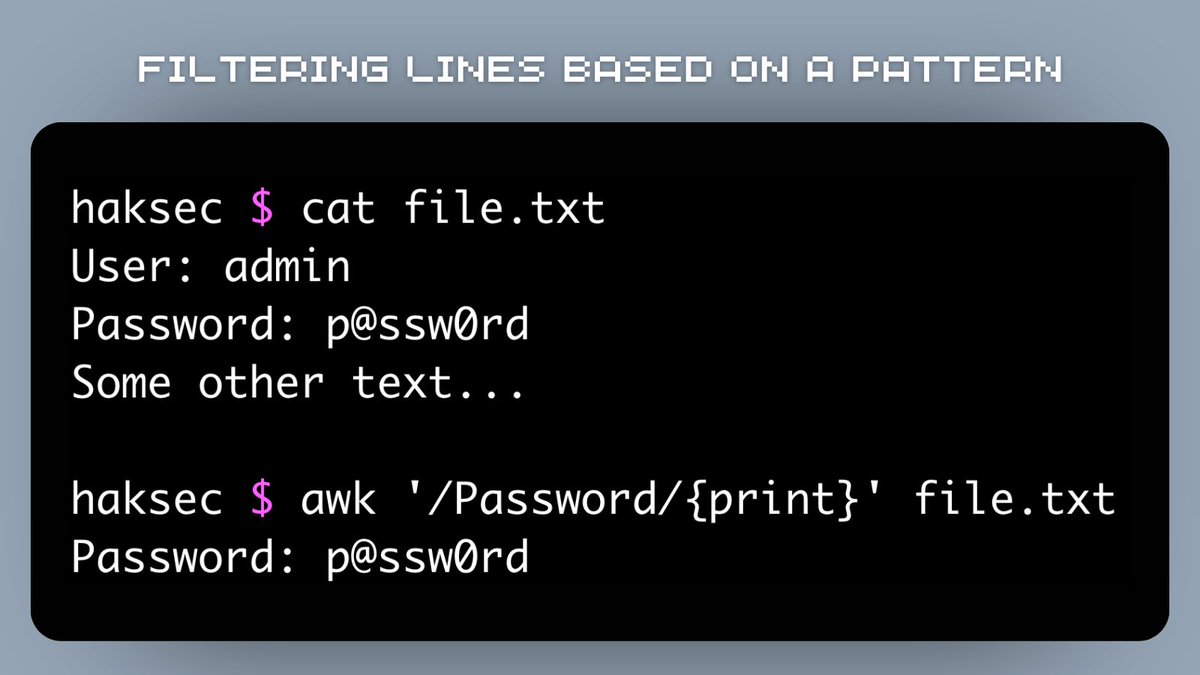
    10 ways to use awk for hackers! 🚀 🧵👇
    Download
    136728243.5K
  11. haksec.io✓@haksecio
    @haksecio
    4️⃣ Modifying a Specific Field Easily replace or anonymize user information in datasets. Safely share data while preserving privacy during penetration testing. #DataAnonymization #PenTesting
    Download
    10111.4K
  12. Graylog@graylog2
    Yes... important to learn #loganalysis‼️😉 #Graylog #logmanagement
    InfoSec Pandey🥷🏻 🇮🇳 🕉️ @InfosecPandey
    Learn Log Analysis: 1. Log management tools – #Splunk, #ELK, and #Graylog to parse, search, and analyze logs. 2. Common log formats – #Syslog, Apache, and Windows Event Logs 3. Study log analysis, parsing, and search techniques 4. Regular expressions (#Regex)
    013653
  13. Aleyda Solis 🕊️✓@aleyda
    7 fundamental technical SEO questions to answer with a log analysis (and how to easily do it) > - my post about #loganalysis from 2 years ago. If you like it, don’t miss the log analysis session tomorrow at #DTDconf 🤖
    1824
  14. SANS DFIR@sansforensics
    In their #DFIRSummit talk Jon Stewart and Noah Rubin discuss how to optimize systems for log searching, and cover a variety of command-line tools, including Stroz Friedberg's open source multipattern grep tool, Lightgrep. #DFIR #LogAnalysis
    Download
    041
  15. Show more posts