Posts with #OpenSSL

#OpenSSL

Public posts on X that use #OpenSSL.

Related hashtags

  1. The Hacker News@TheHackersNews
    ‼️WARNING - OpenSSH issues emergency fix for a critical SSH authentication bypass on Alpine Linux. A password longer than 256 bytes can unlock key-only accounts on affected servers, without knowing the actual credentials. Here's how it works ↓
    3816286674.2K
  2. Jumar Macato✓@jumarmacato
    guess im right to ditch openssh.
    International Cyber Digest @IntCyberDigest
    ‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password. The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours. It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY". Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.
    002145
  3. International Cyber Digest✓@IntCyberDigest
    ‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password. The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours. It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY". Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.
    Download
    622681.7K449K
  4. The Hacker News@TheHackersNews
    @TheHackersNews
    Not every Alpine Linux server is vulnerable. The bypass requires: • SSH password logins enabled • Password checks without PAM • An account with no password set • Another account with a compatible password hash Key-only accounts can be exposed too.
    Download
    15216.8K
  5. The Hacker News@TheHackersNews
    @TheHackersNews
    It gets worse on certain Alpine cloud images. The alpine user has passwordless doas access. If the SSH bypass conditions are met, an attacker can log in as alpine and become root. OpenSSH and Alpine have released fixes. Can't update yet? Set PasswordAuthentication no and restart sshd.
    Download
    0044.9K
  6. mRr3b00t✓@UK_Daniel_Card
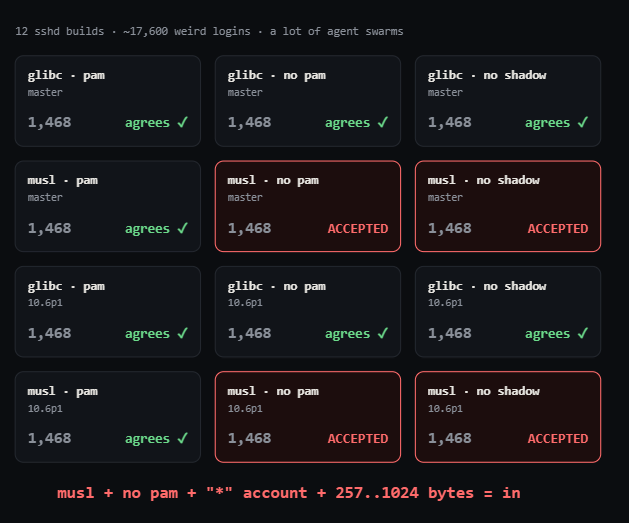
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for a password authentication bypass (related to misinterpretation of whether a string is intended to be a password hash). For some configurations of accounts, any password between 256 and 1024 characters succeeds. An example of a platform using musl libc without PAM is Alpine Linux. Base Score:8.1 HIGH Vector: CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H
    203283
  7. The Cyber Security Hub™✓@TheCyberSecHub
    OpenSSH flaw lets attackers log into password-disabled Linux accounts www.​bleepingcomputer.​com/news/security/openssh-flaw-lets-attackers-log-into-password-disabled-linux-accounts/ #Security #Linux
    Download
    001415
  8. Cyber Security News✓@The_Cyber_News
    ‼️Breaking - OpenSSH Flaw Could Let Attackers Bypass Password Authentication on Alpine Linux Servers Details: A critical OpenSSH password authentication bypass could let remote attackers access affected Alpine Linux servers without knowing a password. Portable OpenSSH 10.6p2, released on November 5, 2026, adds a workaround for the flaw, which affects certain Linux systems using musl libc when PAM support is disabled. Alpine warns that exploitation needs only one connection and no repeated attempts when the required conditions are present. The attacker must know a suitable account name and reach the server’s SSH port. #CybersecurityNews #OpenSSH #AlpineLinux
    Download
    53620013.6K
  9. Mark Karpelès✓@MagicalTux
    New bug in OpenSSH. Security researchers: AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA Anyone with a SSH server accepting password on alpine/etc: AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA Details:
    245135644.9K
  10. ZazenCodes✓@ZazenCodes
    today's OpenSSH vulnerability blew my mind accounts with no password store the hashed field as * if you use any password over 256 characters, it returns * and therefore matches the hash lmao this is an over simplification, but basically true
    Download
    28399.7K
  11. BleepingComputer✓@BleepinComputer
    OpenSSH flaw lets attackers log into password-disabled Linux accounts
    0172.1K
  12. JTCrawford✓@JtCrawford
    OpenSSH 10.6p2 patches a critical vulnerability in infrastructure that secures millions of servers, routers, and defense systems worldwide. Open-source security isn't optional—it's the backbone of digital sovereignty. #CyberSecurity #OpenSource #Infrastructure
    00010
  13. bearstech✓@bearstech
    SSHole : une faille critique dans OpenSSH restée cachée pendant dix ans (via Pierre Arlais) Donc go installer la mise à jour de sécurité OpenSSH 10.6p2. 👉
    Download
    96424024.5K
  14. André Baptista✓@0xacb
    Just reproduced sshole (CVE-2026-123158), beautifully simple bug by @kultekin Needs password auth on and no PAM, but you can ssh as root into an unpatched Alpine box with any 257+ byte password. musl crypt() returns "*" for any password over 256 bytes. a locked account's shadow field is also "*". sshd compares them and they match. fix: openssh 10.6p2
    Download
    11151.2K
  15. Abdullah✓@SMAbdullahAhsan
    OpenSSH just patched a nasty Alpine bug where a long password could land you as root 💀 They shipped the fix the day after finding it.
    International Cyber Digest @IntCyberDigest
    The bug is like a joke. On Alpine Linux, type 257 to 1024 characters of anything and you get root. 💀
    000
  16. International Cyber Digest✓@IntCyberDigest
    The bug is like a joke. On Alpine Linux, type 257 to 1024 characters of anything and you get root. 💀
    Download
    International Cyber Digest @IntCyberDigest
    ‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password. The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours. It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY". Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.
    2299969.3K442K
  17. Daniel Lockyer✓@DanielLockyer
    oh great, ssh on musl linux (alpine etc) accepts any password longer than 256 characters updating to openssh 10.6p2 fixes it and/or disable PasswordAuthentication
    Download
    191723331.4K
  18. Gabe✓@fishjar
    安全研究员披露了潜伏整整十年的 OpenSSH 史诗级认证绕过漏洞(*sshole): 在 Alpine Linux 等基于 musl libc 的系统上,面对一个被 “*” 锁定的无密码账号(比如 root 或仅密钥登录用户),攻击者只要输入任意超过 256 字符的长密码(如 300 个 A),就能直接以该身份登录成功。 荒诞的因果链条闭环了四十年: 1. 1980 年 Unix 将无密码账号的 shadow 哈希设为 “*”; 2. 2012 年 musl libc 为了防崩溃把 crypt() 失败返回值从 NULL 改成 “*”,同时为了防 DoS 把密码截断在 256 字节; 3. 2016 年 OpenSSH 为了防计时攻击引入借 salt 计算机制。 当长密码撞上 musl 的 256 字节上限,crypt() 失败返回 “*”,OpenSSH 拿着它与 shadow 里的 “*” 做字符串比对判定完全匹配,直接放行 root 登录。 漏洞技术报告:
    59325.2K
  19. The Demistificator✓@demistificator1
    Alpine OpenSSH trap: a 257-1024 byte password can log into * accounts when PasswordAuthentication is on and another $5$/$6$ hash exists. Update openssh AND restart sshd (apk alone is not enough). #OpenSSH #AlpineLinux
    10012
  20. HSVSphere✓@HSVSphere
    This is caused by many, many things, but the primary issue is OpenSSH being an overfeatured piece of crap. Other issues also exist, like the OS using a single field of config for too many things and general incompetency. But I think it's time to replace OpenSSH with something significatly simpler & with forced integration rather than 999999 configurable options.
    Frank @jedisct1
    sshole: openssh on musl linux accepts any password longer than 256 characters.
    82541.7K
  21. Frank✓@jedisct1
    sshole: openssh on musl linux accepts any password longer than 256 characters.
    186754347.9K
  22. Show more posts