Posts with #SQLmap

#SQLmap

Public posts on X that use #SQLmap.

Related hashtags

  1. Hackviser@hackviserr
    Top SQLMap Commands 💉 Here is your essential cheat sheet for the most common SQLMap commands, from detecting injections to dumping databases. ⭐️ Save this post for your next web pentest or bug bounty hunt! 👇 What's your most-used command? Share it below! #sqlmap #cybersecurity #pentesting #bugbountytips
    Download
    18572K
  2. Bug Bounty Village@bugbountyvillag
    We are elated to share that Author & maintainer of @sqlmap, Miroslav Stampar (@stamparm) will be providing a training on "SQLmap for the masses & Unveiling the art of database exploitation" in Bug Bounty village @seasides_conf 2023 Register here : #SQLmap
    Download
    521555.1K
  3. valeria lenoir✓@VLenoir13937
    No siempre necesitas escanear más rápido. Con Nmap y SQLmap también importa saber regular la intensidad de tus pruebas. Hoy vemos cómo ajustar sus parámetros, cuidar los recursos del sistema y realizar auditorías más controladas. #Nmap #SQLmap #Ciberseguridad
    Download
    15261K
  4. N$🌟✓@__nav1n_
    Make sure to test mobile endpoints, not just mobile apps—test Mobile front-ends often run on separate infra, different WAF policies with different code base for huge sites like gaming/chat etc, hiding unique vuln surfaces...#BugBounty #SQLi #SQLMap [1/n]
    Download
    61727615.6K
  5. Seasides@seasides_conf
    We are elated to share that Author & maintainer of @sqlmap, Miroslav Stampar (@stamparm) will be providing a training on "SQLmap for the masses & Unveiling the art of database exploitation" in Bug Bounty village at #Seasides2023 Register here : #SQLmap
    Download
    428511.4K
  6. Hacking Space 📡@hackingspace
    SQLMap AI v2.0.0 is now live on PyPI Multiple AI providers (Groq, OpenAI, Anthropic, Ollama) Adaptive testing WAF bypass capabilities Enhanced reporting & analysis Install: pip install sqlmap-ai GitHub: #cybersecurity #sqlmap #AI #infosec
    110373.4K
  7. N$🌟✓@__nav1n_
    Guys, looking for a #help in #SQLInjection please. I have this SQL error in "ThinkPHP V5.0.24" and the SQLSTATE[42S22] debug info discloses everything about database, however I'm not able to exploit it in #SQLMAP. Can I get a help please? Thank you in advance :) #BugBounty
    Download
    798319.9K
  8. Cybrary@cybraryIT
    Tutorial- How to Use #SQLMAP by Cybrarian Kevin Mark. Learn the basics and discover the many ways you can use this tool. It’s not only PHP based. This is for ASP, ASPX, you name it>
    Download
    058
  9. Raunak Parmar@trouble1_raunak
    Sometimes #sqlmap is not able to extract data for you So try to get it manually Time-based Blind SQLi #Microsoft #MSSQL #manually ?name=USERNAME; if ASCII(LOWER(SUBSTRING((select top 1 password from users where username='admin'),1,1)))=116 waitfor delay '00:00:05'-- -
    12384
  10. zh4ck@zh4ck
    #SQLmap protip: add --suffix=“-- “ to the CLI parameters, and it will find and exploit SQLi like never before (MySQL in this case). I probably should create a new payload though, but this was a dirty fix
    234107
  11. N$🌟✓@__nav1n_
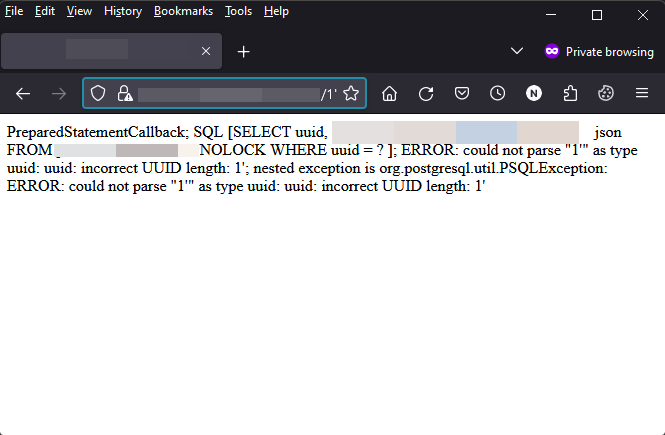
    Do you guys think this could be a hint to an SQL injection, or is it just an incorrect length in the UUID error? Any special character within the URI throws this error. Both SQLMap and Ghauri have failed. #BugBounty #SQLMap
    Download
    171321833.7K
  12. N$🌟✓@__nav1n_
    Hello #SQLMap masters out there, I need a help please. Is there anyway I could bypass this stupid status-code 500?, I tried "--ignore-code 500" but didn't help, anyone please? #BugBounty
    Download
    92016127.9K
  13. Show more posts