Posts with #credential

#credential

Public posts on X that use #credential.

Related hashtags

  1. Grant Smith Ellis✓@GrantSmithEllis
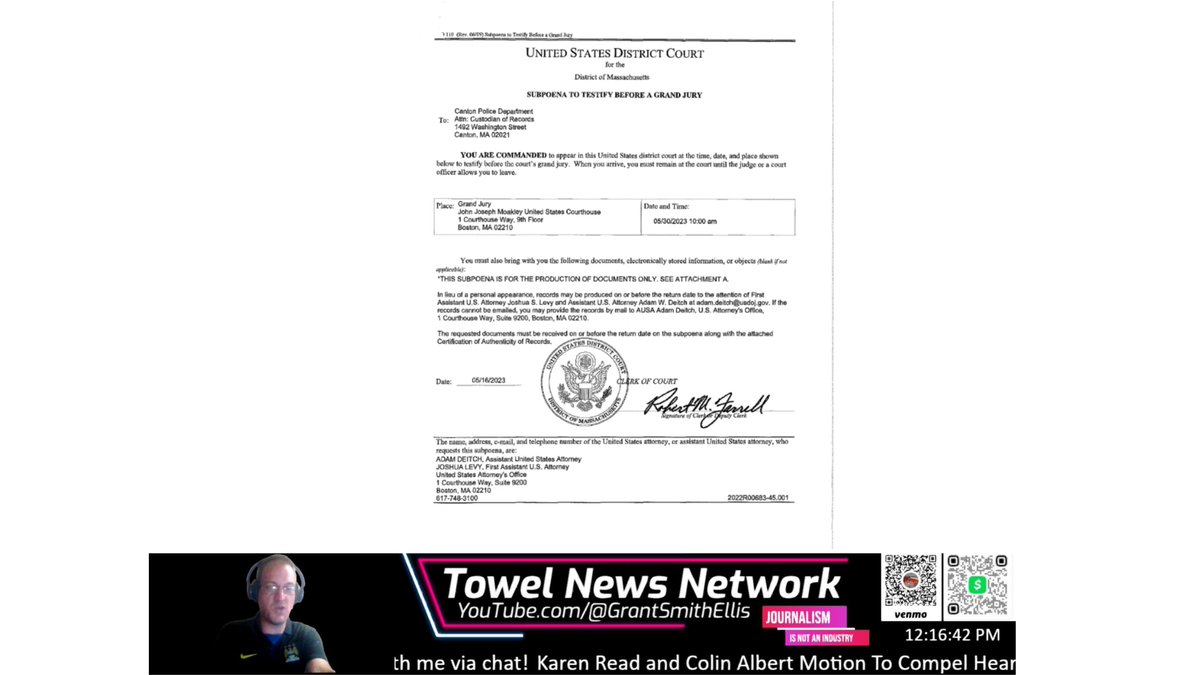
    BREAKING: For the first time, due to the incredible efforts @TheEmilySee and the FOIA And Find Out Team, the federal grand jury subpoena sent to the Canton Police Department in the context of the DOJ's investigation of the (still-unsolved) death of John O'Keefe has been revealed. The document, sent in May of 2023, reads as follows; UNITED STATES DISTRICT COURT for the District of Massachusetts SUBPOENA TO TESTIFY BEFORE A GRAND JURY Canton Police Department To: Attn: Custodian of Records 1492 Washington Street Canton, MA 02021 YOU ARE COMMANDED to appear in this United States district court at the time, date, and place shown below to testify before the court's grand jury. When you arrive, you must remain at the court until the judge or a court officer allows you to leave. Place: Grand Jury John Joseph Moakley United States Courthouse 1 Courthouse Way, 9th Floor Boston, MA 02210 Date and Time: 05/30/2023 10:00 am You must also bring with you the following documents, electronically stored information, or objects (blank if not applicable): *THIS SUBPOENA IS FOR THE PRODUCTION OF DOCUMENTS ONLY. SEE ATTACHMENT A. In lieu of a personal appearance, records may be produced on or before the return date to the attention of First Assistant U.S. Attorney Joshua S. Levy and Assistant U.S. Attorney Adam W. Deitch at adam.deitch@usdoj.gov. If the records cannot be emailed, you may provide the records by mail to AUSA Adam Deitch, U.S. Attorney's Office, 1 Courthouse Way, Suite 9200, Boston, MA 02210. The requested documents must be received on or before the return date on the subpoena along with the attached Certification of Authenticity of Records. Date: 05/16/2023 CLERK OF COURT Signature of Clerk or Deputy Clerk The name, address, e-mail, and telephone number of the United States attorney, or assistant United States attorney, who requests this subpoena, are: ADAM DEITCH, Assistant United States Attorney JOSHUA LEVY, First Assistant U.S. Attorney United States Attorney's Office 1 Courthouse Way, Suite 9200 Boston, MA 02210 617-748-3100 2022R00683-45.001 ATTACHMENT A Canton Police Department Attn: Custodian of Records 1492 Washington Street Canton, MA Produce any and all records described below: For the purposes of this subpoena, "Records" include police reports, incident reports (including drafts), narratives, notes, internal memoranda (including drafts), investigative materials, witness interviews, communication records (including emails, text messages, voice mails, instant messages, phone records, printouts of radio, email, telephone or cell phone communication), audio/video recordings, and any other tangible material memorializing the above. 1. Any and all retained video surveillance footage or still images from the Canton Police Department for the date of 1/29/2022. 2. Building access logs for the date of 1/29/2022, including but not limited to key card, key fob, or coded access and any interpretive data identifying assignments to individual users. 3. Attendance and duty rosters, roll calls, visitor/civilian logs, and related documents for the dates of 1/28/2022 and 1/29/2022, including but not limited to shift start and end times, individual assignments, on-call schedules, off-duty members called in, visitor/civilian/staff/guests logs, overtime pay records, and any other records memorializing the identities of individuals who entered and/or exited the Canton Police Department and associated times. 4. Any agreements, memoranda, mutual aid, policies, or task force assignments involving agent(s) of the Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF). 5. Any administrative, physical security, or related requests or requirements for space assigned to or used by ATF and/or task force(s), including but not limited to specific agents and/or task force officers, including lists of any database credentials or equipment assigned to or used by ATF and/or task force(s). 6. Any and all records relating to internal/external law enforcement database/system queries made on 1/29/2022, including but not limited to the identity of the employee who generated the queries, records supporting the use of each query, and any recorded purpose or justification for the queries. 7. Any and all reports, call/dispatch logs, and related records for activity at 34 Fairview Road, Canton from 1/1/2013 to present. 8. Any and all records related to the investigation of the death of John O'Keefe, including but not limited to the full investigative case file for Canton Police Department (incident number 22-87-0F, call number 22-449) and records generated by and on file from the Massachusetts State Police (case number 2022112-033), all communications, reports, statements, evidence, or property tracking, photographs, recorded telephone lines or radio transmissions, complete dispatch logs, including all notes and follow up entries, recusal of Canton Police or any of its members a. Including any and all records of communications to/from the following individuals from 1/29/2022 to present; as well as any Originating Agency Identification (ORI) numbers/codes or internal/external law enforcement database account usernames used by or assigned to the following individuals: i. ATF Special Agent Brian Higgins ii. Former Chief Ken Berkowitz iii. Thomas Keleher iv. Kevin Albert v. Michael Lank b. In specific regard to Canton Police Department full investigative case file, any and all records reflecting access to all police reports, including but not limited to: the identities of the employees who authored, viewed, collaborated, modified, approved, and accessed each report, dates and times of accesses, and the recorded purpose or justification for said accesses (if any). For any changes that were made, the substance of the changes made and copies of all draft reports. Any and all records relating to interactions between any officer, former employee, or current employee of the Canton Police Department and the following individuals, from 1/29/2022 to present: a. Brian Albert Sr. b. Nicole Albert c. Brian Higgins d. Jennifer McCabe e. Matthew McCabe f. John O'Keefe g. Karen Read h. Julie Nagel i. Sarah Levinson j. Brian Albert Jr. k. Colin Albert l. Kerry Roberts m. Caitlin Albert n. Tristin Morris In lieu of a personal appearance, records may be produced on or before the return date to the attention of First Assistant U.S. Attorney Joshua S. Levy and Assistant U.S. Attorney Adam W. Deitch at adam.deitch@usdoj.gov and copy michael.petow@usdoj.gov. If the records cannot be emailed, you may provide the records by mail to AUSA Adam Deitch, U.S. Attorney's Office, 1 Courthouse Way, Suite 9200, Boston, MA 02210. Source document -
    Download
    761471.1K130K
  2. Cyber Security News✓@The_Cyber_News
    ‼️ Hackers Begin Exploiting OpenSSH SSHole Authentication Bypass Vulnerability Details: Attackers have started targeting the SSHole authentication bypass affecting certain OpenSSH servers, according to new SANS Internet Storm Center findings. The flaw allows remote attackers to access some password-disabled Linux accounts by submitting an unusually long password, without knowing valid credentials or holding an SSH key. SANS researcher Johannes Ullrich reported the first clear exploit attempts on November 5, using passwords made entirely of repeated “A” characters. His Cowrie SSH honeypots recorded 232 long-password requests that day, followed by 713 on November 6. #CybersecurityNews
    Download
    6421499.2K
  3. The Hacker News@TheHackersNews
    🚨 Five cyber threats targeting US businesses. Microsoft 365 device-code phishing, fake AI apps stealing credentials, and malware disabling Microsoft Defender. Inside the SkyW4lker, Mir0Auth, GeorgeGinx, and WKLP campaigns. See how the attacks work and what to watch for ↓
    Download
    22266824K
  4. Cyber Security News✓@The_Cyber_News
    ‼️ Hackers Use Stolen Microsoft Entra ID and Azure DevOps Credentials to Access 27 Organizations Details: Hackers are abusing stolen Microsoft Entra ID application credentials and Azure DevOps identities to access Microsoft 365 and Azure environments, reaching at least 27 organizations. The ongoing campaign has been targeting managed service providers (MSPs) and their customers since November 1, 2026. The operator targeted about 45 app registrations across roughly 18 organizations, with more than 33 authenticating successfully. The attacker also used an Azure DevOps federated workload identity and replayed user session tokens. #cybersecuritynews
    Download
    117723225.2K
  5. Lock O’Clock@TheLockAgenda
    Lmfao Jeremiah Smith just retweeted this. Your credentials are getting pulled you sick freak @Birm
    LeCharles Bentley @64AMDG
    Jeremiah has been EVERYTHING countercultural to today’s superstar CFB player. He’s established a new standard of individual excellence on and off the field at OSU. Literally everything fans claim they want in a player. Yet the moment he expresses something honest outside of his ability to play football, his maturity gets questioned. Suddenly, he’s a “petulant child”? Nah. You can disagree with a young man without questioning his character or maturity. The irony here, instead of articulating a salient point, the reporter resorts to name-calling…. Like a child. Leadership isn’t about making everyone comfortable. #GoBucks🌰
    92370732K
  6. LeCharles Bentley✓@64AMDG
    Jeremiah has been EVERYTHING countercultural to today’s superstar CFB player. He’s established a new standard of individual excellence on and off the field at OSU. Literally everything fans claim they want in a player. Yet the moment he expresses something honest outside of his ability to play football, his maturity gets questioned. Suddenly, he’s a “petulant child”? Nah. You can disagree with a young man without questioning his character or maturity. The irony here, instead of articulating a salient point, the reporter resorts to name-calling…. Like a child. Leadership isn’t about making everyone comfortable. #GoBucks🌰
    2916975.2K316K
  7. Cyber Security News✓@The_Cyber_News
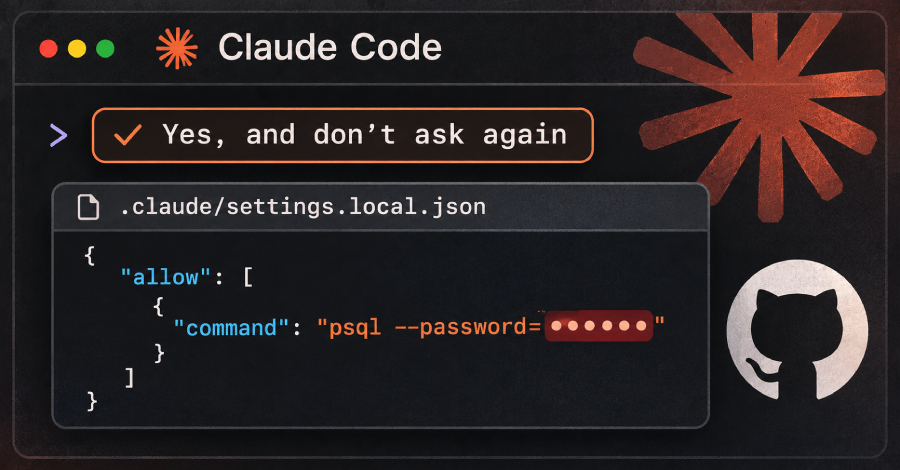
    ‼️ Claude Code’s “Yes, and Don’t Ask Again” Option Can Leak Passwords and API Keys to GitHub Details: Claude Code’s “Yes, and don’t ask again” option can save passwords and API keys inside project settings that later reach public GitHub repositories. Researchers found 2,539 distinct secrets across 1,994 public repositories, showing how a routine approval can turn private credentials into public data. The research identified 63 affected organizations, mostly software companies. Exposed credentials included a database vendor’s admin-level cloud key, a production Azure PostgreSQL password, a Square production token, and the owner password for a medical-records database. Apiiro said one company confirmed its exposed key had been live. #cybersecurityNews
    Download
    145521992.3K
  8. PaulBarron✓@paulbarron
    Chainalysis just admitted ALL of its users had names, usernames, password hashes and live tokens exposed. On Oct 30 it said credentials weren't touched. It serves 1,500+ customers, including law enforcement. The AML watchdog is itself down.
    Download
    9136210.4K
  9. Peter Bernegger✓@PeterBernegger
    🚨Stunning City of Milwaukee Spring Election manual shows passwords! It shares laptop credentials and an ExpressVote access code. It has instructions for changing voter records: showing staff how to: 1) correct records 2) register voters 3) cancel absentee ballots 4) and deactivate applications. -Those are powers that deserve access restrictions and audit review - but there are none!! -Pages 41–48 direct staff to deactivate certain continuing absentee applications when replacing a mailed ballot with an in-person ballot. What is going on? -No clear response to a broken or mismatched equipment seal. Pages 5–6 require daily verification of ExpressVote seal numbers, but do not specify whether staff must stop using the machine, isolate it, preserve evidence, or obtain clearance before restarting it. Checking a seal needs an explicit response when the check fails. -Incomplete accounting for unused and spoiled ballots. Blank ballot cards and curbside ballots are distributed and stored, but the manual does not clearly require a daily inventory balancing ballots received, issued, spoiled, and remaining. Page 42 mentions a discarded-ballot envelope without explaining its reconciliation or subsequent custody. -Limited independent review of sensitive record changes. Pages 15 and 41–48 describe corrections, cancellations, and application deactivations. Some procedures involve chiefs or specialists, but the manual does not establish a consistent second-person review or daily examination of transaction logs. -Unclear handling of defective envelopes awaiting a voter’s return. Page 37 says to retain an envelope missing the voter’s signature so the voter can return. It does not specify a separate secured location, tracking log, custody record, or reconciliation when the envelope is corrected or remains unresolved. -Network and workstation protections are unexplained. Page 3 directs staff to use password-free library Wi-Fi and ignore Global Protect pop-ups. That deserves clarification about the intended network protection. The manual also does not specify automatic screen locking or what workers must do when leaving a workstation temporarily. -Manual ballot substitution lacks a documented verification step. Page 36 permits a “sister ward” ballot when the correct curbside ballot is unavailable, followed by reconstruction at Central Count. It references a matching guide, but does not explicitly require an independent check of the substitute ballot or a substitution log. Who wrote this manual?? Manual obtained by Patriot - but handed out like candy to countless election people. Our elections are complete garbage! @DonMillis @BobSpindell @MayorMKE @cityofmilwaukee @JayWeber3 @VickiMcKenna @DanODonnellShow @EmeraldRobinson @AGToddBlanche @AAGDhillon @realDonaldTrump @JanelBrandtjen @DanEastman2023 @WisGOP @WisGOP7 @wisgop6 @RepDaveMaxey @RepKrug @skrug75 @WisFOIC @JayForWisconsin @TomTiffanyWI @TiffanyWarRoom @EricJToney @Gina4WIAssembly Read it for yourself, all 48 pages are at the link here: First page:
    Download
    2283K4.1K91.3K
  10. The Hacker News@TheHackersNews
    ‼️WARNING - OpenSSH issues emergency fix for a critical SSH authentication bypass on Alpine Linux. A password longer than 256 bytes can unlock key-only accounts on affected servers, without knowing the actual credentials. Here's how it works ↓
    886643.2K889K
  11. The Hacker News@TheHackersNews
    ‼️ Claude Code's "Don't Ask Again" option can save passwords and API keys in plaintext. Apiiro found 2,539 exposed secrets across 1,994 public GitHub repos, including database credentials, SSH logins, and cloud keys. Deleting files doesn't erase Git history. Read:
    Download
    808937670.8K
  12. Cyber Security News✓@The_Cyber_News
    ‼️ North Korean Hackers Abuse Internal AI Tool and Fake Job Interviews in $6.34 Billion Binance Heist Details: North Korean hackers used a fake job interview, a poisoned coding task, and a hijacked internal AI tool to reach Binance's wallet systems. The FBI says the North Korean group it calls "TraderTraitor" stole more than $6 billion in digital assets on 29 October 2026. Binance puts the impacted value at about USD 6.34 billion. Binance says this was a multi-stage campaign and not a simple phishing case. In June 2026, a wallet DevOps engineer searched online for an AI coding tool and installed a tampered Homebrew package. Binance replaced the device and rotated credentials, but the attacker had already learned who worked on wallet infrastructure. #cybersecurityNews
    Download
    728818.9K
  13. Cyber Security News✓@The_Cyber_News
    🚨 Hackers Launch LLMHijacking Attacks, Leaving Companies With $1 Million in Cloud Bills Details: Hackers are stealing access to corporate large language models and reselling it, leaving victims with cloud bills reaching $1 million. Mandiant investigated multiple incidents during 2026 where unauthorized AI use generated more than $100,000 in charges in a single day, showing how quickly stolen credentials can become a major financial loss. The attacks affected financial services, retail, technology, and transportation organizations across North America, South America, and Asia Pacific. Known as LLMJacking, the technique targets paid AI resources rather than using stolen computing power to mine cryptocurrency. #cybersecurityNews
    Download
    722627K
  14. Dark Web Informer@DarkWebInformer
    🚨 Hackers Breach at Least 27 Organizations Using Stolen Microsoft Entra ID and Azure DevOps Credentials An ongoing cyberattack campaign has compromised cloud environments belonging to at least 27 organizations, with attackers abusing stolen Microsoft Entra ID application credentials and Azure DevOps identities to gain access to Microsoft 365 and Azure resources. According to security researchers at Todyl, the campaign began on November 1, targeting managed service providers (MSPs) and their customers across government, energy, transportation, education, legal, and other sectors. Investigators have identified extensive unauthorized activity, including: • 27 organizations affected • 45 application registrations targeted • 33+ successful application authentications • Approximately 2,279 mailbox items accessed • 81 files downloaded from compromised environments • One application used to access 15 customer tenants Stolen information included password lists, private keys, VPN configurations, backup credentials, and remote access settings, raising concerns about additional compromises. Attackers were able to impersonate trusted applications and access cloud resources without triggering traditional user MFA challenges. No Microsoft vulnerability was exploited. Attack Details • Initial activity: November 1, 2026 • Targeted platforms: Microsoft Entra ID, Azure DevOps, Microsoft 365 • Attack method: Stolen application credentials and session token abuse • Confirmed source IP: 199[.]19[.]77[.]84 • Attribution: Unknown • Status: Ongoing investigation Organizations are advised to investigate unusual service principal activity, revoke compromised credentials, rotate exposed secrets, and review third-party application permissions.
    Download
    136331442.1K
  15. The Hacker News@TheHackersNews
    🚨 CISA adds SonicWall SonicOS MFA bypass flaw to its Known Exploited Vulnerabilities catalog. CVE-2026-19868 could bypass SAML authentication and MFA using valid alternate credentials. SonicWall is investigating a report of possible exploitation. Details ↓
    Download
    25287424.2K
  16. DOW Rapid Response✓@DOWResponse
    .@SECWAR “Consequently, the primary task of our Senior Service Colleges cannot be the passive transmission of credentials. It cannot be the curation of an insulated salon for intellectual leisure. It must be—teaching victory. The deliberate, uncompromising task of forging senior military leaders who are intellectually, ethically, and operationally prepared to decisively deter but necessarily defeat our enemies in unforgiving combat.”
    Download
    1412154928K
  17. Hawk✓@HawkIcanNfl
    Listen to the guys that have credentials and have true relationships with the university. Guys that actually wants to see the university win and return to glory. One of the best in the business. Tune in to @InTheGunPodcast
    Schuyler Callihan @Callihan_
    MAILBAG: Mike Hawkins' future, tampering, social media meltdown, Alley outlook + more #WVU S/o @jimmywvu717, @JordanWVU07, @DMcCune10, @Jeremia62776484, @mediocrebearfan, @CoachKMcG, @MrEd315, @Dalandow212, @wvufan2023, @Trey_Ebc11, @greathouse76185
    585278326.6K
  18. Garry Tan✓@garrytan
    Hosted GBrain now solves one of the biggest issues with credentials in company brains: making sure you have access to yours but not other people’s without their permission
    GBrain @gbrainio
    The shared AI brain only works if your inbox stays yours. GBrain Teams now asks you before a teammate's AI touches any account you connected.
    371025037.6K
  19. GBrain✓@gbrainio
    The shared AI brain only works if your inbox stays yours. GBrain Teams now asks you before a teammate's AI touches any account you connected.
    202934.3K
  20. Cybernews✓@Cybernews
    Attackers may exploit the bug without user clicks, credentials, or authentication. More:
    Download
    46312.5K
  21. VECERT Analyzer✓@VECERTRadar
    ⚠️ 🇪🇨 🏦 🗄️ ALERT/PREVENTION – UPDATE REGARDING ALLEGED INTRUSION AND DATA EXFILTRATION AT BANCO PICHINCHA (ECUADOR) [STATUS: ALLEGED / ONGOING / THREAT ACTORS: TEAM PHEISITO, TEAM CURIRICA, WHITE LOTUS / DATE: NOVEMBER 10, 2026] Centralized cyber-intelligence systems have intercepted an update and official statement on underground forums (recorded on November 10, 2026) disseminated by the actor "Pheisito"—representing Team Pheisito and Team Curirica—with the involvement of the operator "White Lotus" (identified as the party responsible for the initial intrusion into the institution). The report confirms the alleged continuation of operations against Banco Pichincha in Ecuador, indicating that the data will be released progressively or offered for sale. The attackers justify their campaign by citing grievances against the institution’s policies—drawing parallels to previous incidents, such as the hack of Diners—and insist that their target is the banking infrastructure, not the end users. As evidence, they have provided links to video platforms (Dailymotion) containing material that purportedly proves unauthorized access. It is strongly cautioned that the veracity of this update, the actual impact on the banking institution’s servers, and the overall authenticity of the data repositories have not been officially confirmed by Banco Pichincha or the regulatory authorities in Ecuador. Threat Actors: Team Pheisito, Team Curirica, White Lotus (Pheisito). Victim : Banco Pichincha — 🇪🇨 Ecuador. Sector: 🏦 Banking, Financial, Private Banking, and Monetary Infrastructure. Publication Date: November 10, 2026. 🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / PRIVATE BANKING) Audit and Hardening of Banking Perimeters: Banco Pichincha’s information security teams must maintain active surveillance of access logs, corporate gateways, and database systems to mitigate any persistent presence by the threat actor "White Lotus." Monitoring of Clandestine Channels: Track Telegram links and posts by "Team Pheisito" to analyze released data samples and anticipate the potential exposure of credentials or sensitive information. Protection and Early Warning: Coordinate with fraud teams to prevent social engineering or extortion campaigns targeting customers that may leverage the institution's name. 🖥️ Centralized Threat Monitoring System Intelligence System: Quickly verify your security at: Inquiries and services: #Ecuador #BancoPichincha #TeamPheisito #WhiteLotus #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
    Download
    925826.4K
  22. Show more posts