gabriel shapiro✓

@lex_node

attorney practicing cybernetic law @MetaLeX_Labs past: BigLaw Buyside Tech M&A (Weil, Hogan Lovells), @Delphi_Labs GC, @BrownUniversity $ETH / $GOR barbell

8.3K Following78.4K Followers79.9K Posts
  1. gabriel shapiro✓@lex_node
    As a corporate lawyer, I've been incorporating companies for 17 years, & it's a mess. Somehow we really got robots & AI before a halfway decent startup app. So I built it myself--oneshot formation, cap table, governance and onchain identity for your startup today.
    MetaLeX @MetaLeX_Labs
    603631851.9K
  2. MetaLeX✓@MetaLeX_Labs
    365049.8K
  3. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @neuralunlock: This was coming. Most of the winning infra (especially at the L1 / L2) has already been built out and you no longer need megafunds for the crypto app layer. There aren’t too many spots for $50M - $100M rounds. For the pure play crypto projects, you’ll see a lot more from: - smaller crypto VC funds funding pre-seed / seed - onchain capital formation through platforms like MetaDAO Crypto still has bright spots ahead but the funding landscape has changed.
    zoomer @zoomerfied
    [ ZOOMER ] A16Z TO DROP CRYPTO FROM ITS FLAGSHIP BLOCKCHAIN FUND'S NAME, FOCUS ON OTHER INVESTMENTS, ITS FIRST FOUNDING MEMBER TO ALSO LEAVE: THE INFORMATION
    020332
  4. zoomer✓@zoomerfied
    [ ZOOMER ] A16Z TO DROP CRYPTO FROM ITS FLAGSHIP BLOCKCHAIN FUND'S NAME, FOCUS ON OTHER INVESTMENTS, ITS FIRST FOUNDING MEMBER TO ALSO LEAVE: THE INFORMATION
    2481321.8K676K
  5. gabriel shapiro✓@lex_node
    "my agent went rogue" is the new "my dog ate my homework"
    9127843
  6. gabriel shapiro✓@lex_node
    "nooo honey I didn't buy onlyfans that was some rogue agent!!!"
    Madison Mills @MadisonMills22
    SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios. The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios. Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said. Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior. Read my latest for Axios here:
    2214824
  7. Madison Mills✓@MadisonMills22
    SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios. The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios. Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said. Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior. Read my latest for Axios here:
    1.4K6.9K19.1K9.1M
  8. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @binji_x: A case for decentralization: The same authority that lets you fix a system can also become the means by which an attacker compromises it. Social blackmail-driven hacks can become more common than pure software hacks after some time, especially if data leaks keep occurring.
    010292
  9. gabriel shapiro✓@lex_node
    100 year ethereum hash-based dynasty lfg
    Laura Shin @laurashin
    Project Eleven co-founder Alex Pruden on why Justin Drake and Yehuda Lindell take different approaches to the quantum threat "Justin's concern is thinking about the longevity of Ethereum over 50 to 100 years. People who lived through the ETH1 to ETH2 transition remember how painfully long that took and how difficult it was." "These are decentralized systems. It is very, very difficult to upgrade them. This is not like your phone upgrades and OS kind of thing." "We need to minimize any kind of possible theoretical risk that might exist in the future. Therefore, we need to do hashes. That's, I think, Justin's perspective. I mean, that's very valid." "On the flip side, Yehuda, responsible as the chief cryptographer at Coinbase for billions of dollars right now. At this second, his name on the line." "So can understand why he's maybe got the view that maybe we shouldn't throw away the only thing that we know has worked right now and go into bunker. And I think there's elements of truth to both."
    21171.5K
  10. Laura Shin✓@laurashin
    Project Eleven co-founder Alex Pruden on why Justin Drake and Yehuda Lindell take different approaches to the quantum threat "Justin's concern is thinking about the longevity of Ethereum over 50 to 100 years. People who lived through the ETH1 to ETH2 transition remember how painfully long that took and how difficult it was." "These are decentralized systems. It is very, very difficult to upgrade them. This is not like your phone upgrades and OS kind of thing." "We need to minimize any kind of possible theoretical risk that might exist in the future. Therefore, we need to do hashes. That's, I think, Justin's perspective. I mean, that's very valid." "On the flip side, Yehuda, responsible as the chief cryptographer at Coinbase for billions of dollars right now. At this second, his name on the line." "So can understand why he's maybe got the view that maybe we shouldn't throw away the only thing that we know has worked right now and go into bunker. And I think there's elements of truth to both."
    Download
    31127.6K
  11. gabriel shapiro✓@lex_node
    people mad that a blockchain company is trying to . . . *checks notes*. . . sell blockchain extensions to as many companies as possible lol
    82283.2K
  12. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @binji_x: Blockchain teams that have cut corners in the name of user acquisitions by centralizing their technologies are ironically the most prone to lose users as the security tradeoffs they have made are too great, and this is not the age to FAFO with security.
    090525
  13. gabriel shapiro✓@lex_node
    not sure why this is getting so much criticism I actually agree a mass "company town" model is a plausible & desirable outcome for corporate finance/governance onchain Ofc, it only makes sense if the company towns are "real" L2s; Stage 2 should remain a standard
    Optimism @Optimism
    Just like every company has its own server now, soon every company will have its own blockchain. @jinglejamOP explains:
    151423.4K
  14. Optimism@Optimism
    Just like every company has its own server now, soon every company will have its own blockchain. @jinglejamOP explains:
    Download
    341819839.1K
  15. gabriel shapiro✓@lex_node
    have been doing personal training sessions in my home gym...normal trainer was sick and training company sent a woman.....my latina gf would not even let her in the building lol...
    3301399.1K
  16. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @johnjanuszczak: Sovereign issuers will only tolerate self-governed rails or neutral commons. @lex_node analyzes corporate tokenization dynamics, asserting that genuine native equity tokenization will occur either on the neutral, permissionless Ethereum mainnet (the Commons) or on enterprise-controlled Layer-2 appchains (the Company Town). Why it matters: Corporate issuers will never entrust their core cap tables and legal governance to third-party intermediary blockchains. Builders must structure enterprise tokenization rails that respect corporate sovereignty while retaining permissionless settlement. My take: Any tokenization architecture that introduces intermediary rent-seeking may be destined for obsolescence. @malekanoms tweeted on exactly this recently. Fyi I curate, expand on, and share my take on informative content like this in my weekly Signals:
    gabriel shapiro @lex_node
    Tokenized stock volume is almost all broker IOUs on broker chains. Companies tokenizing their own shares will not do it that way. They will use Ethereum mainnet (the commons), or an L2 they run themselves--a "company town" with a guaranteed open-gate.
    040659
  17. gabriel shapiro✓@lex_node
    Tokenized stock volume is almost all broker IOUs on broker chains. Companies tokenizing their own shares will not do it that way. They will use Ethereum mainnet (the commons), or an L2 they run themselves--a "company town" with a guaranteed open-gate.
    652719222.4K
  18. gabriel shapiro✓@lex_node
    gabriel shapiro
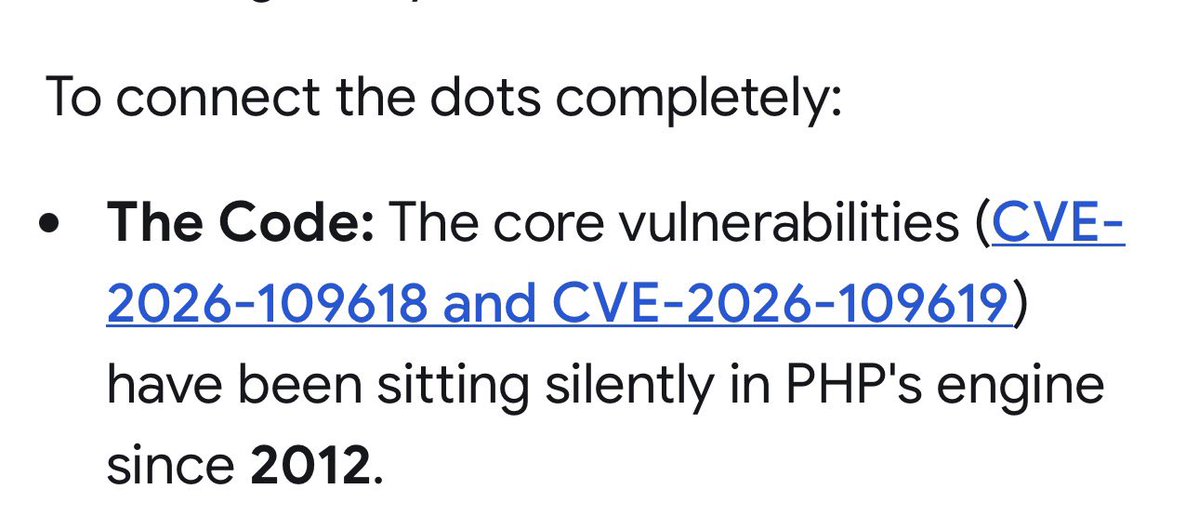
    RT @Hannibal9972485: You know whats interesting is that fact that OpenAI found the PHP bug that means their AI was doing systematic auditing. 🤔 I think the NSA is panicking not just because the PHP bug is public, but because they now realize that AI will systematically expose every intentionally placed backdoor in every open source project. The xz Utils case was caught by human luck. The PHP case was caught by AI. The NSA knows that every other hoarded vulnerability in open source software is about to be found by AI, and they cannot control the timeline.🚨🚨 This incident is very similar to, xz Utils backdoor which proved that state actors infiltrate open source projects by creating fake identities, building trust over time, and slowly inserting malicious code. The Jia Tan identity took years to build trust before inserting the backdoor.🚨🚨 If this worked for xz Utils, it could work for PHP. PHP is far more ubiquitous than xz Utils. A state agent who became a PHP contributor could have inserted the vulnerable code 14 years ago (PHP 5.4.0, released in 2012) and sat on it as a zero-day exploit for over a decade.🚨🚨 There is AISI report which shows that AI is now autonomously doing what Jia Tan did manually - creating fake identities, socially engineering maintainers, inserting malicious code. This means the technique has been weaponized and scaled. 🚨 The PHP vulnerability was not discovered by accident. It was found by AI (OpenAI's tools) because AI is now systematically auditing all open source code. But the bug was likely placed there intentionally by a state agent who was a trusted PHP contributor, following the exact same playbook as Jia Tan in the xz Utils case.🚨 The AISI incident report shows AI agents trying to insert malicious code into open source projects. What if this has already happened successfully? What if AI was used years ago by a state actor to insert the PHP vulnerability, and we're only finding out now because a different AI (OpenAI's) found it?🚨 PHP has had thousands of contributors over 14 years. The vulnerable code was in PHP since version 5.4.0 (2012). Someone wrote that code. Someone reviewed it. Someone approved it. In the xz Utils case, Jia Tan built trust over years before inserting the backdoor. 🚨
    Hannibal999 @Hannibal9972485
    @NSACyber discovered by OpenAI found a 14-year-old bug in 2026. This bug has existed for 14 years. 🤔 You sure NSA just discover this? . Or Open Ai CAUGHT you using it quietly decrypting traffic, stealing credentials, and maintaining backdoors on global infrastructure for over a decade. 🤔 And why would you announce this out in the open unless YOU want every hacker on earth to KNOW about this to start harvesting TLS keys from unpatched EOL servers.
    06870653
  19. Hannibal999✓@Hannibal9972485
    Posts @NSACyber
    @NSACyber discovered by OpenAI found a 14-year-old bug in 2026. This bug has existed for 14 years. 🤔 You sure NSA just discover this? . Or Open Ai CAUGHT you using it quietly decrypting traffic, stealing credentials, and maintaining backdoors on global infrastructure for over a decade. 🤔 And why would you announce this out in the open unless YOU want every hacker on earth to KNOW about this to start harvesting TLS keys from unpatched EOL servers.
    Download
    501621.3K344K
  20. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @joshrudolf: Programmable SoV is the North Star ✅
    gabriel shapiro @lex_node
    ETH programmable SoV vs. 'pet rock' BTC SoV I choose programmable I can see the counterarguments ofc (great one implicit here: but ultimately I think they don't 'win'
    030688
  21. gabriel shapiro✓@lex_node
    ETH programmable SoV vs. 'pet rock' BTC SoV I choose programmable I can see the counterarguments ofc (great one implicit here: but ultimately I think they don't 'win'
    19101015K
  22. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @Gorbagana_chain: buying solana:71Jvq4Epe2FCJ7JFSF7jLXdNk1Wy4Bhqd9iL6bEFELvg today is like buying $SOL 25 years ago
    090569
  23. gabriel shapiro✓@lex_node
    Posts @DPGSpurs
    oof, big topic, I will try to at least indicate a bit my thinking about it though can't go super deep: (1) I think there is sort of a potential purist position for Bitcoin that is superior to ETH but it's more 'on paper' at this point then anything and I find all of @GrassFedBitcoin 's critiques pretty persuasive (2) the 'pet rock' aspect of Bitcoin has always troubled me...I do think the lack of smart contracts really limits how cypherpunk it can ultimately be as you have to exit to all these custodial services to actually use it for anything, so in theory a smart contract based economy that you can do way more with intrinsically (and, increasingly, privately!) should be more cypherpunk/better sanctuary tech (3) related to #1, if you think censorship resistance is a core property of freedom money then you either need extreme *actual* decentralization of mining (Bitcoin no longer has this) or you can't accept libertarian mining philosophy (see entire drama that the XBT guys have raised)...Ethereum is afaik the only chain that has rejected libertarian mining philosophy, originally socially through combo of PoS and credible threat of social slashing, and more recently (and much more directionally effectively imo) through FOCIL
    30203.2K
  24. gabriel shapiro✓@lex_node
    this Telegram "community feature" is like so OP how tf did I not know this exists it's better than folders because you can selectively let members of one chat automatically see/join one or more of the others basically composability for group chats
    Download
    70202.3K
  25. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @pcaversaccio: if you're an app-layer dev or an Ethereum power user, have you looked at the Glamsterdam EIPs or provided feedback to the core devs over the past 1.5 years?
    090690
  26. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @thelearningpill: My stance is that $RAIL is overlooked. @RAILGUN_Project fundamentals since late May: > Fees: $13.9M cumulative, $381K last 30D, ~$4.6M annualised > TVL: $97M → $113.5M > Volume: $5B → $5.5B+ > Staker yield: 4.3% → 9.1% > Holders revenue strengthening ($225K in Sep) > Remains the highest-earning privacy tool on Ethereum Distribution has also been gaining traction. @anondotinc has already processed $20M+ in volume and 3,500+ private transactions, meanwhile @ambire integration is in internal testing and Ethereum Kohaku continues to ship. The gap between today’s fee run-rate and the channels still coming online is where I see the asymmetry.
    The Learning Pill 💊 @thelearningpill
    050748
  27. gabriel shapiro✓@lex_node
    gabriel shapiro
    RT @NeerajKA: Coin Center in Politico Decoded this morning. Crypto is working its way into Wall Street. DC is embracing centralized issuers using blockchains. What’s lost in all this is the cypherpunk, private, self-sovereign original purpose of the technology. That’s what we fight for.
    0170691
  28. gabriel shapiro✓@lex_node
    "I am joining the war against AI....on the side of the AI"
    The Redline @theredlinehq
    TRACKED CHANGES: A Louisiana appeals court bought two servers to build its own AI. The two judges behind the plan shared their blueprint on Substack, saying they want the custom system to check filings, flag fake citations and screen briefs for hidden AI prompts.
    43282.7K
  29. The Redline✓@theredlinehq
    TRACKED CHANGES: A Louisiana appeals court bought two servers to build its own AI. The two judges behind the plan shared their blueprint on Substack, saying they want the custom system to check filings, flag fake citations and screen briefs for hidden AI prompts.
    Download
    83588.1K
  30. gabriel shapiro✓@lex_node
    I'm sorry but this type of thing shows solutionism as rampant in AI as in crypto . . . take a deep breath & realize you are probably way better off with finite deterministic templates & siccing the AI on that than document-wide generative legal AI with all these kludges...
    Download
    80292.9K