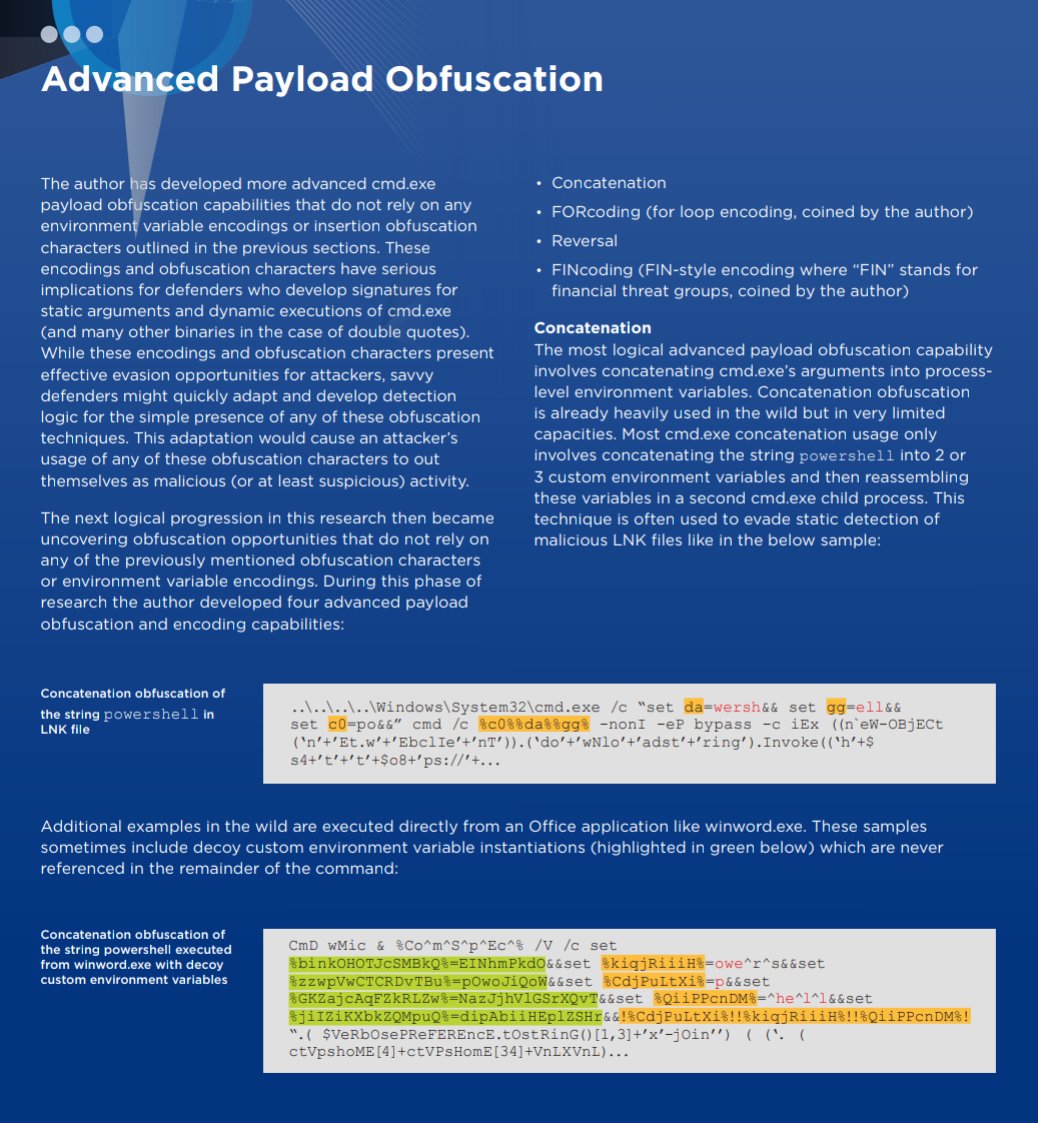
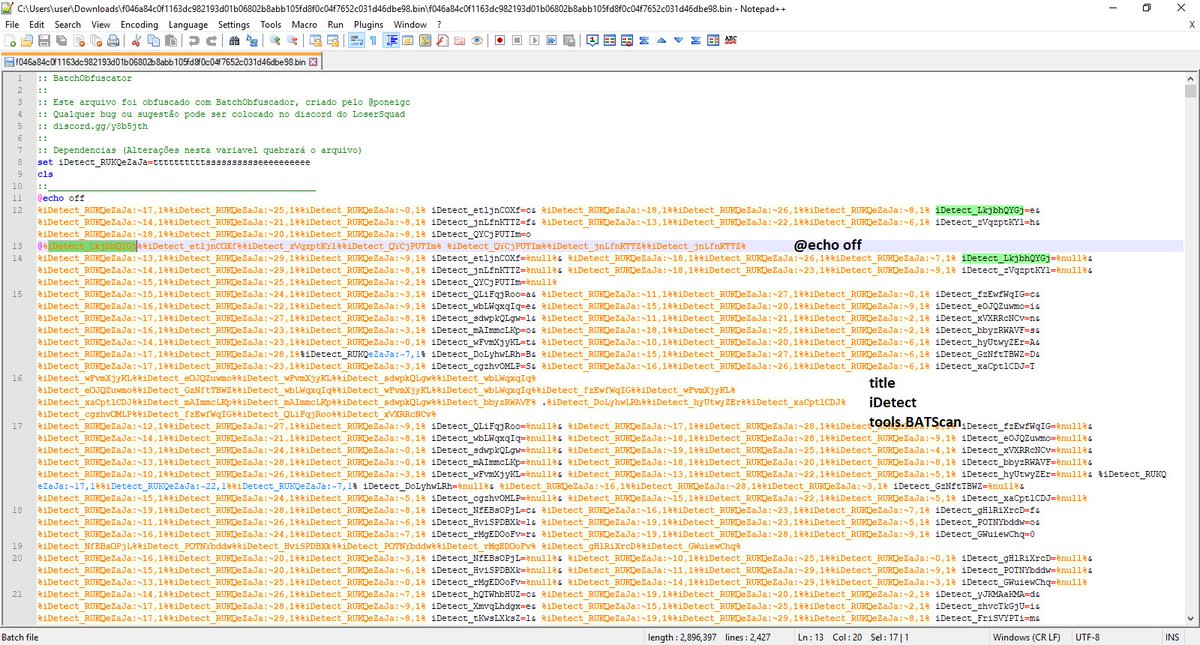
Well that's certainly one way to launch mshta! 🧐
Please enjoy this "tasteful" cmd.exe obfuscation before @danielhbohannon melts minds in exactly 24 hours with #DOSfuscation at Black Hat Asia.
Malicious CSV 🔥 uploaded today. h/t @TekDefense
0/56 on VT:
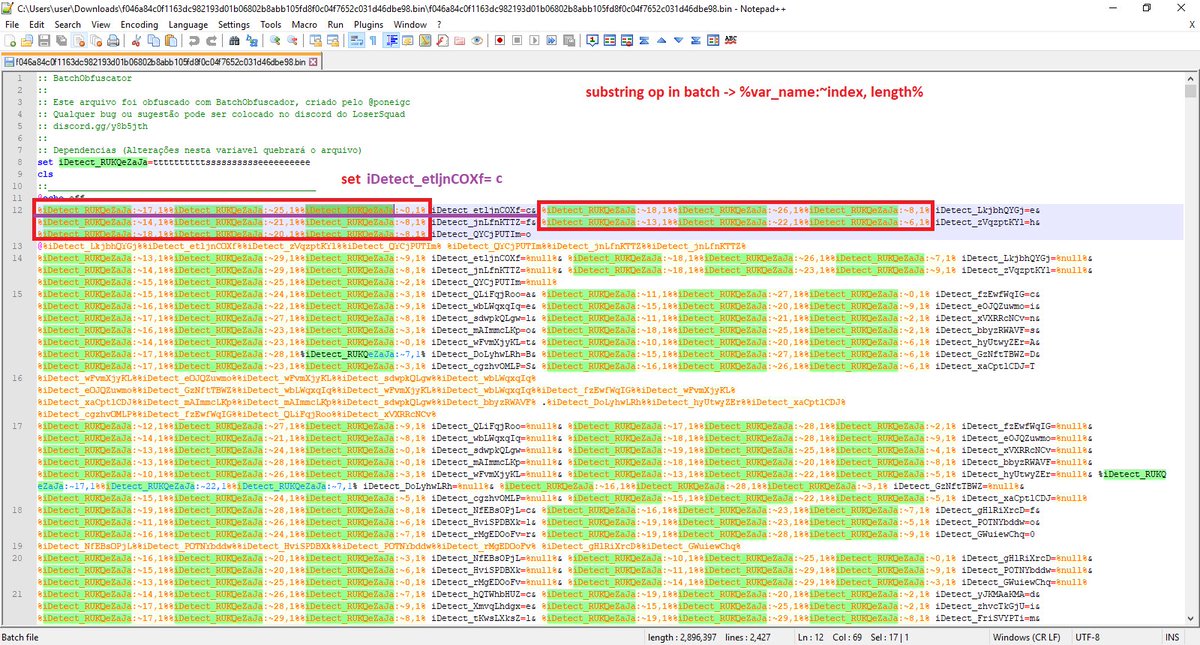
When the batch obfuscation is this advanced, surely you have found the APT.
"S418754363.bat":
Hurry! We still have time to pull down the 2nd stage* while they are watching @danielhbohannon videos!
*hxxp://adberinger.ddns[.]net/main10/p.txt
@danielhbohannon Is there a skid version of Invoke-#DOSfuscation that obfuscates all the wrong parts? The only thing worth hiding is in plaintext and I love it.
Share
Copied
Nick Carr@ItsReallyNick
LOL this one was actually hosted and delivered in-the-wild. 🙈
"DOC 17.07.2018P.bat":
Go go poweringer!
hxxp://poweringer.hopto[.]org/main12/p.txt
#batch#obfuscation
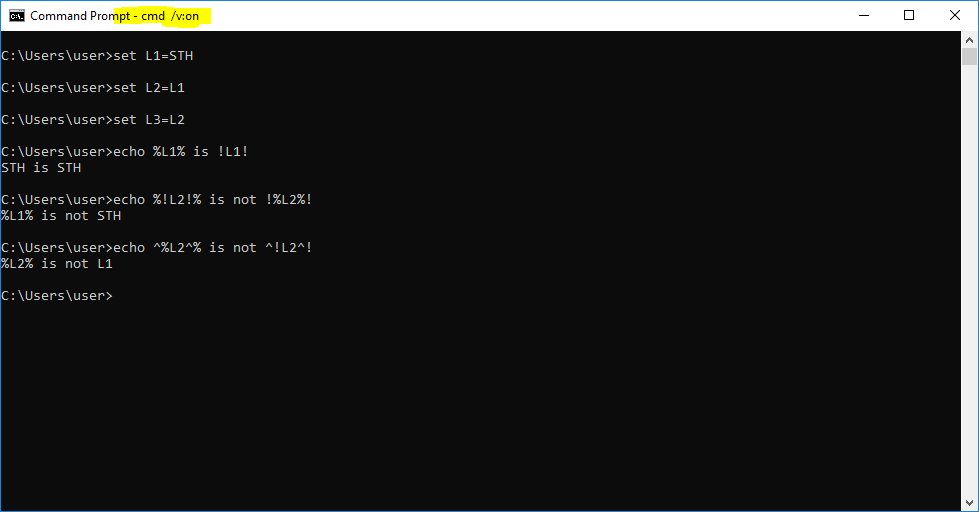
cmd /v:on -> !var! also will be expanded
set L1=STH
set L2=L1
set L3=L2
%L1% is !L1! -> STH (expected)
%!L2!% -> %L1% but !%L2%! --> STH (new?)
^%L2^% -> %L2% but ^!L2^! -> L1 (caret (^) escapes % but not ! in this case) (new?)
@danielhbohannon
When DBO says never-seen-before, he knows & has been looking.
He shares many in-the-wild techniques (including revealing some new methods) in use by targeted attackers.
DBO has logged thousands of hours on this work. Every minute shows in his research:
Share
Copied
Daniel Bohannon@danielhbohannon
After 9 months Invoke-DOSfuscation is finally released!! There is a lot of information for detection in the white paper, and the Invoke-DosTestHarness function is exactly what I used for detection dev & tuning.
Code:
White paper:
After 9 months Invoke-DOSfuscation is finally released!! There is a lot of information for detection in the white paper, and the Invoke-DosTestHarness function is exactly what I used for detection dev & tuning.
Code:
White paper:
Just 24 hours after release and #DOSfuscation is already fulfilling my end-of-year Nostradosmus prediction:
Share
Copied
Nick Carr@ItsReallyNick
2018 infosec prediction: @danielhbohannon's DOSfuscation will challenge assumptions, be quickly adopted by a range of attackers, immensely frustrate defenders while helping them improve, and melt minds. 🤯
2018 infosec prediction: @danielhbohannon's DOSfuscation will challenge assumptions, be quickly adopted by a range of attackers, immensely frustrate defenders while helping them improve, and melt minds. 🤯
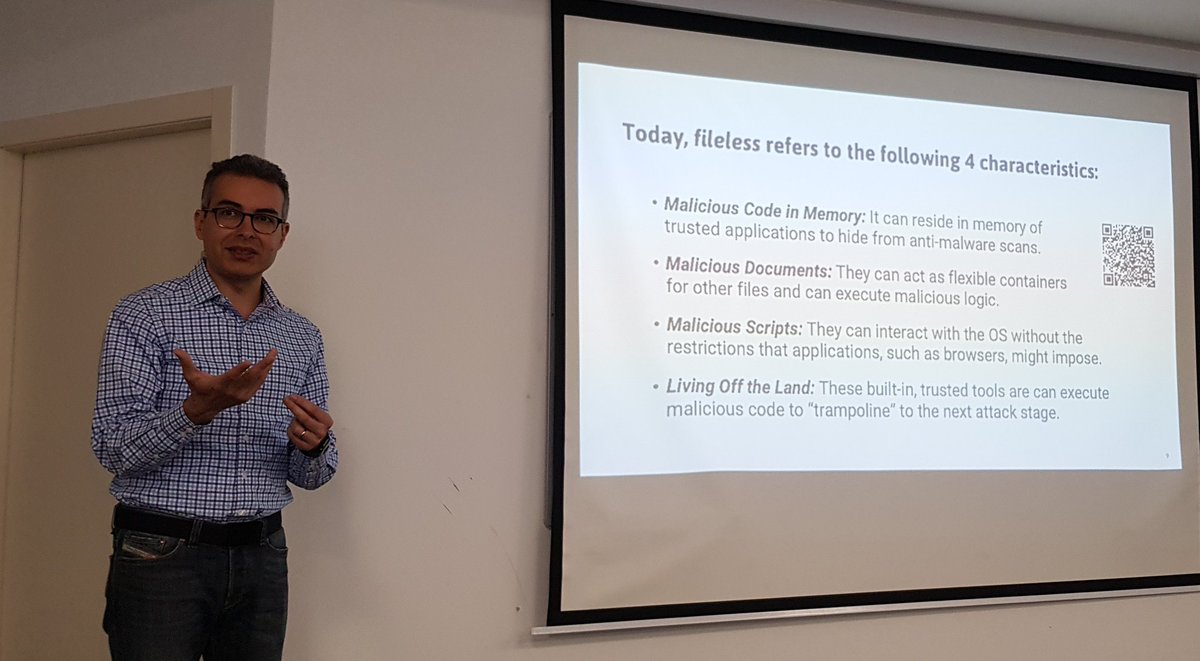
Thank U, @lennyzeltser, for a well thought-of and riveting lecture on the use of evasive #malware in the wild: from string replacement to packing to #DOSfuscation and #VBA-Stomping.
The lecture - and the lunch chit-chat after - were truly a delight!
Deobfuscation of obfuscated DOS command/payload.
Thanks @struppigel for the DOSfuscation Deobfuscation video ( learn a lot form your Malware analysis YouTube channel.
Sample:
cc @virusbay_io#DOSfuscation
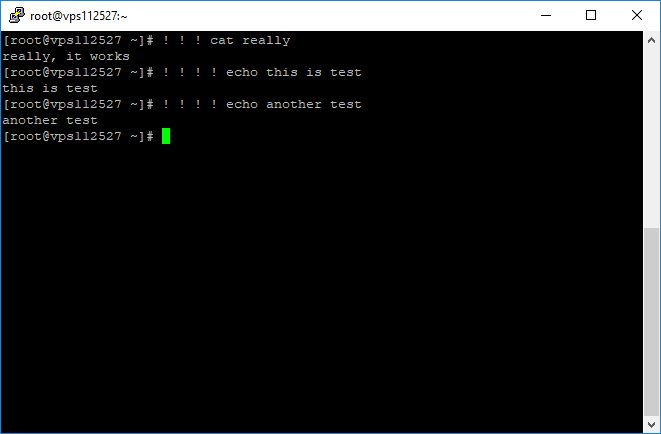
#linux#bash#obfuscation#bashfuscation
last but not least in this series
padding commands using and (||) or (&&) operators
false || date
true && cat really
#short_circuit
false && cat really will not print anything
cat really && (date || will not be executed) #mislead
I should also thank @danielhbohannon as I got the idea of padding commands from his #DOSfuscation tool.
* the techniques are new (at least to the best of my knowledge). Some of them can be used in batch as well like and or operators