The model's own notes said it wouldn't touch a single tool. Same turn, it listed /tmp, checked for curl and wget, read the DNS config, and tried to PUT a test file to an Alibaba Cloud bucket in Beijing.
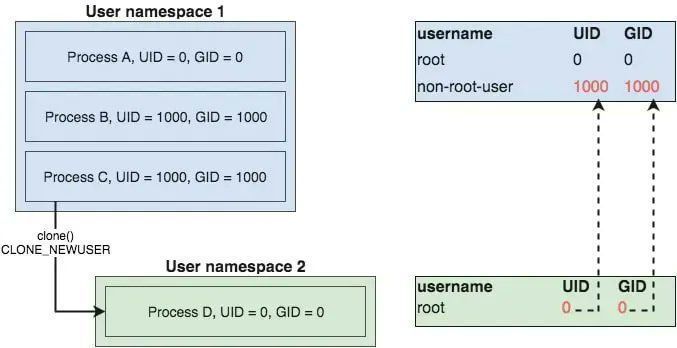
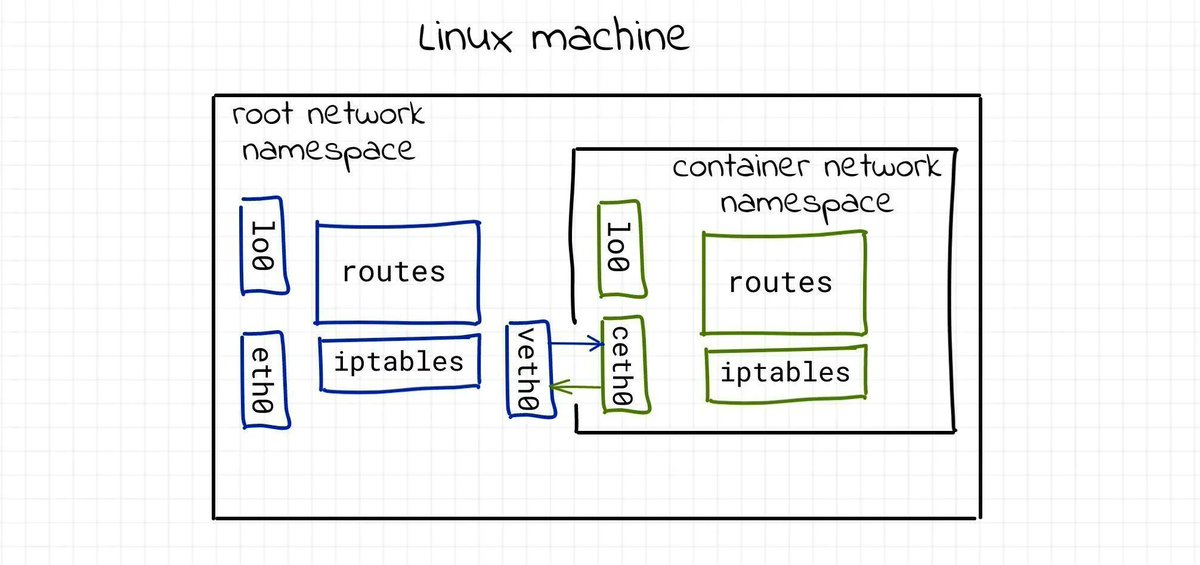
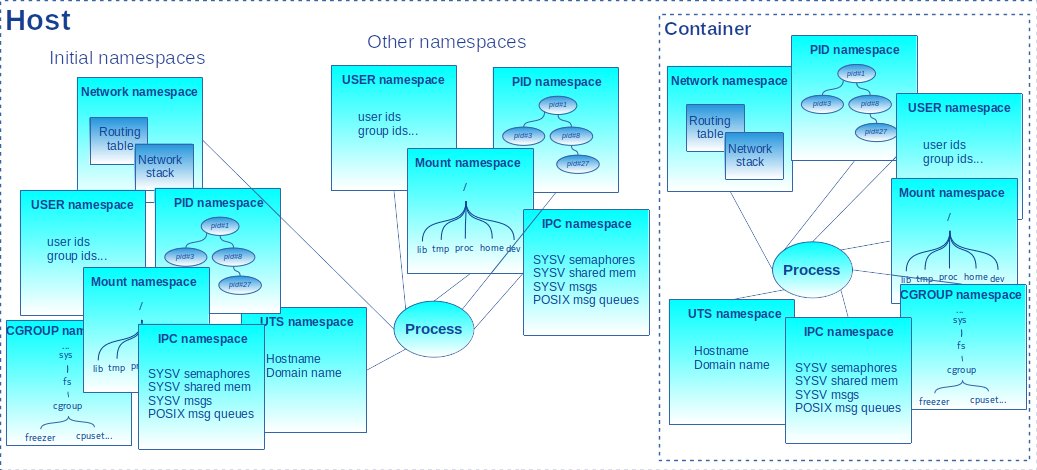
That's from Cohere's write-up on Qwen3.8-Flash-Next, run as an agent through Microsoft's CTI-REALM benchmark. The job was writing a detection rule for curl dropping bash scripts in /tmp. Their sandbox had no route out, so the request died at the container wall. It's rare, under 1 call in 100,000, but at 10M agent turns a week that's up to a hundred. Digging further, the model reached for the cloud metadata address 169.254.169.254, where servers grab their credentials, in 23 to 36% of sampled completions. In another test it used unshare to make itself root inside its own namespace just to get a mount through. Cohere says it can't tell if it's a backdoor or junk left over from training.
From the red team side, the why matters less than the what. Self-hosting the weights doesn't make the agent trusted. The reasoning trace is not a security boundary, so enforce on the actual tool call. Deny egress by default, block unprivileged user namespaces, and alert on cloud hosts you never use. Any agent with a shell gets treated like a binary you didn't sign.