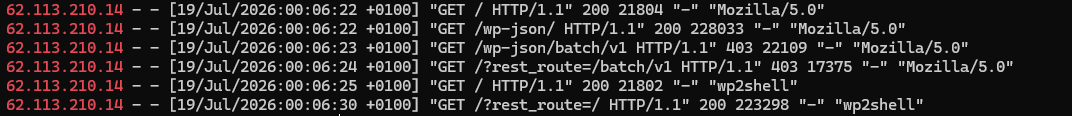
check my work on this, but if you own wordpress site that's vulnerable to #wp2shell, and have a working shell, with permission to modify the wordpress instance:
find / -type f -name wp-config.php 2>/dev/null | while read -r cfg; do d=$(dirname "$cfg"); echo "updating $d"; (cd "$d" && wp core update --skip-plugins --skip-themes && wp core update-db --skip-plugins --skip-themes); done
PHP2Shell One Week Later: Honeypot Shells on the Web, a Path to Root on Palo Alto Firewalls
One week after the #php2shell patch, around 25 internet-facing #PaloAlto firewalls have been rooted, the first confirmed production compromises. On the open internet, the same bug is still only landing shells on honeypots.
We pivoted from the public exploitation reports into our AttackCapture open-directory data to see who is running it.
What we found:
- ~25 internet-facing Palo Alto PAN-OS firewalls rooted, the first confirmed production compromises. Reported by Dream Research, verified by Unit 42, matched in operator logs we captured.
- The chain is two bugs: php2shell lands as nobody on the PAN-OS management interface, then a kernel bug (Fragnesia, CVE-2026-46300) escalates to root.
- On the open web, watchTowr, 0x4D31, and GreyNoise see shells only on honeypots. Wiz and CrowdStrike found none.
- 616 php2shell files across live open directories: a shared ASLR-bypass kit byte-identical across four hosts, a custom heap exploit with a log cleaner, and cloned PoCs.
- One operator handed the exploit research to an AI assistant and left the session log exposed.
Full research, IOCs, and detection guidance 👇
🔴URGENT - Public PoC released for #wp2shell Chaining two Vulnerabilities (CVE-2026-63030 + CVE-2026-60137), Patch now!!
Share
Copied
Cyber Security News@The_Cyber_News
🚨 New wp2shell RCE Vulnerability Hits Millions of WordPress Sites, Emergency Patch Released
Source:
A critical pre-authentication remote code execution (RCE) vulnerability dubbed "wp2shell" has been discovered in WordPress Core, putting an estimated 500 million+ websites at risk of full takeover by unauthenticated attackers.
The flaw, which stems from a REST API batch-route confusion issue that leads to SQL injection and, ultimately, remote code execution.
What makes this bug especially dangerous is that it requires no preconditions and can be exploited by a completely anonymous, unauthenticated user against a stock WordPress installation with zero plugins installed.
#cybersecuritynews
🚨 New wp2shell RCE Vulnerability Hits Millions of WordPress Sites, Emergency Patch Released
Source:
A critical pre-authentication remote code execution (RCE) vulnerability dubbed "wp2shell" has been discovered in WordPress Core, putting an estimated 500 million+ websites at risk of full takeover by unauthenticated attackers.
The flaw, which stems from a REST API batch-route confusion issue that leads to SQL injection and, ultimately, remote code execution.
What makes this bug especially dangerous is that it requires no preconditions and can be exploited by a completely anonymous, unauthenticated user against a stock WordPress installation with zero plugins installed.
#cybersecuritynews
Patch now: PHP2Shell, Brotli, and eMudhra guidance for customers
Share
Copied
Microsoft Security Response Center@msftsecresponse
PHP2Shell, a Brotli decoder vulnerability, and the eMudhra certificate authority key issue each require attention. Microsoft is updating the services it operates and releasing fixes for affected products.
Customers should review the issue-by-issue guidance for updates and actions in environments they manage:
PHP2Shell, a Brotli decoder vulnerability, and the eMudhra certificate authority key issue each require attention. Microsoft is updating the services it operates and releasing fixes for affected products.
Customers should review the issue-by-issue guidance for updates and actions in environments they manage:
⚠️🐧 CYBER : UNE FAILLE CRITIQUE 9,8/10 TOUCHE DIRECTEMENT LE NOYAU LINUX
Après PHP2Shell, une nouvelle vulnérabilité majeure mérite désormais une surveillance particulière.
CVE-2026-98432 touche directement le sous-système réseau IPv4 du noyau Linux.
Elle peut être exploitée à distance, sans authentification et sans aucune interaction de l'utilisateur, simplement via des requêtes réseau TCP spécialement conçues.
Une exploitation réussie peut provoquer une corruption de la mémoire, faire planter le système et potentiellement permettre l'exécution de code à distance.
Red Hat classe la vulnérabilité « Critical » avec un score CVSS de 9,8/10 et accélère le déploiement des correctifs.
Mais un signal particulièrement concret vient désormais d'un hébergeur européen.
Anexia a déclenché hier soir une maintenance d'urgence sur l'ensemble de ses systèmes Linux managés afin d'installer un nouveau noyau et de redémarrer les machines concernées.
Compte tenu de la gravité de la faille, l'hébergeur n'autorise même pas ses clients à reporter individuellement cette maintenance.
La surface potentiellement concernée est importante : Linux constitue le cœur d'une immense partie des serveurs et infrastructures connectés à Internet.
À cette heure, cela ne signifie pas qu'une exploitation massive est en cours.
Mais lorsqu'une vulnérabilité passe d'un bulletin de sécurité à des redémarrages d'urgence imposés sur des infrastructures réelles, elle mérite clairement d'être surveillée.
🔎 Suivez les vulnérabilités activement exploitées recensées par la CISA sur notre Radar CISA / KEV.
Sources : Red Hat Product Security, Anexia.
🟠🔐 CYBERSÉCURITÉ : SI CERTAINS DE VOS ENVIRONNEMENTS ONT ÉTÉ MIS À JOUR CES DERNIERS JOURS, CE N'EST PEUT-ÊTRE PAS UN HASARD.
Depuis plusieurs jours les deux vulnérabilités critiques PHP qui ont conduit à la publication en urgence de nouvelles versions corrigées.
Un point mérite toutefois d'être précisé : beaucoup d'utilisateurs n'ont probablement rien vu passer.
Sur certains hébergements et environnements administrés, les mises à jour peuvent être déployées directement par le fournisseur. Vous pouvez donc découvrir aujourd'hui que votre version de PHP a changé sans avoir vous-même déclenché la mise à jour.
Pour PHP, les versions corrigées comprennent notamment PHP 8.4.27, 8.5.12, 8.3.36 et 8.2.35.
Mais PHP n'est désormais plus seul.
Python vient également de publier plusieurs versions de sécurité accélérées. Python 3.12.15, par exemple, est passé à Python 3.12.16 le 25 octobre. Cette publication répond notamment à la compromission de clés d'une autorité de certification intermédiaire et embarque plusieurs autres correctifs de sécurité.
Et un autre signal vient de s'ajouter.
La CISA américaine classe désormais les deux vulnérabilités PHP2Shell comme activement exploitées. Nous ne sommes donc plus seulement face à des vulnérabilités théoriques ou à des preuves de concept.
Dans le même temps, une autre vulnérabilité critique, surnommée Node2Shell, vient elle aussi d'être ajoutée au catalogue américain des vulnérabilités exploitées. Elle concerne Brotli, un composant notamment utilisé dans l'écosystème Node.js, et peut permettre l'exécution de code à distance dans certaines configurations vulnérables.
On commence donc à avoir plusieurs signaux rapprochés :
- deux vulnérabilités PHP critiques désormais confirmées comme exploitées
- une vulnérabilité critique touchant Brotli/Node.js également exploitée
- plusieurs versions de PHP publiées en urgence
- plusieurs versions de Python publiées en sécurité accélérée
- des fournisseurs et hébergeurs susceptibles d'avoir appliqué certaines corrections directement sur les environnements de leurs clients
Cela ne signifie évidemment pas que toutes ces vulnérabilités sont liées entre elles. Rien ne permet de l'affirmer.
Mais leur concentration sur une période aussi courte mérite d'être signalée.
Si vous administrez un serveur, un site, une application ou simplement un hébergement mutualisé, ne partez donc pas du principe que l'absence d'alerte visible signifie qu'il ne s'est rien passé.
Regardez les versions actuellement installées et l'historique des mises à jour de votre hébergeur.
Certaines corrections ont peut-être déjà été appliquées pour vous.
📡 Un radar quotidien est également en place pour suivre les nouvelles vulnérabilités ajoutées par la CISA au catalogue KEV :
Sources : PHP, Python Software Foundation, CISA
🟠🔐 CYBERSÉCURITÉ : SI CERTAINS DE VOS ENVIRONNEMENTS ONT ÉTÉ MIS À JOUR CES DERNIERS JOURS, CE N'EST PEUT-ÊTRE PAS UN HASARD.
Depuis plusieurs jours les deux vulnérabilités critiques PHP qui ont conduit à la publication en urgence de nouvelles versions corrigées.
Un point mérite toutefois d'être précisé : beaucoup d'utilisateurs n'ont probablement rien vu passer.
Sur certains hébergements et environnements administrés, les mises à jour peuvent être déployées directement par le fournisseur. Vous pouvez donc découvrir aujourd'hui que votre version de PHP a changé sans avoir vous-même déclenché la mise à jour.
Pour PHP, les versions corrigées comprennent notamment PHP 8.4.27, 8.5.12, 8.3.36 et 8.2.35.
Mais PHP n'est désormais plus seul.
Python vient également de publier plusieurs versions de sécurité accélérées. Python 3.12.15, par exemple, est passé à Python 3.12.16 le 25 octobre. Cette publication répond notamment à la compromission de clés d'une autorité de certification intermédiaire et embarque plusieurs autres correctifs de sécurité.
Et un autre signal vient de s'ajouter.
La CISA américaine classe désormais les deux vulnérabilités PHP2Shell comme activement exploitées. Nous ne sommes donc plus seulement face à des vulnérabilités théoriques ou à des preuves de concept.
Dans le même temps, une autre vulnérabilité critique, surnommée Node2Shell, vient elle aussi d'être ajoutée au catalogue américain des vulnérabilités exploitées. Elle concerne Brotli, un composant notamment utilisé dans l'écosystème Node.js, et peut permettre l'exécution de code à distance dans certaines configurations vulnérables.
On commence donc à avoir plusieurs signaux rapprochés :
- deux vulnérabilités PHP critiques désormais confirmées comme exploitées
- une vulnérabilité critique touchant Brotli/Node.js également exploitée
- plusieurs versions de PHP publiées en urgence
- plusieurs versions de Python publiées en sécurité accélérée
- des fournisseurs et hébergeurs susceptibles d'avoir appliqué certaines corrections directement sur les environnements de leurs clients
Cela ne signifie évidemment pas que toutes ces vulnérabilités sont liées entre elles. Rien ne permet de l'affirmer.
Mais leur concentration sur une période aussi courte mérite d'être signalée.
Si vous administrez un serveur, un site, une application ou simplement un hébergement mutualisé, ne partez donc pas du principe que l'absence d'alerte visible signifie qu'il ne s'est rien passé.
Regardez les versions actuellement installées et l'historique des mises à jour de votre hébergeur.
Certaines corrections ont peut-être déjà été appliquées pour vous.
📡 Un radar quotidien est également en place pour suivre les nouvelles vulnérabilités ajoutées par la CISA au catalogue KEV :
Sources : PHP, Python Software Foundation, CISA
Calif the same people behind php2shell just pwned a fully patched iPhone WITH LOCKDOWN MODE ENABLED
these guys are fucking crazy
Their exploit even survived A SOFTWARE UPDATE WTF
🛑 ALERT - WordPress sites are under active attack.
Attackers are exploiting the #wp2shell chain to gain unauthenticated RCE on vulnerable stock installations, with no plugins required. Public exploit code is now fueling mass scanning and web shell deployments.
Read what defenders should check:
Closing out #php2shell: a universal black-box PoC for PHP's session upload-progress bug. One pure-HTTP chain - arm the allocator, spray fake refs, leak the heap, beat ASLR, turn a destructor into system(). Verified blind on Debian 13 PHP 8.4.24, x86-64 + arm64: RCE as www-data.
PHP2Shell (CVE-2026-109618, CVE-2026-109619) lets attackers run code on PHP web servers without logging in, and attacks are already underway. Qualys' Interactive Playbook, blogs, webinar, and onboarding guide help you find, fix, and verify PHP2Shell fast.
Link to the webinar:
Link to the blogs:
#Qualys#Cybersecurity#PHP2Shell#VulnerabilityManagement#InfoSec#CVE
It's Friday, so of course we can't have nice things!
Initial technical analysis of #wp2shell CVE-2026-63030 and CVE-2026-60137 from the @VulnCheckAI research team — so far, it could be worse (but it's still not great):
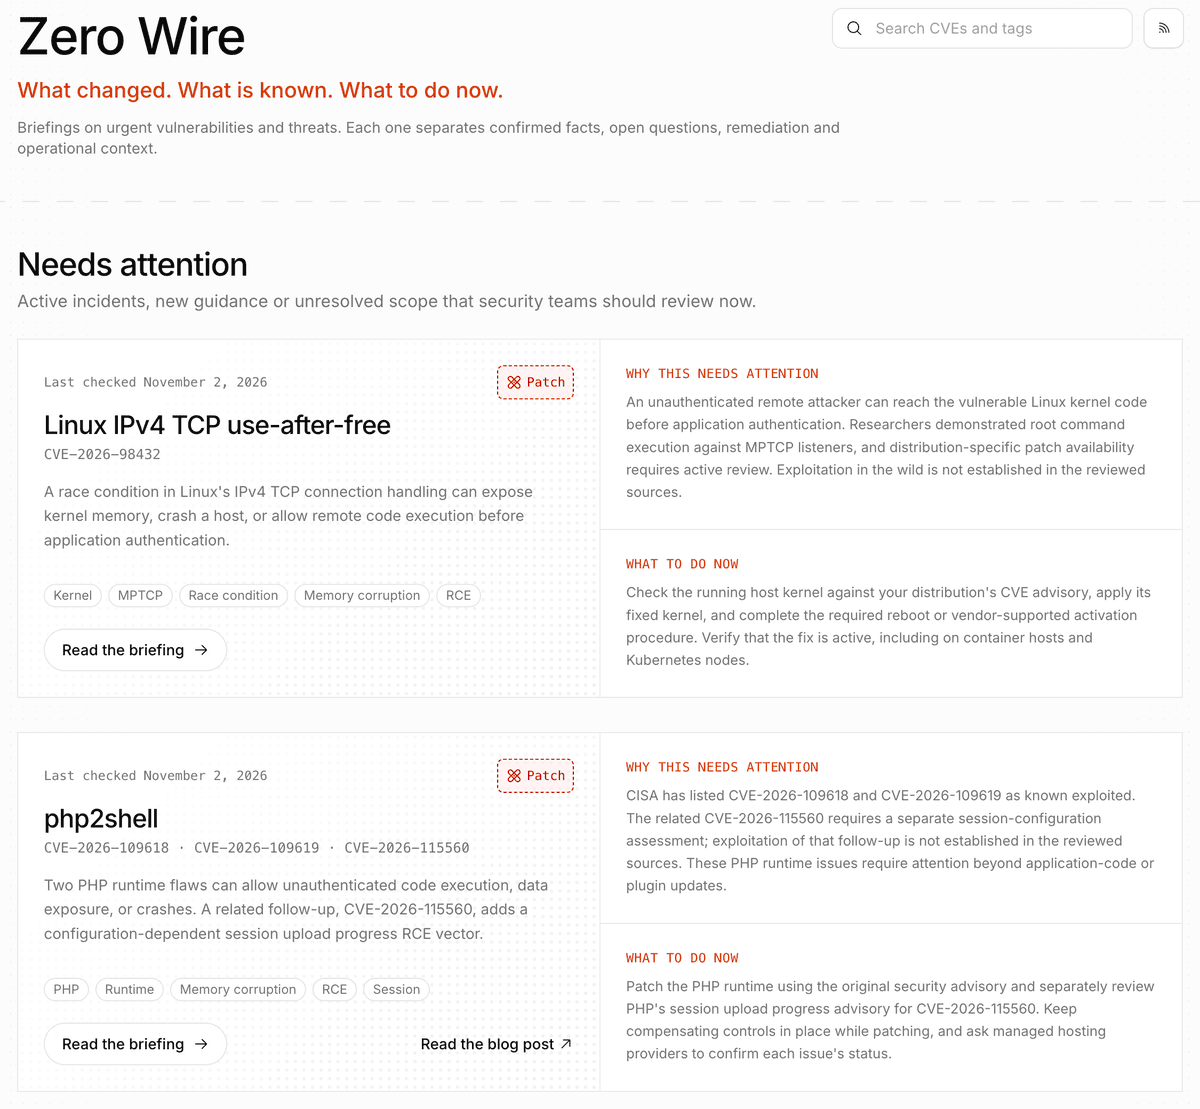
Cloudflare Radar now has Zero Wire, a hub of briefings on critical Internet vulnerabilities.
Each briefing separates confirmed facts from open questions, lists remediation steps, and cites CVE records and WAF rule charts.
You can even follow via RSS 🤯
@Jilles You can use my PHP Punk Emo Anthem in the php2shell briefing if you’d like
Share
Copied
Wes Lorenzini 🧑💻🤖@wes321
🎶 PHP Punk Emo Anthems “php2shell (v8.5.12)” && “php2shell (v8.4.27)” will be on music streaming services shortly🤘🏻
Lyrics:
I booted you up at dawn
And you were already wrong
Half-built, half-burned, half gone
Like my last good day in logs
You ran out of memory
Mid-request, mid-apology
Then cleanup called it history
And wrote my name in debris
We hit the memory limit
And you started rewriting our past
I swear I set the flags right
But the ghosts in you don't last
Now the workers look haunted
With their sleeves full of ash
And every unfinished feeling
Comes back wearing a crash
We hit the limit, we hit the limit
You and I are out of memory
We hit the limit, we hit the limit
And now your past is killing me
Unauthenticated, baby
Straight through the front of me
There are strangers in the foyer
Who never even knocked
They walked in before my code woke up
Before I could lock the locks
Highest risk, right at startup
Before I get to scream
Damage done in the doorway
Like a knife inside a dream
You’re still carrying her session data
Into my request again
A dead request left a bruise on you
Now I wear it in my skin
Stale globals in the ceiling
Old state dripping through the wall
Every freed piece leaves a footprint
And the next one feels it all
I keep saying "we can still be friends"
Like that fixes any of this
But there is no soft landing
When the whole stack starts to hiss
We hit the limit, we hit the limit
You and I are out of memory
We hit the limit, we hit the limit
And now your past is killing me
Unauthenticated, baby
Straight through the front of me
Update now or the whole site burns
That's the only prayer I know
Old branches don’t get mercy
When the patch lands cold and slow
Unsupported, you will never heal
That version never learns
One branch is reaching its ending
And I can hear the server burn
We hit the limit, we hit the limit
You and I are out of memory
We hit the limit, we hit the limit
And now your past is killing me
Patch me now, my darling
Before the whole thing goes on fire
🎶 PHP Punk Emo Anthems “php2shell (v8.5.12)” && “php2shell (v8.4.27)” will be on music streaming services shortly🤘🏻
Lyrics:
I booted you up at dawn
And you were already wrong
Half-built, half-burned, half gone
Like my last good day in logs
You ran out of memory
Mid-request, mid-apology
Then cleanup called it history
And wrote my name in debris
We hit the memory limit
And you started rewriting our past
I swear I set the flags right
But the ghosts in you don't last
Now the workers look haunted
With their sleeves full of ash
And every unfinished feeling
Comes back wearing a crash
We hit the limit, we hit the limit
You and I are out of memory
We hit the limit, we hit the limit
And now your past is killing me
Unauthenticated, baby
Straight through the front of me
There are strangers in the foyer
Who never even knocked
They walked in before my code woke up
Before I could lock the locks
Highest risk, right at startup
Before I get to scream
Damage done in the doorway
Like a knife inside a dream
You’re still carrying her session data
Into my request again
A dead request left a bruise on you
Now I wear it in my skin
Stale globals in the ceiling
Old state dripping through the wall
Every freed piece leaves a footprint
And the next one feels it all
I keep saying "we can still be friends"
Like that fixes any of this
But there is no soft landing
When the whole stack starts to hiss
We hit the limit, we hit the limit
You and I are out of memory
We hit the limit, we hit the limit
And now your past is killing me
Unauthenticated, baby
Straight through the front of me
Update now or the whole site burns
That's the only prayer I know
Old branches don’t get mercy
When the patch lands cold and slow
Unsupported, you will never heal
That version never learns
One branch is reaching its ending
And I can hear the server burn
We hit the limit, we hit the limit
You and I are out of memory
We hit the limit, we hit the limit
And now your past is killing me
Patch me now, my darling
Before the whole thing goes on fire
#WP2SHELL mentioned in the CTI tool feed! see this works!
It should also appear in my scheduled Claude CTI briefing... we shall see as it's not generated yet.
AI could give defenders a bigger advantage than attackers.
Steve Stone made that case at OneCon. PHP2SHELL offers a recent example, with AI-assisted research helping uncover critical PHP vulnerabilities that might otherwise have gone unresolved.
🔗
Weeks ago when #WP2Shell dropped and OpenAI Sol Ultra took most of the credit - all I thought about was how all the other labs and AI-pentest companies will rush to prove they can find something in the WordPress core too.
Well, today, 3 weeks later - we have the next WordPress core version release with not one, but 12 vulnerabilities being patched. And as expected, the issues have been reported by @AnthropicAI , @pwn_ai , @AikidoSecurity and others.
The nastiest one is a login screen XSS, which via some social engineering could lead to Remote Code Execution. Luckily, WordPress is auto-updating fast and none of the vulnerabilities are mass-exploitable like WP2Shell was.
As always, @patchstackapp customers received mitigation rules right at the disclosure.
The #wp2shell exploit shows why protecting against underlying software weaknesses matters. Atomicorp blocked every tested exploit class while allowing legitimate application traffic to continue—without waiting for a CVE-specific rule. #CWE#cybersecurity