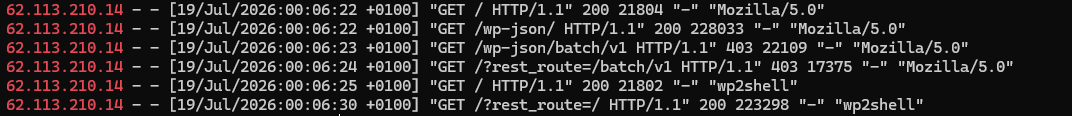
PHP2SHELL is so easy to exploit remotely, that all my WAF bypasses are dupes, and I am out of trial reports 🫡
LiveOverflow 🔴 hextree.io @LiveOverflowHere is the time the WAF buys you
9523024.9K
Posts with #wp2shell
Public posts on X that use #wp2shell.
LiveOverflow 🔴 hextree.io @LiveOverflowHere is the time the WAF buys you


Elastic Security Labs @elasticseclabswp2shell PoCs went public within hours of disclosure, and we are seeing active exploitation. Pre-auth RCE in WordPress Core. No plugins required. CVE-2026-63030 and CVE-2026-60137. We ran the Icex0 PoC end-to-end with Elastic Defend. On the host, every run ends the same way. The web server writes PHP under wp-content/plugins/, then spawns a shell. 4 rules caught it: - Payload Execution by Web Server: EDR, kills the shell on launch - PHP File Creation in WordPress Plugin Directory: catches the drop before execution - Suspicious Command Execution via Web Server: flags discovery commands from the web parent - Unusual Command Execution via Web Server: alerts on command lines the host has never run The PoC self-cleans after running. A missing plugin folder doesn't mean a clean host. Patch to 7.0.2 or 6.9.5. Hunt the IOCs while tooling is still stock. Full rule walkthrough, process lineage, and Attack Discovery correlation:


The Hacker News @TheHackersNews🛑 URGENT - A single anonymous HTTP request can run code on an unpatched #WordPress 6.9 or 7.0 site, even on a default install with zero plugins. The new wp2shell flaw sits in core and still has no CVE for scanners to match. Affected releases and mitigations 🠖


Cyber Security News @The_Cyber_News🚨 New wp2shell RCE Vulnerability Hits Millions of WordPress Sites, Emergency Patch Released Source: A critical pre-authentication remote code execution (RCE) vulnerability dubbed "wp2shell" has been discovered in WordPress Core, putting an estimated 500 million+ websites at risk of full takeover by unauthenticated attackers. The flaw, which stems from a REST API batch-route confusion issue that leads to SQL injection and, ultimately, remote code execution. What makes this bug especially dangerous is that it requires no preconditions and can be exploited by a completely anonymous, unauthenticated user against a stock WordPress installation with zero plugins installed. #cybersecuritynews


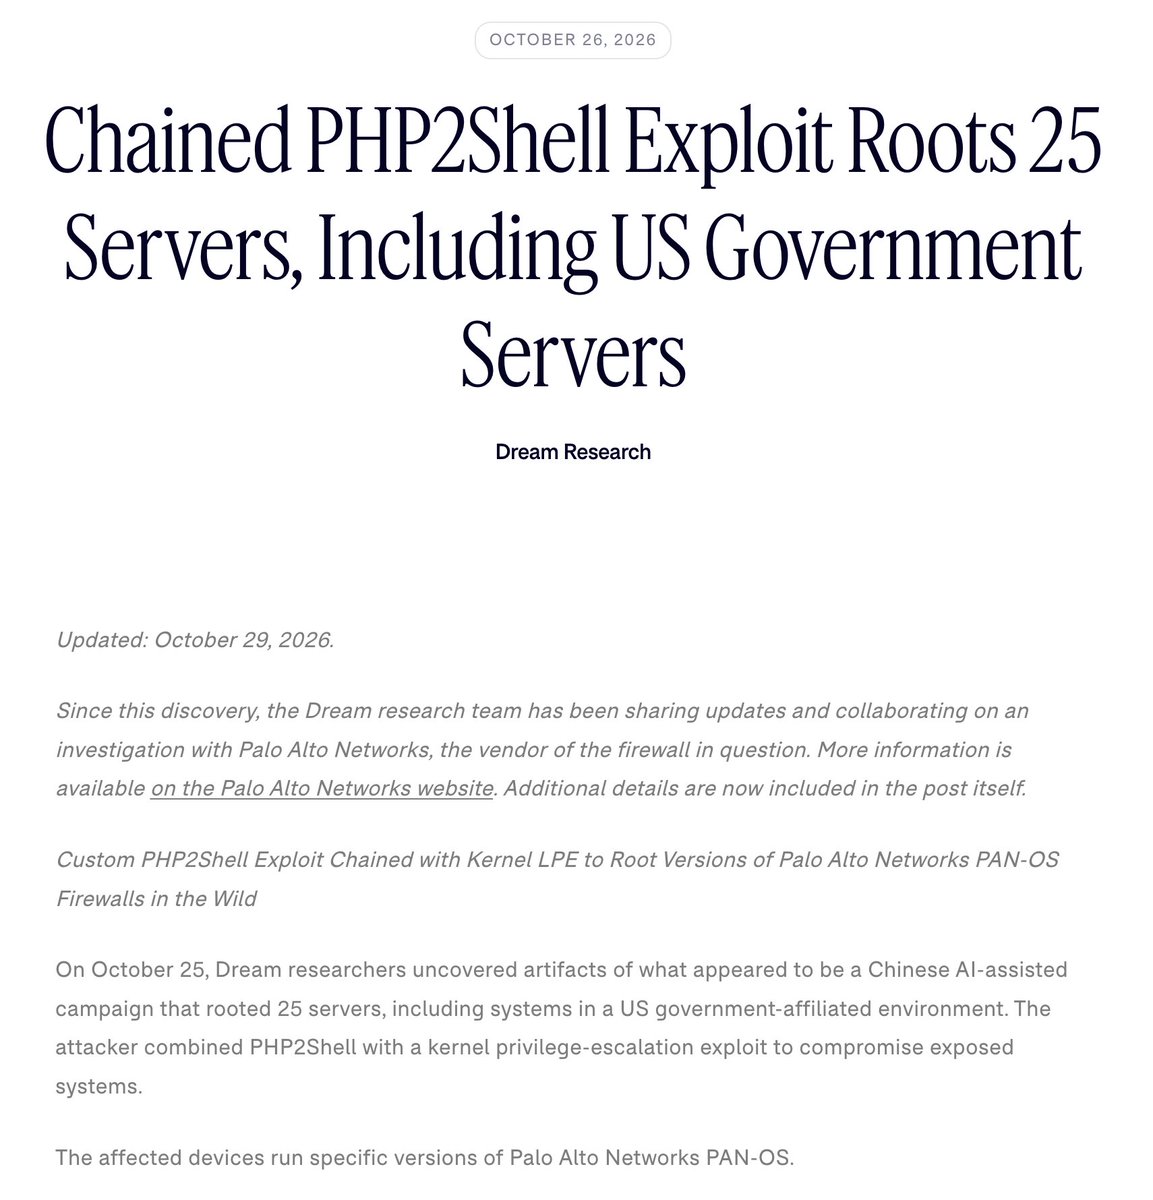
Dan Guido @dguidoUpdate: Our PHP exploit is now production-grade. * stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load * ARM64 + x86-64 targets * MediaWiki, WordPress, phpBB, Laravel * Apache/mod_php and nginx/php-fpm -> root