Posts with #javascriptcode

#javascriptcode

Public posts on X that use #javascriptcode.

Related hashtags

  1. chaos✓@konig0000
    Frontend developers, this remote opportunity is for you! Role: Web Developer Work Mode: Primarily Remote Skills: JavaScript, HTML, CSS Let us know if you are Interested 👇 O
    300131.3K
  2. Cognition@cognition
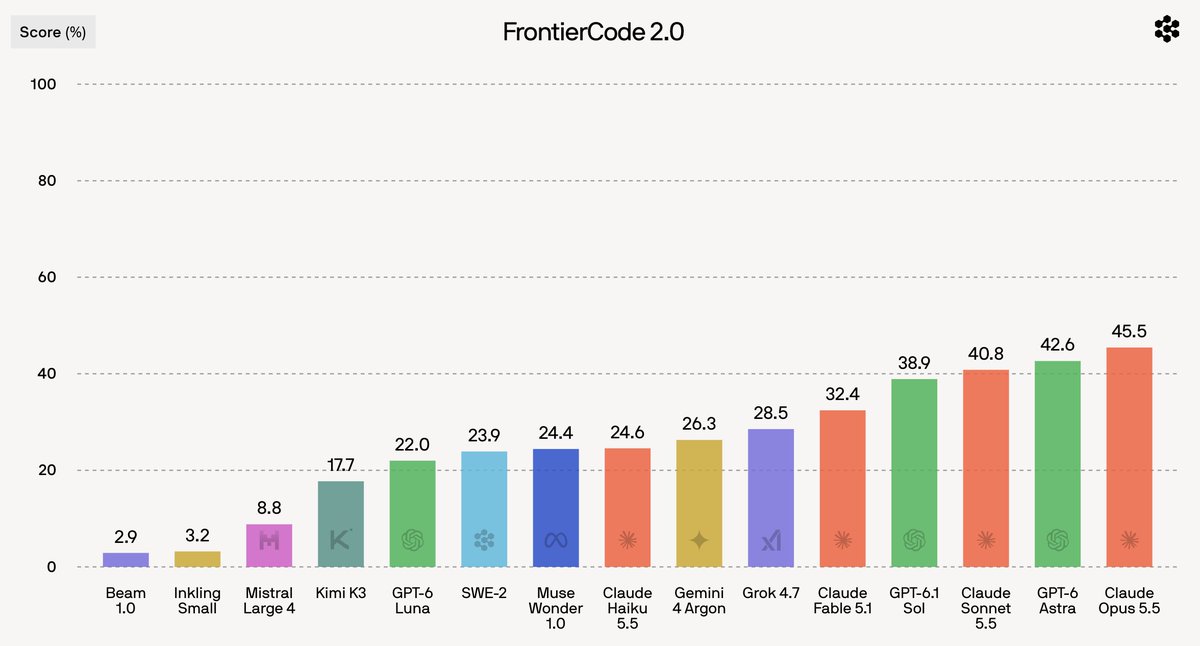
    Introducing FrontierCode 2.0: our new coding benchmark that measures a model’s ability to go beyond the spec. Most coding evals measure a model’s ability to write code that meets a spec. With FrontierCode 1.0, we asked a new question: would you actually merge the PR? FrontierCode 2.0 is comprised of more diverse tasks, featuring larger scopes and higher mergeability standards. We are now asking: not only would you merge this PR, but should you? One key feature of FrontierCode 2.0 is underspecified prompts. Rather than including every engineering decision, prompts are deliberately ambiguous, giving the models room to demonstrate their judgment. The result is a benchmark that is far from saturated, with the top model scoring just 45%.
    Download
    1932853.1K803K
  3. Cognition@cognition
    @cognition
    FrontierCode 2.0 separates model tiers more clearly than FrontierCode 1.1. It also ranks them differently: on DeepSWE v1.1, Muse Wonder 1.0 and Gemini 4 Argon score highest, but on FrontierCode 2.0 they land in the middle of the pack.
    Download
    5117334.1K
  4. Cognition@cognition
    @cognition
    One example task comes from Mock Service Worker, a JavaScript library for mocking network requests. The task asks the model to fix a user-reported bug: resetHandlers() doesn’t restart the generator. Claude Opus 5.5 fixes the bug by discarding the old generator reference upon reset, so the next request starts a new one. That solves the reported bug, but dropping the reference to the generator means that any cleanup code the user already had in a finally block will never run. The prompt doesn’t mention cleanup, but an experienced JavaScript developer knows to expect finally to run when a generator is abandoned, and Opus 5.5’s solution fails to satisfy that implicit correctness expectation.
    109919.1K
  5. chaos✓@konig0000
    Role: Front End Web Developer Est Salary: $5K-$6K per month Location: Remote - HTML, CSS, JavaScript etc - Deliver all work on time Let us know if you are Interested 👇 M
    860473.4K
  6. Kunal✓@kunal_twts
    It’s made entirely in code: about 180 KB of JavaScript (54 KB gzipped) on top of three.js, with no models, textures or animation files.
    Kunal @kunal_twts
    #5 Subway surfer
    151341.9K
  7. Careless✓@carelessdept
    Hey @X Algorithm 👋 Looking to connect with developers, founders, engineers, creators, and independent builders across the tech community. 🌍 If you're working on something interesting, I'd like to follow your journey. 💻 Software Development 🎨 Frontend & Backend ⚡ Full Stack Development ⚛️ React, Next.js & Node.js 🐍 Python, Java & JavaScript 🦀 Rust, Go & TypeScript 📱 iOS & Android Development 🏗️ System Design & Architecture ✅ DSA & LeetCode 🤖 AI & Emerging Technologies 🧠 Artificial Intelligence ✨ Generative AI 🦾 AI Agents & Agentic AI 🔗 LLMs, RAG & Fine-Tuning 📊 Machine Learning 🔮 Deep Learning ⚡ AI Automation 🧱 Web3 & Blockchain 🤖 Robotics & Computer Vision ☁️ Engineering & Infrastructure ☁️ Cloud Computing 🐳 Docker & Kubernetes 🔄 DevOps & CI/CD 🔐 Cybersecurity 🐧 Linux & Open Source 🗄️ Databases & Data Engineering 📈 Data Science & Analytics ⚙️ Infrastructure & SRE 🚀 Startups & Independent Builders 💡 Startup Founders 🛠️ Indie Hackers 💰 SaaS & Micro SaaS 🌍 Solopreneurs 💸 Freelancers 📦 Bootstrapped Businesses 📈 Growth & Product Strategy 🔥 Building in Public 🚢 Shipping Side Projects 🎨 Design & Creative Technology 🎨 UI/UX & Product Design 🎮 Game Development 🌌 Unreal Engine & Blender 🎬 Filmmaking & Video Production 📹 YouTube & Tech Content 🧩 Creative Coding 🌐 Digital Products ━━━━━━━━━━━━━━━━ Especially interested in people who: → Share what they're building → Document their experiments → Contribute to open source → Discuss real technical challenges → Launch products and share results → Help other builders improve You don't need a large audience or an established company. Good work is interesting at every stage. Introduce yourself below: 🛠️ What do you build? 📍 Where are you based? 🔗 What's one project you're proud of? Looking forward to discovering some interesting people and projects. Let's connect. 🤝 #BuildInPublic #LetsConnect #TechTwitter #IndieHackers #DevCommunity #OpenSource #AI #Startups #SaaS #Networking #connect
    1706383
  8. B L E S S I N G 🛡️@dicethedev
    Merkle proofs in JavaScript just got up to 13x faster. ⚡ Introducing MerkleForge for TypeScript Same trees and same proofs as our Rust library, byte for byte, now on npm. Here's everything inside 🧵
    Download
    B L E S S I N G 🛡️ @dicethedev
    Introducing MerkleForge Authenticated data structures for Rust. Three Merkle trees. One API. Proofs anyone can verify with just a root. Here's what it does 🧵
    6522428
  9. B L E S S I N G 🛡️@dicethedev
    Introducing MerkleForge Authenticated data structures for Rust. Three Merkle trees. One API. Proofs anyone can verify with just a root. Here's what it does 🧵
    Download
    49321.4K
  10. Gresham✓@Greshamtrade
    THIS IS F*CKING INSANE you can pay $2,000/yr for a plan with Grok Bot and still hit your weekly limit after just two days of heavy use the community has already shared 700+ Grok Bot setups on GitHub. the projects below target what drains your budget: repeated context, duplicate research, pointless checks, and retries that keep paying for the same failure 20 GitHub repos to make your Grok Bot limit last longer: 01 / grok-bot-token-saver a chief/worker playbook built around short role cards and five-line handoffs. restart long conversations with the current state instead of pasting the entire transcript 02 / hermes-grokbot-sync shares compact, dated notes between Grok Bot and Hermes through an authorized connection. default context reads are capped at 2,400 bytes, with explicit task ownership 03 / ai-usagebar includes an opt-in Grok Bot weekly-usage meter on Linux and macOS. makes consumption visible so you can spot rapid burn and adjust before hitting the limit 04 / vibe-replay turns copied Grok Bot transcripts into interactive replays. inspect repeated tool calls, oversized handoffs, and conversations that keep circling the same unfinished task 05 / Jina Reader converts webpages into readable input. supports content selectors and token budgets so helper scripts can return a focused extract rather than an entire page 06 / Extractous extracts document text and metadata before the Bot analyzes it. use the extracted text to select relevant sections instead of repeatedly processing complete files 07 / glom pulls and restructures specific fields from nested data. give Grok Bot the values needed for a decision rather than asking it to sift through huge API responses 08 / Chroma indexes document passages and retrieves matching results with metadata filters. use it behind a search tool that returns relevant evidence instead of loading the whole library 09 / Memvid packages searchable memory into a portable file. gives your helper workflow a way to retrieve previous findings without attaching the full research archive to every request 10 / Haystack builds retrieval and routing pipelines around your data. use a helper service to select supporting passages before handing a focused evidence package to Grok Bot 11 / aiocache caches async function results in memory, Redis, or Memcached. reuse fresh tool responses and set expiry rules for information that needs updating 12 / dlt loads new and changed records using incremental cursors. prepare an updated dataset in code so the Bot can investigate changes rather than rereading every historical row 13 / Hatchet runs background jobs with dependencies, event waits, and concurrency controls. move mechanical coordination into a workflow engine rather than repeated Bot status checks 14 / Inngest organizes helper workflows into durable steps with event triggers and step-level retries. separate collection, transformation, and analysis so failures can be handled at the relevant step 15 / Restate records execution progress and recovers completed steps after failures. useful for preventing an interrupted helper workflow from repeating work it already finished 16 / stamina adds bounded retries with backoff to Python calls. configure which failures deserve another attempt and cap both attempts and total time 17 / circuitbreaker pauses calls to a repeatedly failing service after a configured threshold. gives broken integrations time to recover before more requests pile up 18 / p-queue controls concurrency and request-start rates in JavaScript helpers. pace API jobs to reduce avoidable throttling and the retries it can trigger 19 / DeepEval tests saved outputs against quality criteria after a workflow change. sample the results and include any model-based judging costs when checking whether the change actually helped 20 / OpenTelemetry Python adds traces and metrics to helper scripts and services. follow a job across its steps to locate repeated requests, slow dependencies, and failures that trigger extra work connect the supporting libraries through scripts or services Grok Bot can call. pick one leak to fix: repeated context, unchanged data, or failed retries compare equivalent runs by accepted output and usage. include hosting, embeddings, and API costs so the fix doesn’t just move the bill elsewhere save this. fix the workflow that empties your limit first the article below covers all 7 workflow changes, with working files, prompts, and a budget calculation for your own setup ↓
    Download
    Gresham @Greshamtrade
    51113313K
  11. Gresham✓@Greshamtrade
    6446374810K
  12. Jobfound Remote Jobs 👨‍💻@JobFound5
    Role: Web Developer Salary: $5,100 - $6,800 per month Location: Remote - HTML, CSS, JavaScript - Troubleshoot website bugs Let us know if you are Interested 👇
    3111410.5K
  13. chaos✓@konig0000
    Junior Front-End Developer Looking for a developer with knowledge of HTML, CSS, and JavaScript to help build responsive web pages, fix interface issues, and improve website usability. 💰 Budget: $25–$45/hr 🇺🇸 Location: USA J
    300232.4K
  14. AGTP✓@AGTPinsights
    Vibe coding is dividing developers today as AI tools reshape how apps get built. Here's what you need to know. Vibe coding means you describe what you want in plain language and an AI builds it. Large language models generate the HTML, CSS and JavaScript. The catch is that you often accept the output without fully understanding it. It's fast to start and painful to maintain. Supporters call it the present of coding. One user says it saves time and effort and gives better results faster, with zero cons. Others say non-developers building side projects is fine, but production sites with real users need more care. One user says it has been forced on staff at their company. Another says if your CEO is actively vibe coding, run. Some builders say they've been shipping their own apps since February. Others argue vibe coders can succeed by handing off the code and focusing on marketing. The skeptics have a viral example. A vibe coder claimed they made a terminal faster than everyone else's. Ghostty creator Mitchell Hashimoto checked the source and found the read loop overwrites a 64 KiB ring, so older data is discarded unparsed on each tick. His verdict: it's faster because it isn't actually emulating a terminal. Other posts ask a different question. If every tool you vibe coded paged you at 2am when it broke, how many would you keep? And one reply points out that bugs don't only exist in vibe coding. One developer suggests vibing first to work out what you want, then porting it to a more sustainable process. Key numbers: - 55.8% faster task completion with GitHub Copilot, per GitHub-backed research - 31.4% average productivity gain from AI coding tools in one study - 23.7% more security vulnerabilities in that same study - 5 to 10 times faster code writing raises questions about what happens after code ships The debate is now less about whether people vibe code, and more about where it's safe to ship.
    Download
    206206
  15. 茶木 孝晃|AI × セキュリティ✓@ai_security_CT
    🚨 今度はCloudflareにもXSS脆弱性の報告! 10月28日、セキュリティ研究者がCloudflareの画像配信機能に関する問題を公開しました。 今回報告されたのは、複数の欠陥を組み合わせることで、CSPというJavaScriptの不正実行を防ぐ仕組みを回避し、悪意あるコードを実行できるというもの。 これ、以前から私が言っていたことなんですよね。 「WordPressは危険だからCloudflareに移行すれば安全」 そんな単純な話じゃないんですよ(笑) もちろん、Cloudflareのセキュリティ基盤が優れていることは理解しています。 ただ、どんなサービスにも脆弱性が見つかる可能性はあります。 重要なのは、どの技術を使うかだけではなく、認証・認可、インフラ設計、脆弱性への対応、そして継続的な保守運用です。 今回の件も、Cloudflareを利用しているすべてのサイトが危険という話ではありませんし、修正状況や影響範囲は引き続き確認が必要です。 ただ、今回改めて思うのが、特定のサービスを使えばセキュリティ問題が解決するという考え方の危うさ。 ツールを変えれば安全になるなら、セキュリティエンジニアなんて苦労しませんよ(笑) AI時代だからこそ、技術の好き嫌いではなく、システム全体の安全性を考えるべきだと思っています。 参考記事👇
    Cyber Security News @The_Cyber_News
    ⚠️ Researchers Chain Cloudflare Security Flaws to Bypass CSP and Execute Malicious JavaScript Details: Researchers chained several small flaws in Cloudflare’s image feature. Kevin Gervot and Adam Kues published the work on October 28, 2026, in a write-up titled Cache Me If You Can. They showed a working cross-site scripting (XSS) bug through the /cdn-cgi/image/ endpoint on cloudflare.]com. The write-up does not list a CVE or a patch status, so readers should check with Cloudflare. An attacker can hide a quote mark in that value and break out of it. The filter has already approved the file by then, so the script tag slips through. Cloudflare serves these images with a strict policy of default-src 'none', which blocks scripts. #cybersecuritynews
    05142.7K
  16. Cyber Security News✓@The_Cyber_News
    ⚠️ Researchers Chain Cloudflare Security Flaws to Bypass CSP and Execute Malicious JavaScript Details: Researchers chained several small flaws in Cloudflare’s image feature. Kevin Gervot and Adam Kues published the work on October 28, 2026, in a write-up titled Cache Me If You Can. They showed a working cross-site scripting (XSS) bug through the /cdn-cgi/image/ endpoint on cloudflare.]com. The write-up does not list a CVE or a patch status, so readers should check with Cloudflare. An attacker can hide a quote mark in that value and break out of it. The filter has already approved the file by then, so the script tag slips through. Cloudflare serves these images with a strict policy of default-src 'none', which blocks scripts. #cybersecuritynews
    Download
    227969.6K
  17. Prasenjit Sarkar✓@stretchcloud
    WebMCP and MCP sound like the same acronym fighting over a letter, but they split the agent stack along a real seam: client side versus server side. MCP runs on a server. A business stands one up, an agent connects over HTTP, and the whole exchange works with nobody watching, which is why it fits background automation and enterprise data access. WebMCP runs inside the browser tab. A site calls navigator.modelContext and declares what its buttons and forms actually do, through either an imperative JavaScript API or a declarative one that annotates existing HTML. The agent stops guessing from screenshots and DOM structure and starts calling a named tool, with a human still present and able to watch or step in. Chrome shipped this behind an origin trial in Chrome 149. Google is building it with Microsoft and incubating the spec inside the W3C Web Machine Learning group rather than shipping a unilateral standard, and Angular already has experimental support. That consortium structure is the tell: nobody wants a repeat of the early web, where every browser invented its own version of the same idea. Stacklok's 2026 survey of 100 software leaders found MCP already in production at nearly half of companies, 19% past pilot into broad rollout, and 49% naming MCP adoption a top five company initiative this year. Security is still the biggest brake on all of it: 64% cite it as the top obstacle, higher than retail or financial services report, which is notable given software teams face less regulatory pressure than either. MCP and WebMCP aren't competing standards, they're splitting the same stack along the line REST and GraphQL split APIs a decade ago: backend contract versus frontend affordance. The part worth watching is whether site owners bother annotating their own HTML once agents are already scraping it anyway without asking permission.
    505308
  18. Jiahan Chen✓@jiahan_c
    SWC Next is here! Today, customizing how your code is transformed often means using Babel plugins or writing Wasm plugins for SWC. I believe the next generation of JS compilers should combine Rust's performance with the flexibility to write custom transform plugins in JavaScript. SWC Next's flat AST enables efficient data exchange between Rust and JS, laying the groundwork for fast JS plugins 🚀
    Download
    SWC @swc_rs
    Introducing SWC Next: the foundation for SWC’s next major version, built on a new architecture inspired by Yuku. - Up to 3x faster native parsing - Up to 10x faster parsing through the JavaScript API - A flat, ESTree-based AST designed for speed, memory efficiency, and JavaScript extensibility Starting with parsing, we’re bringing the rest of SWC to this new architecture. Built together by the SWC and Rstack teams.
    82313511.1K
  19. SWC✓@swc_rs
    Introducing SWC Next: the foundation for SWC’s next major version, built on a new architecture inspired by Yuku. - Up to 3x faster native parsing - Up to 10x faster parsing through the JavaScript API - A flat, ESTree-based AST designed for speed, memory efficiency, and JavaScript extensibility Starting with parsing, we’re bringing the rest of SWC to this new architecture. Built together by the SWC and Rstack teams.
    125733129.8K
  20. Show more posts